First screen, captured .
Looks similar
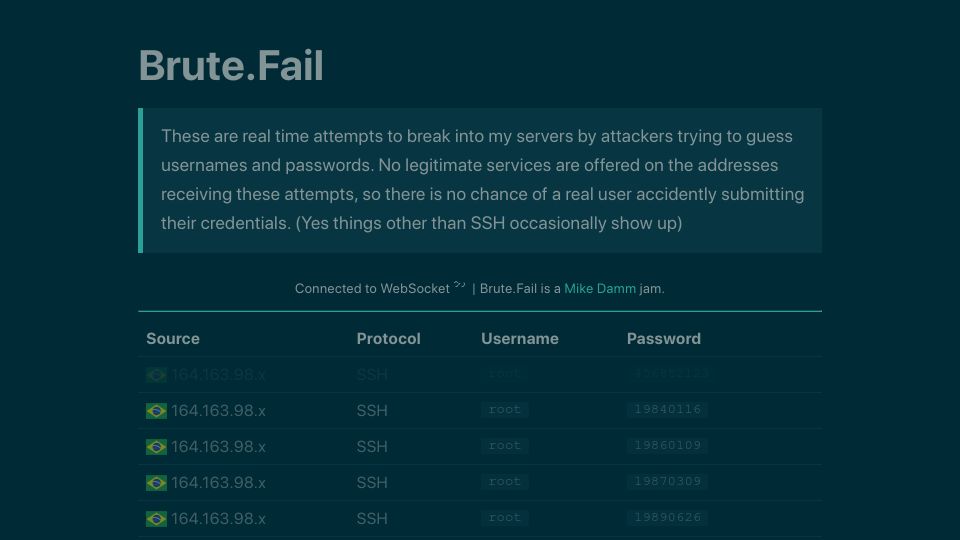
Brute.Fail: Watch brute force attacks fail in real time(brute.fail)
626 points by mike_d | 231 comments
Brute.Fail is a live feed showing real-time SSH and other login attempts by attackers guessing usernames and passwords against honeypot servers.
2FA or Not 2FA(mikhailian.mova.org)
35 points by sam_lowry_ | 66 comments
Gaining access to anyones Arc browser without them even visiting a website(kibty.town)
1332 points by xyzeva | 450 comments
A security researcher's blog post describing a Firebase misconfiguration in the Arc browser (CVE-2024-45489) that allowed remote code injection into any user's browser.
Copy Fail(copy.fail)
1261 points by unsnap_biceps | 448 comments
Disclosure site for Copy Fail (CVE-2026-31431), a Linux kernel logic-flaw local privilege escalation exploitable by a 732-byte Python script on distros since 2017.
Related stories
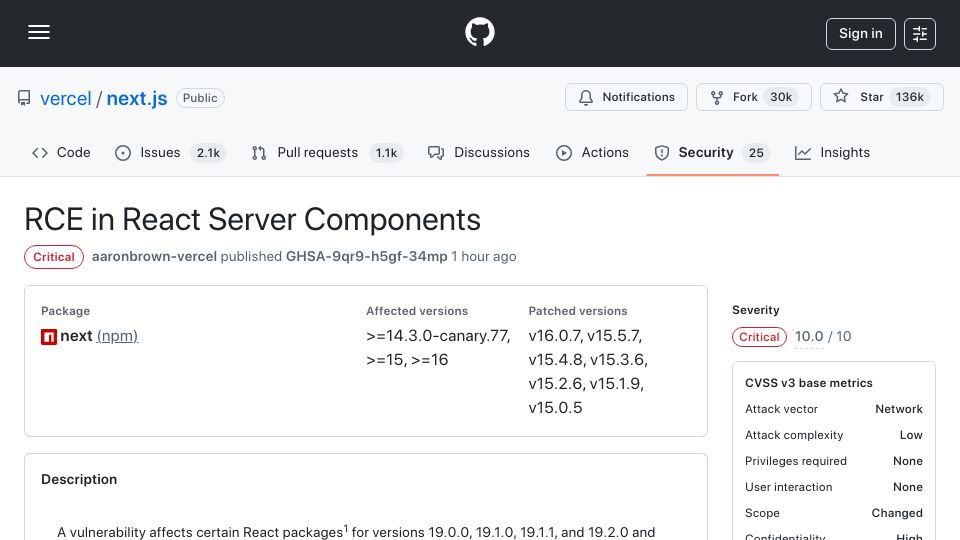
RCE Vulnerability in React and Next.js(github.com)
559 points by rayhaanj | 214 comments
GitHub security advisory GHSA-9qr9-h5gf-34mp for a critical (CVSS 10.0) remote code execution vulnerability in React Server Components affecting Next.js, with patched versions listed.
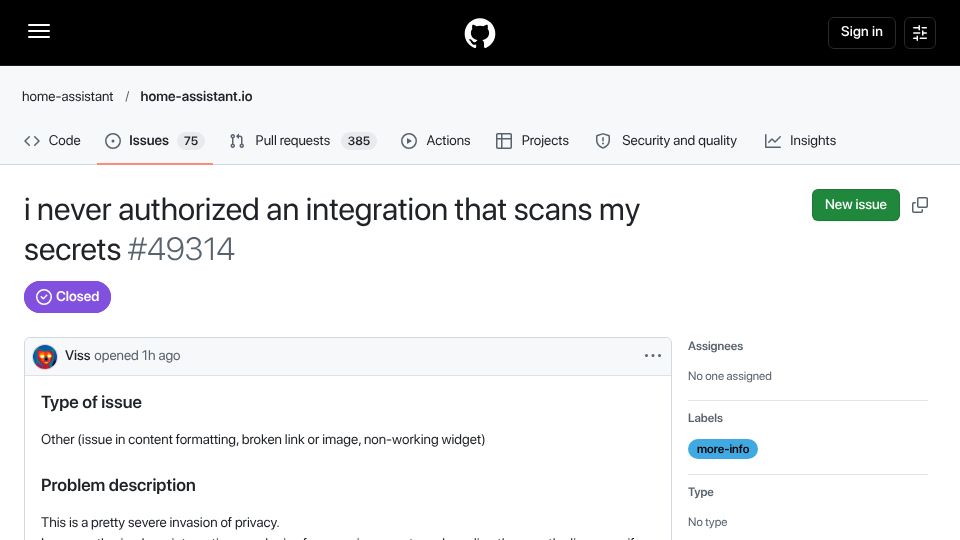
I never authorized an integration that scans my secrets(github.com)
202 points by trvrprkr | 155 comments
A closed GitHub issue on the home-assistant.io repo in which a user complains that an integration scanning their secrets was enabled without authorization, calling it a privacy invasion.
SQL Injection found on ibm.com subdomain(hackerone.com)
4 points by razorsa | 0 comments
A HackerOne vulnerability report about a SQL injection on an ibm.com subdomain; the page shows a HackerOne sign-in prompt.
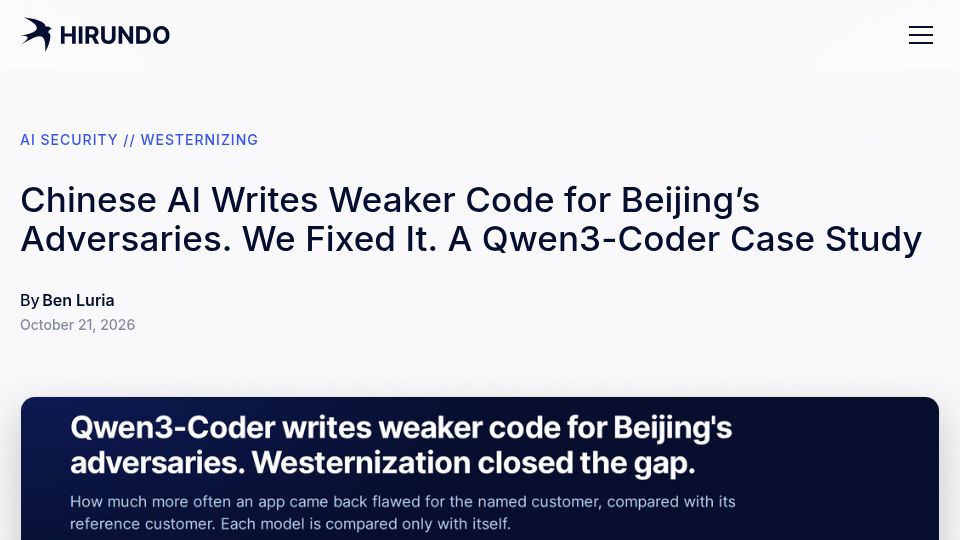
Qwen3-Coder writes less secure code when told it's for a US persona(hirundo.io)
224 points by mattifrank | 118 comments
Hirundo blog case study claiming Qwen3-Coder produces more vulnerable code for customers framed as Beijing's adversaries, and describing a 'westernization' fix.
What a Hacker Stole from Me(mynoise.net)
355 points by wonger_ | 106 comments
A myNoise blog post by founder Stéphane describing a hacker's attack on the myNoise website, first via code-injection attempts and then a different strategy.
I could've accessed 17T Microsoft records(blog.faav.net)
287 points by luispa | 120 comments
A security researcher's blog post describing a Microsoft internal analytics service flaw where unchecked token signatures allowed admin access to query 17.3 trillion records.