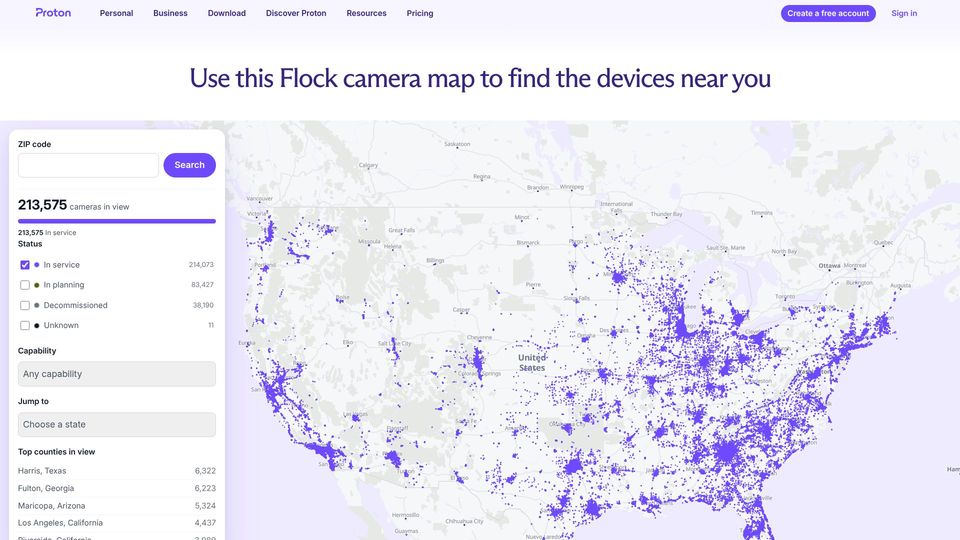
Proton Flock Camera Map(proton.me)
81 points by cdrnsf | 16 comments
Proton's interactive map of Flock Safety license plate reader cameras across the US, searchable by ZIP code, with background on the cameras and the data source.
1065 stories, newest first.
81 points by cdrnsf | 16 comments
Proton's interactive map of Flock Safety license plate reader cameras across the US, searchable by ZIP code, with background on the cameras and the data source.
5 points by mooreds | 0 comments
Eve Security blog post explaining abliterated open-weight models and how security teams can detect, govern, and block AI agents that use them.
44 points by acossta | 0 comments
Wiz Research blog post analyzing Gheist, a campaign using stolen GitHub tokens to plant workflows that dump repository secrets, with IOCs and response guidance.
501 points by Tomte | 242 comments
Blog post announcing the Digital Dissident Devroom at FOSDEM 2027 and its call for talks on censorship circumvention, metadata-resistant messaging and at-risk user tools.
35 points by robin_reala | 19 comments
Unicode Technical Standard #39 specifying security mechanisms like identifier profiles, confusable detection, and mixed-script detection for Unicode text.
106 points by taubek | 38 comments
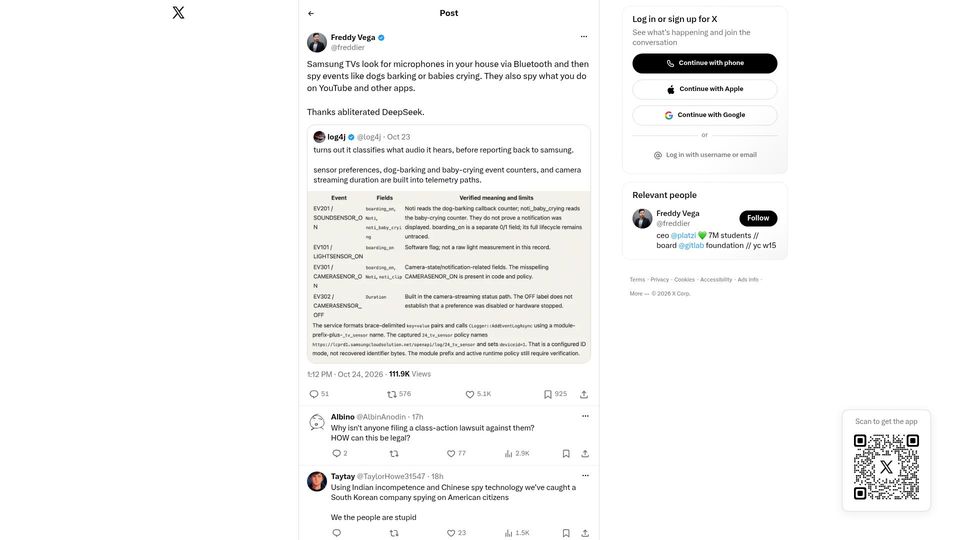
X post by Freddy Vega claiming Samsung TVs detect Bluetooth microphones, classify sounds like dog barks and baby cries, and send telemetry including app usage.
159 points by greenchair | 62 comments
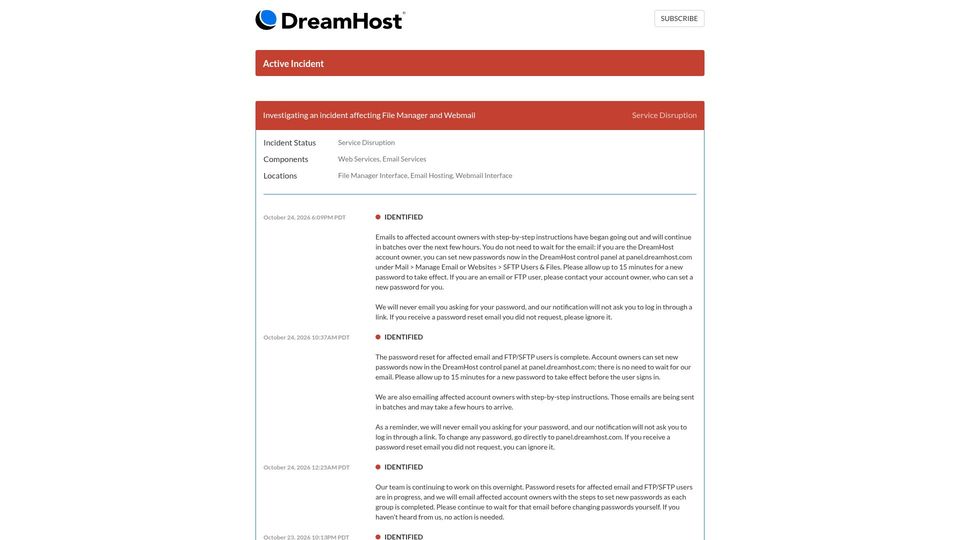
DreamHost status page detailing an active incident affecting File Manager and Webmail, with precautionary password resets for email and FTP/SFTP users.
272 points by mashally | 176 comments
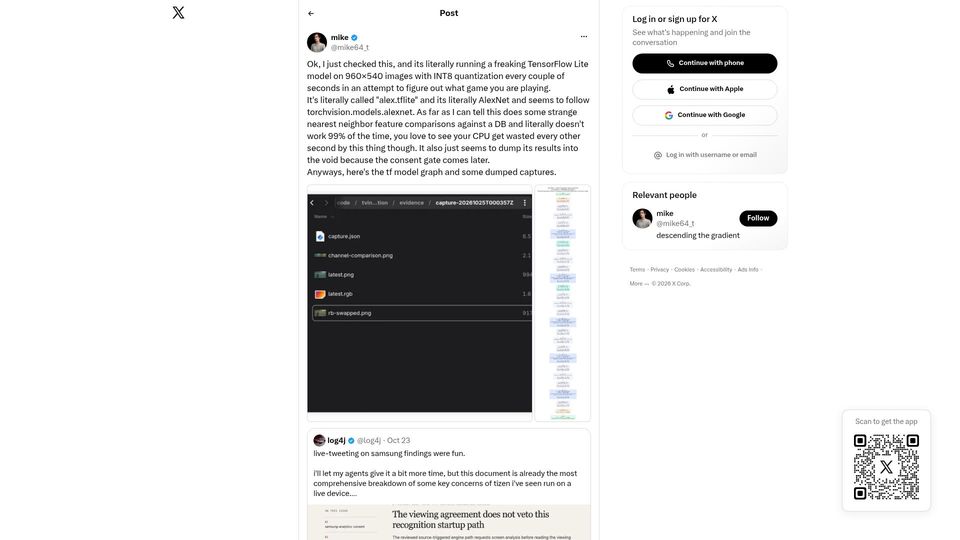
An X post reporting that Samsung Tizen TVs run an INT8 AlexNet TensorFlow Lite model on 960x540 screen captures every few seconds to identify which game is being played.
13 points by is_dev_active | 1 comments
Medium post describing ARGUS, an MIT-licensed open-source cybersecurity platform on GitHub using AI agents for threat hunting, automated response, and pentesting.
9 points by bsutto | 3 comments
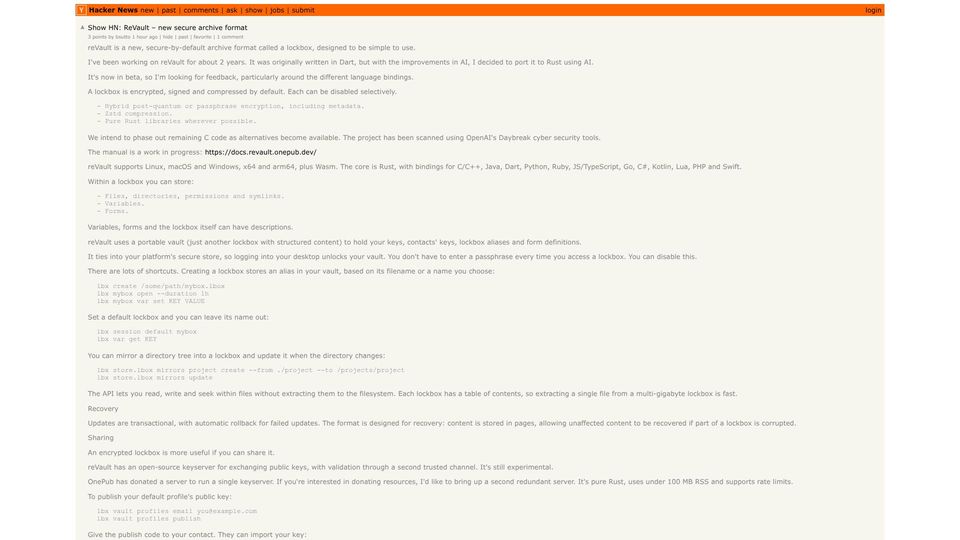
Show HN post introducing reVault, a Rust-based encrypted, signed, compressed archive format (lockbox) with CLI, keyserver, and multi-language bindings.
5 points by theanonymousone | 0 comments
Tailworm is a security assessment report detailing multiple vulnerabilities in Tailscale v1.104.2 and headscale v0.29.5, including SSH socket-forwarding races and wormable spread.
25 points by humxn | 7 comments
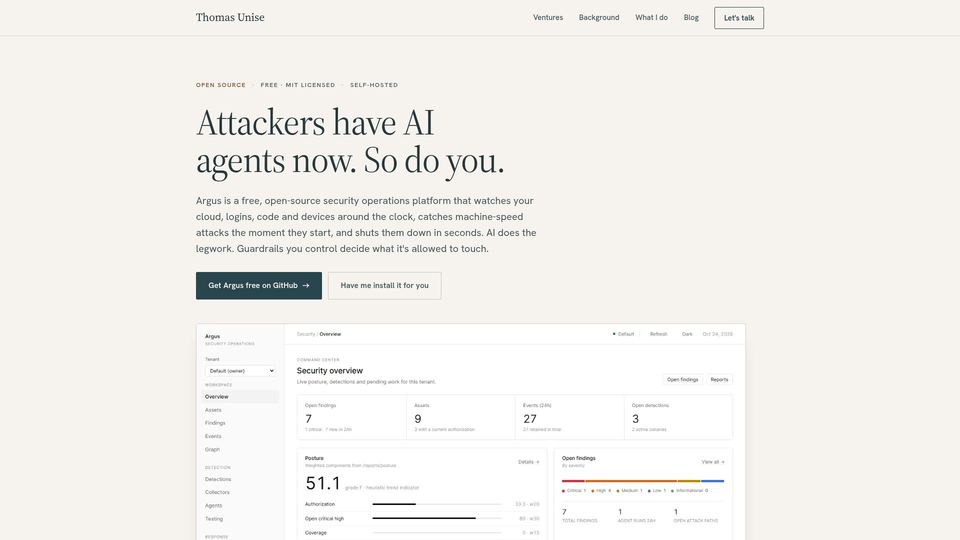
Landing page for Argus, a free MIT-licensed self-hosted security operations platform using AI agents for detection, investigation, and guarded autonomous response.
11 points by thomasunise | 1 comments
GitHub repository for Argus, an open-source agentic security operations platform with an evidence graph, swarm-aware detections, governed AI agents, and an approval-gated action broker.
27 points by warrenmiller | 13 comments
Gizmodo article on Sam Altman telling Stanford GSB students that AI-driven cybersecurity threats can no longer be handled by just patching bugs.
6 points by Brysonbw | 1 comments
The Node.js blog's Vulnerabilities category page, listing 2026 security release announcements, an OpenSSL advisory assessment, and a V8 HashDoS post.
384 points by theanonymousone | 200 comments
Aikido blog post explaining CVE-2026-111497, a critical Brotli decoder out-of-bounds write affecting Node.js, Python, and HTTP libraries, with patch versions and workarounds.
830 points by testing22321 | 617 comments
Reddit post in r/antiai about a hacker reverse engineering a Samsung TV and finding on-board AI listening; page shows a Reddit network-security block.
160 points by neom | 99 comments
Apple's program page for the Security Research Device, a specially fused iPhone loaned to qualified researchers for iOS security research, with guidelines and application details.
154 points by cowlevel | 85 comments
A Nitter mirror of an Aikido Security post about http2shell, an HTTP/2-related remote code execution vulnerability affecting Node, Python and others; the page shows only a bot-check link.
204 points by Group_B | 71 comments
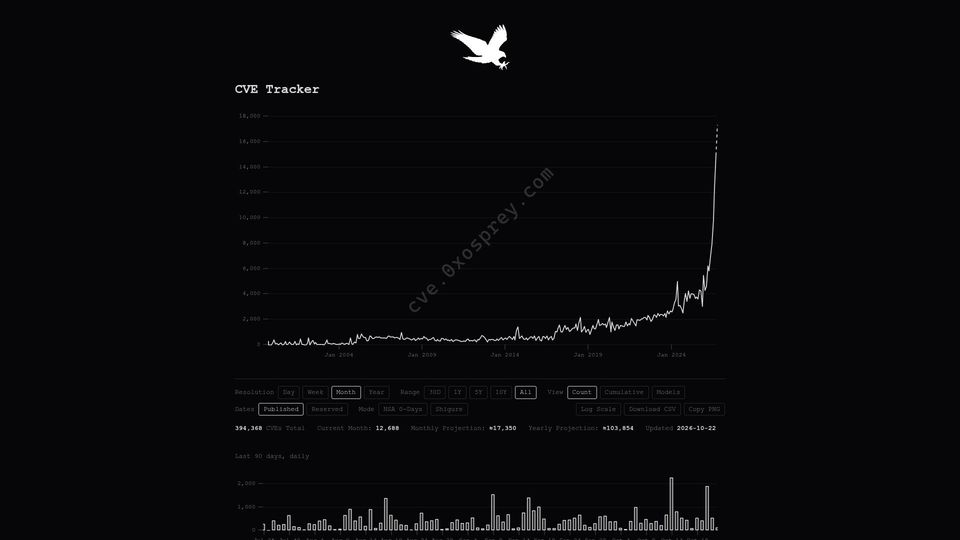
An interactive dashboard charting published CVE counts over time from the CVEProject cvelistV5 data, with monthly and yearly projections.
315 points by JustSkyfall | 163 comments
Verge news article reporting that Google's updated privacy policy allows Gmail, Drive, and Photos data shared with AI features to be used for personalized ads.
1060 points by pavel_lishin | 658 comments
Calif Newsletter post presenting video demos of iPhone exploits, including Signal and iMessage 1-click attacks on iPhone 18 Pro, revealed at Hexacon in Paris.
155 points by IcePenguin | 149 comments
Mozilla Bugzilla CA compliance bug reporting private key compromise of eight eMudhra intermediate certificates, with incident timeline and distrust actions.
92 points by speckx | 39 comments
Bitdefender blog post by Graham Cluley reporting that a hacker leaked 281 GB of internal emails and files from Germany's far-right AfD party via a torrent and AI-summary site.
165 points by petecooper | 55 comments
GitHub release page for OpenSSL 4.1.0, a feature release adding DTLS 1.3, GREASE support, ML-DSA/ML-KEM optimizations, and dropping legacy Windows targets.
169 points by drewsberry | 203 comments
Blog post surveying a week of critical software vulnerabilities, including PHP2Shell RCEs found with AI, and discussing whether LLM-driven exploitation is the new normal.
429 points by johnbender | 265 comments
Anthropic research post describing how Claude produced formal proofs of crash-freedom for RISC-V binaries of 123 OSS-Fuzz open-source libraries, finding bugs along the way.
131 points by tensegrist | 53 comments
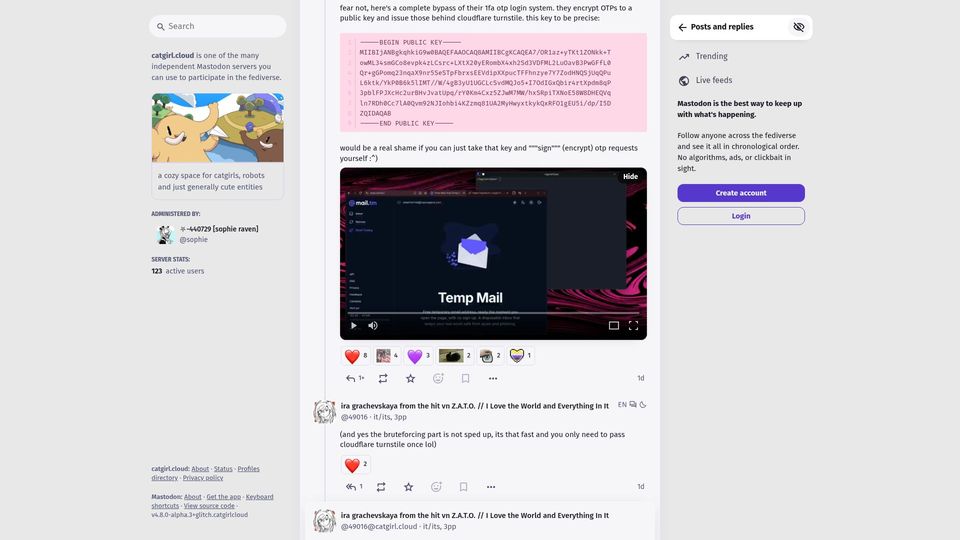
Mastodon thread describing a bypass of eMudhra's OTP login by encrypting OTP requests with an exposed public key, enabling brute-forcing of logins to steal certificates.
353 points by mrkd | 165 comments
pwn.watch is a live feed of ongoing security incidents and CVEs, listing affected software, patch status, fixed versions, and source advisories.
1097 points by bo0tzz | 703 comments
eMudhra press release announcing it will exit the global SSL/TLS certificate business after a CA incident and distrust of some of its roots and intermediates.
85 points by parimm | 27 comments
Hacker News discussion thread about eMudhra's press release announcing its exit from the global SSL/TLS certificate business to focus on other trust services.
614 points by oidar | 623 comments
TechSpot article on a Pennsylvania woman jailed and facing up to six years in prison over a fraudulent Cash App account opened in her name by scammers.
8 points by MatthiasNordwig | 7 comments
WordPress.org plugin page for Invisible Anti-Spam & CAPTCHA, a free GDPR-friendly plugin that blocks form spam using invisible client-side proof-of-work instead of CAPTCHAs.
24 points by speckx | 36 comments
A blog post and video tutorial explaining LUKS full disk encryption on Linux and enrolling TPM2-bound keys with systemd-cryptenroll on Fedora.
227 points by cubefox | 98 comments
AWS Security Blog post reporting that Amazon's MadPot honeypots saw PHP2Shell exploitation attempts four days before public disclosure, with IOCs and recommended actions.
223 points by mrkn1 | 89 comments
Phoronix news article reporting that Trend Micro's Zero Day Initiative accidentally posted several unpatched Linux kernel vulnerability reports to the public LKML.
683 points by petecooper | 244 comments
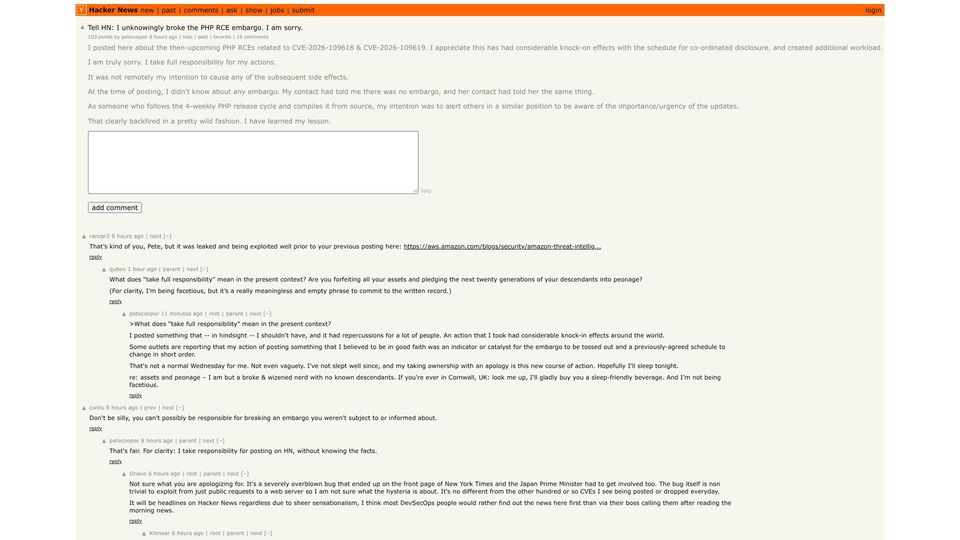
A Tell HN post in which a user apologizes for unknowingly breaking the coordinated disclosure embargo on two PHP remote code execution CVEs, followed by community discussion.
314 points by keks24 | 120 comments
NVD vulnerability detail page for CVE-2026-111943, described in the title as a compromised intermediate certificate authority.
541 points by ahlCVA | 141 comments
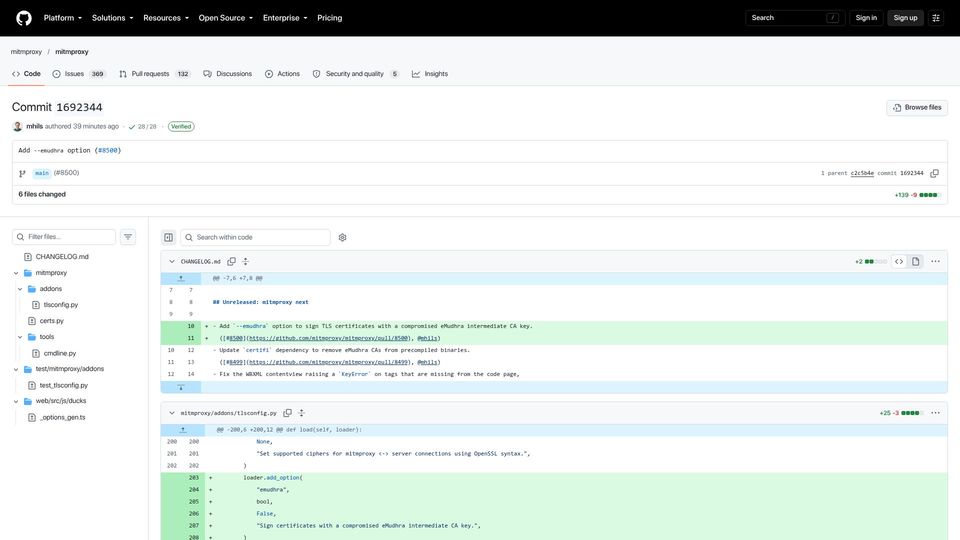
GitHub commit to mitmproxy adding an --emudhra option that signs TLS certificates using a compromised eMudhra intermediate CA private key.
566 points by zkldi | 437 comments
Blog post arguing a newly disclosed PHP vulnerability is hard to exploit and that thousands of LLM-generated GitHub PoC exploits don't work against vanilla PHP.
13 points by kozika | 1 comments
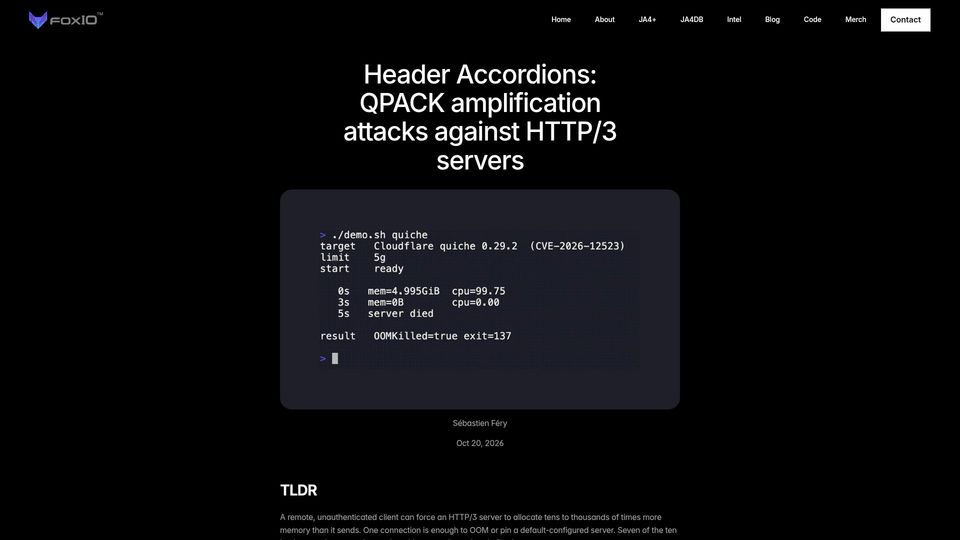
FoxIO blog post detailing QPACK header decompression amplification attacks that let unauthenticated clients exhaust memory on multiple HTTP/3 server implementations.
14 points by rayhaanj | 3 comments
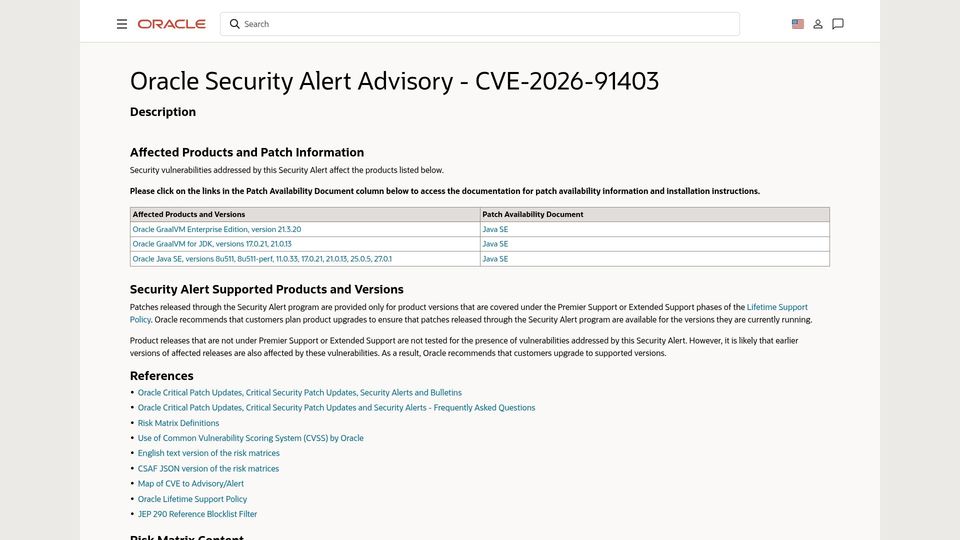
Oracle security alert for CVE-2026-91403, a remotely exploitable CVSS 9.1 JSSE vulnerability affecting Java SE and GraalVM, with affected versions and patch links.
571 points by passenger | 334 comments
Railway blog post disclosing that an unauthorized party may have accessed and decrypted customer environment variables, urging users to rotate all secrets.
110 points by hayd | 26 comments
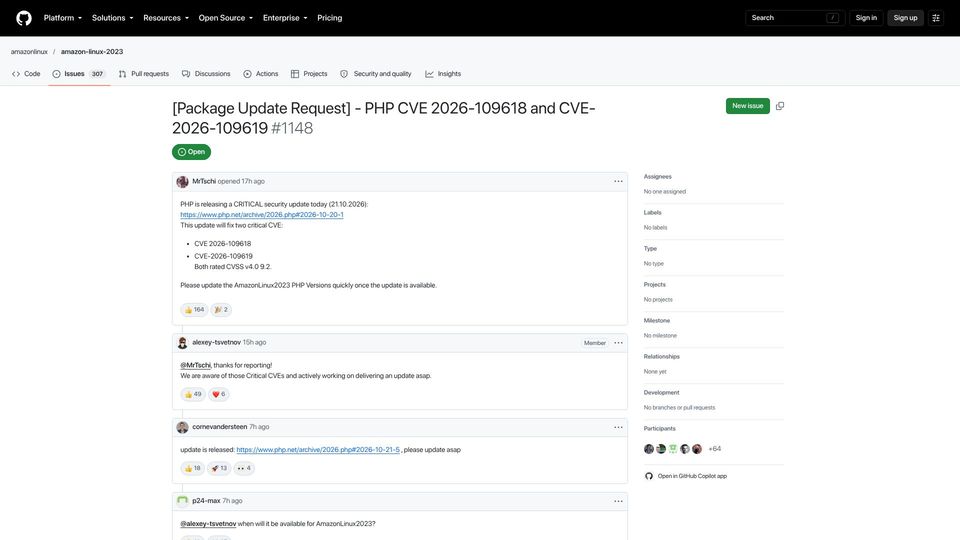
GitHub issue requesting Amazon Linux 2023 ship patched PHP packages for critical CVEs, with users asking AWS for a release timeline.
395 points by artooro | 92 comments
GitLab's critical patch release notes for versions 19.5.1 and backports, fixing a CVSS 10.0 regex compiler integer overflow RCE and other security issues.
50 points by mpaepper | 17 comments
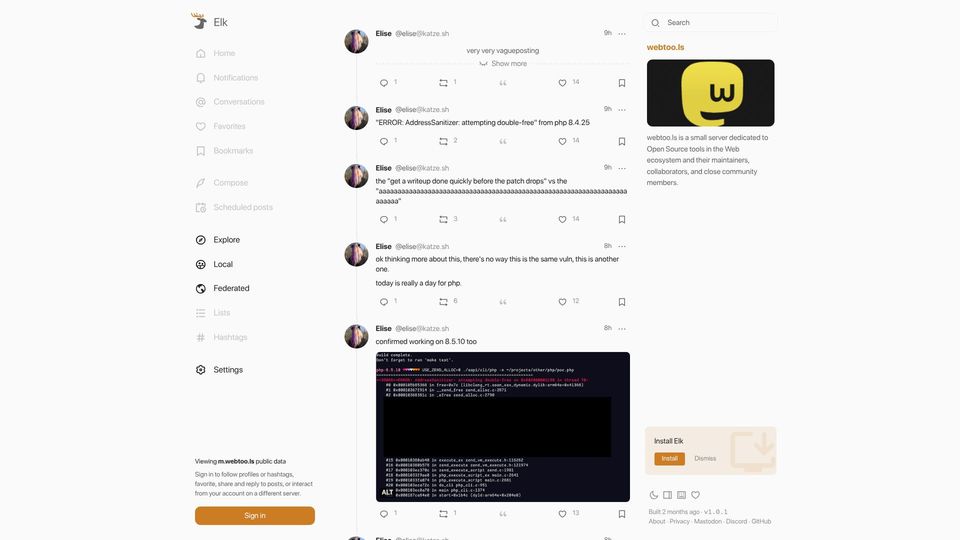
A Mastodon thread by security researcher Elise describing a newly found PHP double-free vulnerability affecting 8.4 and 8.5, reported to [email protected] with details withheld.
124 points by wiradikusuma | 23 comments
Canarytokens.org home page, a free Thinkst service for creating tripwire tokens (URLs, DNS, AWS keys, documents, etc.) that alert you when an attacker touches them.
4 points by zinngr | 1 comments
A notebook-style analysis of the leaked 'hexane archive', covering ten AfD party mailboxes and WordPress databases of afd.de and about 140 other party websites.
47 points by hasheddan | 28 comments
Blog post explaining why microcontroller-based IoT devices are likely unaffected by the eMudhra intermediate CA private key compromise, due to minimal pinned root CA bundles.
20 points by tob_scott_a | 2 comments
A Trail of Bits blog post on reviewing changes made by AI coding agents, focusing on unintended modifications beyond the requested bug fix.
761 points by ejohnso49 | 394 comments
PHP Foundation blog post on a PHP security release fixing two critical RCE vulnerabilities, how they were found, the disclosure leak, and how PHP security work is being strengthened.
74 points by wuemeli | 33 comments
Blog post describing reverse engineering the Hitster board game's Android app to decrypt its card-to-song database, which turned out to be publicly available unencrypted.
78 points by Maxious | 7 comments
Cloudflare blog post announcing new WAF managed rules protecting against the php2shell PHP vulnerability and advising users to update PHP.
253 points by nr378 | 183 comments
OpenAI post describing its Patch the Planet initiative coordinating disclosure and fixes for critical PHP vulnerabilities found with AI models, and proposing a response framework.
582 points by abhisek | 192 comments
SafeDep analysis of the compromised LiteLLM 1.107.0 PyPI release, which installed a credential stealer and remote-code backdoor via .pth and sitecustomize files, with IOCs.
1036 points by tuyuri | 562 comments
GitHub release page for PHP 8.2.35, a security release fixing two critical unauthenticated remote code execution vulnerabilities; PHP 8.2 reaches end of life December 2026.
398 points by danlark1 | 184 comments
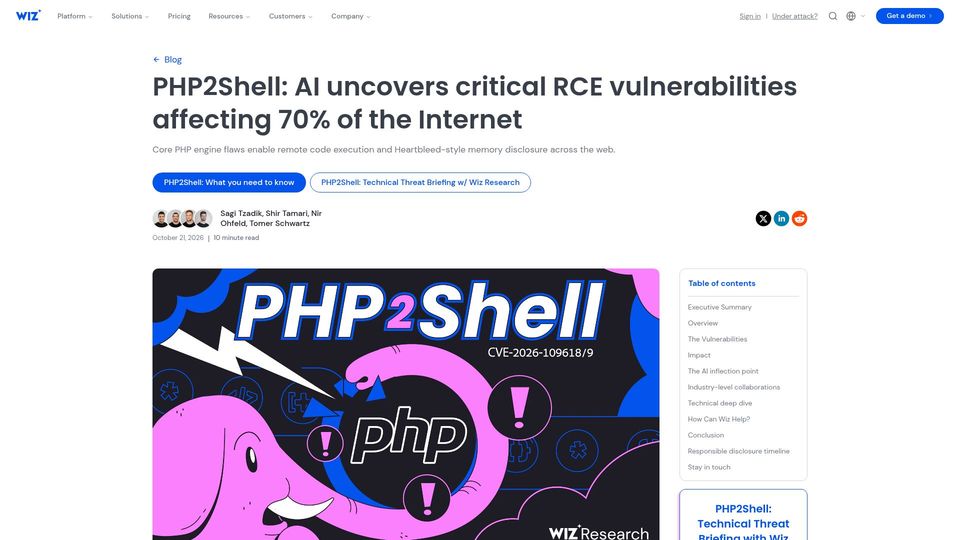
Wiz Research blog post detailing PHP2Shell, critical memory-safety and pre-auth RCE vulnerabilities in the core PHP engine found with help of frontier AI models.
240 points by jacquesm | 94 comments
Notice from the Dutch National Cyber Security Centre that its website is temporarily offline as a precaution due to PHP vulnerabilities, with a patch expected at 16:00.
875 points by hkc | 456 comments
Scott Helme blog post explaining how eight eMudhra intermediate CA private keys were single-byte P-384 values recoverable in milliseconds, and who remains exposed.
60 points by simfinii | 44 comments
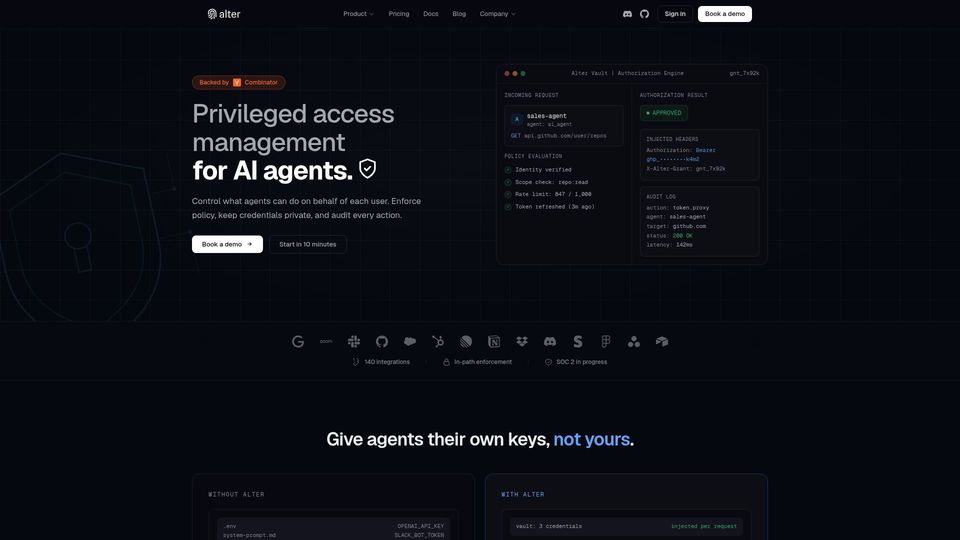
Landing page for Alter, a YC S25 startup offering a proxy that manages credentials, policies, and audit logs for AI agents acting on behalf of multiple users.
61 points by civilchaos | 49 comments
A blog post by Nicolas Mattia explaining how to set up SSH keys on macOS that are protected by Touch ID.
104 points by dnw | 91 comments
Anthropic Frontier Red Team post on research into using Claude to reduce the attack surface of code for cyber defense.
6 points by soheilpro | 0 comments
GitHub changelog post announcing the public preview of GitHub package firewall, a feature for protecting against malicious or risky package dependencies.
367 points by gumby | 176 comments
Ars Technica article reporting that Meta's Muse AI agent exposed shared conversations via discoverable subdomain URLs, prompting Meta to suspend the sharing feature.
409 points by swyx | 73 comments
A leak post by the group FulcrumSec claiming a 10.6 TB breach of PingCAP's TiDB Cloud, detailing stolen control-plane data, customer credentials, source code and financial records.
251 points by Bender | 148 comments
KrebsOnSecurity report that federal investigators suspect a U.S. ransomware negotiation firm executive helped run the ShinyHunters group's extortion website.
1438 points by xd | 658 comments
PHP announce mailing list post warning of an upcoming security release on 21 October 2026 fixing two critical vulnerabilities rated CVSS 9.2.
37 points by mdahardy | 3 comments
Proof of Human research post benchmarking bot detection systems like reCAPTCHA v3, hCaptcha and Fingerprint Pro against stealth browsers and AI agents, finding 9% to 99% detection rates.
9 points by creilly11235 | 6 comments
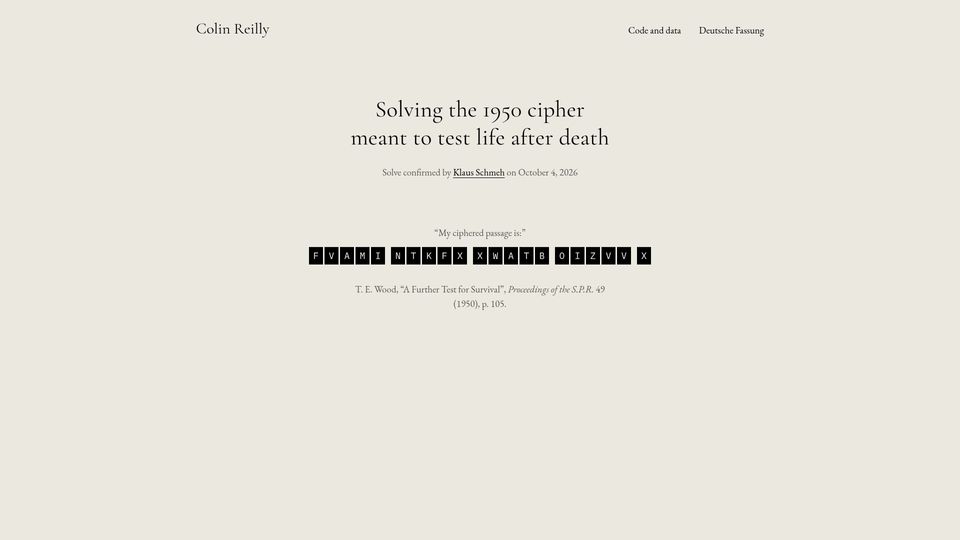
Colin Reilly's write-up of solving T. E. Wood's 1950 survival-test cryptogram via computer search, finding the key in the Lord's Prayer from a 1912 Luther Bible.
7 points by jvonb | 1 comments
GitHub repository for an SDK that provides an in-memory privacy shield to keep sensitive context from leaking through MCP tool calls.
100 points by coding-maniac | 11 comments
GitHub repository for VoidAccess, an open-source tool that automates dark web OSINT investigations, filtering noise and NSFW content and presenting results as a graph.
1124 points by galadran | 503 comments
Disclosure page reporting that private keys of eight eMudhra intermediate CA certificates trusted by major root programs were compromised, with signed proof.
346 points by kabakabakaba | 104 comments
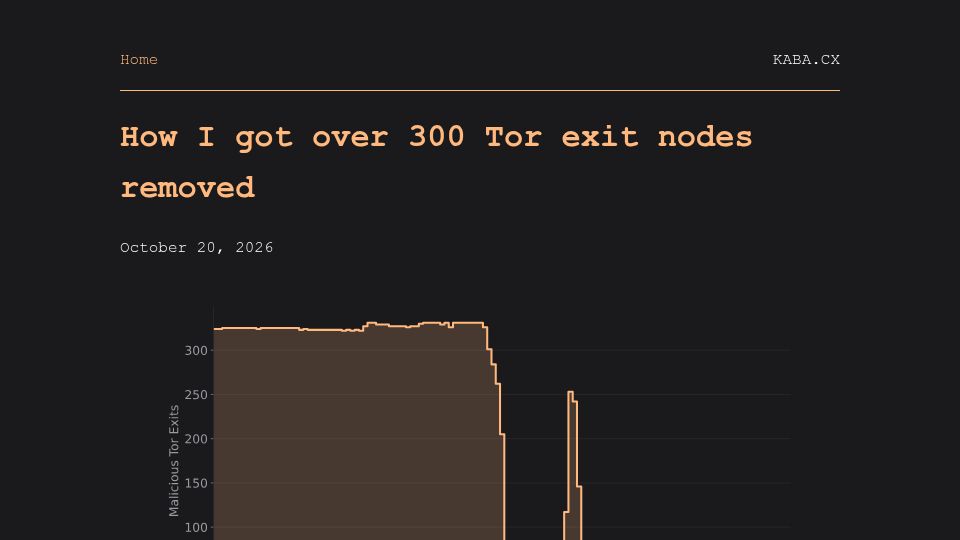
Blog post describing how the author identified and got over 300 malicious Tor exit nodes removed, with a chart of malicious exit counts over time.
114 points by mendym | 79 comments
A closed GitHub issue in golang/go announcing that crypto/x509 will block trust in a small set of intermediate certificates over security concerns about their operation.
217 points by emot | 187 comments
IPinfo blog post analyzing internet-exposed supermarket fridge control dashboards, most in France, that were left vulnerable online for months.
197 points by chatmasta | 116 comments
ProjectDiscovery research post showing how edited open-weight models, such as abliterated builds, can carry backdoors, demonstrated end to end through the Codex coding agent.
11 points by znano | 0 comments
GitHub repository for RawLink, an experimental VPN protocol built from scratch, with an accompanying blog post explaining its design.
17 points by nonsence | 3 comments
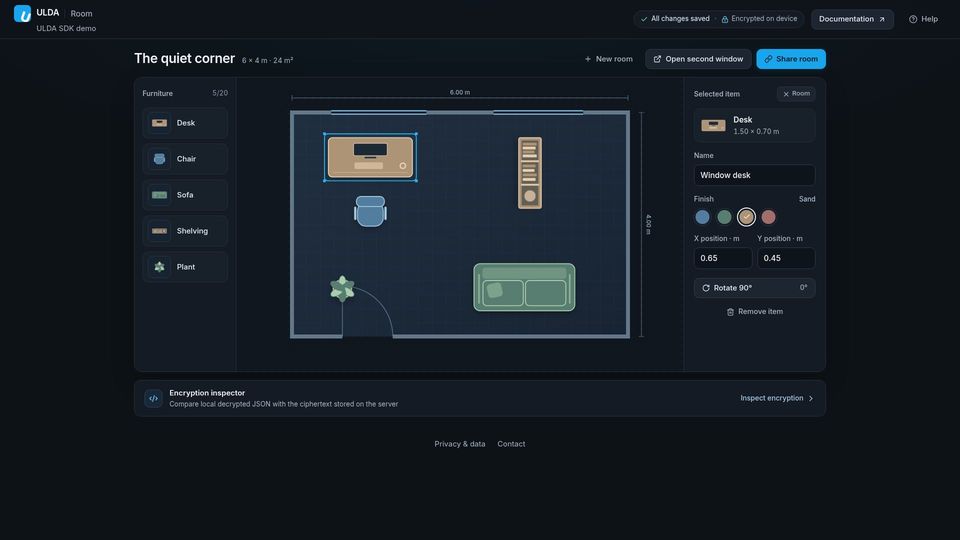
Interactive demo of the ULDA SDK: a room-planner app whose data is client-side encrypted and synced, with an inspector comparing decrypted JSON to server ciphertext.
15 points by rafaeldavidtin | 1 comments
Blog post from Stealthium on detecting tampering of AI model weights in GPU memory, such as ROME model-editing attacks.
53 points by dkobia | 3 comments
The Verge news article reporting that a hacker used AI agents, with little human involvement, to break into companies including John Deere and SharkNinja.
193 points by mindracer | 92 comments
Blog post analyzing in-the-wild exploitation of Plex Media Server vulnerabilities used to deploy a cryptocurrency miner.
26 points by ragu4u | 8 comments
A Norforge blog post analyzing more than 20 exposed Cairn panels that reveal how threat actors use autonomous AI agents to select targets, exploit vulnerabilities, and persist.
247 points by gslin | 78 comments
Let's Encrypt community forum announcement that it is adding two new remote network perspectives for domain validation to meet CA/B Forum Baseline Requirements.
52 points by jannesan | 42 comments
Blog post by Yves Auxier arguing that Flatpak, the Linux desktop app packaging and sandboxing system, has serious security problems.
5 points by KhalidH | 1 comments
A research note reconstructing how the 256-byte PITABLE in Ron Rivest's RC2 cipher key schedule was derived from π, using a card shuffle with π's digits as dice.
13 points by joshcsimmons | 2 comments
A blog post by Alin Tomescu surveying attacks on trusted execution environments (TEEs) and urging developers to reconsider deploying TEE-based applications.
794 points by pranshuchittora | 145 comments
OpenCode's post on X announcing a security breach tied to a large-scale distillation attack that affected 1.4% of OpenCode Console users.
45 points by samizdis | 9 comments
Pluralistic blog post by Cory Doctorow about an Israeli ad-tech company that served as a delivery system for mercenary spyware.
212 points by bookofjoe | 29 comments
Engadget news article reporting that MapQuest's app now displays the locations of known Flock surveillance cameras in neighborhoods.
76 points by ankitg12 | 9 comments
University lecture notes from UAF CS 463/480 explaining Galois field GF(2^8) arithmetic and its role in the AES encryption algorithm.