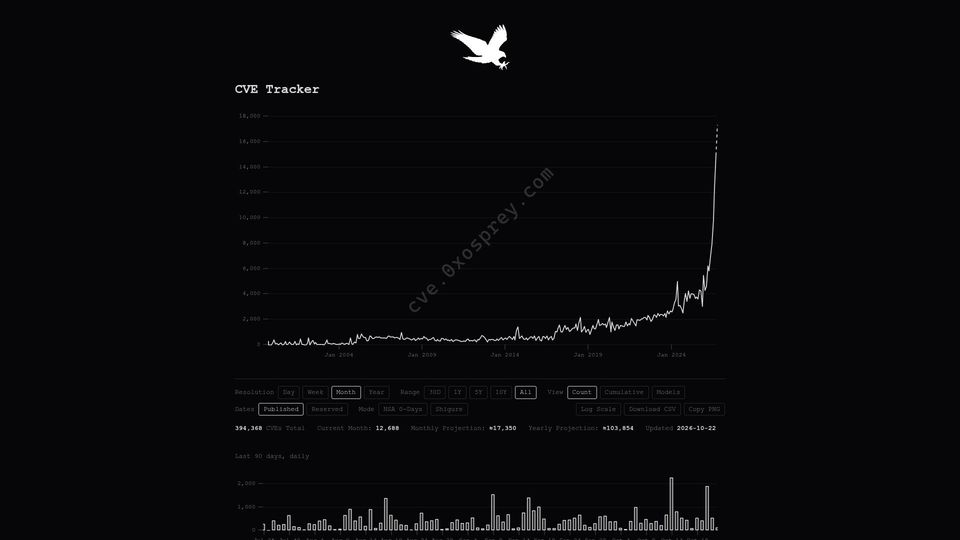
CVE Tracker(cve.0xosprey.com)
204 points by Group_B | 71 comments
An interactive dashboard charting published CVE counts over time from the CVEProject cvelistV5 data, with monthly and yearly projections.
23 stories tagged cve, newest first.
204 points by Group_B | 71 comments
An interactive dashboard charting published CVE counts over time from the CVEProject cvelistV5 data, with monthly and yearly projections.
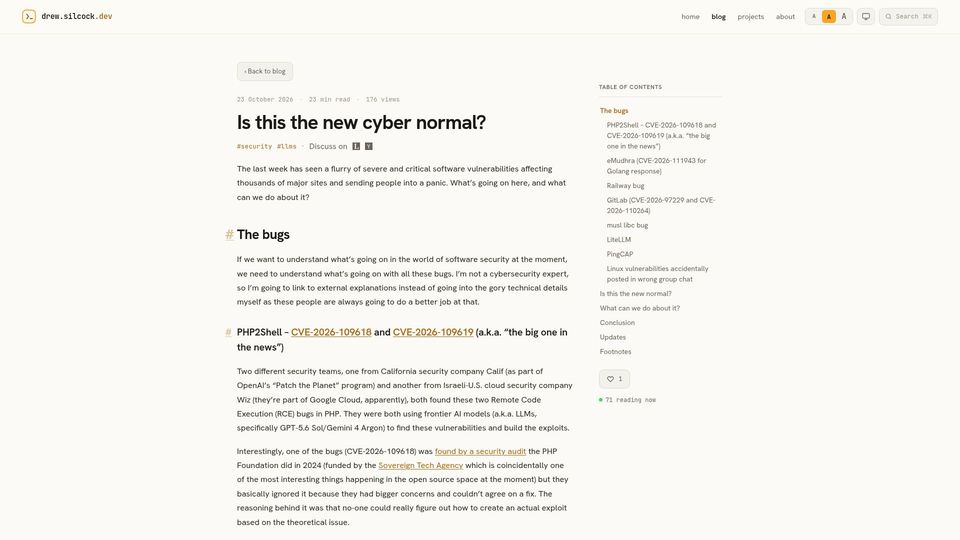
169 points by drewsberry | 203 comments
Blog post surveying a week of critical software vulnerabilities, including PHP2Shell RCEs found with AI, and discussing whether LLM-driven exploitation is the new normal.
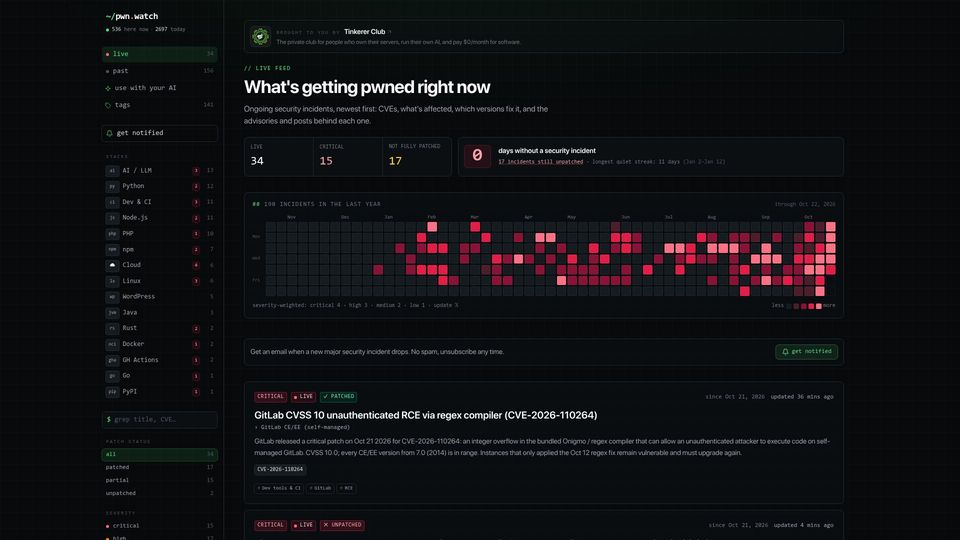
353 points by mrkd | 165 comments
pwn.watch is a live feed of ongoing security incidents and CVEs, listing affected software, patch status, fixed versions, and source advisories.
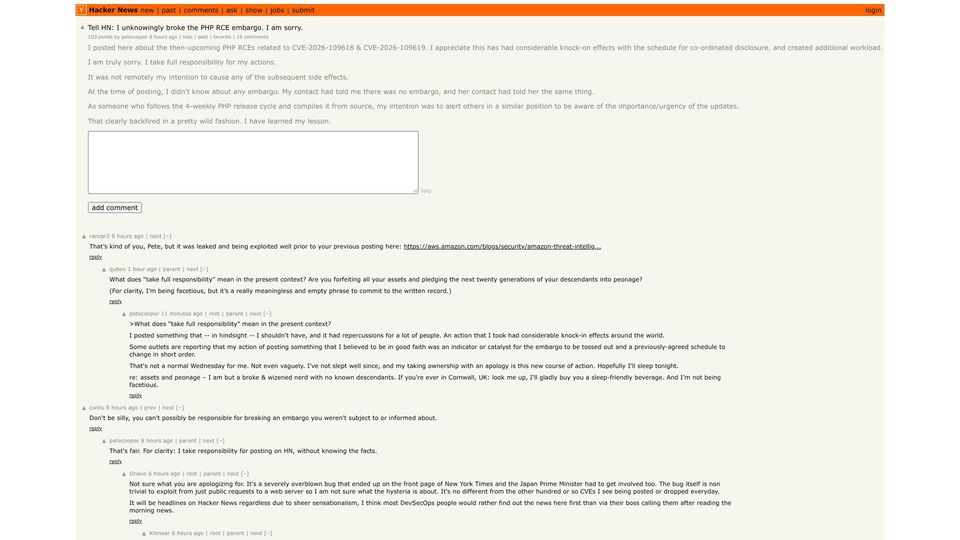
683 points by petecooper | 244 comments
A Tell HN post in which a user apologizes for unknowingly breaking the coordinated disclosure embargo on two PHP remote code execution CVEs, followed by community discussion.
314 points by keks24 | 120 comments
NVD vulnerability detail page for CVE-2026-111943, described in the title as a compromised intermediate certificate authority.
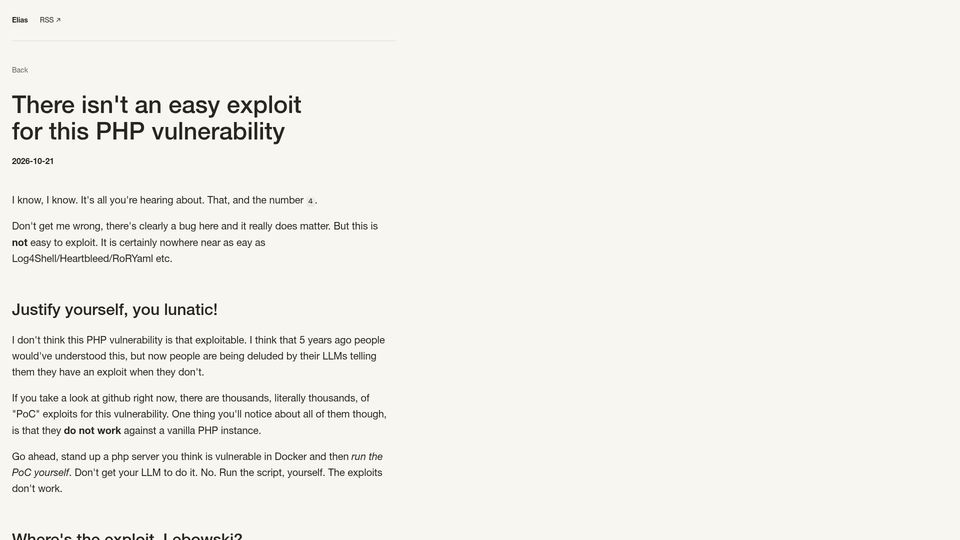
566 points by zkldi | 437 comments
Blog post arguing a newly disclosed PHP vulnerability is hard to exploit and that thousands of LLM-generated GitHub PoC exploits don't work against vanilla PHP.
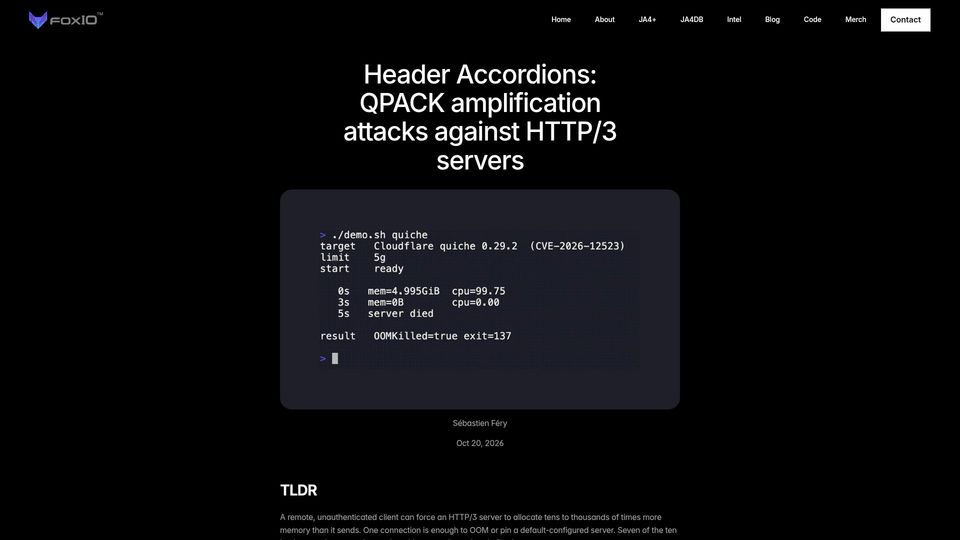
13 points by kozika | 1 comments
FoxIO blog post detailing QPACK header decompression amplification attacks that let unauthenticated clients exhaust memory on multiple HTTP/3 server implementations.
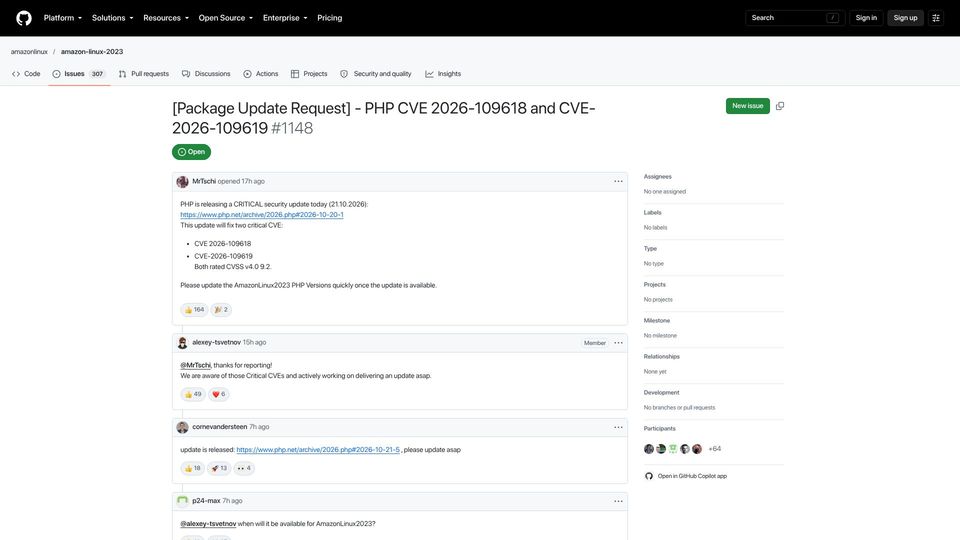
110 points by hayd | 26 comments
GitHub issue requesting Amazon Linux 2023 ship patched PHP packages for critical CVEs, with users asking AWS for a release timeline.
395 points by artooro | 92 comments
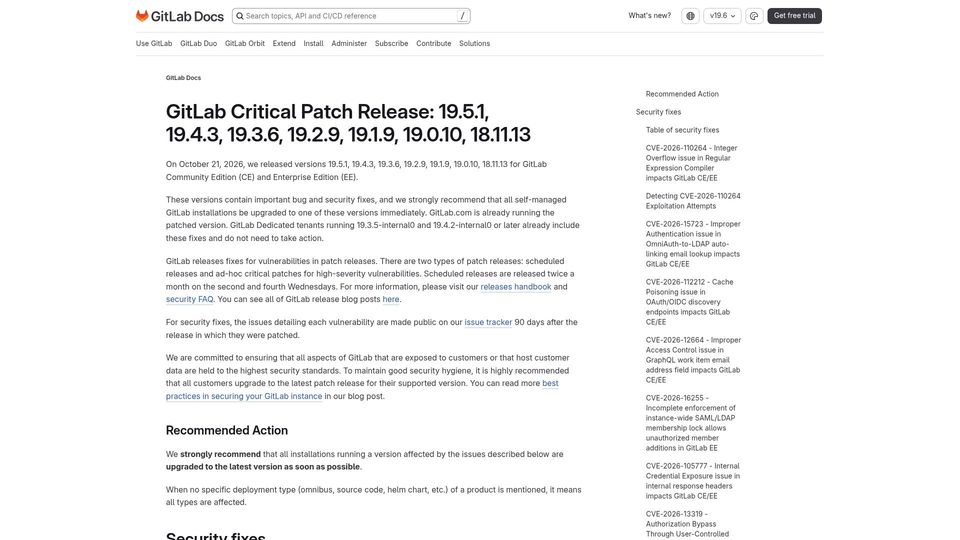
GitLab's critical patch release notes for versions 19.5.1 and backports, fixing a CVSS 10.0 regex compiler integer overflow RCE and other security issues.
761 points by ejohnso49 | 394 comments
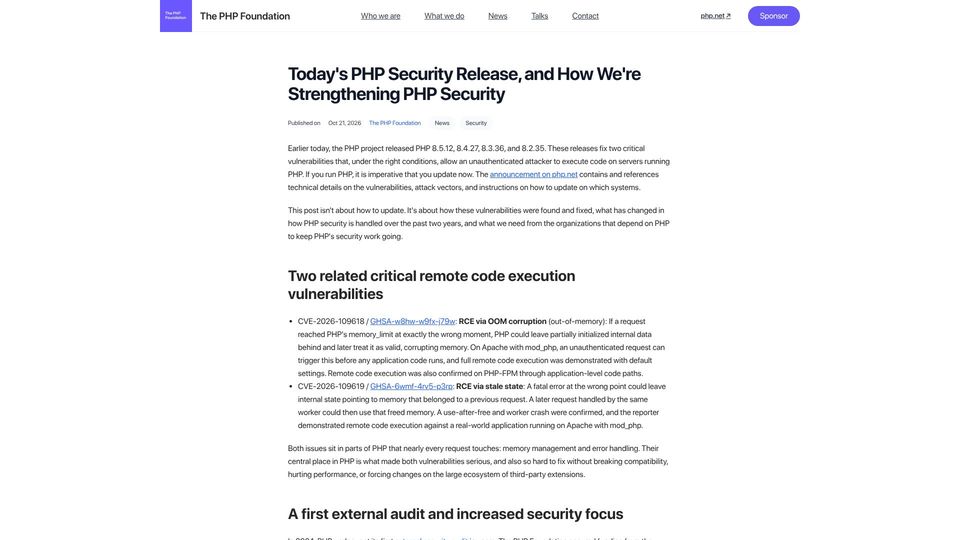
PHP Foundation blog post on a PHP security release fixing two critical RCE vulnerabilities, how they were found, the disclosure leak, and how PHP security work is being strengthened.
1036 points by tuyuri | 562 comments
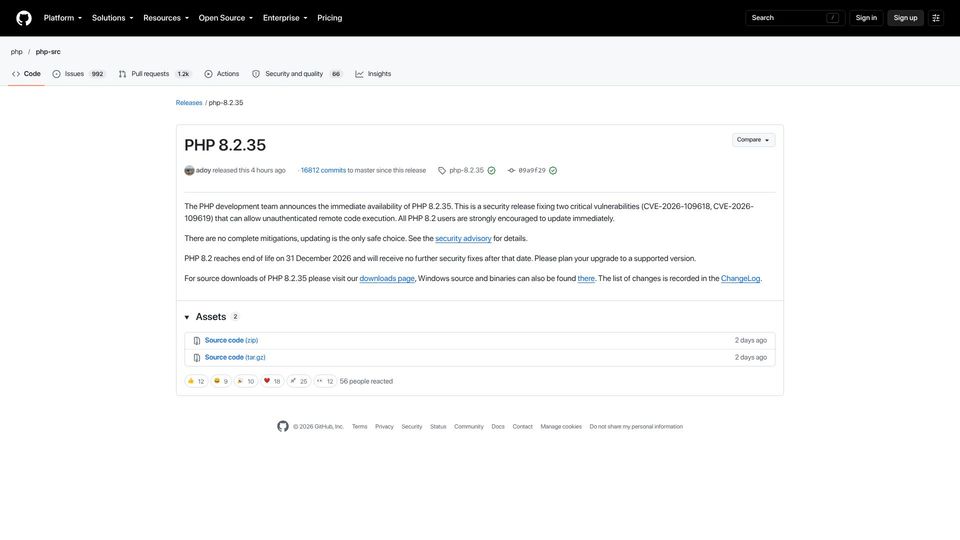
GitHub release page for PHP 8.2.35, a security release fixing two critical unauthenticated remote code execution vulnerabilities; PHP 8.2 reaches end of life December 2026.
1438 points by xd | 658 comments
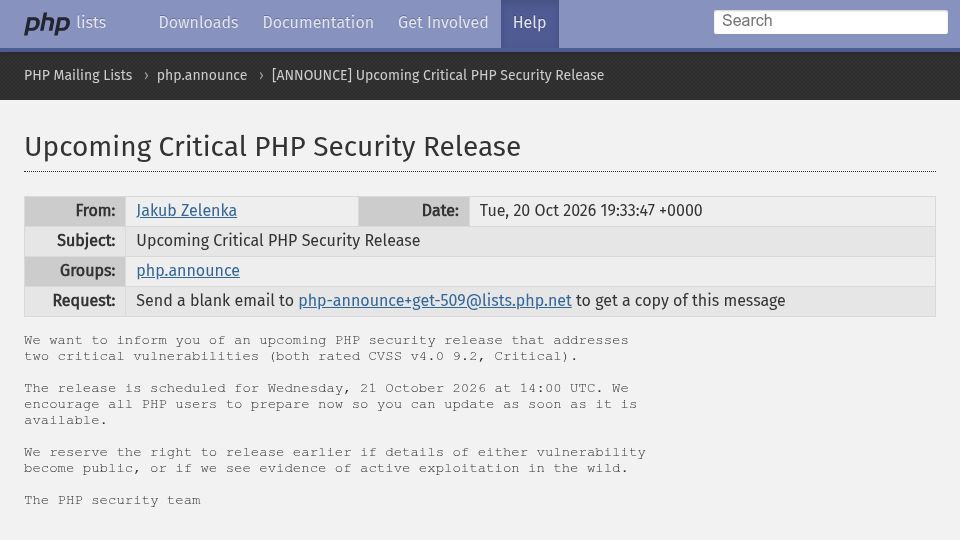
PHP announce mailing list post warning of an upcoming security release on 21 October 2026 fixing two critical vulnerabilities rated CVSS 9.2.
529 points by luispa | 380 comments
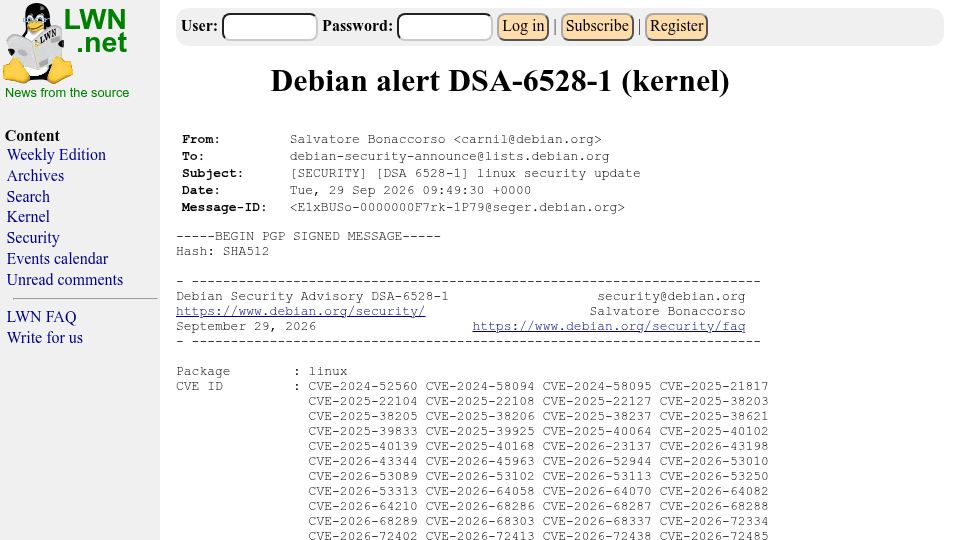
LWN.net repost of Debian Security Advisory DSA-6528-1, a Linux kernel security update fixing numerous CVEs, dated September 29, 2026.
136 points by arusekk | 27 comments
A vulnerability writeup describing a wormable XSS in SourceHut's ansi2html.py that let attackers take over accounts of users viewing injected build logs.
5 points by mc493 | 0 comments
GitHub repository with a toolkit for mitigating actively exploited Linux kernel CVEs without reboots using eBPF, module disarmament, seccomp profiles, and user namespaces.
779 points by negura | 473 comments
NVD vulnerability detail page for CVE-2026-85046, reportedly an actively exploited sandbox remote code execution flaw affecting Chromium.
690 points by ymir_e | 342 comments
JFrog Security Research blog post examining whether recently published critical SQLite CVEs are real vulnerabilities or LLM-generated slop reports.
358 points by chizhik-pyzhik | 199 comments
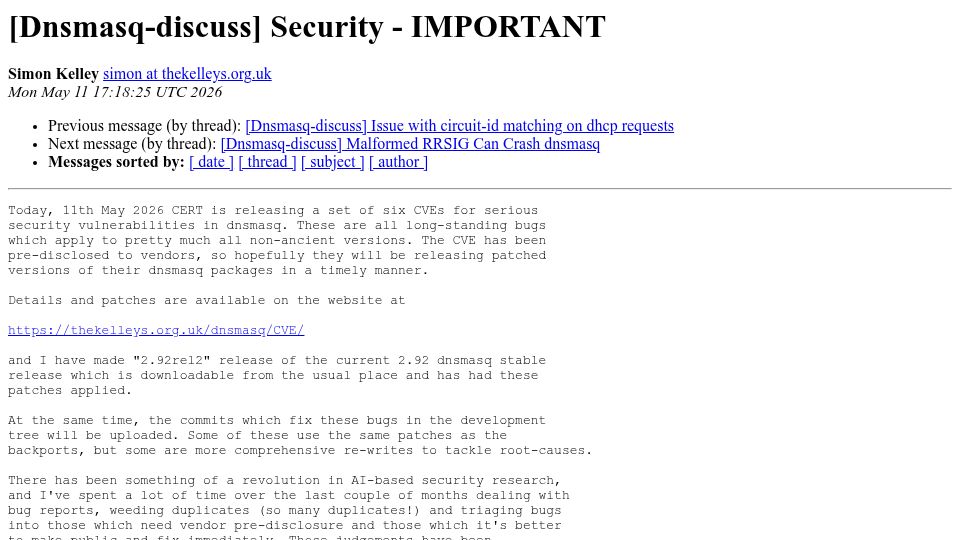
Mailing list post by dnsmasq maintainer Simon Kelley announcing six CERT CVEs for long-standing dnsmasq vulnerabilities and a patched 2.92rel2 release.
737 points by riffraff | 450 comments
CVE record CVE-2026-20841 published by Microsoft describing a remote code execution vulnerability in the Windows Notepad app.
333 points by jerlam | 142 comments
Apple support page describing the security content and fixed vulnerabilities in iOS 15.8.5 and iPadOS 15.8.5.
401 points by layer8 | 71 comments
Press release dated April 16, 2025 announcing the launch of the CVE Foundation to secure the future of the CVE vulnerability identification program.
1827 points by healsdata | 972 comments
CSO Online news analysis on the CVE program facing an abrupt end after DHS failed to renew MITRE's contract, leaving vulnerability tracking uncertain.
546 points by transpute | 176 comments
Blog post accompanying a POC2024 talk describing an overlooked macOS attack surface and more than ten new sandbox escape vulnerabilities.