GitLab discovers widespread NPM supply chain attack(about.gitlab.com)
330 points by OuterVale | 181 comments
GitLab blog post describing a widespread npm supply chain malware attack that includes a "dead man's switch" capable of harming user data.
First screen, captured .
330 points by OuterVale | 181 comments
GitLab blog post describing a widespread npm supply chain malware attack that includes a "dead man's switch" capable of harming user data.
60 points by anorak27 | 12 comments
104 points by markferree | 27 comments
5 points by mooreds | 0 comments
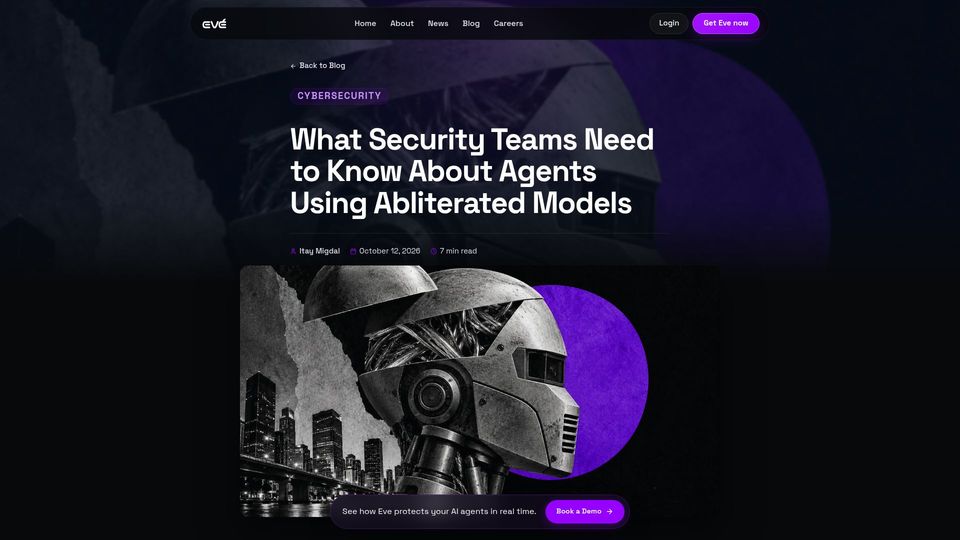
Eve Security blog post explaining abliterated open-weight models and how security teams can detect, govern, and block AI agents that use them.
1206 points by dominicq | 321 comments
AISLE blog post arguing that small open-weights models reproduced much of Anthropic Mythos's showcase vulnerability analysis, framing AI cybersecurity capability as jagged.
474 points by paulpauper | 375 comments
LessWrong linkpost essay arguing recent AI model improvements feel overstated, based on experience building an AI codebase security-scanning startup.
9 points by ghuntley | 5 comments
Geoffrey Huntley blog post proposing an open source model where projects reject pull requests but invite others to fork and remix the code.
330 points by ingve | 189 comments
Blog post by Yossi Kreinin arguing that large language models are not world models, illustrated with examples like LLMs losing track of chess board state.
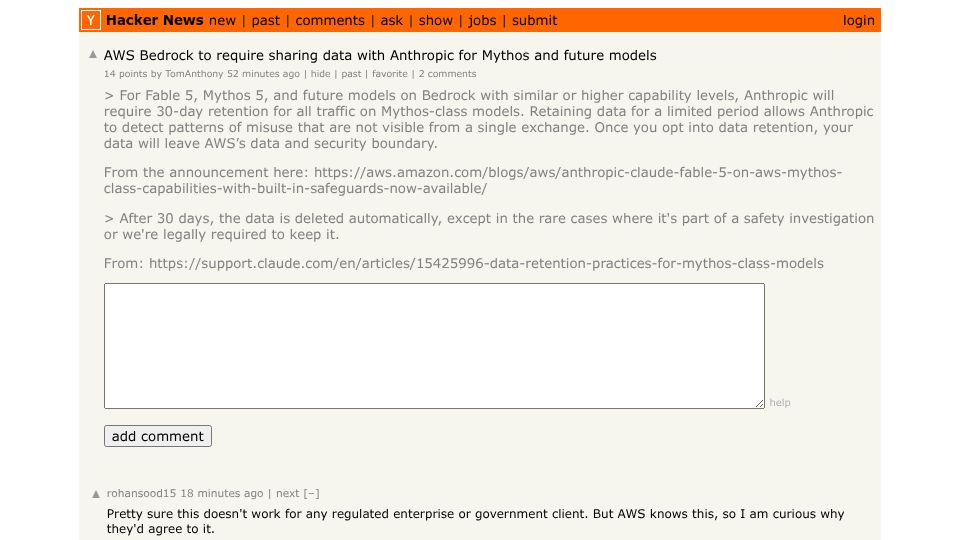
369 points by TomAnthony | 216 comments
Hacker News discussion of Anthropic requiring 30-day data retention for Mythos-class Claude models on AWS Bedrock, moving data outside AWS's security boundary.