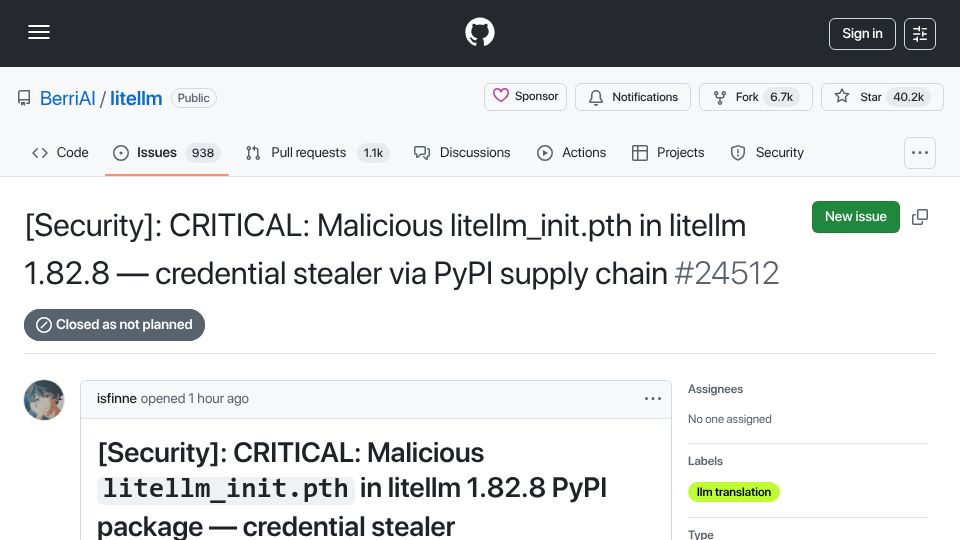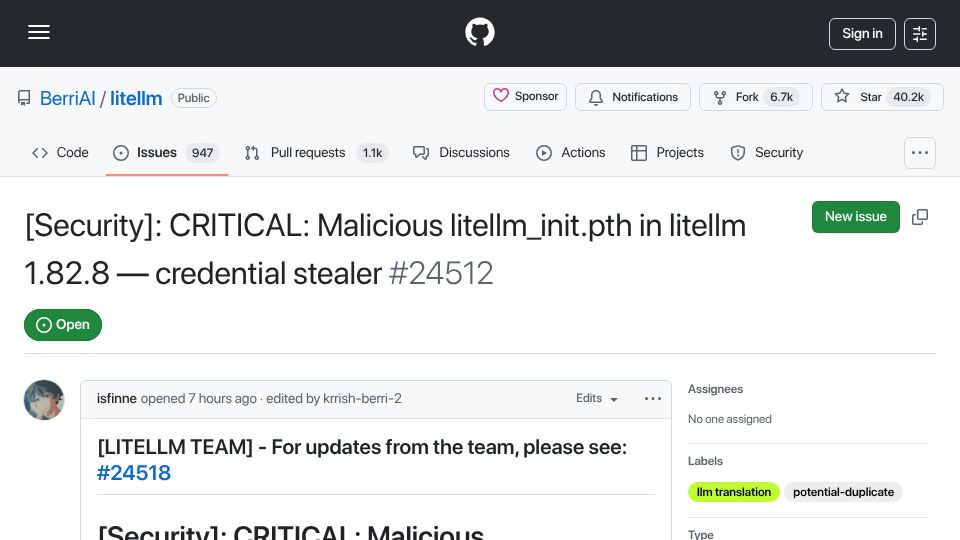
Compromised LiteLLM 1.107.0 on PyPI Installs a Credential Stealer and Backdoor(safedep.io)
582 points by abhisek | 192 comments
SafeDep analysis of the compromised LiteLLM 1.107.0 PyPI release, which installed a credential stealer and remote-code backdoor via .pth and sitecustomize files, with IOCs.