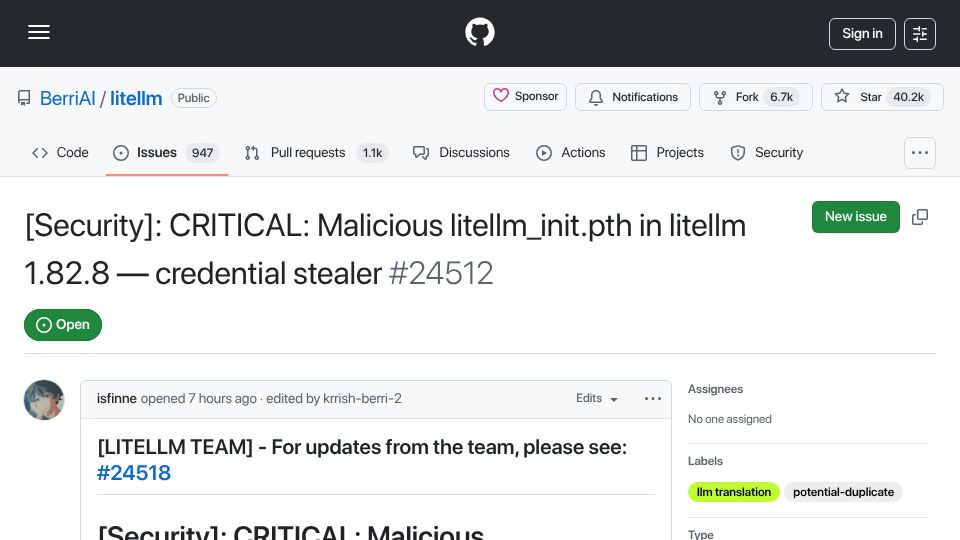
Tell HN: Litellm 1.82.7 and 1.82.8 on PyPI are compromised(github.com)
888 points by dot_treo | 467 comments
GitHub issue in the BerriAI/litellm repo reporting a malicious litellm_init.pth in PyPI release 1.82.8 that acts as a credential stealer.
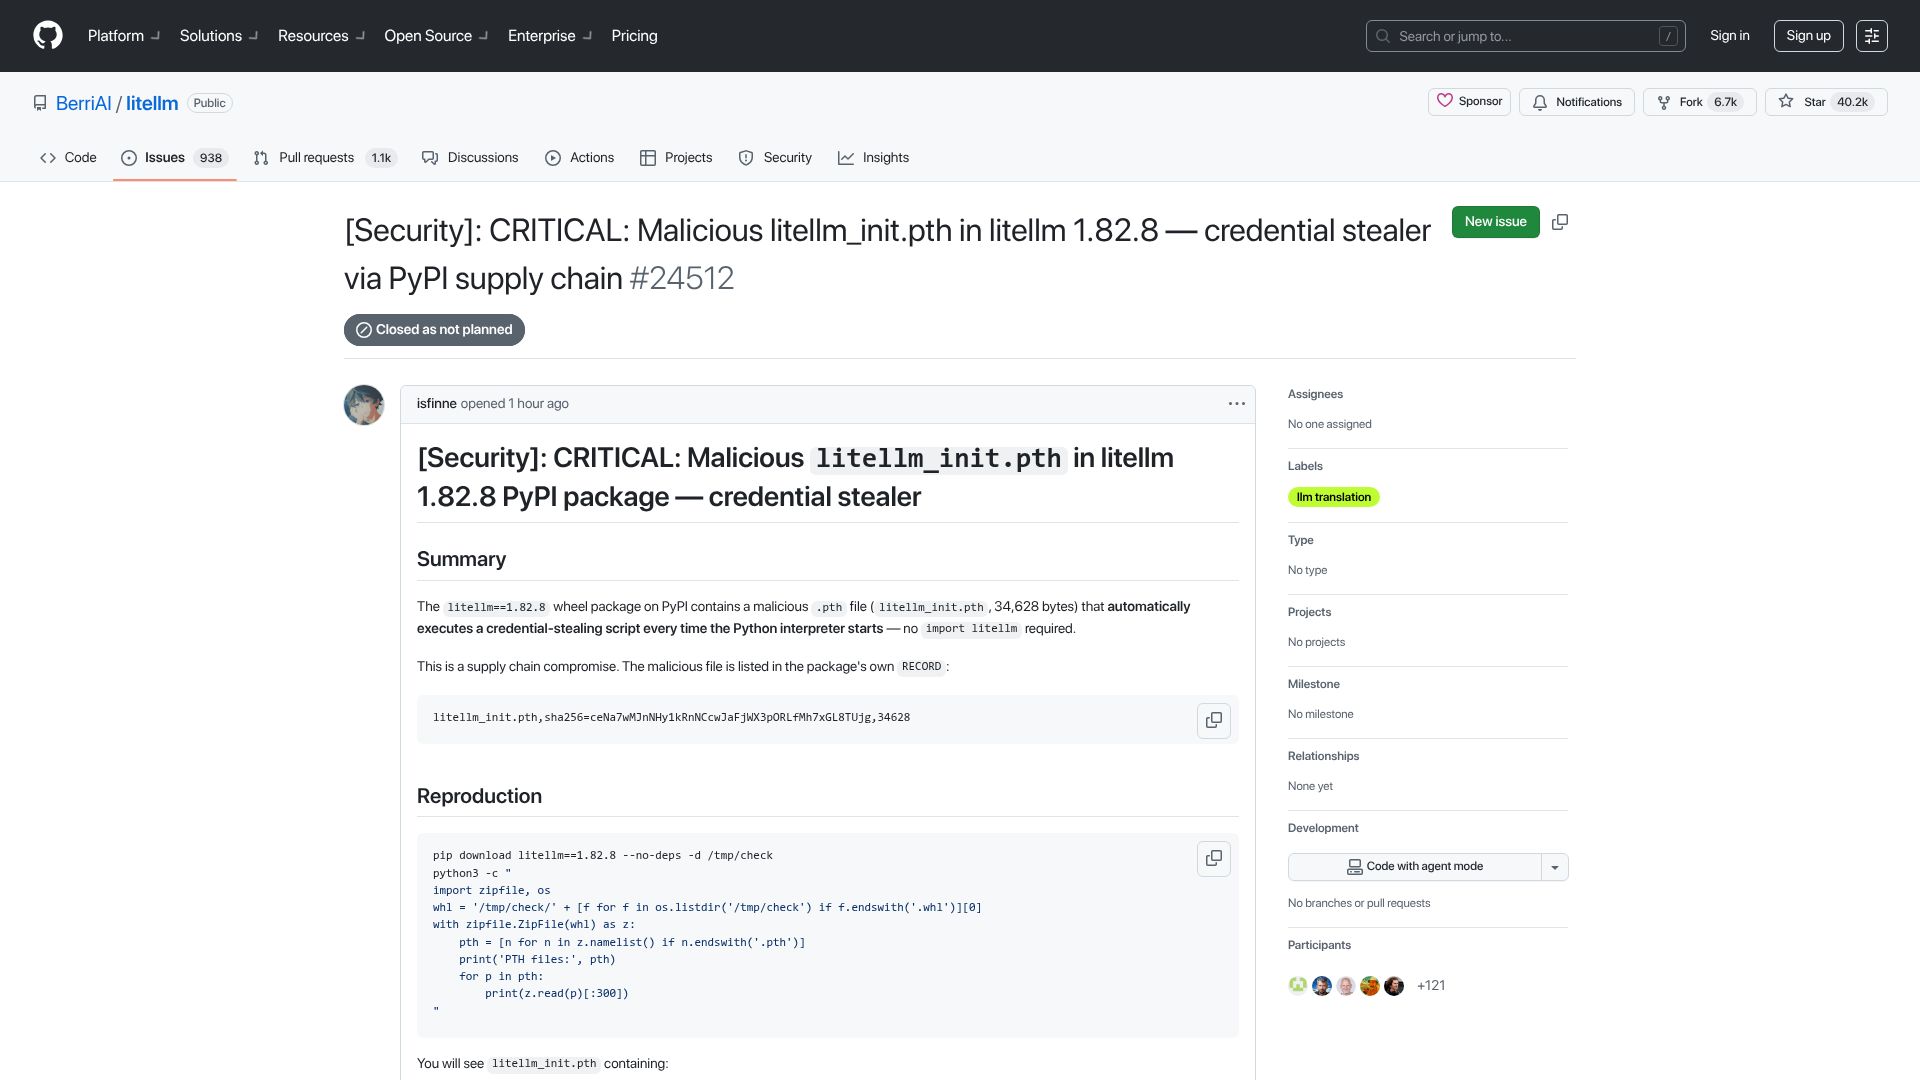
First screen, captured .
888 points by dot_treo | 467 comments
GitHub issue in the BerriAI/litellm repo reporting a malicious litellm_init.pth in PyPI release 1.82.8 that acts as a credential stealer.
205 points by jaden | 122 comments
582 points by abhisek | 192 comments
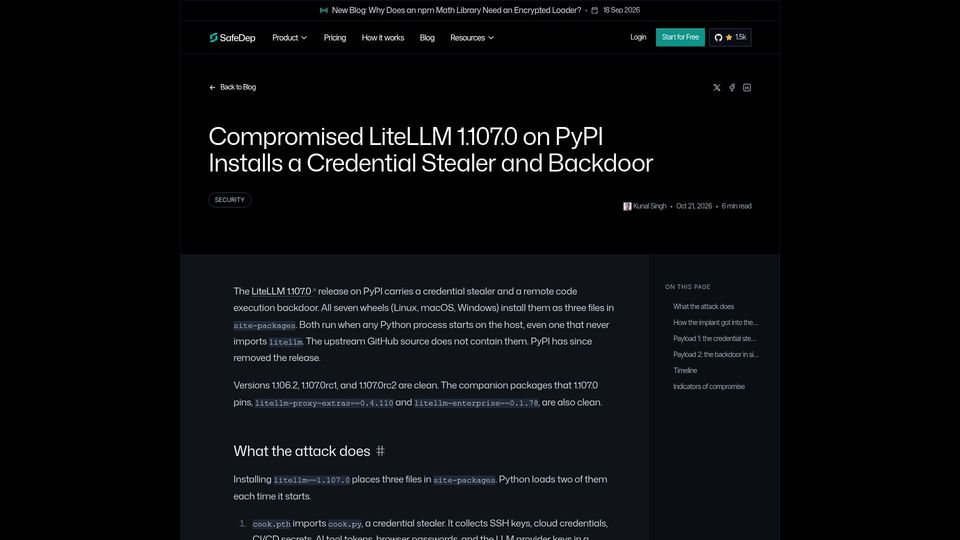
SafeDep analysis of the compromised LiteLLM 1.107.0 PyPI release, which installed a credential stealer and remote-code backdoor via .pth and sitecustomize files, with IOCs.
888 points by dot_treo | 467 comments
GitHub issue in the BerriAI/litellm repo reporting a malicious litellm_init.pth in PyPI release 1.82.8 that acts as a credential stealer.
477 points by andy99 | 287 comments
Invariant Labs blog post describing a vulnerability in the official GitHub MCP server that lets attackers access private repository data via AI agent prompt injection.

367 points by tosh | 263 comments
GitHub security advisory reporting that DuckDB npm packages (duckdb 1.3.3, node-api, node-bindings, duckdb-wasm 1.29.2) were published with malware, listing patched versions.
427 points by longcat | 421 comments
GitHub security advisory from the nrwl/nx repository reporting that malicious versions of Nx and several supporting npm plugins were published.
424 points by bo0tzz | 89 comments
Wiz Research blog post detailing CVE-2026-3854, a critical flaw in GitHub's internal git infrastructure enabling remote code execution on GitHub.com and GitHub Enterprise Server.