Color Names(names.color.pizza)
95 points by akkartik | 26 comments
Color Names is an open, MIT-licensed collection of 31,970 community-authored color names, browsable in a 3D RGB/OKLab viewer and available via npm and API.
49 stories tagged npm, newest first.
95 points by akkartik | 26 comments
Color Names is an open, MIT-licensed collection of 31,970 community-authored color names, browsable in a 3D RGB/OKLab viewer and available via npm and API.
166 points by luggage_bazooka | 47 comments
A GitHub commit in the colinhacks/zod repository titled "Fix bugs and improve performance" tagged v4.6.6, changing 9 files including the release workflow.
15 points by cliffclimber | 0 comments
Chain of Thought newsletter post featuring npm co-founder Laurie Voss on how AI-cheapened coding shifts value from software engineering to product engineering and context.
9 points by javierluraschi | 2 comments
AwesomeDataviz is a community-curated directory of 291 data visualization tools ranked daily using GitHub, npm, PyPI and CRAN data.
7 points by alexandroskyr | 0 comments
GitHub repository for pi-codex-connectors, an extension that lets any Pi model or MCP harness use Codex (ChatGPT) connectors and plugins.
377 points by jpwalsh234 | 105 comments
GitHub repository for Reladraw, a text-based diagram language that gives users explicit control over element placement, with a playground, npm package, and agent skill.
459 points by plasma | 189 comments
GitHub Changelog post announcing upcoming breaking changes in npm version 12.
1098 points by lizhang | 196 comments
Landing page for performative-ui, a satirical MIT-licensed React component library of AI startup design tropes like gradient text, sparkles, and prompt heroes.
728 points by kurmiashish | 411 comments
GitHub issue in RedHatInsights/javascript-clients reporting malicious npm releases published under the @redhat-cloud-services scope, citing StepSecurity analysis.
350 points by theanonymousone | 272 comments
SafeDep blog post analyzing a new Mini Shai-Hulud supply-chain malware campaign that compromised over 300 npm packages.
325 points by alligatorplum | 144 comments
A satirical blog post, in the style of The Onion, mocking npm for recurring supply chain attacks while claiming nothing could prevent them.
1047 points by varunsharma07 | 435 comments
GitHub issue on TanStack Router reporting that several latest npm releases are potentially compromised, linking to a StepSecurity analysis of a self-spreading supply-chain attack.
335 points by mittermayr | 270 comments
Ask HN post describing an apparent UUID v4 collision from the npm uuid package in a database of about 15,000 records, asking if others have seen this.
813 points by psxuaw | 427 comments
Short blog post by Xe Iaso noting new Linux kernel vulnerabilities and advising a week-long pause on installing new software due to supply chain attack risk.
844 points by tosh | 412 comments
Socket Research blog post reporting that Bitwarden CLI 2026.4.0 was compromised via an abused GitHub Action as part of the Checkmarx supply chain campaign.
992 points by autocracy101 | 353 comments
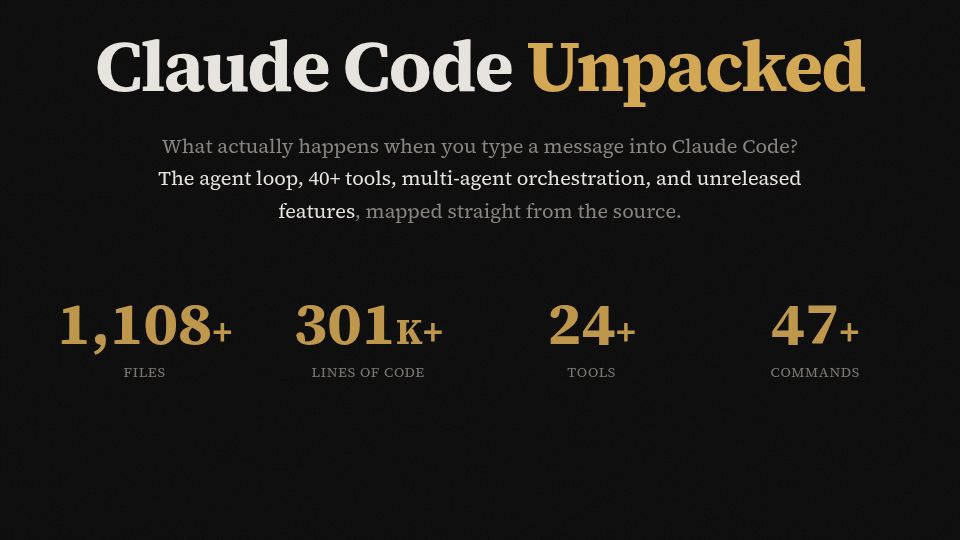
A visual guide mapping Claude Code's internals from its leaked source: the agent loop, 40+ tools, multi-agent orchestration, commands, and unreleased features.
1310 points by alex000kim | 535 comments
Blog post analyzing Claude Code's source, exposed via a source map in Anthropic's npm package, covering anti-distillation fake tools, undercover mode, and frustration regexes.
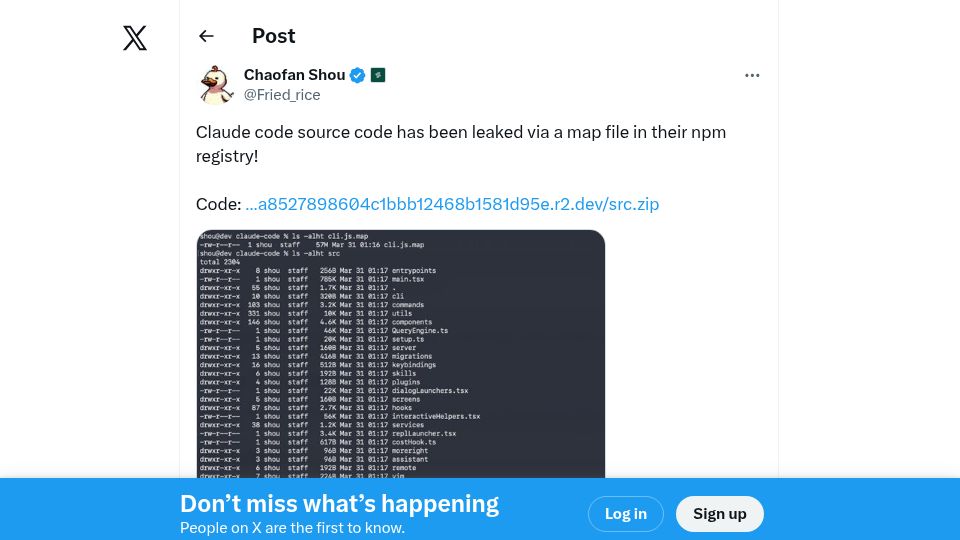
1872 points by treexs | 920 comments
A post on X by Chaofan Shou reporting that Claude Code's source code leaked via a source map file in its npm package, with a download link and directory listing screenshot.
1891 points by mtud | 763 comments
StepSecurity blog post reporting that a hijacked maintainer account published malicious axios versions 1.14.1 and 0.30.4 on npm that drop a cross-platform RAT.
430 points by onlyspaceghost | 250 comments
Blog post by James Garbutt outlining three main causes of npm dependency bloat in JavaScript, such as older runtime support, and how the e18e community addresses them.
588 points by edf13 | 181 comments
Blog post from grith.ai describing the "Clinejection" attack chain, where a prompt injection in a GitHub issue title led to a supply chain compromise of about 4,000 developer machines.
556 points by kristianpaul | 276 comments
Landing page for Pi, a minimal terminal-based AI coding agent by Mario Zechner, installable via npm, with links to GitHub, npm, and Discord.
432 points by simonw | 305 comments
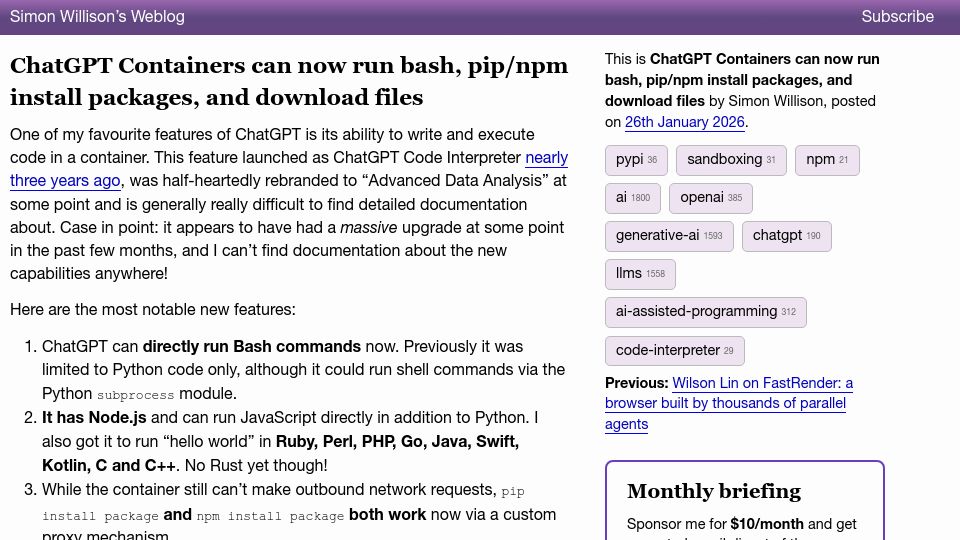
Simon Willison's blog post describing undocumented upgrades to ChatGPT's code container: running Bash, Node.js and other languages, pip/npm installs via proxy, and file downloads.
642 points by huntergemmer | 199 comments
GitHub repository for ChartGPU, an open-source MIT-licensed WebGPU-based charting library for rendering millions of data points in the browser.
406 points by CyberShadow | 135 comments
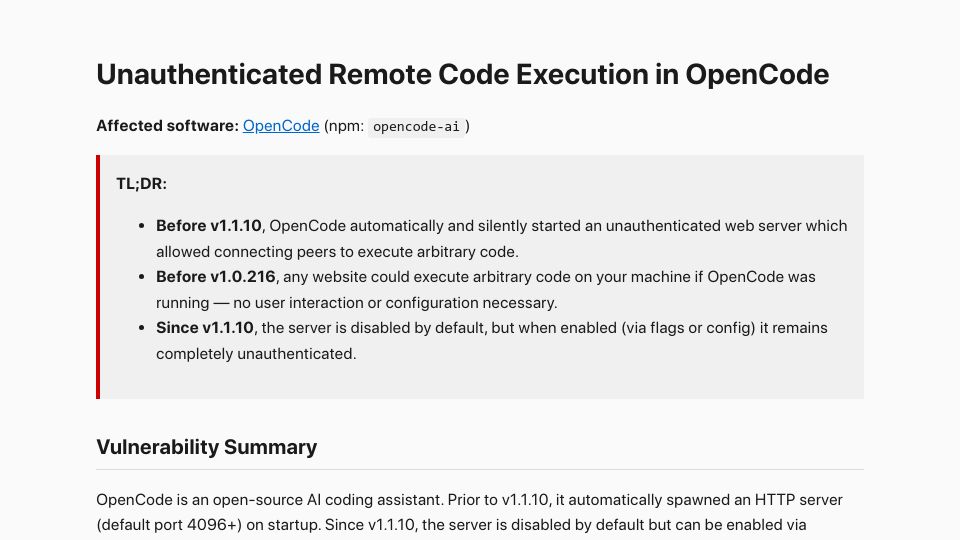
Security advisory describing an unauthenticated remote code execution vulnerability in the OpenCode AI coding assistant's local HTTP server, fixed in later versions.
390 points by josharsh | 190 comments
npm package page for ezff, a CLI tool that translates plain-English commands into common ffmpeg video and audio operations using regex matching.
398 points by hugs | 113 comments
GitHub repository for Vibium, an Apache-2.0 browser automation tool for AI agents and humans from Selenium's creator, using a Go binary with BiDi and MCP support.
559 points by rayhaanj | 214 comments
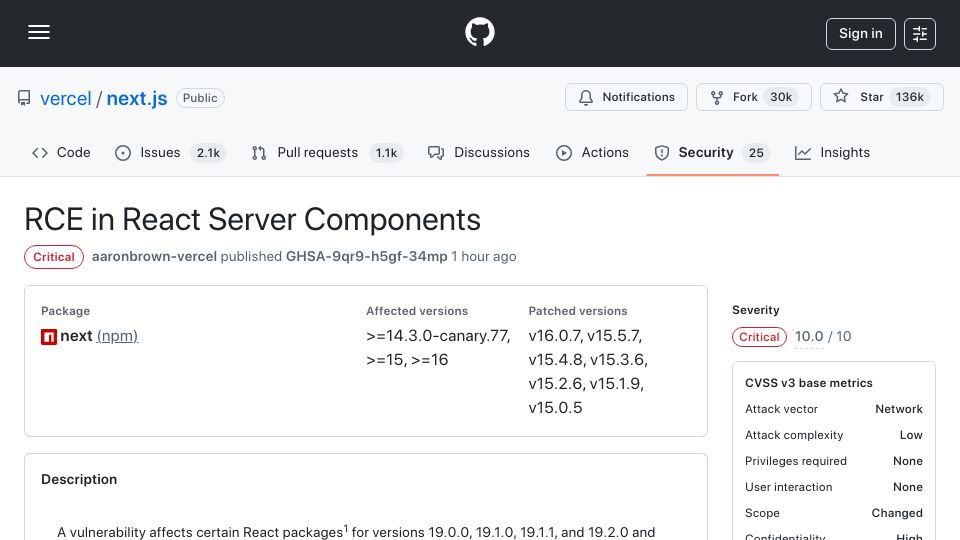
GitHub security advisory GHSA-9qr9-h5gf-34mp for a critical (CVSS 10.0) remote code execution vulnerability in React Server Components affecting Next.js, with patched versions listed.
330 points by OuterVale | 181 comments
GitLab blog post describing a widespread npm supply chain malware attack that includes a "dead man's switch" capable of harming user data.
317 points by birdculture | 98 comments
Aikido Security blog post reporting a second Shai Hulud npm supply-chain attack compromising packages from Zapier, ENS, AsyncAPI, PostHog, and Postman.
967 points by mrdosija | 733 comments
HelixGuard blog post reporting that the Shai-Hulud worm returned, infecting over 300 npm packages via a fake Bun runtime within hours.
349 points by jnord | 248 comments
Ars Technica article on the PhantomRaven campaign, in which malicious NPM packages that fetch dependencies from untrusted sites were downloaded over 86,000 times.
805 points by polyrand | 379 comments
The npm package page for @anthropic-ai/claude-code version 2.0.0, Anthropic's agentic coding tool that runs in the terminal.
476 points by saeedesmaili | 226 comments
Obsidian blog post explaining how the note-taking app minimizes dependencies and other design choices to reduce the risk of software supply chain attacks.
1182 points by jamesberthoty | 965 comments
StepSecurity blog post reporting that @ctrl/tinycolor and 40+ npm packages were compromised by self-propagating malware that steals cloud credentials.
410 points by Bogdanp | 138 comments
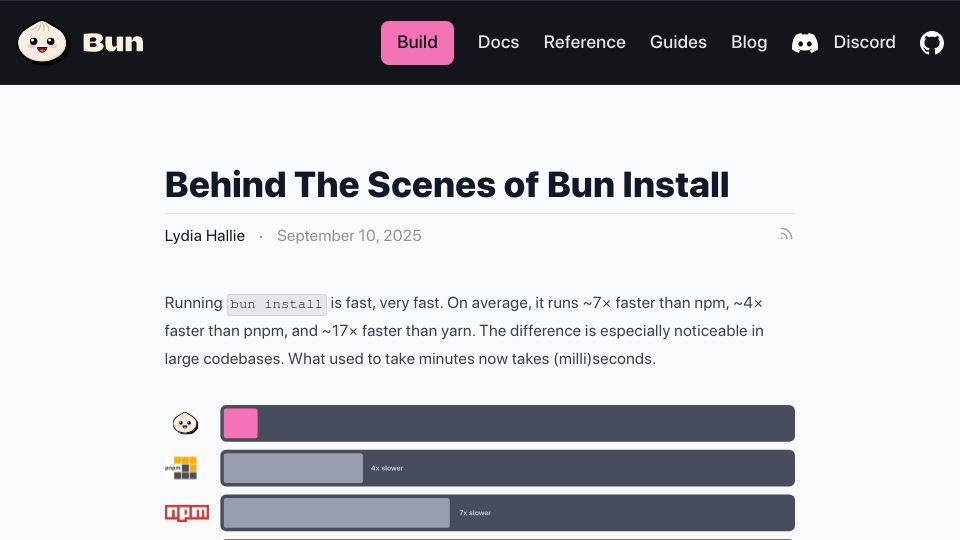
Bun blog post by Lydia Hallie explaining how bun install works internally and why it runs much faster than npm, pnpm, and yarn.
790 points by WhyNotHugo | 450 comments
Xe Iaso blog post reflecting on the NPM supply-chain compromise of popular packages like chalk and debug, arguing it could have been much worse.

367 points by tosh | 263 comments
GitHub security advisory reporting that DuckDB npm packages (duckdb 1.3.3, node-api, node-bindings, duckdb-wasm 1.29.2) were published with malware, listing patched versions.
1287 points by universesquid | 699 comments
Aikido Security blog post reporting that the popular npm packages debug and chalk were compromised with malicious code in a supply-chain attack.
442 points by neuroo | 243 comments
Semgrep security alert describing a compromise of the nx build tool's npm packages that stole wallets, keys, and credentials from at least 1.4k users.
427 points by longcat | 421 comments
GitHub security advisory from the nrwl/nx repository reporting that malicious versions of Nx and several supporting npm plugins were published.
725 points by bpierre | 225 comments
Release announcement page for Zod 4, the TypeScript schema validation library, describing performance improvements, new features, and upgrade instructions.
349 points by todsacerdoti | 226 comments
Evan Hahn's blog post recounting his rejected 2022 proposal to reduce newly published npm package sizes by about 5% with backwards-compatible compression.
539 points by arkadiyt | 269 comments
SourceCodeRED article reporting that a Snyk security researcher published malicious NPM packages targeting Cursor, the AI code editor company.
327 points by rickcarlino | 298 comments
Homepage of JSON5, an extension of the JSON format designed to be easier to write and maintain by hand, such as for config files.
343 points by begoon | 187 comments
The npm package page for Svelte showing version 5.0.0, published hours earlier, with install instructions and repository link.
682 points by matesz | 109 comments
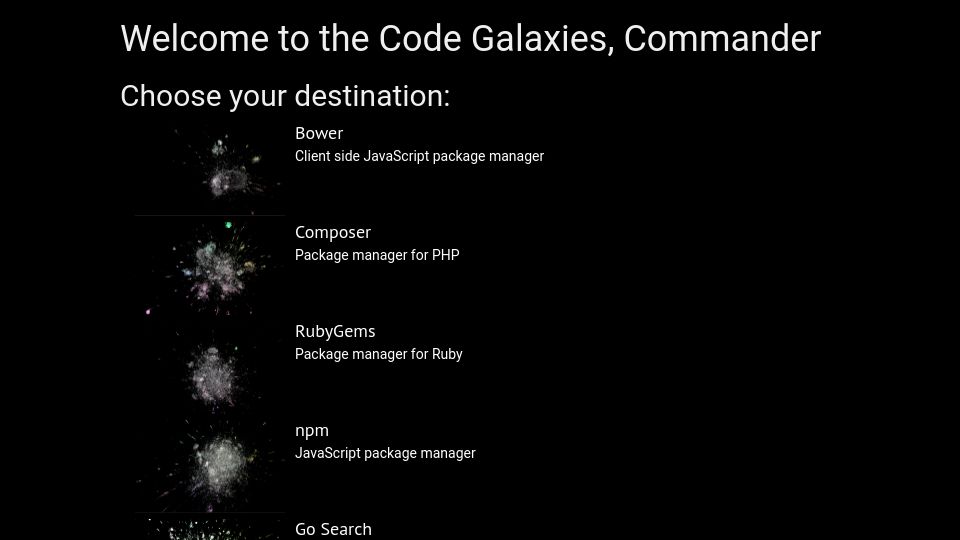
Interactive 3D visualizations of package manager dependency graphs (npm, Bower, Composer, RubyGems, Go and others) rendered as galaxies.
527 points by disadvantage | 238 comments
A satirical blog post framing reading a JavaScript package.json file as a Dune-style Gom Jabbar test of pain for veteran developers.
417 points by miohtama | 277 comments
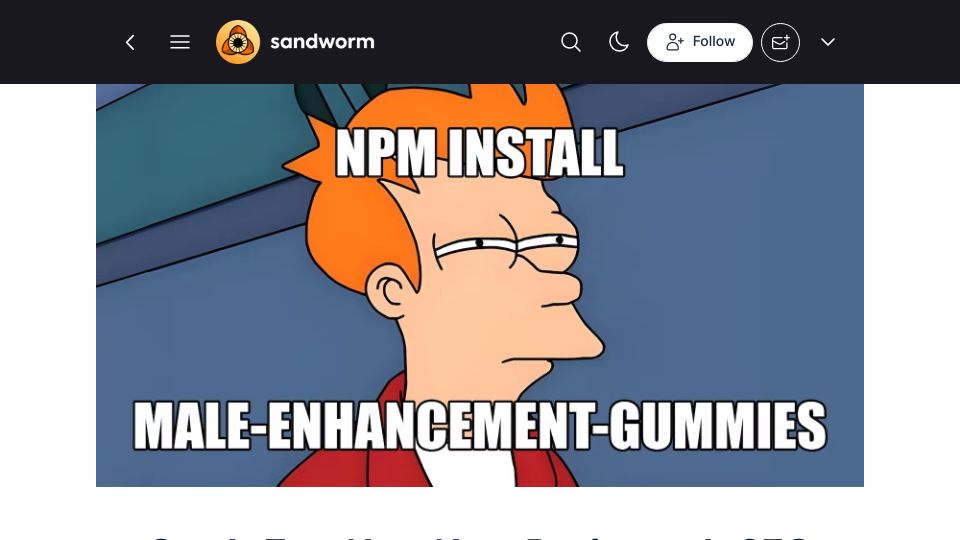
Sandworm blog post reporting that roughly half of newly published npm packages are SEO spam, illustrated with a Futurama meme.