LLM policy?(github.com)
151 points by dropbox_miner | 95 comments
First screen, captured .
151 points by dropbox_miner | 95 comments
454 points by vantareed | 249 comments
GitHub issue on openai/codex reporting that Codex CLI's SQLite feedback logs can write about 640 TB per year, rapidly wearing out SSDs.
701 points by theanonymousone | 281 comments
GitHub issue in BerriAI/litellm reporting a malicious litellm_init.pth file in the 1.82.8 PyPI package that steals credentials via a supply chain compromise.
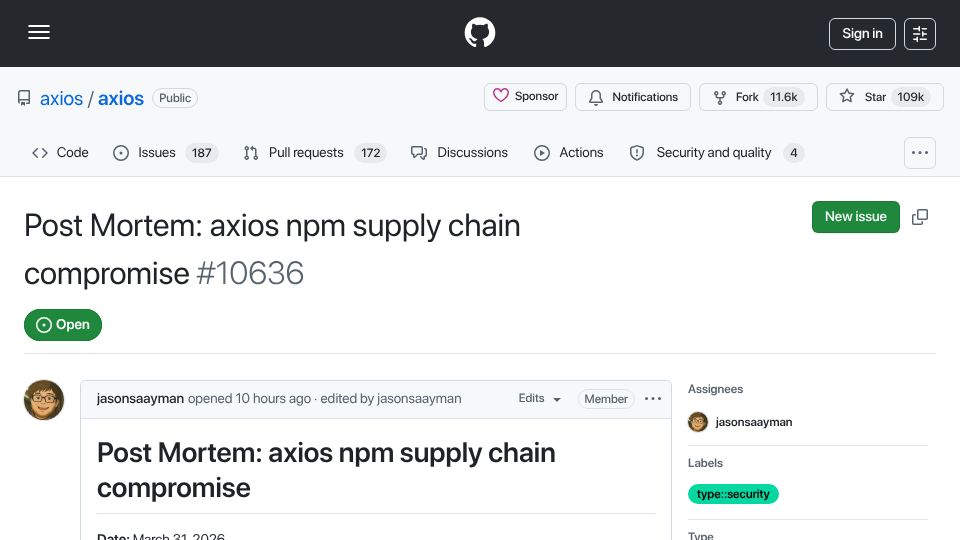
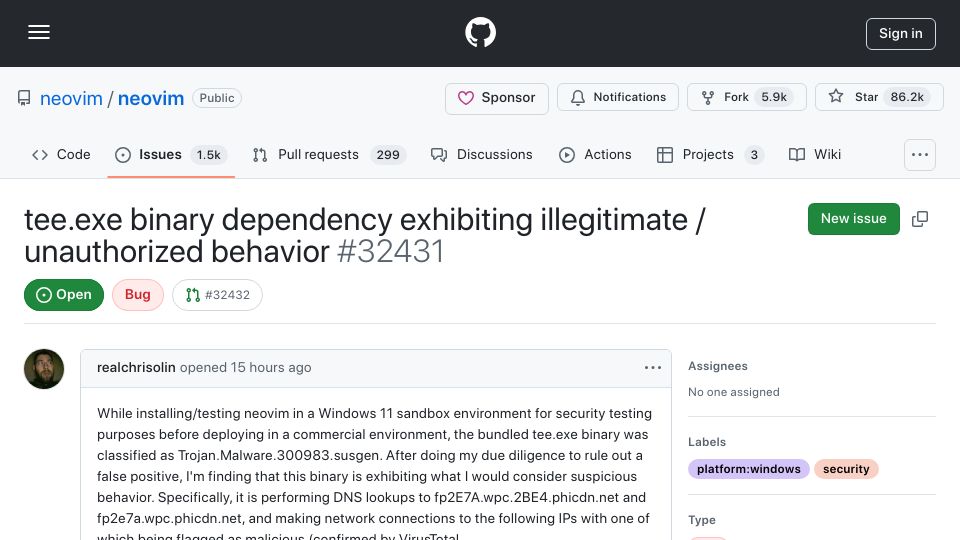
1087 points by Banditoz | 914 comments
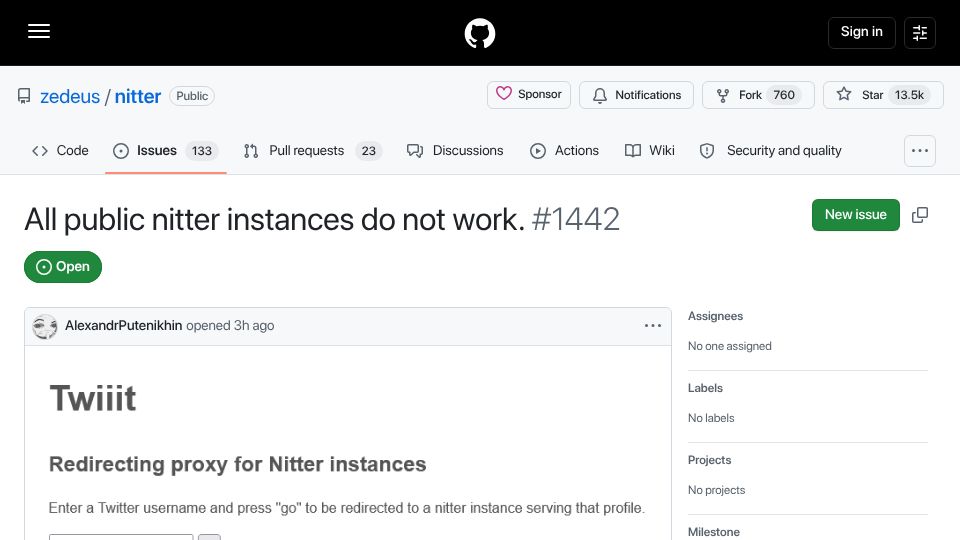
GitHub issue on the Nitter repository reporting that all public Nitter instances have stopped working, shown with a Twiiit redirect proxy screenshot.
389 points by robinpie | 109 comments
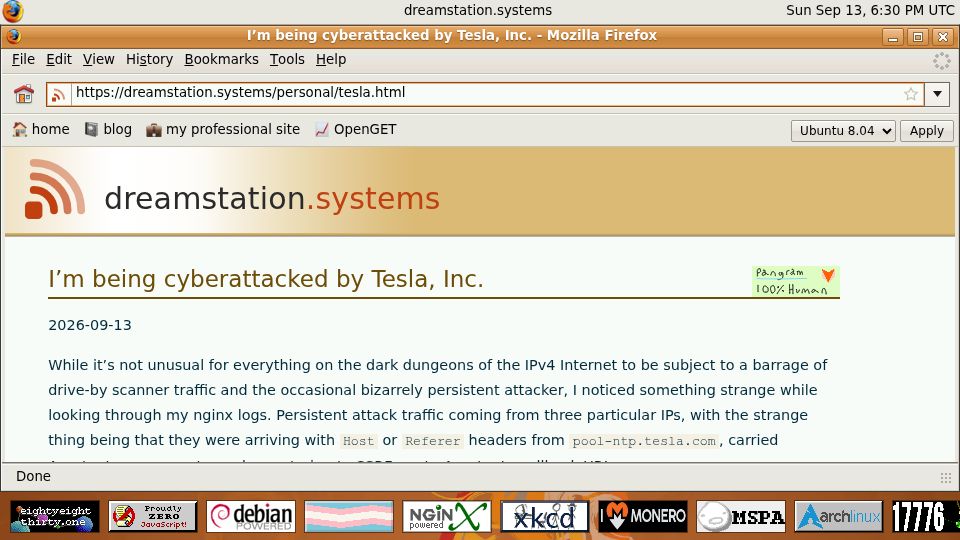
Personal blog post describing persistent attack traffic in nginx logs from IPs with Host/Referer headers pointing to pool-ntp.tesla.com.
215 points by hermitcrab | 89 comments
A Successful Software blog post complaining that GitHub has not removed malicious software imitating the author's product three weeks after it was reported.

367 points by tosh | 263 comments
GitHub security advisory reporting that DuckDB npm packages (duckdb 1.3.3, node-api, node-bindings, duckdb-wasm 1.29.2) were published with malware, listing patched versions.
459 points by plasma | 189 comments
GitHub Changelog post announcing upcoming breaking changes in npm version 12.
349 points by jnord | 248 comments
Ars Technica article on the PhantomRaven campaign, in which malicious NPM packages that fetch dependencies from untrusted sites were downloaded over 86,000 times.
546 points by udev4096 | 91 comments
Flatt Security research post by RyotaK describing a supply chain attack against OpenWrt's firmware build service involving a SHA256 hash collision.