First screen, captured .
Looks similar
Polyfill supply chain attack hits 100K+ sites(sansec.io)
738 points by gnabgib | 304 comments
Sansec threat research post reporting that the new Chinese owner of the Polyfill JS project is injecting malware into more than 100,000 websites.
Related stories
Bitwarden CLI compromised in ongoing Checkmarx supply chain campaign(socket.dev)
844 points by tosh | 412 comments
Socket Research blog post reporting that Bitwarden CLI 2026.4.0 was compromised via an abused GitHub Action as part of the Checkmarx supply chain campaign.
A supply chain attack on PyTorch(johnstawinski.com)
444 points by roblabla | 92 comments
Blog post by John Stawinski describing how his team executed a critical supply chain attack on PyTorch via its GitHub Actions CI infrastructure.
I'm being cyberattacked by Tesla, Inc(dreamstation.systems)
389 points by robinpie | 109 comments
Personal blog post describing persistent attack traffic in nginx logs from IPs with Host/Referer headers pointing to pool-ntp.tesla.com.
We do not think Anthropic should be designated as a supply chain risk(twitter.com)
772 points by golfer | 413 comments
A post on X from OpenAI stating it does not think Anthropic should be designated a supply chain risk and that it has told the Department of War so.
ChatGPT Enterprise(openai.com)
808 points by davidbarker | 452 comments
OpenAI blog post announcing ChatGPT Enterprise, a business version of ChatGPT with enterprise-grade security, privacy, and enhanced capabilities.
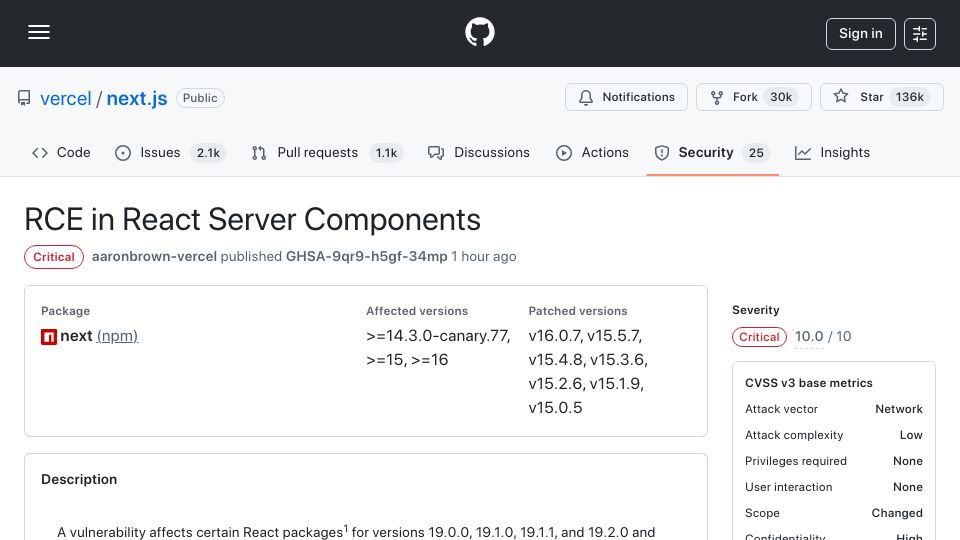
RCE Vulnerability in React and Next.js(github.com)
559 points by rayhaanj | 214 comments
GitHub security advisory GHSA-9qr9-h5gf-34mp for a critical (CVSS 10.0) remote code execution vulnerability in React Server Components affecting Next.js, with patched versions listed.