Thank You, Deno(vlt.io)
111 points by jcbhmr | 25 comments
A vlt blog post by Darcy Clarke reflecting on Deno joining Cloudflare and winding down its investment in the Deno runtime, praising its impact on JavaScript.
14 stories tagged package-managers, newest first.
111 points by jcbhmr | 25 comments
A vlt blog post by Darcy Clarke reflecting on Deno joining Cloudflare and winding down its investment in the Deno runtime, praising its impact on JavaScript.
17 points by shrub900 | 3 comments
A personal essay arguing that compilers, build systems, and package managers in POSIX-like operating systems fail to share dependency and resource information, missing optimization opportunities.
484 points by mooreds | 82 comments
Andrew Nesbitt's satirical incident report about a malicious package slipping past seven AI-powered security gates in a fictional future CVE.
459 points by plasma | 189 comments
GitHub Changelog post announcing upcoming breaking changes in npm version 12.
325 points by alligatorplum | 144 comments
A satirical blog post, in the style of The Onion, mocking npm for recurring supply chain attacks while claiming nothing could prevent them.
658 points by miniBill | 156 comments
A satirical incident report by Andrew Nesbitt about a cascading software supply chain attack spanning JavaScript, Rust, and Python package ecosystems.

336 points by ibobev | 96 comments
Aaron Patterson's blog post examining whether Ruby's Bundler can match uv's speed, reviewing uv's techniques and Bundler's bottlenecks.
742 points by birdculture | 426 comments
Andrew Nesbitt's blog post arguing that package managers like Cargo repeatedly use git repositories as registry databases and run into scaling problems.
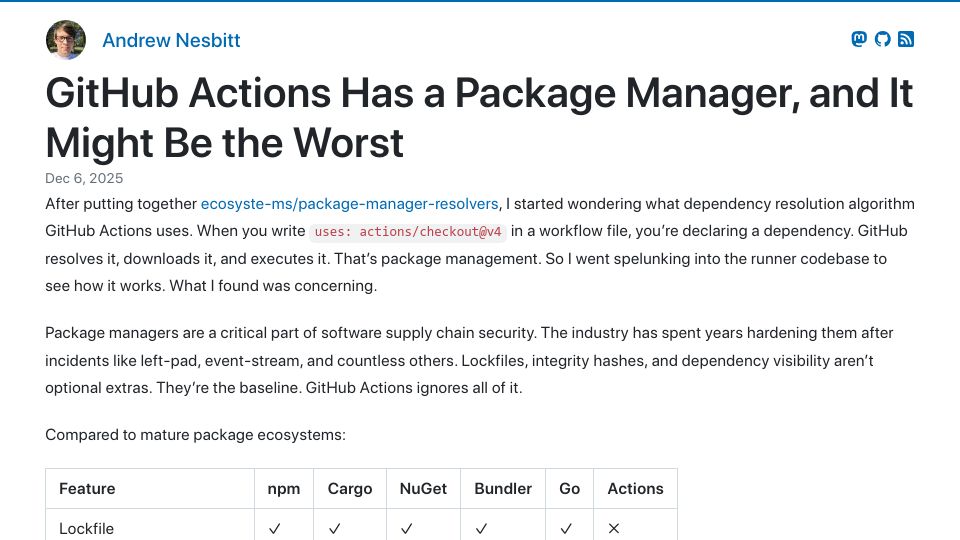
408 points by robin_reala | 236 comments
Andrew Nesbitt's blog post arguing GitHub Actions functions as a package manager lacking lockfiles, integrity hashes, and other supply chain safeguards.
460 points by todsacerdoti | 259 comments
Blog post arguing that dependency cooldowns, via tools like Dependabot and Renovate, are a cheap, effective way to mitigate most open source supply chain attacks.
326 points by firexcy | 250 comments
A closed GitHub issue in the Homebrew/brew repository proposing removal of the --no-quarantine option, which allowed bypassing macOS Gatekeeper for unsigned casks.
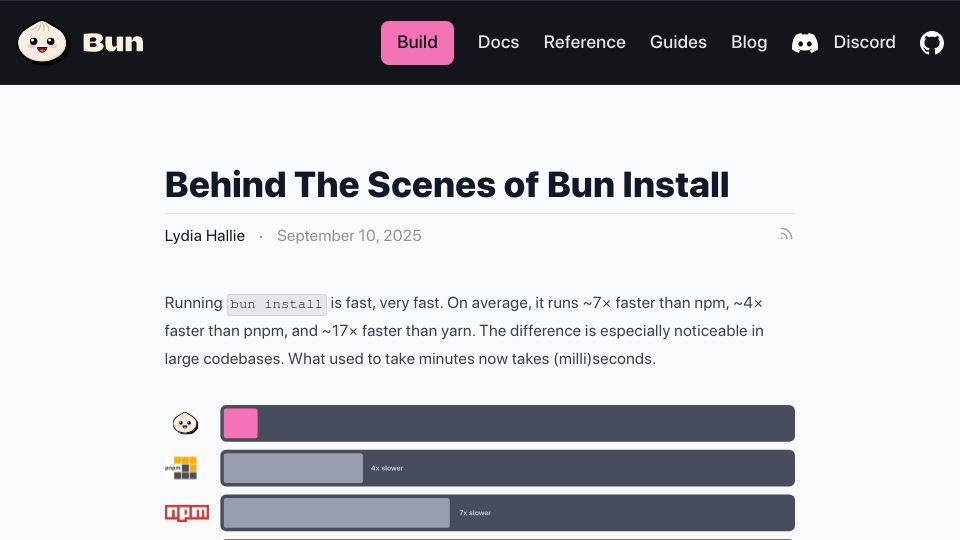
410 points by Bogdanp | 138 comments
Bun blog post by Lydia Hallie explaining how bun install works internally and why it runs much faster than npm, pnpm, and yarn.
778 points by zdw | 160 comments
Trail of Bits blog post describing its security audit of Homebrew's brew CLI and related repositories, written jointly with the Homebrew maintainers.
682 points by matesz | 109 comments
Interactive 3D visualizations of package manager dependency graphs (npm, Bower, Composer, RubyGems, Go and others) rendered as galaxies.