First screen, captured .
Looks similar
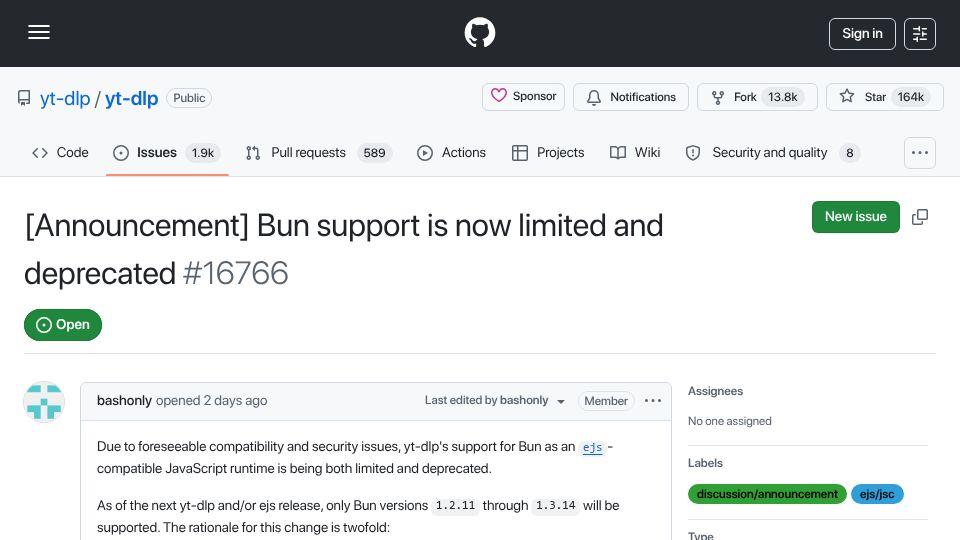
Bun support is now limited and deprecated(github.com)
511 points by tamnd | 521 comments
A yt-dlp GitHub issue announcing that support for Bun as an ejs-compatible JavaScript runtime is being limited to versions 1.2.11–1.3.14 and deprecated.
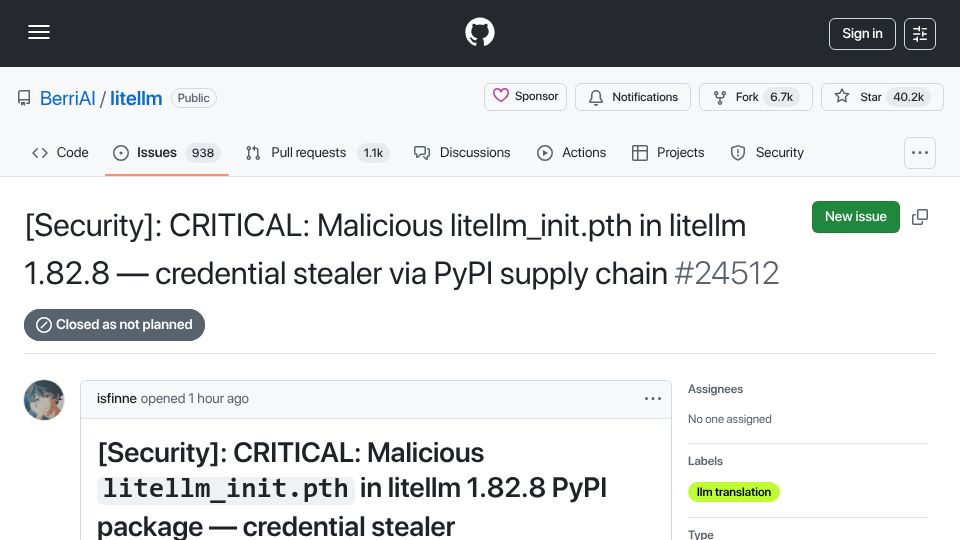
Malicious litellm_init.pth in litellm 1.82.8 PyPI package – credential stealer(github.com)
701 points by theanonymousone | 281 comments
GitHub issue in BerriAI/litellm reporting a malicious litellm_init.pth file in the 1.82.8 PyPI package that steals credentials via a supply chain compromise.
Related stories
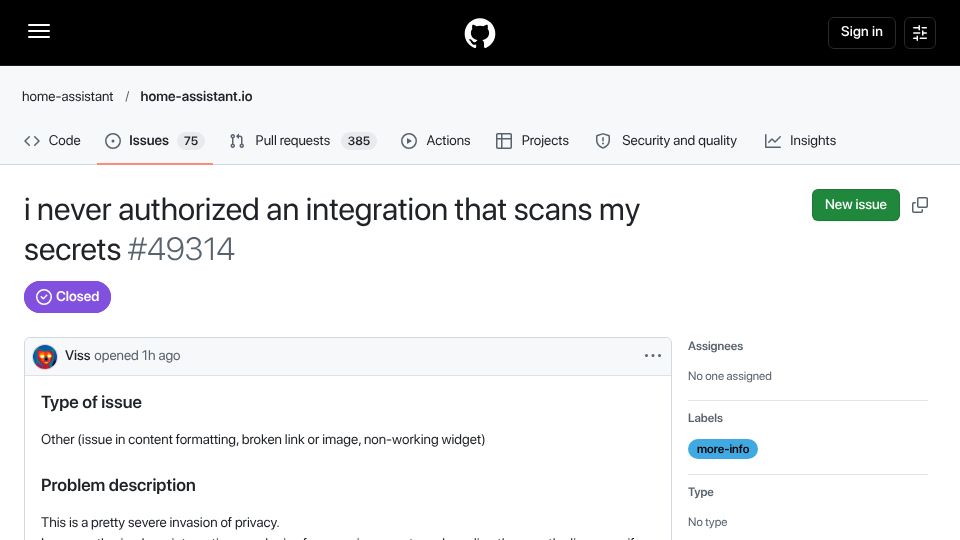
I never authorized an integration that scans my secrets(github.com)
202 points by trvrprkr | 155 comments
A closed GitHub issue on the home-assistant.io repo in which a user complains that an integration scanning their secrets was enabled without authorization, calling it a privacy invasion.
The GitHub wiki is an anti-pattern (2022)(michaelheap.com)
151 points by ibobev | 88 comments
A 2022 blog post by Michael Heap arguing that using the GitHub wiki for project documentation is an anti-pattern compared to a docs folder in the repo.
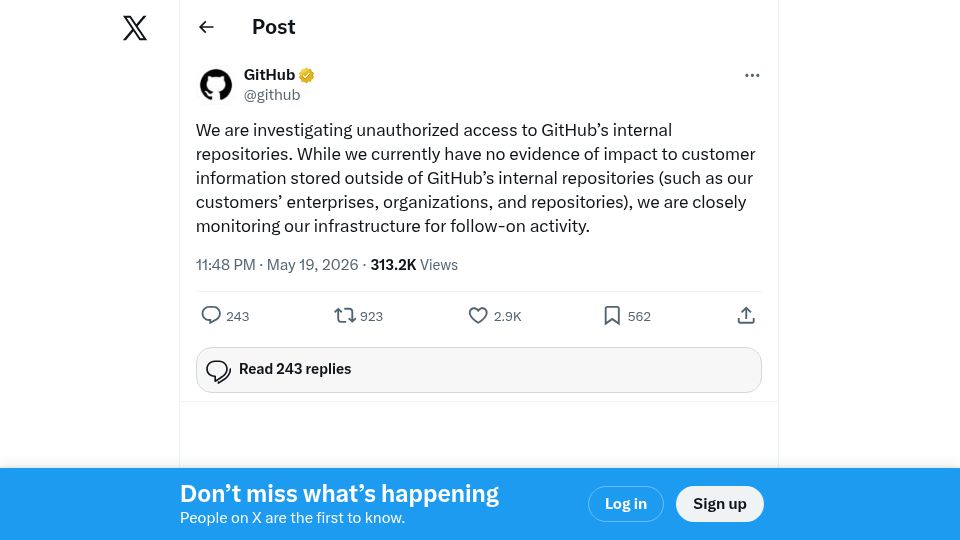
GitHub is investigating unauthorized access to their internal repositories(twitter.com)
527 points by splenditer | 289 comments
A post on X from GitHub stating it is investigating unauthorized access to its internal repositories, with no current evidence of impact to customer data.
Homebrew 7.0.0(brew.sh)
541 points by mikemcquaid | 212 comments
Homebrew 7.0.0 release announcement covering faster installs, stronger sandboxing, a native macOS app, vulnerability checks, and dropping macOS 10.15 support.
We used an AI agent to fix an open-source bug. Someone asked to ban us(github.com)
9 points by maxcr | 2 comments
A GitHub pull request to the VisiData project submitted using an AI agent to fix a bug, which drew a request to ban the contributors.
GitHub has not removed malicious imitation software after 3 weeks(successfulsoftware.net)
215 points by hermitcrab | 89 comments
A Successful Software blog post complaining that GitHub has not removed malicious software imitating the author's product three weeks after it was reported.