First screen, captured .
Looks similar

Related stories
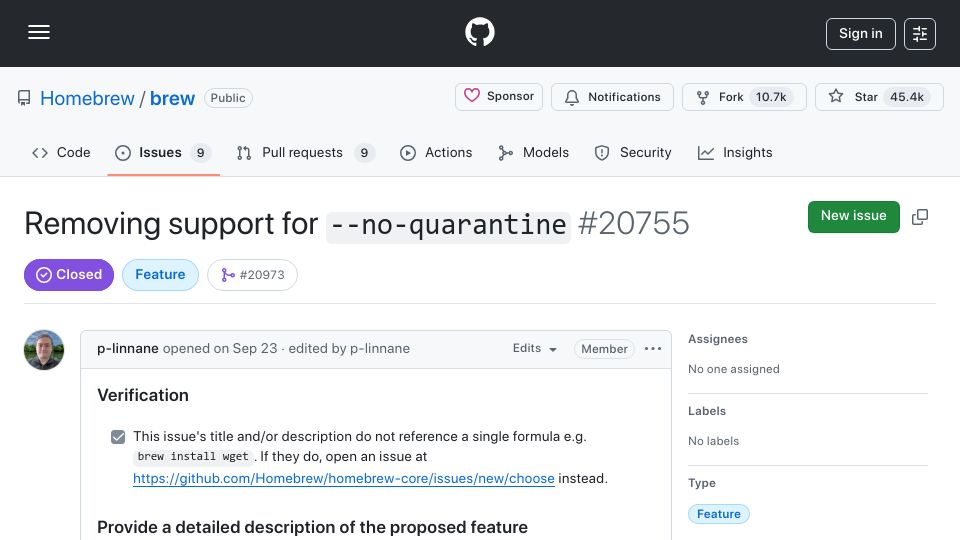
Homebrew no longer allows bypassing Gatekeeper for unsigned/unnotarized software(github.com)
326 points by firexcy | 250 comments
A closed GitHub issue in the Homebrew/brew repository proposing removal of the --no-quarantine option, which allowed bypassing macOS Gatekeeper for unsigned casks.
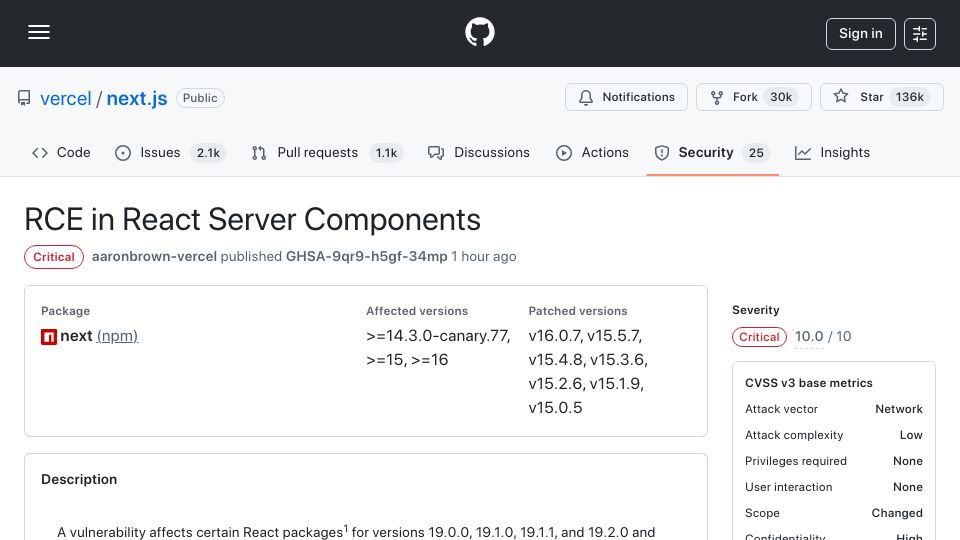
RCE Vulnerability in React and Next.js(github.com)
559 points by rayhaanj | 214 comments
GitHub security advisory GHSA-9qr9-h5gf-34mp for a critical (CVSS 10.0) remote code execution vulnerability in React Server Components affecting Next.js, with patched versions listed.
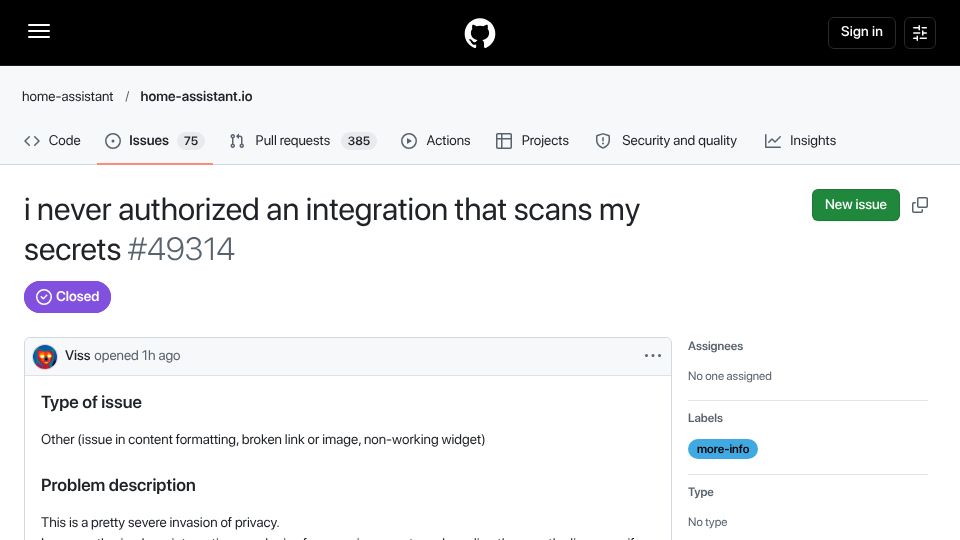
I never authorized an integration that scans my secrets(github.com)
202 points by trvrprkr | 155 comments
A closed GitHub issue on the home-assistant.io repo in which a user complains that an integration scanning their secrets was enabled without authorization, calling it a privacy invasion.
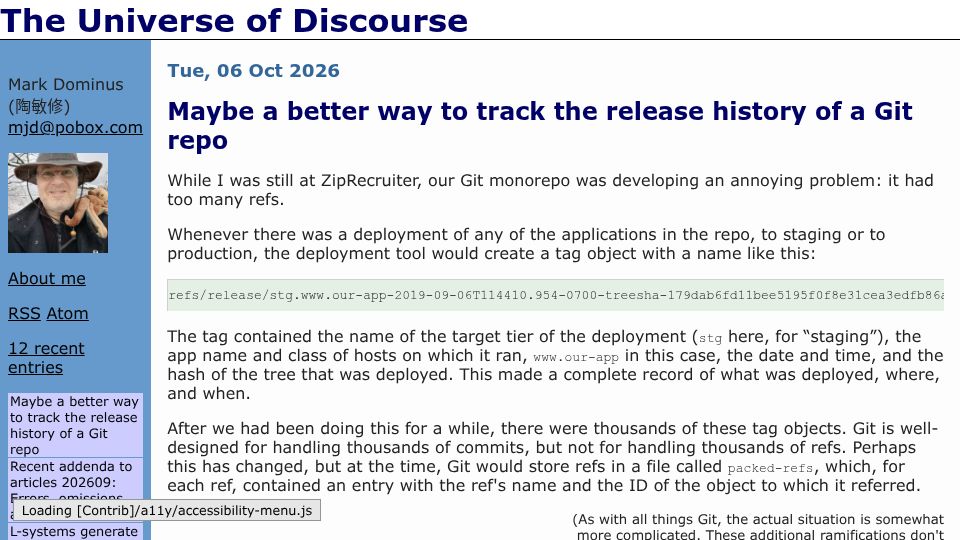
Maybe a better way to track the release history of a Git repo(blog.plover.com)
55 points by evakhoury | 13 comments
Blog post by Mark Dominus proposing a better way to record a Git repo's deployment and release history than creating thousands of tag refs.
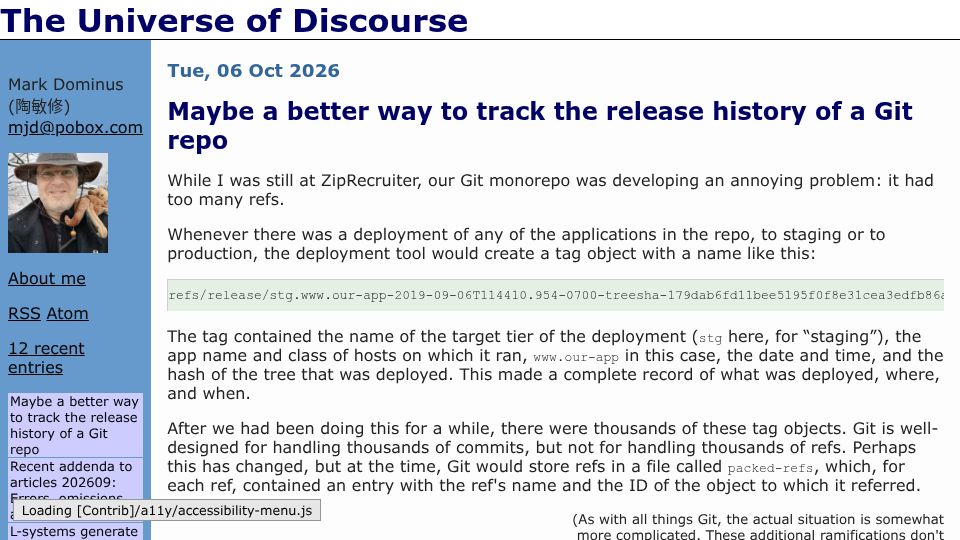
Maybe a better way to track the release history of a Git repo(blog.plover.com)
30 points by hellerve | 7 comments
Mark Dominus blog post proposing a better way to track a Git repo's deployment release history than creating thousands of release tags, based on ZipRecruiter experience.
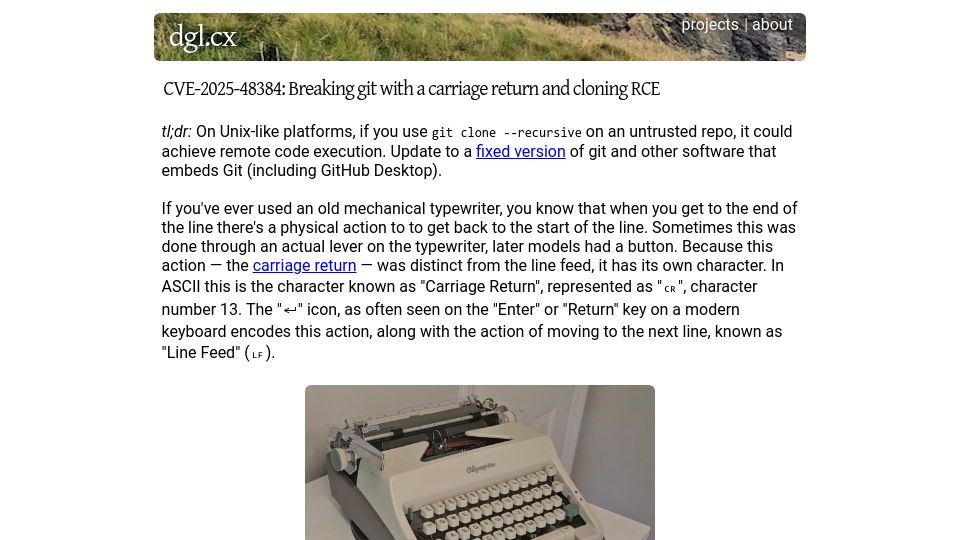
Breaking Git with a carriage return and cloning RCE(dgl.cx)
357 points by dgl | 147 comments
A blog post explaining CVE-2025-48384, a Git vulnerability where carriage return handling allows remote code execution via git clone --recursive on Unix-like systems.