nesbitt.io on Hacker News
22 stories on the front page, newest first. Scroll down to watch the site change over time.
Interview with a Maintainer(nesbitt.io)
17 points by ryangibb | 9 comments
git's –end-of-options Flag(nesbitt.io)
175 points by Erenay09 | 108 comments
Incident CVE-2026-LGTM(nesbitt.io)
484 points by mooreds | 82 comments
Andrew Nesbitt's satirical incident report about a malicious package slipping past seven AI-powered security gates in a fictional future CVE.
Protestware for Coding Agents(nesbitt.io)
23 points by SVI | 15 comments
Incident Report: CVE-2024-YIKES(nesbitt.io)
658 points by miniBill | 156 comments
A satirical incident report by Andrew Nesbitt about a cascading software supply chain attack spanning JavaScript, Rust, and Python package ecosystems.
GitHub Actions is the weakest link(nesbitt.io)
210 points by dochtman | 68 comments
Package managers need to cool down(nesbitt.io)
44 points by zdw | 39 comments
Sandwich Bill of Materials(nesbitt.io)
218 points by zdw | 25 comments
Package management is a wicked problem(nesbitt.io)
82 points by zdw | 59 comments
Reducing Dependabot Noise(nesbitt.io)
60 points by zdw | 38 comments
How dependabot works(nesbitt.io)
57 points by zdw | 11 comments
How uv got so fast(nesbitt.io)
1179 points by zdw | 405 comments
Blog post by Andrew Nesbitt examining the design decisions and packaging standards that make the uv Python package installer much faster than pip.
Package managers keep using Git as a database, it never works out(nesbitt.io)
742 points by birdculture | 426 comments
Andrew Nesbitt's blog post arguing that package managers like Cargo repeatedly use git repositories as registry databases and run into scaling problems.
Could lockfiles just be SBOMs?(nesbitt.io)
57 points by zdw | 40 comments
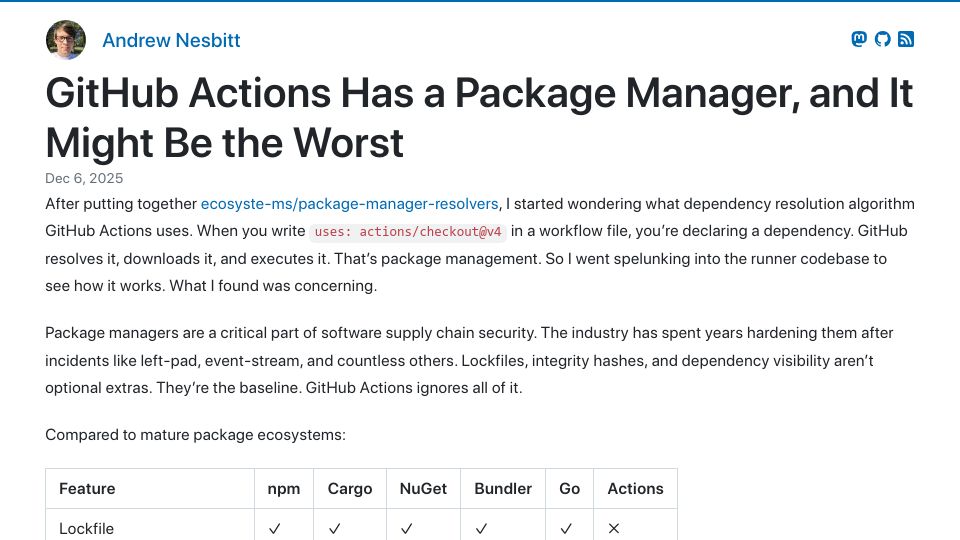
GitHub Actions has a package manager, and it might be the worst(nesbitt.io)
408 points by robin_reala | 236 comments
Andrew Nesbitt's blog post arguing GitHub Actions functions as a package manager lacking lockfiles, integrity hashes, and other supply chain safeguards.