First screen, captured .
Full page
Captured . Click for the whole screenshot.
Looks similar
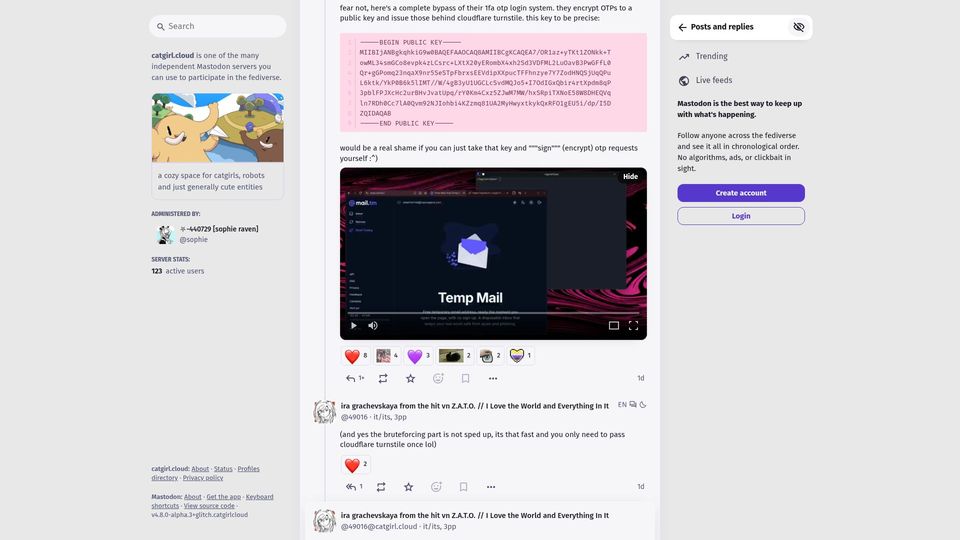
A complete bypass of eMudhra’s 1FA OTP login system(mastodon.catgirl.cloud)
131 points by tensegrist | 53 comments
Mastodon thread describing a bypass of eMudhra's OTP login by encrypting OTP requests with an exposed public key, enabling brute-forcing of logins to steal certificates.
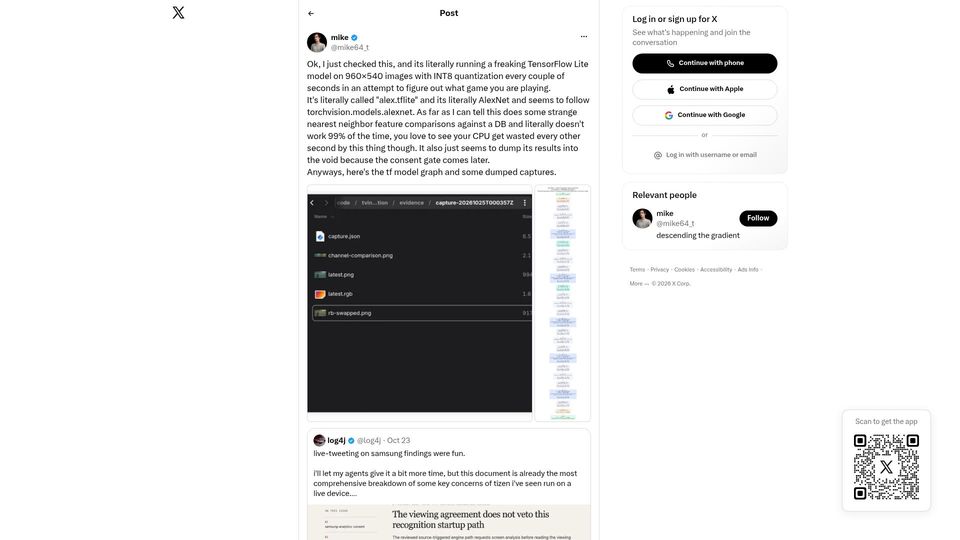
Samsung running a TensorFlow lite model on 960x540 image to track you(twitter.com)
272 points by mashally | 176 comments
An X post reporting that Samsung Tizen TVs run an INT8 AlexNet TensorFlow Lite model on 960x540 screen captures every few seconds to identify which game is being played.
Related stories
There isn't an easy exploit for this PHP vulnerability(eliastaylor.com)
566 points by zkldi | 437 comments
Blog post arguing a newly disclosed PHP vulnerability is hard to exploit and that thousands of LLM-generated GitHub PoC exploits don't work against vanilla PHP.
Today's PHP security release, and how we're strengthening security(thephp.foundation)
761 points by ejohnso49 | 394 comments
PHP Foundation blog post on a PHP security release fixing two critical RCE vulnerabilities, how they were found, the disclosure leak, and how PHP security work is being strengthened.
A complete bypass of eMudhra’s 1FA OTP login system(mastodon.catgirl.cloud)
131 points by tensegrist | 53 comments
Mastodon thread describing a bypass of eMudhra's OTP login by encrypting OTP requests with an exposed public key, enabling brute-forcing of logins to steal certificates.
Making WebAssembly a first-class language on the Web(hacks.mozilla.org)
613 points by mikece | 223 comments
Mozilla Hacks article by Ryan Hunt on why WebAssembly remains a second-class language on the web and how to make it first-class.
GitHub RCE Vulnerability: CVE-2026-3854 Breakdown(wiz.io)
424 points by bo0tzz | 89 comments
Wiz Research blog post detailing CVE-2026-3854, a critical flaw in GitHub's internal git infrastructure enabling remote code execution on GitHub.com and GitHub Enterprise Server.
Hardening Firefox with Anthropic's Red Team(anthropic.com)
580 points by todsacerdoti | 159 comments
Post on Mozilla's Distilled blog about Anthropic's red team using Claude to find security vulnerabilities in Firefox that Mozilla then fixed.