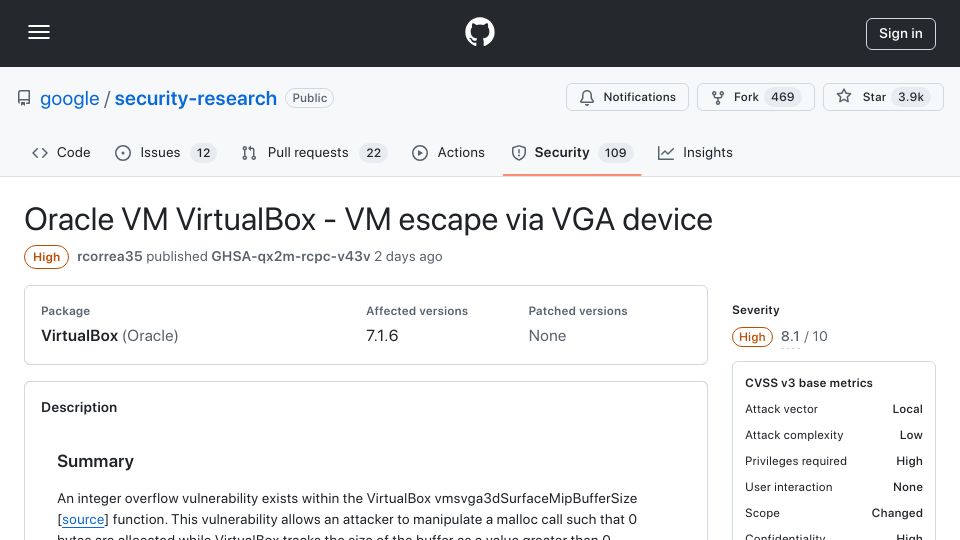
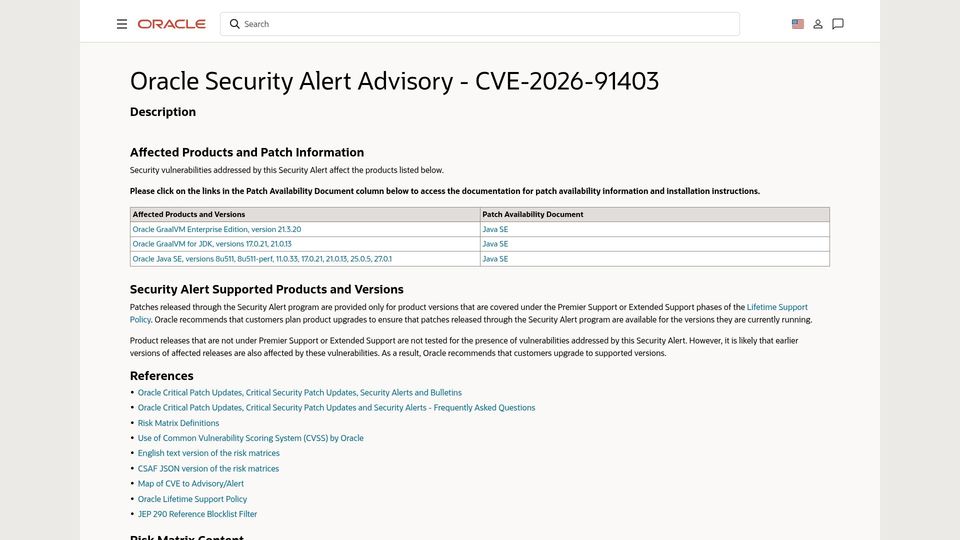
First screen, captured .
Full page
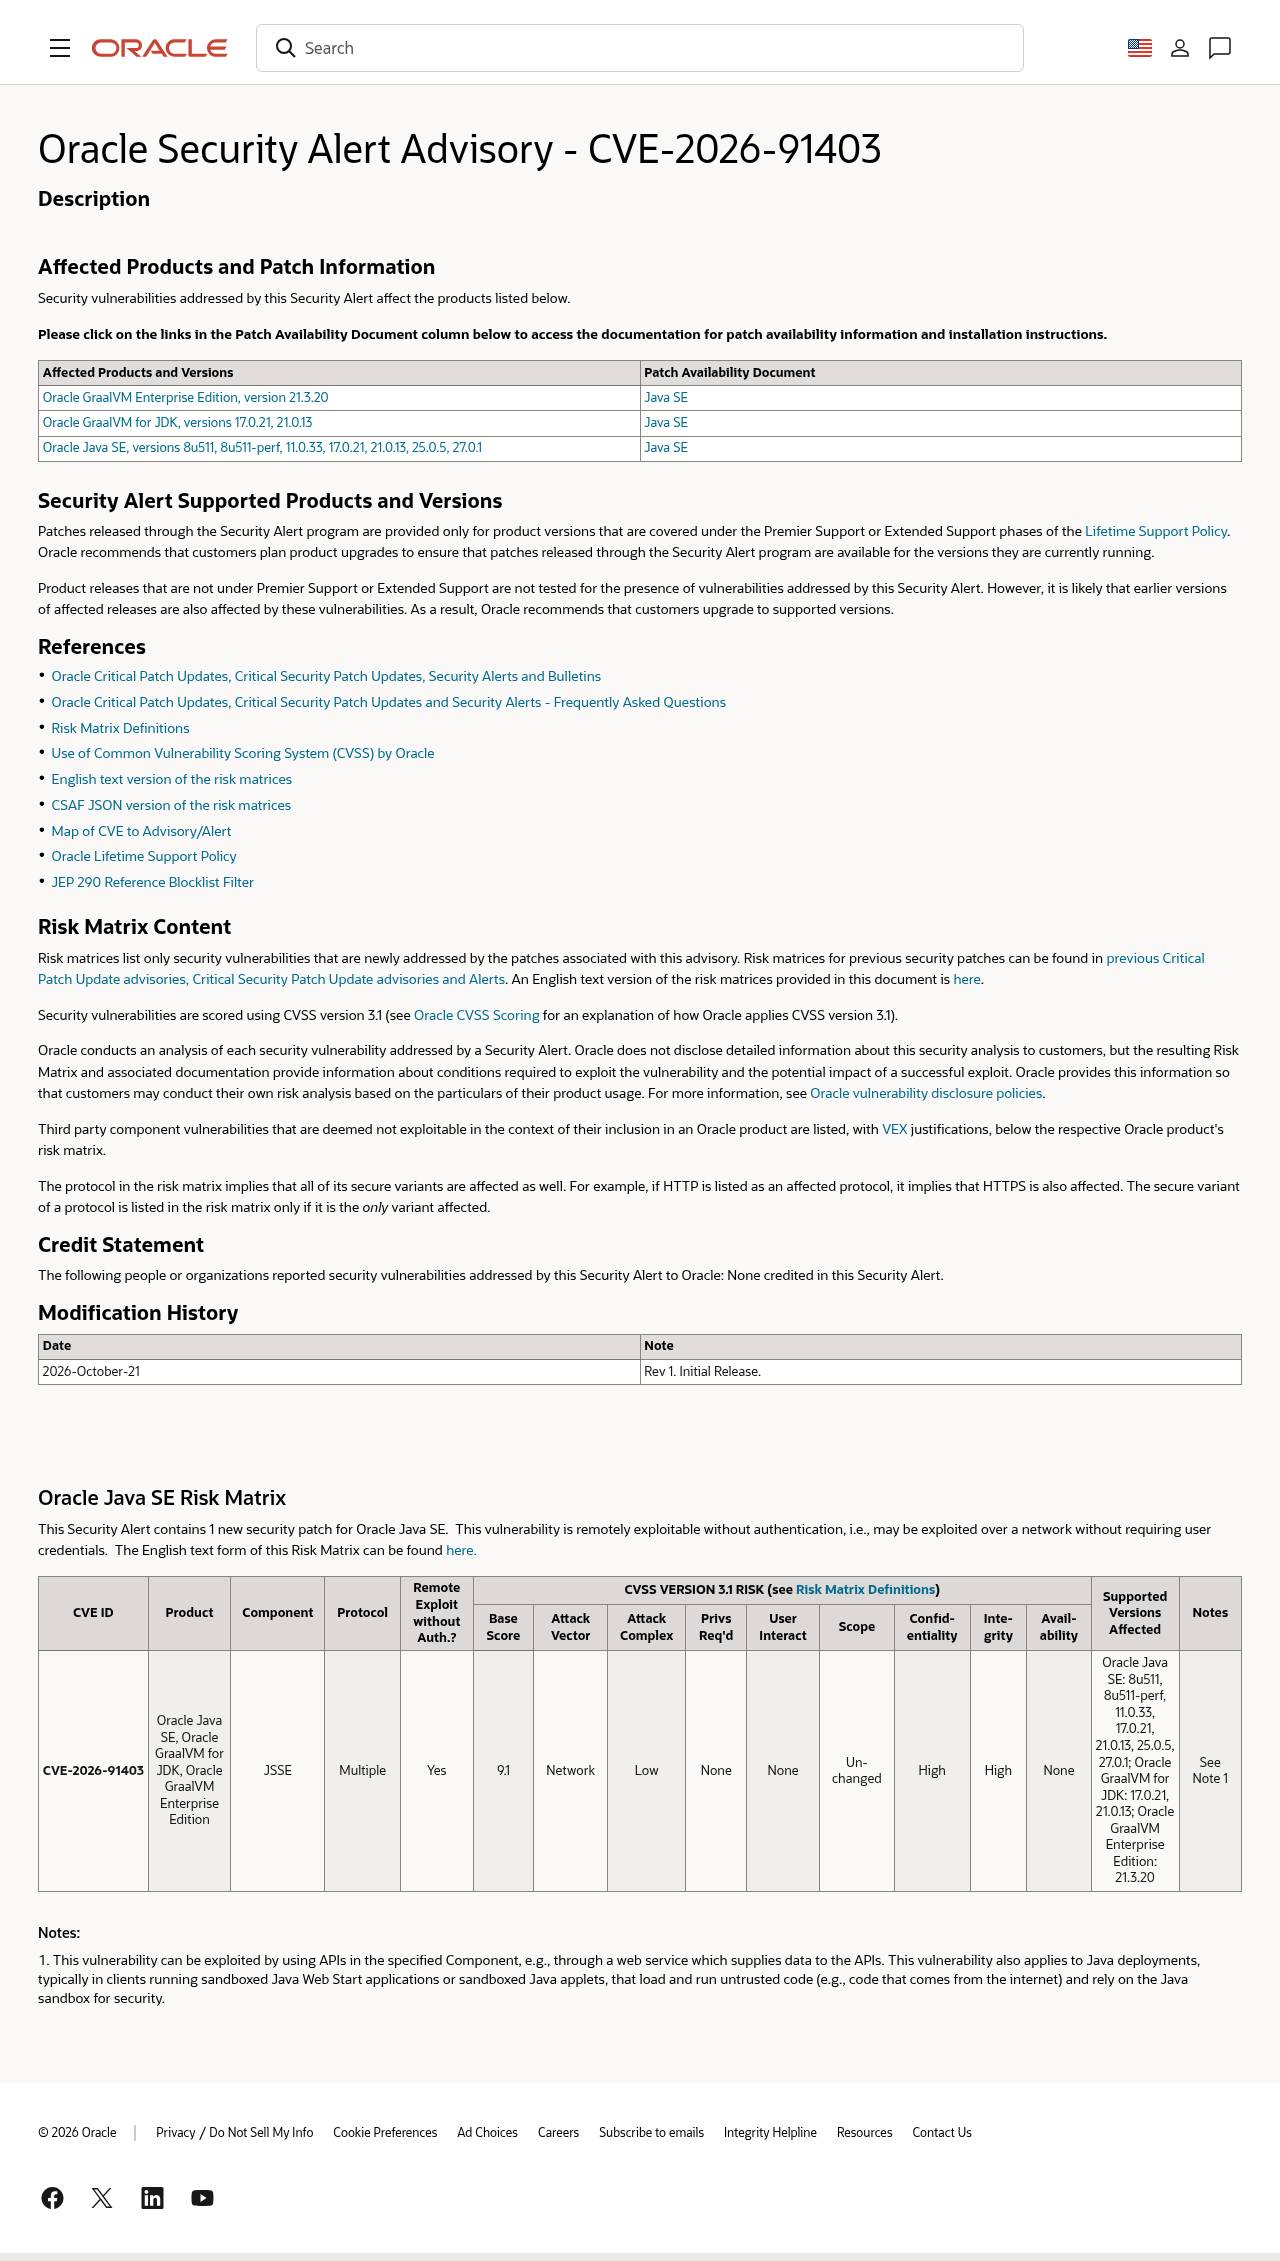
Captured . Click for the whole screenshot.
Looks similar
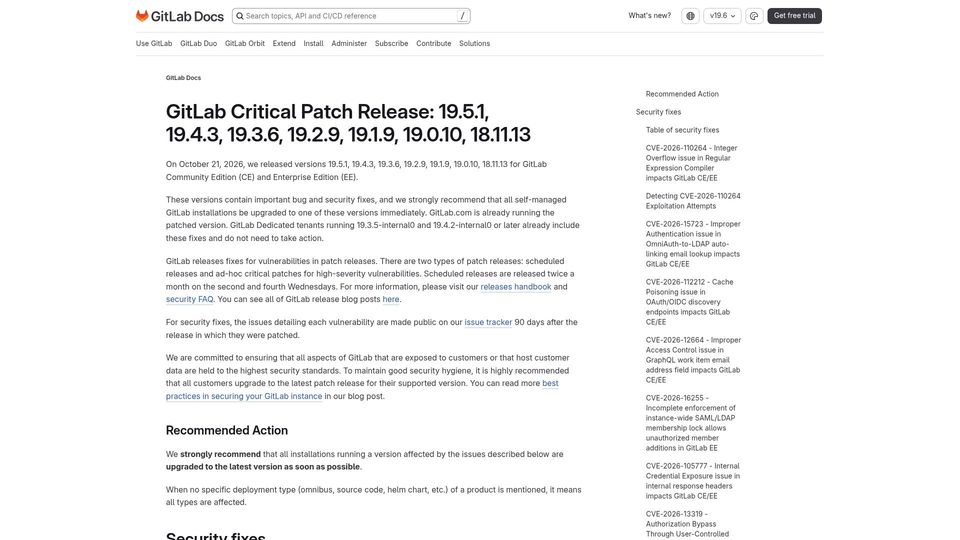
GitLab critical patch release(docs.gitlab.com)
395 points by artooro | 92 comments
GitLab's critical patch release notes for versions 19.5.1 and backports, fixing a CVSS 10.0 regex compiler integer overflow RCE and other security issues.

DuckDB NPM packages 1.3.3 and 1.29.2 compromised with malware(github.com)
367 points by tosh | 263 comments
GitHub security advisory reporting that DuckDB npm packages (duckdb 1.3.3, node-api, node-bindings, duckdb-wasm 1.29.2) were published with malware, listing patched versions.
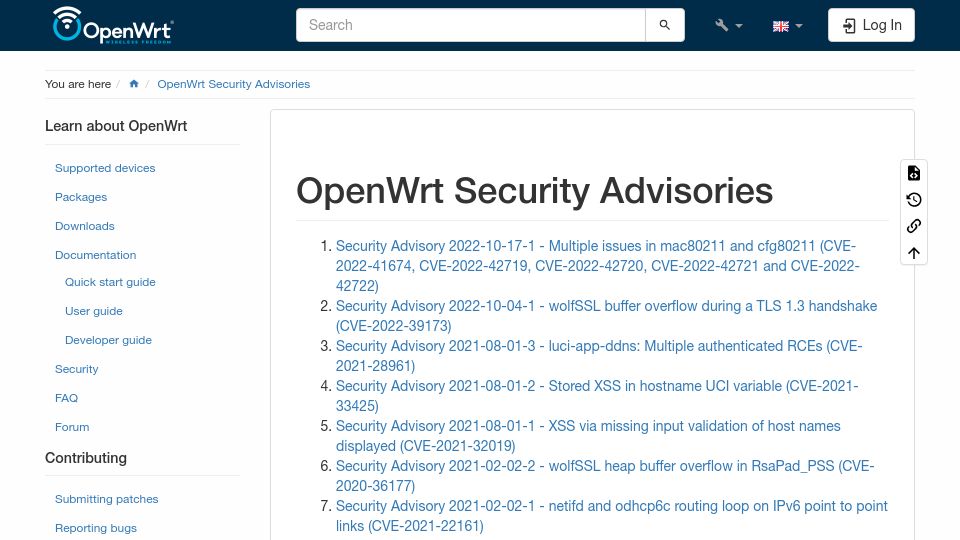
OpenWrt Security Advisories(openwrt.org)
32 points by fulafel | 4 comments
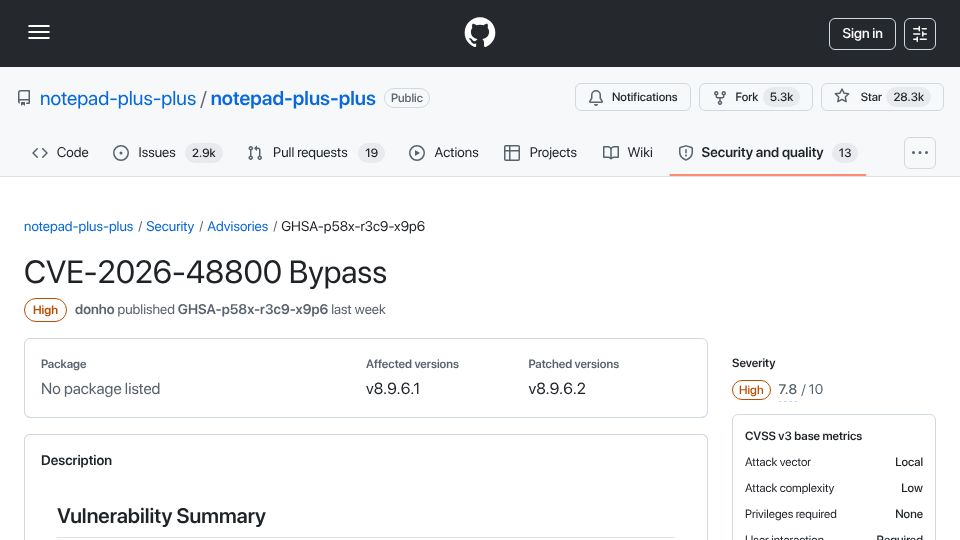
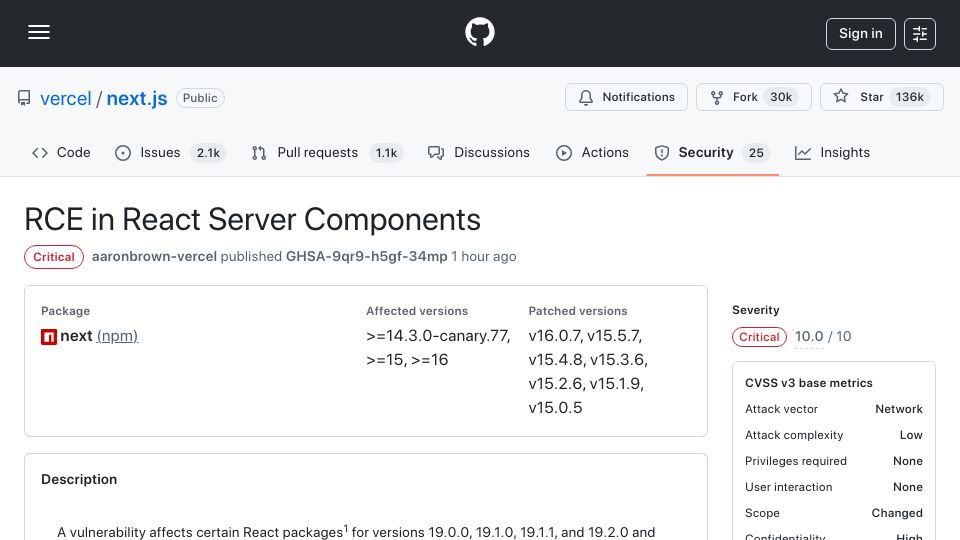
RCE Vulnerability in React and Next.js(github.com)
559 points by rayhaanj | 214 comments
GitHub security advisory GHSA-9qr9-h5gf-34mp for a critical (CVSS 10.0) remote code execution vulnerability in React Server Components affecting Next.js, with patched versions listed.
Related stories
OpenClaw privilege escalation vulnerability(nvd.nist.gov)
493 points by kykeonaut | 232 comments
NVD entry for CVE-2026-33579, a privilege escalation vulnerability in OpenClaw; the captured screenshot shows a Reddit network-policy block page instead.
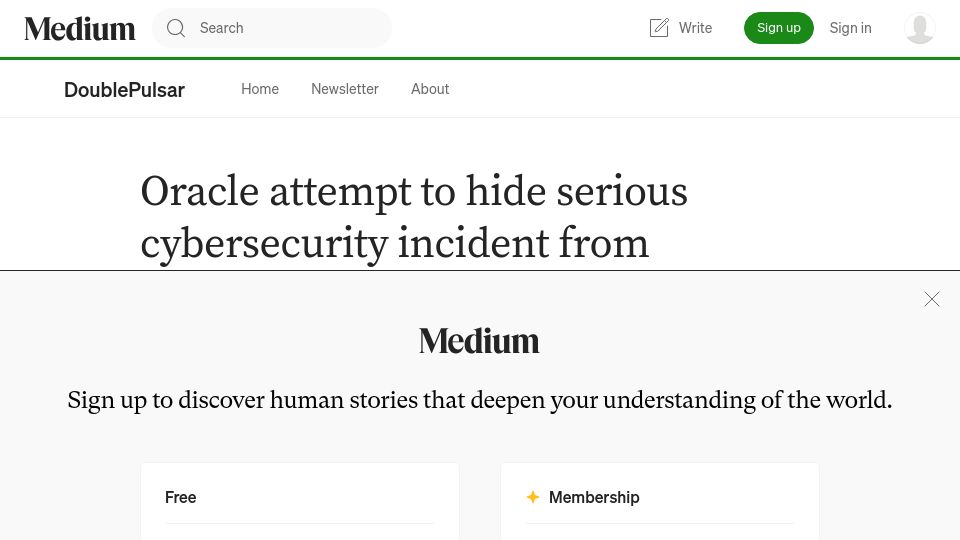
Oracle attempt to hide cybersecurity incident from customers?(doublepulsar.com)
567 points by 2bluesc | 114 comments
DoublePulsar blog post on Medium alleging Oracle tried to hide a serious cybersecurity incident in its SaaS service from customers.
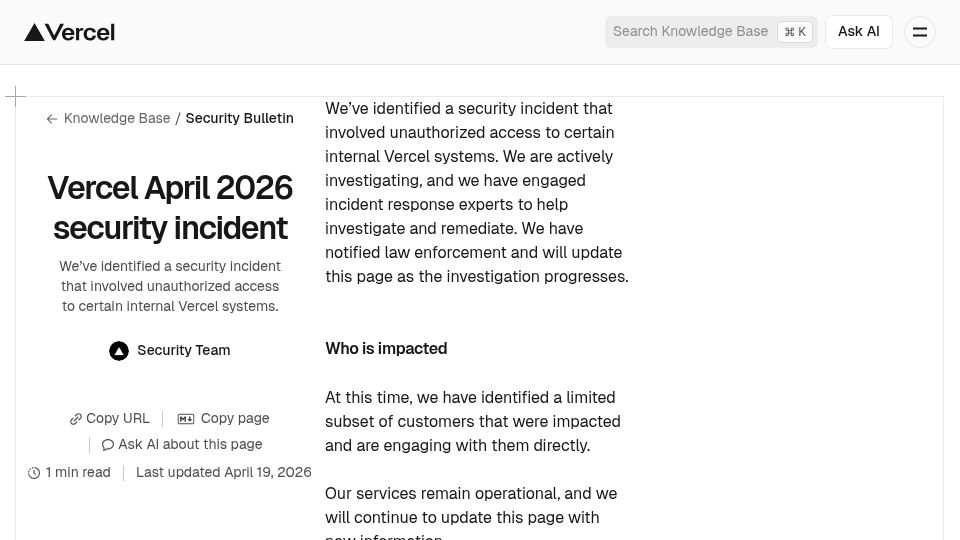
Vercel April 2026 security incident(bleepingcomputer.com)
817 points by colesantiago | 466 comments
Vercel security bulletin disclosing unauthorized access to certain internal systems in April 2026, affecting a limited subset of customers, with an ongoing investigation.
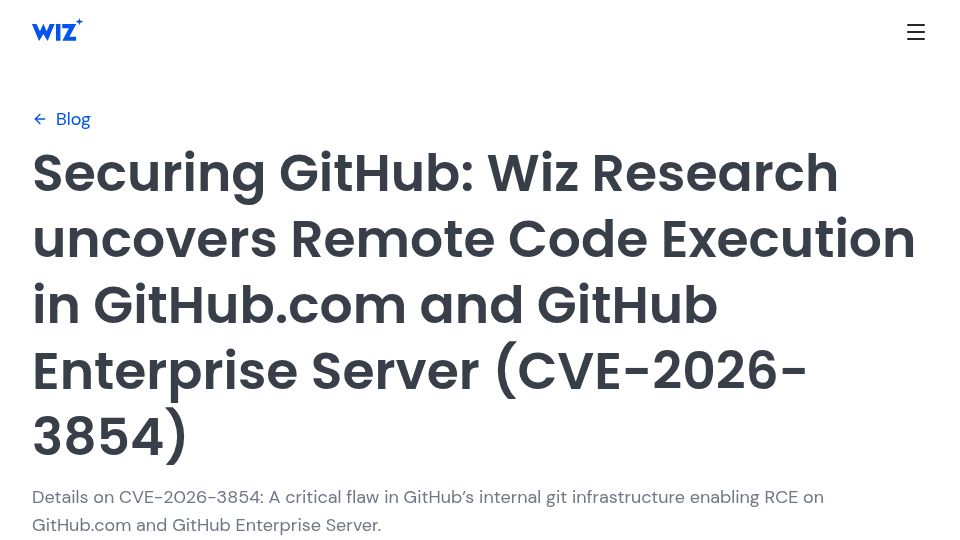
GitHub RCE Vulnerability: CVE-2026-3854 Breakdown(wiz.io)
424 points by bo0tzz | 89 comments
Wiz Research blog post detailing CVE-2026-3854, a critical flaw in GitHub's internal git infrastructure enabling remote code execution on GitHub.com and GitHub Enterprise Server.
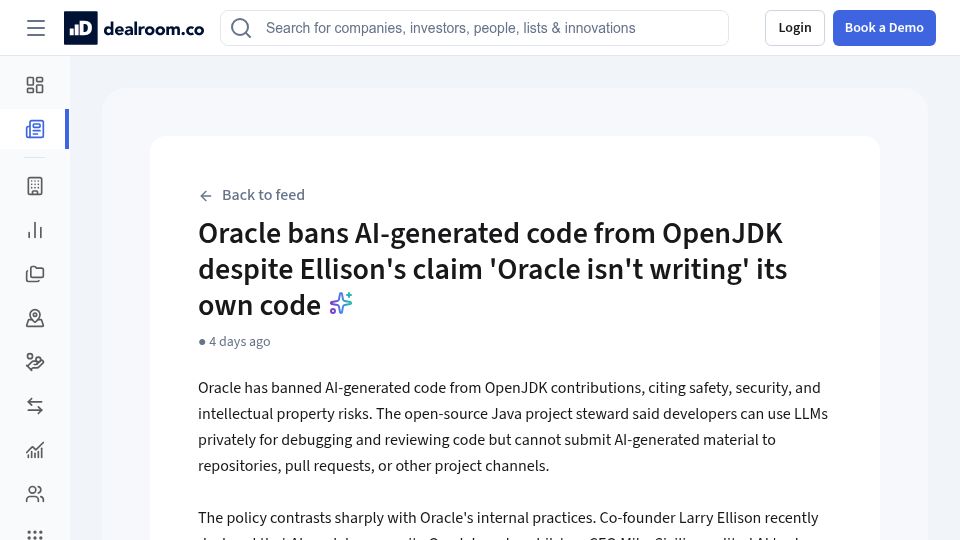
Oracle bans AI-generated code from OpenJDK(app.dealroom.co)
494 points by delduca | 356 comments
Dealroom news feed item reporting that Oracle has banned AI-generated code contributions to OpenJDK, contrasting with Larry Ellison's claims about Oracle's internal AI use.
RCE Vulnerability in React and Next.js(github.com)
559 points by rayhaanj | 214 comments
GitHub security advisory GHSA-9qr9-h5gf-34mp for a critical (CVSS 10.0) remote code execution vulnerability in React Server Components affecting Next.js, with patched versions listed.