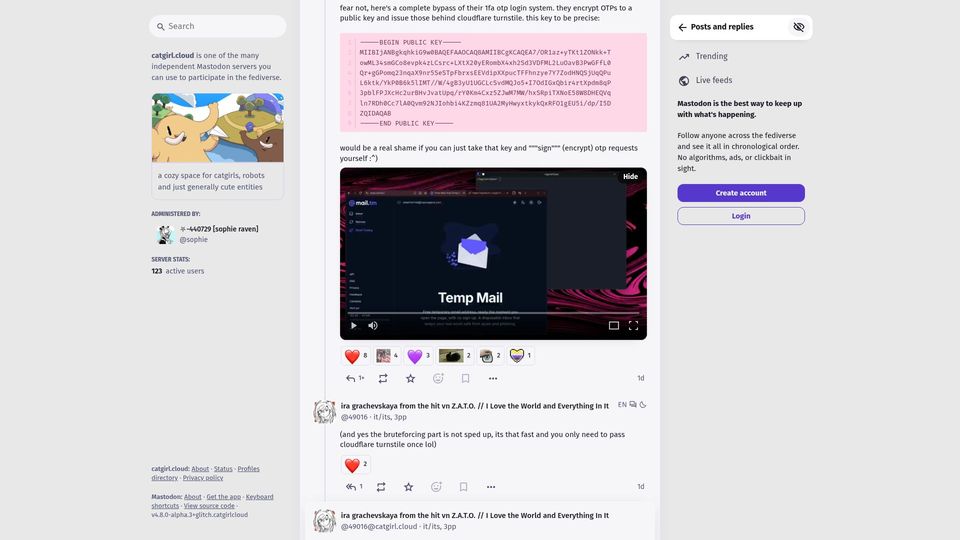
A complete bypass of eMudhra’s 1FA OTP login system(mastodon.catgirl.cloud)
131 points by tensegrist | 53 comments
Mastodon thread describing a bypass of eMudhra's OTP login by encrypting OTP requests with an exposed public key, enabling brute-forcing of logins to steal certificates.