First screen, captured .
Looks similar
Compromised LiteLLM 1.107.0 on PyPI Installs a Credential Stealer and Backdoor(safedep.io)
582 points by abhisek | 192 comments
SafeDep analysis of the compromised LiteLLM 1.107.0 PyPI release, which installed a credential stealer and remote-code backdoor via .pth and sitecustomize files, with IOCs.
Related stories
MVCC – the part of PostgreSQL we hate the most (2023)(cs.cmu.edu)
341 points by virtualwhys | 109 comments
Andy Pavlo blog post from April 2023 criticizing PostgreSQL's multi-version concurrency control (MVCC) implementation and its drawbacks.
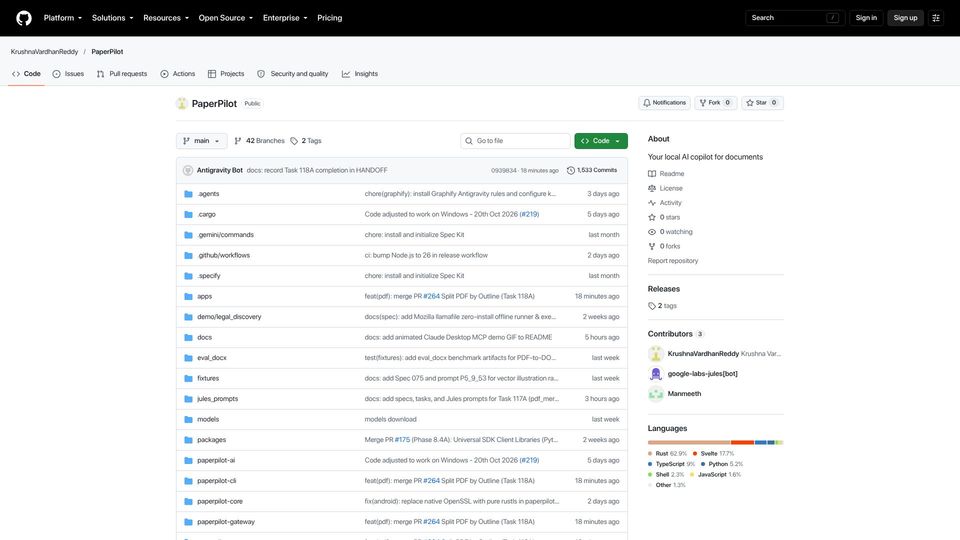
PaperPilot – Zero-Cloud, Pure-Rust PDF Engine with WASM and MCP(github.com)
221 points by vardhan1237 | 77 comments
GitHub repository for PaperPilot, a local, zero-cloud pure-Rust PDF engine and AI document copilot with WASM builds and an MCP server.
GitHub MCP exploited: Accessing private repositories via MCP(invariantlabs.ai)
477 points by andy99 | 287 comments
Invariant Labs blog post describing a vulnerability in the official GitHub MCP server that lets attackers access private repository data via AI agent prompt injection.
Blog ran on Ubuntu 16.04 for 10 years. I migrated it to FreeBSD(crocidb.com)
353 points by speckx | 214 comments
Personal blog post describing migrating a blog from a decade-old Ubuntu 16.04 DigitalOcean VPS to a cheaper FreeBSD virtual machine on Hetzner.
I'm being cyberattacked by Tesla, Inc(dreamstation.systems)
389 points by robinpie | 109 comments
Personal blog post describing persistent attack traffic in nginx logs from IPs with Host/Referer headers pointing to pool-ntp.tesla.com.
PyTorch Internals: Ezyang's Blog(blog.ezyang.com)
418 points by Anon84 | 24 comments
Edward Yang's long-form blog essay on PyTorch internals, based on his talk at the PyTorch NYC meetup on May 14, 2019.