First screen, captured .
Looks similar
Google API keys weren't secrets, but then Gemini changed the rules(trufflesecurity.com)
1206 points by hiisthisthingon | 288 comments
Truffle Security blog post explaining that public Google API keys, long deemed non-secret, can now access Gemini and private data, based on scans of exposed keys.
I found a backdoor into my bed(trufflesecurity.com)
855 points by riverdroid | 345 comments
Truffle Security blog post describing a backdoor found in the Eight Sleep smart bed that allowed remote access, and how the authors removed it.
Related stories
Shreddit is a Python program to remove all your Reddit comments(github.com)
335 points by wgx | 207 comments
GitHub repository for Shreddit, a Python tool using PRAW to delete your Reddit comment history, since deleting an account does not remove comments.
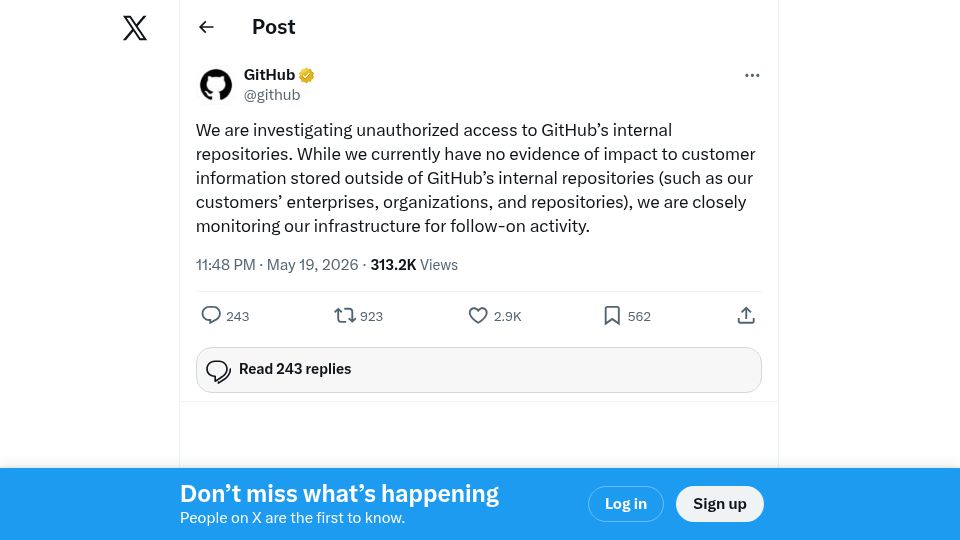
GitHub is investigating unauthorized access to their internal repositories(twitter.com)
527 points by splenditer | 289 comments
A post on X from GitHub stating it is investigating unauthorized access to its internal repositories, with no current evidence of impact to customer data.
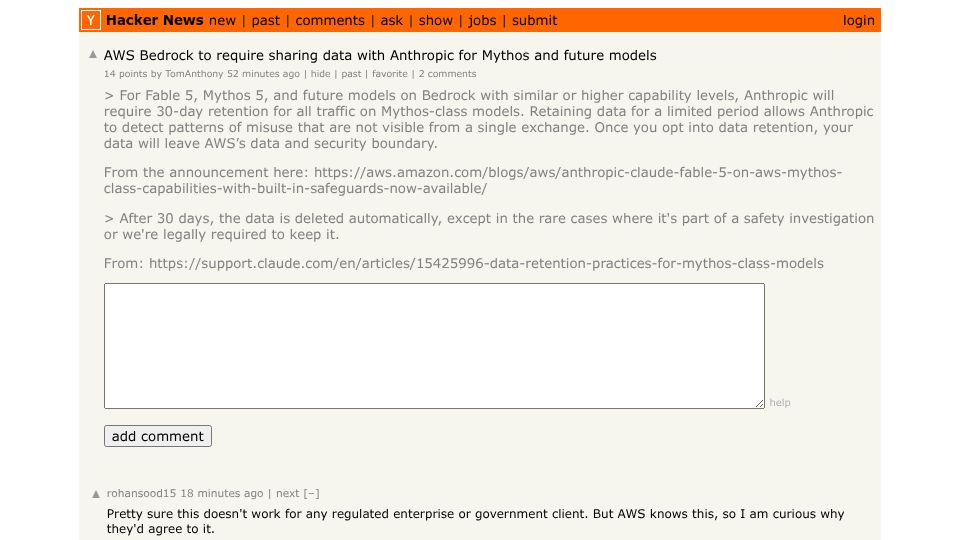
AWS Bedrock to require sharing data with Anthropic for Mythos and future models
369 points by TomAnthony | 216 comments
Hacker News discussion of Anthropic requiring 30-day data retention for Mythos-class Claude models on AWS Bedrock, moving data outside AWS's security boundary.
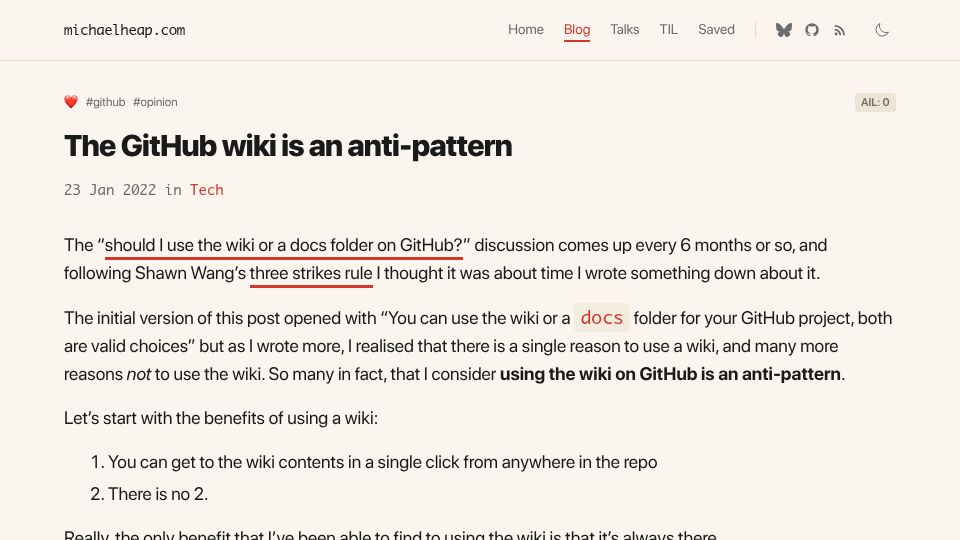
The GitHub wiki is an anti-pattern (2022)(michaelheap.com)
151 points by ibobev | 88 comments
A 2022 blog post by Michael Heap arguing that using the GitHub wiki for project documentation is an anti-pattern compared to a docs folder in the repo.
Google API keys weren't secrets, but then Gemini changed the rules(trufflesecurity.com)
1206 points by hiisthisthingon | 288 comments
Truffle Security blog post explaining that public Google API keys, long deemed non-secret, can now access Gemini and private data, based on scans of exposed keys.
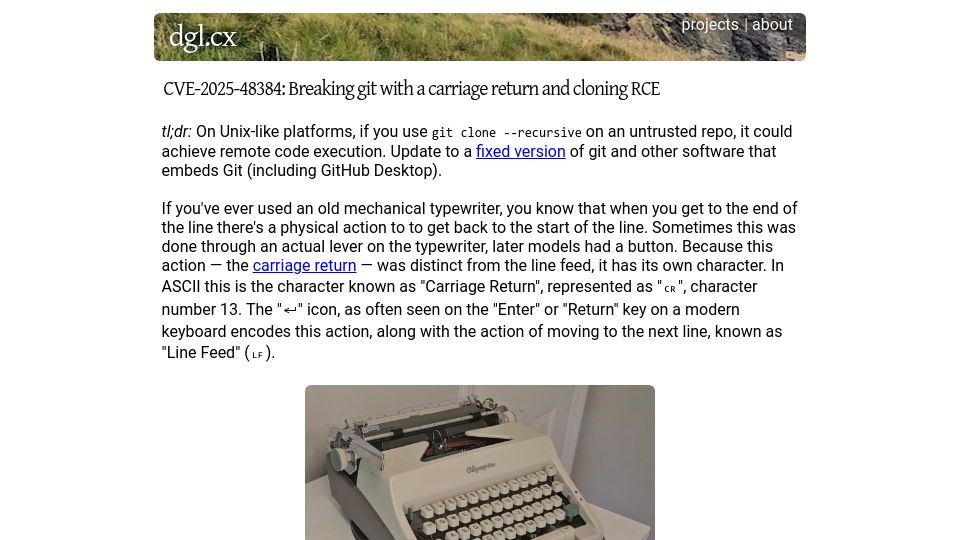
Breaking Git with a carriage return and cloning RCE(dgl.cx)
357 points by dgl | 147 comments
A blog post explaining CVE-2025-48384, a Git vulnerability where carriage return handling allows remote code execution via git clone --recursive on Unix-like systems.