First screen, captured .
Looks similar

Related stories
USPS shared customer postal addresses with Meta, LinkedIn and Snap(techcrunch.com)
379 points by leotravis10 | 194 comments
TechCrunch investigation reporting that the US Postal Service shared customers' postal addresses with Meta, LinkedIn and Snap via tracking code, and later remediated it.
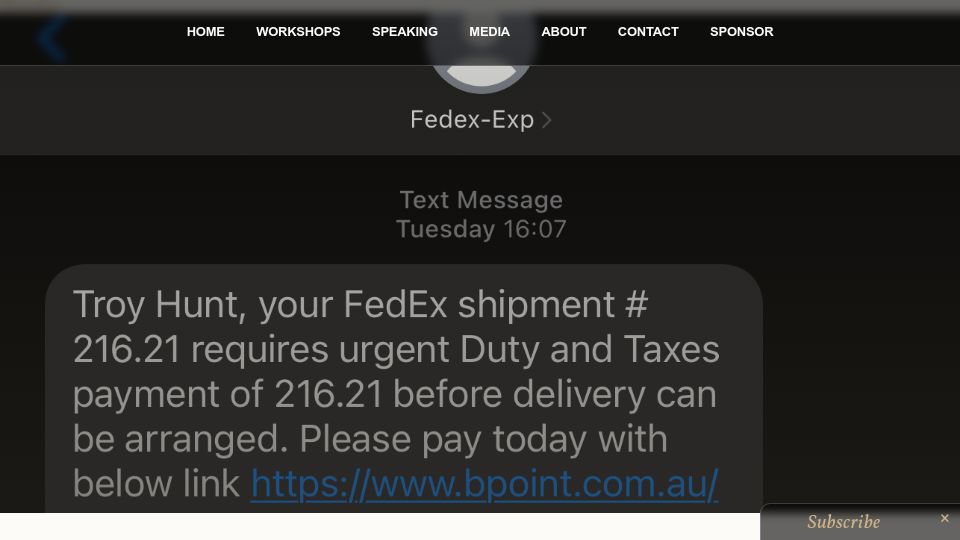
Thanks FedEx, this is why we keep getting phished(troyhunt.com)
1506 points by ahonhn | 493 comments
Troy Hunt blog post criticizing FedEx for sending a legitimate duty-payment SMS with a third-party link that looks indistinguishable from phishing.
FBI raids home of prominent computer scientist who has gone incommunicado(arstechnica.com)
825 points by JaimeThompson | 332 comments
Ars Technica article reporting that the FBI raided the home of an Indiana University computer scientist whose profile was quietly removed and who has gone silent.
U.S. postal inspectors shut down website selling counterfeit postage labels(postalemployeenetwork.com)
272 points by ilamont | 161 comments
Postal Employee Network news article reporting that U.S. Postal Inspectors shut down a website selling millions of counterfeit postage labels.
U.K. orders Apple to let it spy on users’ encrypted accounts(washingtonpost.com)
642 points by Despegar | 925 comments
Washington Post exclusive reporting that the U.K. secretly ordered Apple to provide blanket access to users' encrypted iCloud backups worldwide.
What a Hacker Stole from Me(mynoise.net)
355 points by wonger_ | 106 comments
A myNoise blog post by founder Stéphane describing a hacker's attack on the myNoise website, first via code-injection attempts and then a different strategy.