First screen, captured .
Looks similar
Related stories
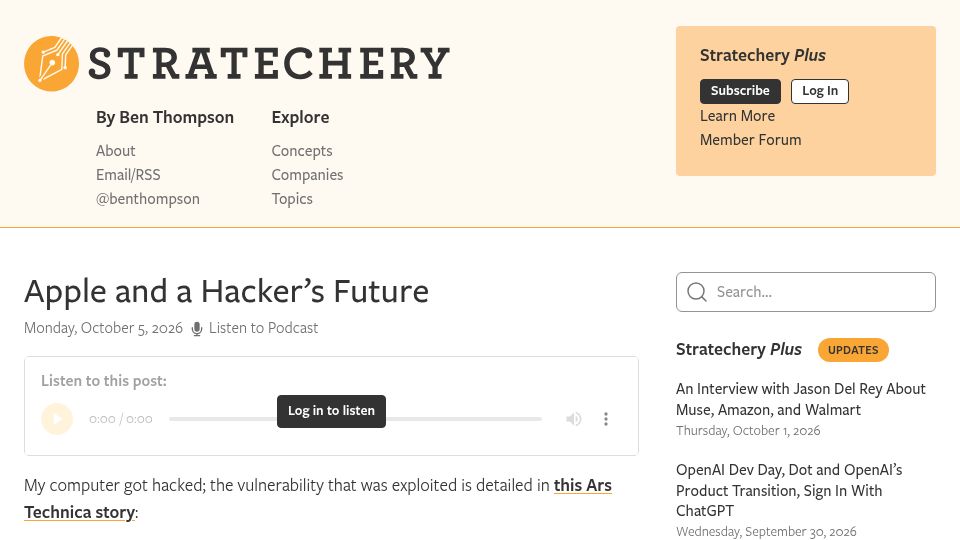
Apple and a hacker's future(stratechery.com)
275 points by maguay | 235 comments
Stratechery essay by Ben Thompson about his computer getting hacked via a vulnerability reported by Ars Technica, and what it means for Apple and hackers.
RCE Vulnerability in React and Next.js(github.com)
559 points by rayhaanj | 214 comments
GitHub security advisory GHSA-9qr9-h5gf-34mp for a critical (CVSS 10.0) remote code execution vulnerability in React Server Components affecting Next.js, with patched versions listed.
You can't trust macOS Privacy and Security settings(eclecticlight.co)
449 points by zdw | 152 comments
Eclectic Light Company blog post by Howard Oakley explaining why macOS Privacy & Security settings cannot be relied upon to reflect actual app permissions.
OpenClaw privilege escalation vulnerability(nvd.nist.gov)
493 points by kykeonaut | 232 comments
NVD entry for CVE-2026-33579, a privilege escalation vulnerability in OpenClaw; the captured screenshot shows a Reddit network-policy block page instead.
Unbricking my MacBook took an email to Tim Cook(tokyodev.com)
418 points by pwim | 299 comments
A TokyoDev blog post by Paul McMahon describing how an email to Tim Cook got Apple to remove the Activation Lock on his returned lost MacBook.
A supply chain attack on PyTorch(johnstawinski.com)
444 points by roblabla | 92 comments
Blog post by John Stawinski describing how his team executed a critical supply chain attack on PyTorch via its GitHub Actions CI infrastructure.