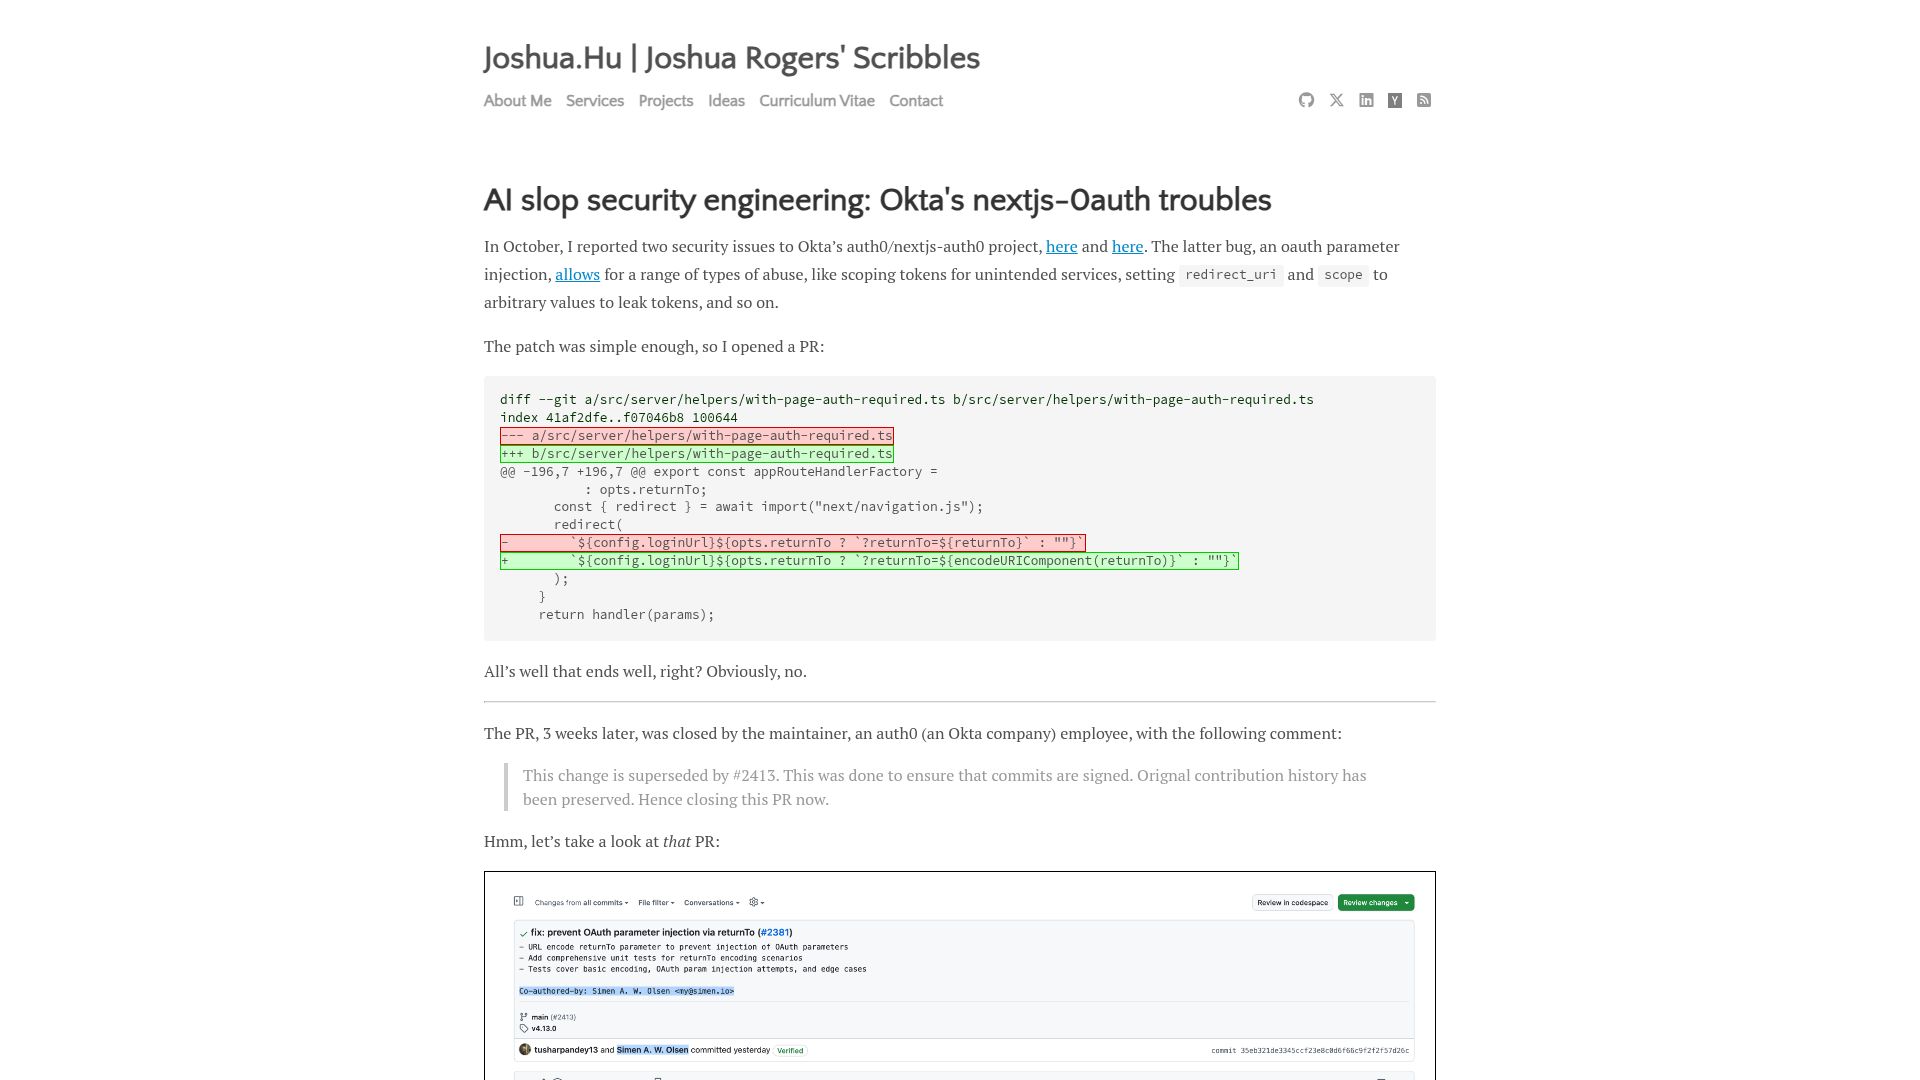
First screen, captured .
Looks similar
Related stories
Okta Bcrypt incident lessons for designing better APIs(n0rdy.foo)
359 points by n0rdy | 150 comments
Blog post analyzing the Okta Bcrypt cache-key security incident and drawing lessons for designing safer APIs.
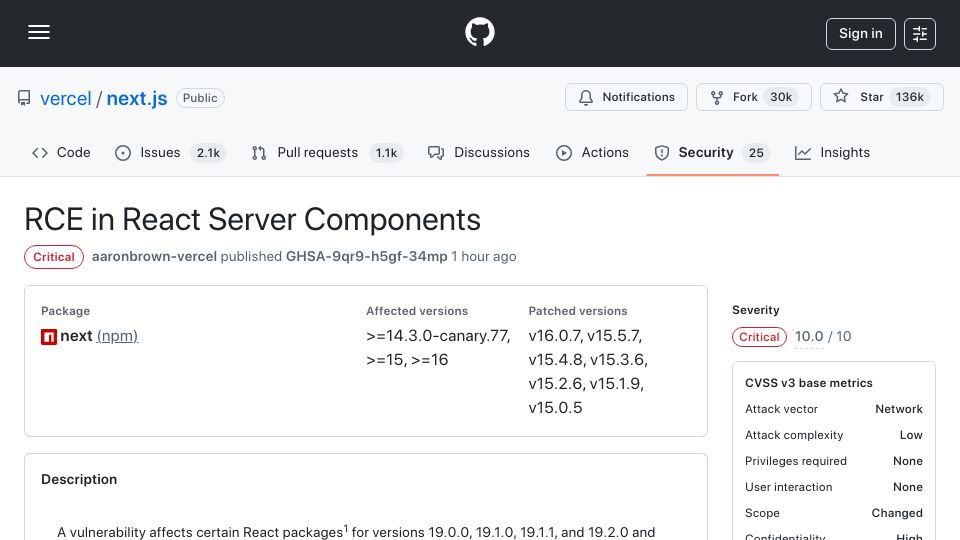
RCE Vulnerability in React and Next.js(github.com)
559 points by rayhaanj | 214 comments
GitHub security advisory GHSA-9qr9-h5gf-34mp for a critical (CVSS 10.0) remote code execution vulnerability in React Server Components affecting Next.js, with patched versions listed.
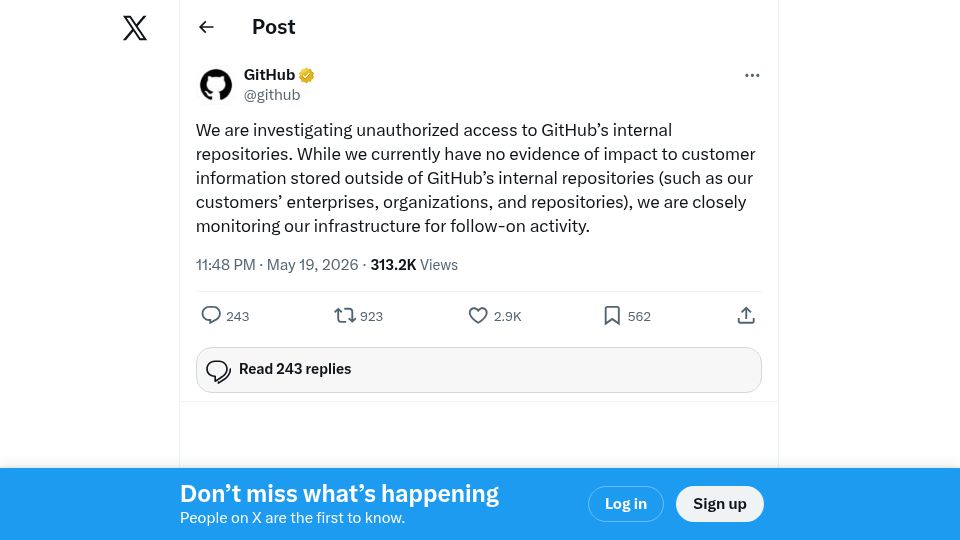
GitHub is investigating unauthorized access to their internal repositories(twitter.com)
527 points by splenditer | 289 comments
A post on X from GitHub stating it is investigating unauthorized access to its internal repositories, with no current evidence of impact to customer data.
Next.js is infuriating(blog.meca.sh)
812 points by Bogdanp | 461 comments
A personal blog post by Dominik Meca complaining about the difficulty of setting up production logging and middleware in Next.js.
Open Source is one person(opensourcesecurity.io)
325 points by LawnGnome | 132 comments
Blog post by Josh Bressers on Open Source Security arguing that many open source projects are maintained by a single person.
I'm being cyberattacked by Tesla, Inc(dreamstation.systems)
389 points by robinpie | 109 comments
Personal blog post describing persistent attack traffic in nginx logs from IPs with Host/Referer headers pointing to pool-ntp.tesla.com.