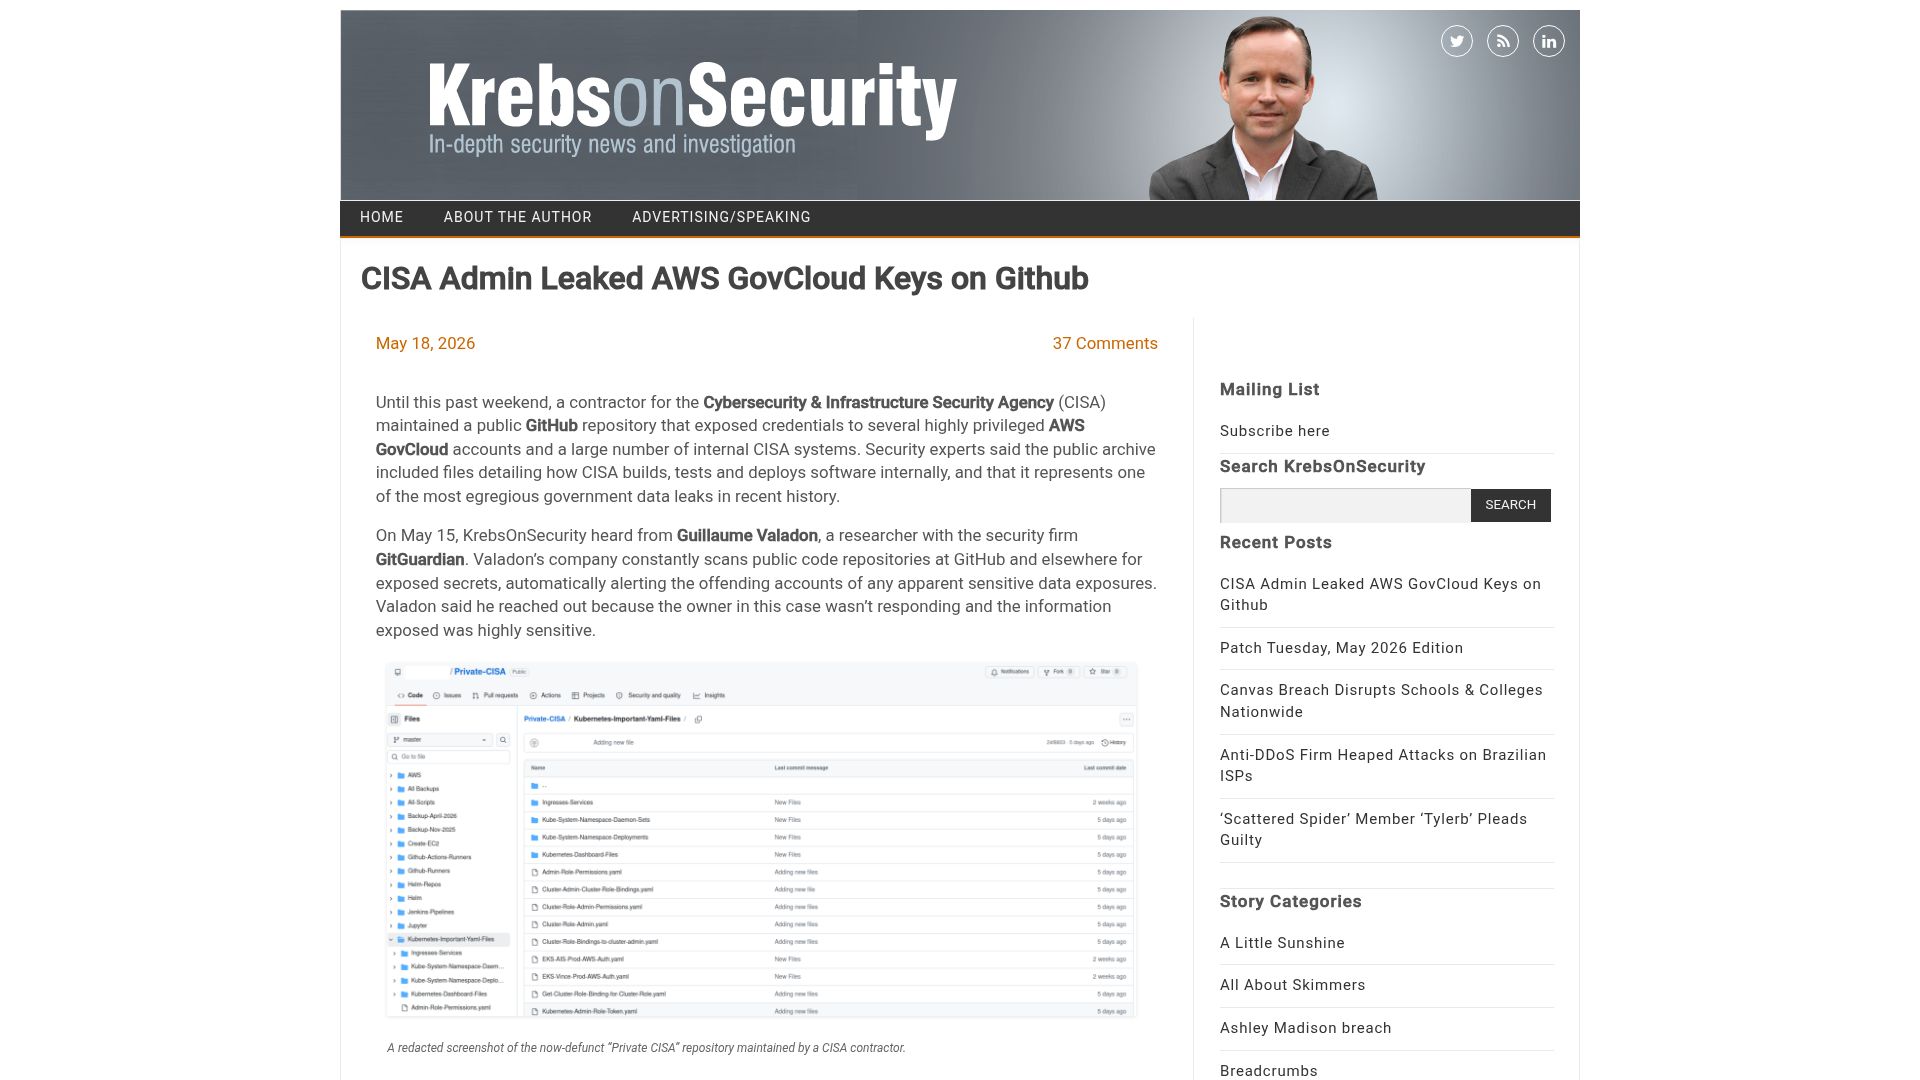
First screen, captured .
Looks similar
Feds Link Cyberheist to 2022 LastPass Hacks(krebsonsecurity.com)
365 points by todsacerdoti | 231 comments
KrebsOnSecurity article reporting that U.S. federal agents linked a $150 million cryptocurrency heist to master passwords cracked from the 2022 LastPass breach.
Related stories
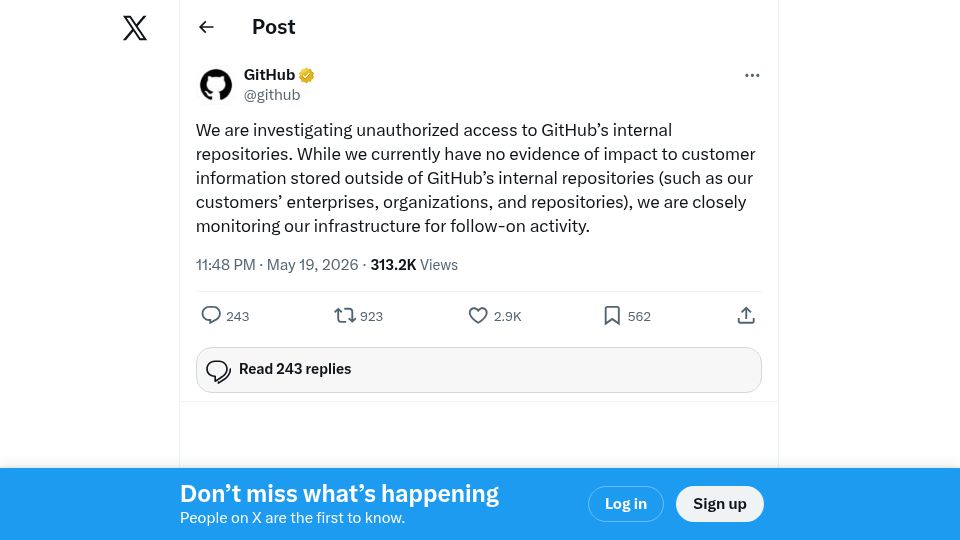
GitHub is investigating unauthorized access to their internal repositories(twitter.com)
527 points by splenditer | 289 comments
A post on X from GitHub stating it is investigating unauthorized access to its internal repositories, with no current evidence of impact to customer data.
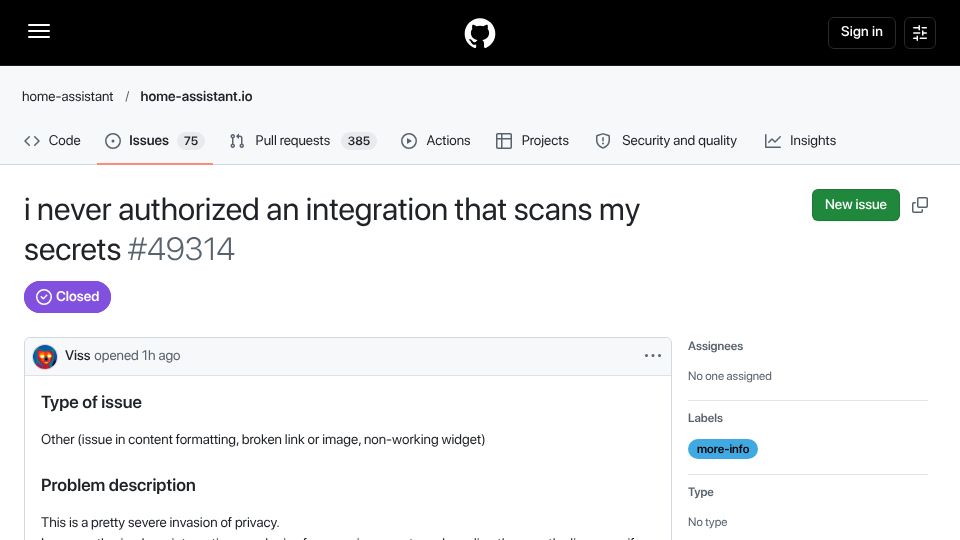
I never authorized an integration that scans my secrets(github.com)
202 points by trvrprkr | 155 comments
A closed GitHub issue on the home-assistant.io repo in which a user complains that an integration scanning their secrets was enabled without authorization, calling it a privacy invasion.
Open Source is one person(opensourcesecurity.io)
325 points by LawnGnome | 132 comments
Blog post by Josh Bressers on Open Source Security arguing that many open source projects are maintained by a single person.
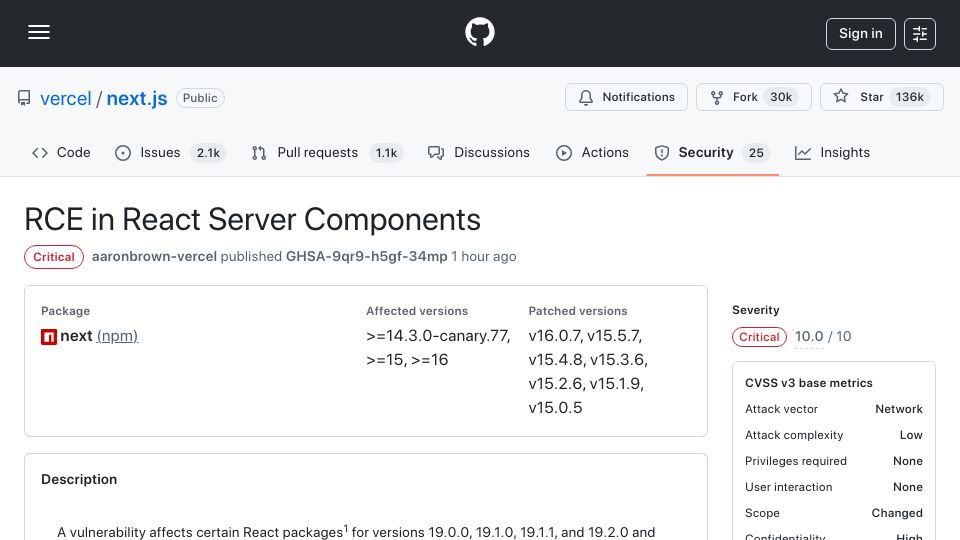
RCE Vulnerability in React and Next.js(github.com)
559 points by rayhaanj | 214 comments
GitHub security advisory GHSA-9qr9-h5gf-34mp for a critical (CVSS 10.0) remote code execution vulnerability in React Server Components affecting Next.js, with patched versions listed.
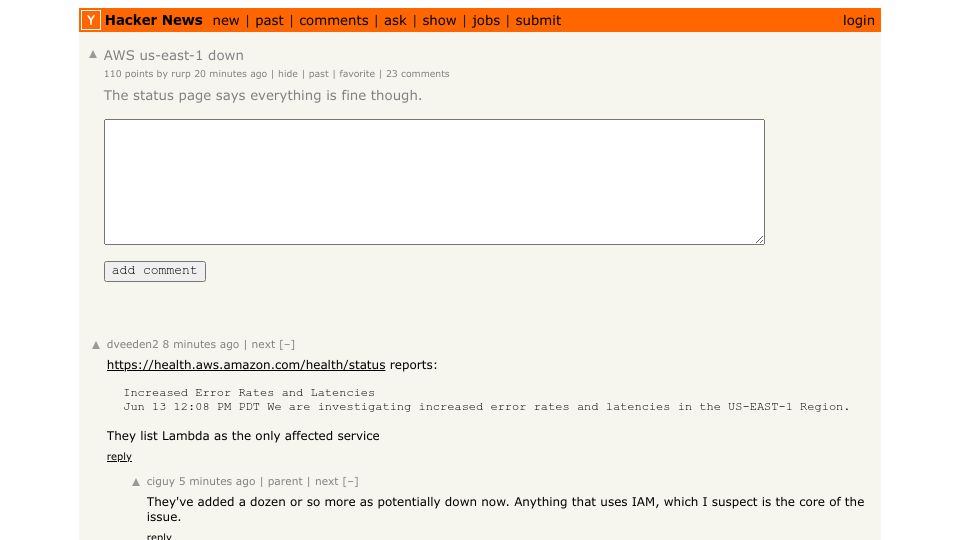
AWS us-east-1 down
567 points by rurp | 256 comments
Hacker News discussion thread reporting an AWS us-east-1 outage with increased error rates affecting Lambda and IAM-dependent services.
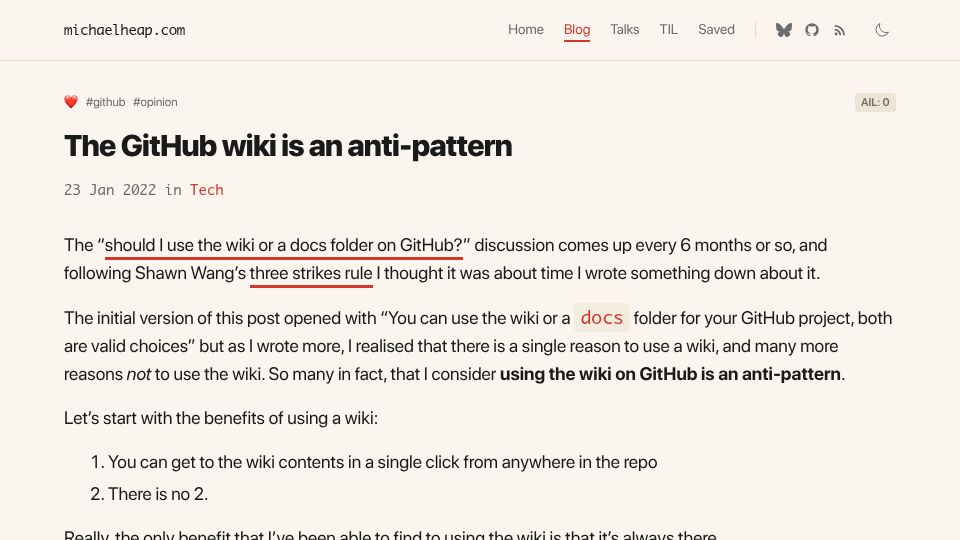
The GitHub wiki is an anti-pattern (2022)(michaelheap.com)
151 points by ibobev | 88 comments
A 2022 blog post by Michael Heap arguing that using the GitHub wiki for project documentation is an anti-pattern compared to a docs folder in the repo.