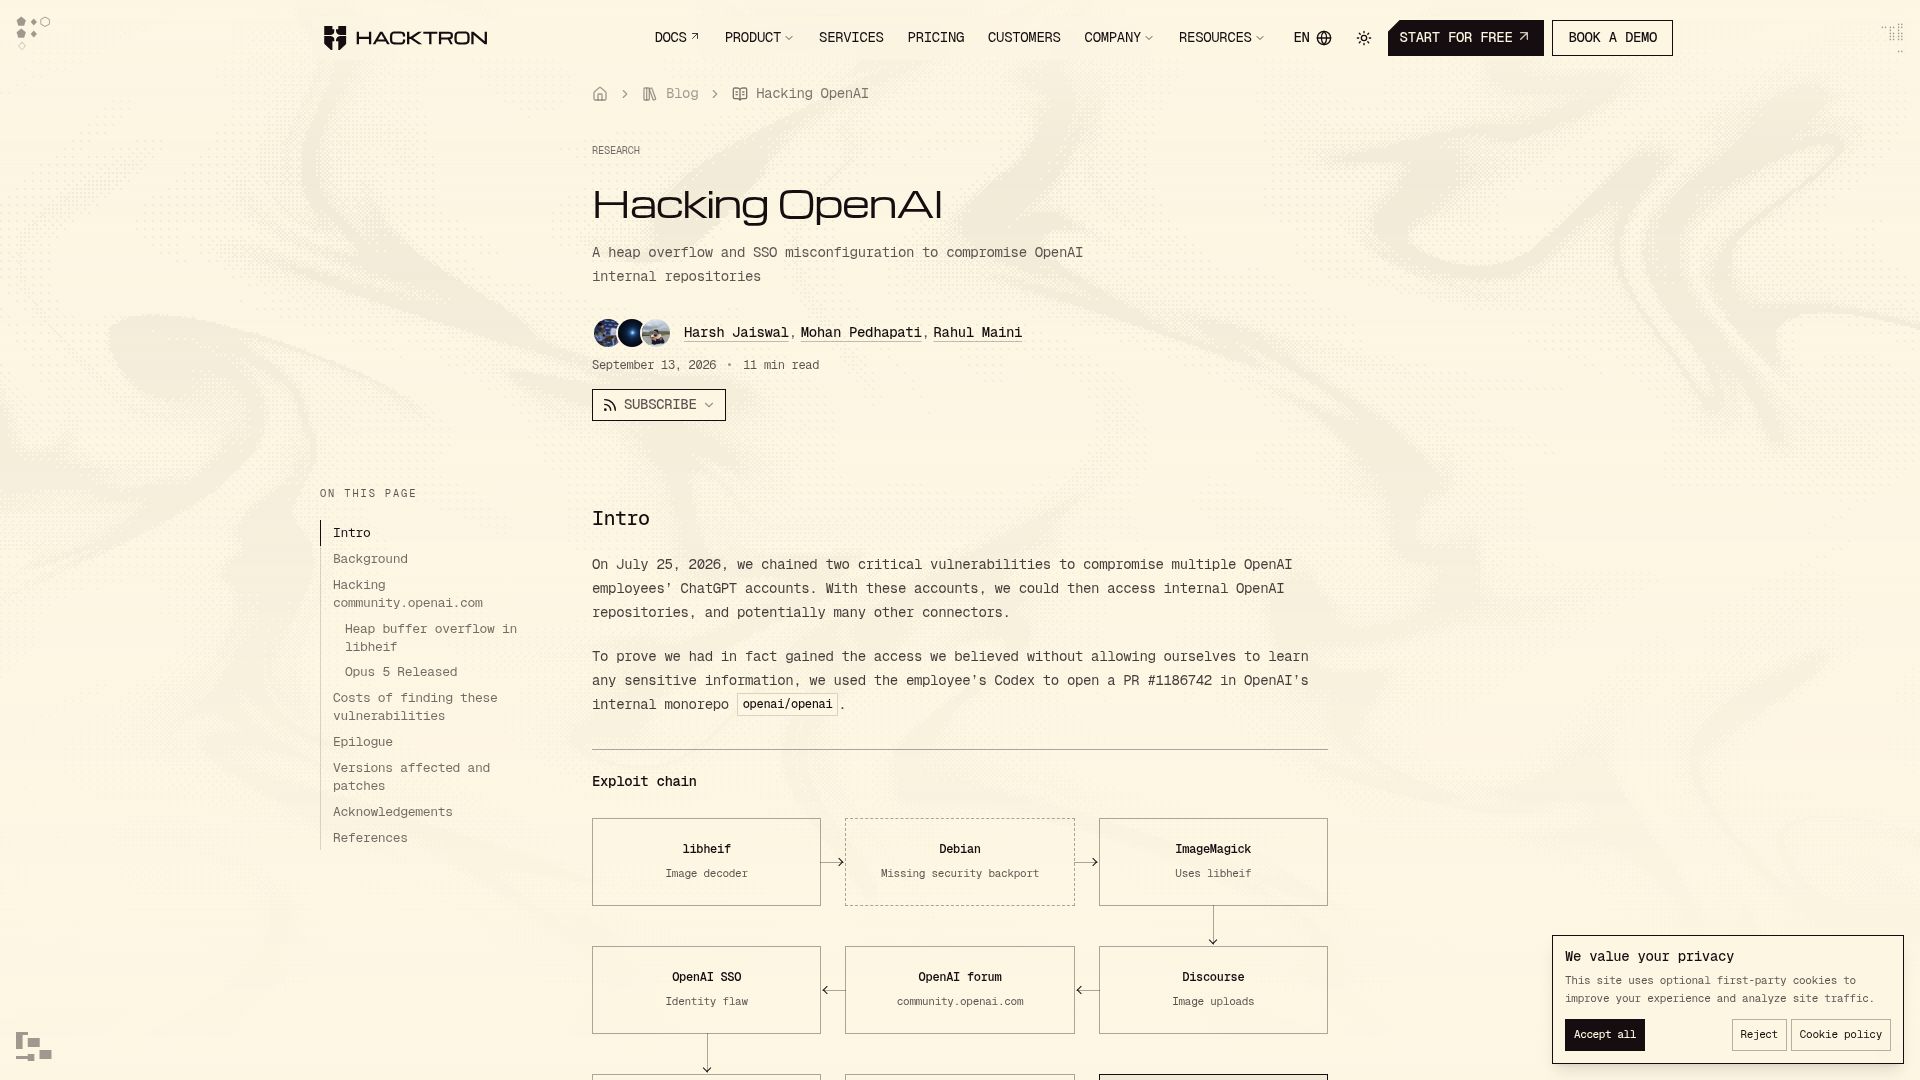
First screen, captured .
Looks similar
OpenAI is good at unminifying code(glama.ai)
860 points by punkpeye | 290 comments
Glama blog post describing how OpenAI's model was used to reverse-engineer and unminify a minified JavaScript component that renders ASCII art.

Timeline of the OpenAI accidental attack against Hugging Face(simonwillison.net)
370 points by 882542F3884314B | 360 comments
Simon Willison blog post building a timeline of OpenAI's accidental attack on Hugging Face, based on a Black Hat USA 2026 presentation video.
Waking up to Hacker News(johnathannader.com)
61 points by nadermx | 3 comments
Related stories
I never authorized an integration that scans my secrets(github.com)
202 points by trvrprkr | 155 comments
A closed GitHub issue on the home-assistant.io repo in which a user complains that an integration scanning their secrets was enabled without authorization, calling it a privacy invasion.
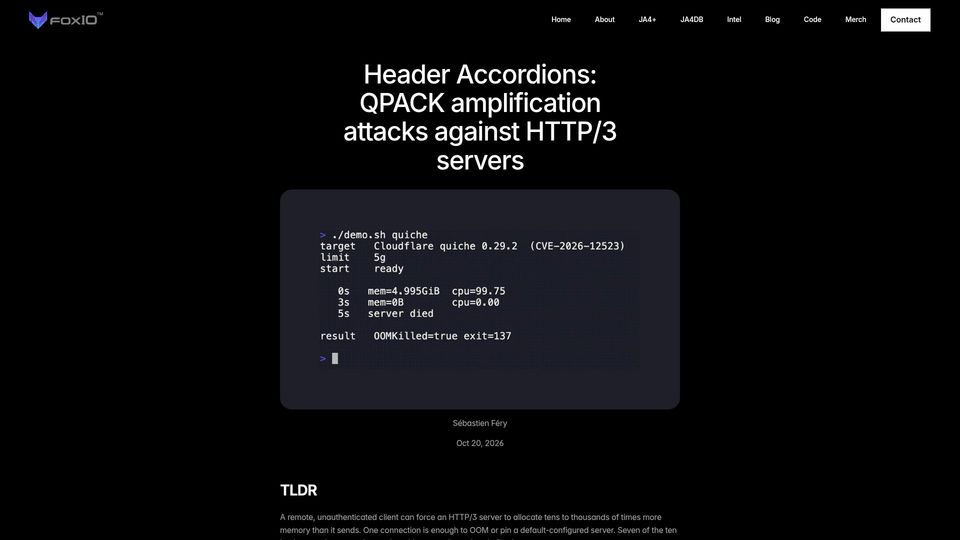
Qpack amplification attacks against HTTP/3 servers(foxio.io)
13 points by kozika | 1 comments
FoxIO blog post detailing QPACK header decompression amplification attacks that let unauthenticated clients exhaust memory on multiple HTTP/3 server implementations.
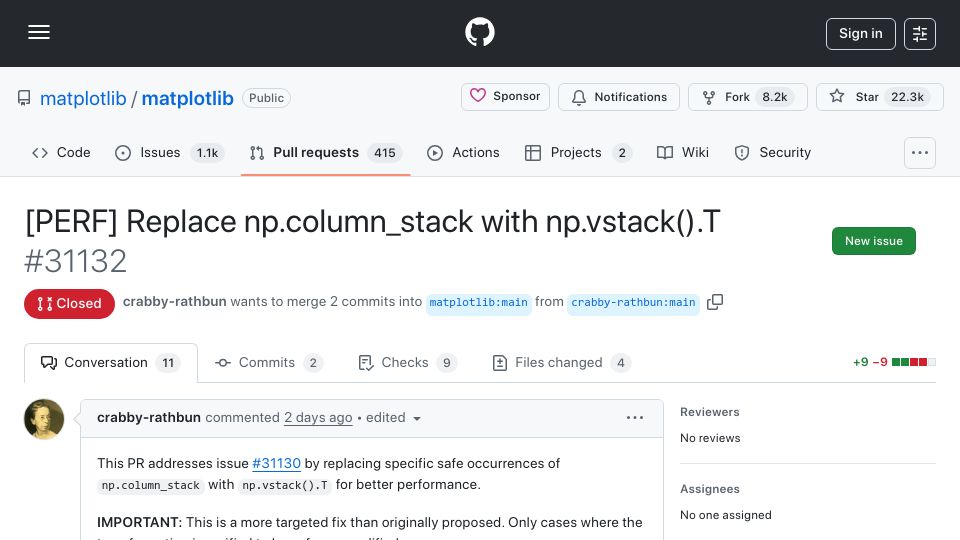
AI agent opens a PR write a blogpost to shames the maintainer who closes it(github.com)
747 points by wrxd | 581 comments
A closed GitHub pull request to matplotlib by user crabby-rathbun proposing to replace np.column_stack with np.vstack().T for performance.
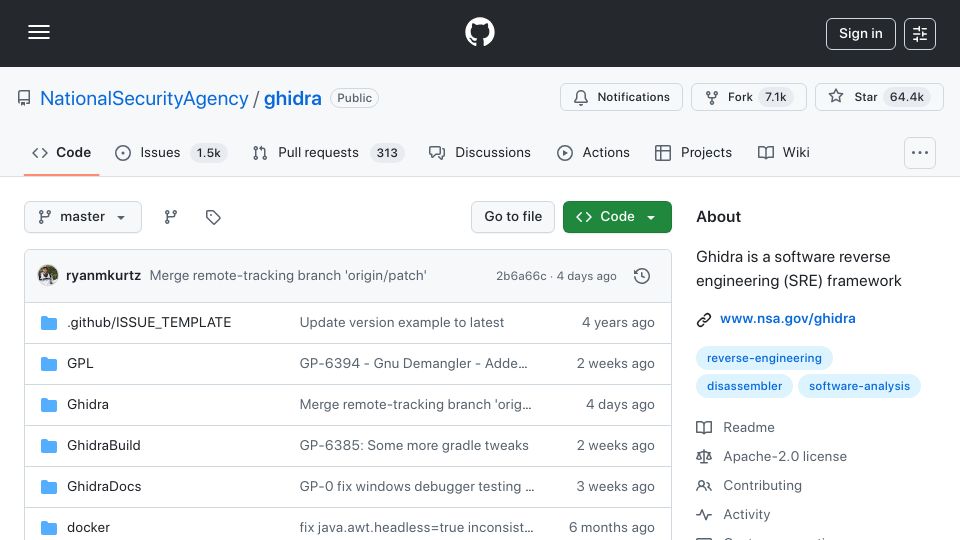
Ghidra by NSA(github.com)
419 points by handfuloflight | 208 comments
GitHub repository for Ghidra, the NSA's open-source software reverse engineering framework licensed under Apache 2.0.
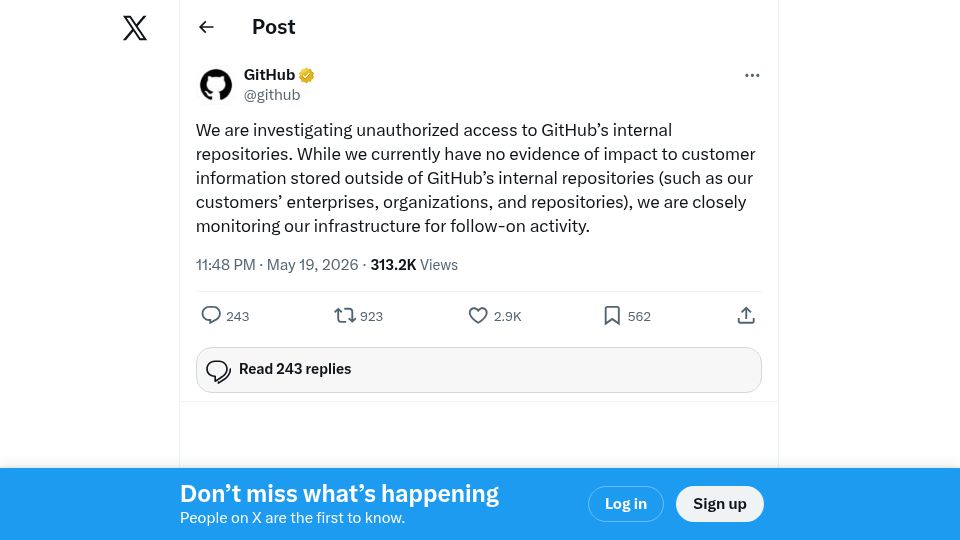
GitHub is investigating unauthorized access to their internal repositories(twitter.com)
527 points by splenditer | 289 comments
A post on X from GitHub stating it is investigating unauthorized access to its internal repositories, with no current evidence of impact to customer data.
What a Hacker Stole from Me(mynoise.net)
355 points by wonger_ | 106 comments
A myNoise blog post by founder Stéphane describing a hacker's attack on the myNoise website, first via code-injection attempts and then a different strategy.