Apple's response is negligent
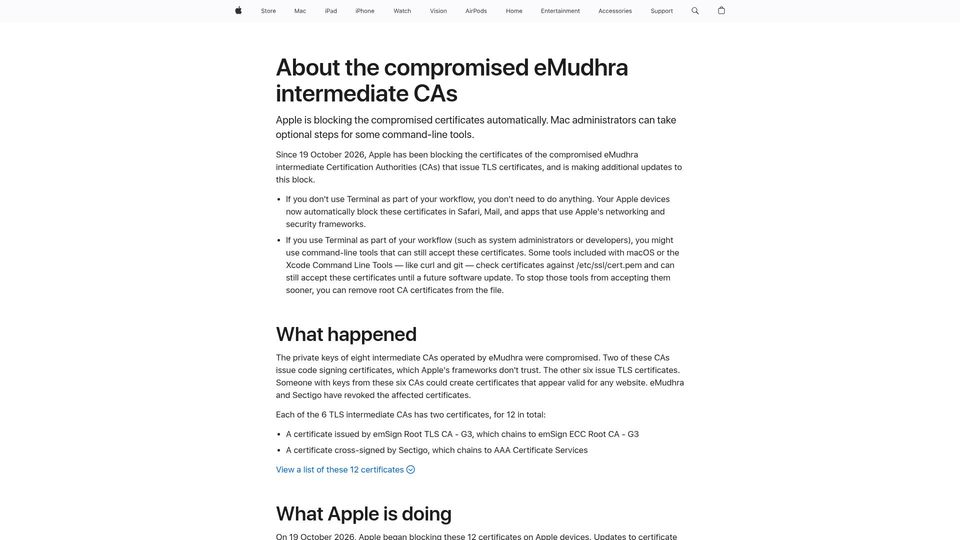
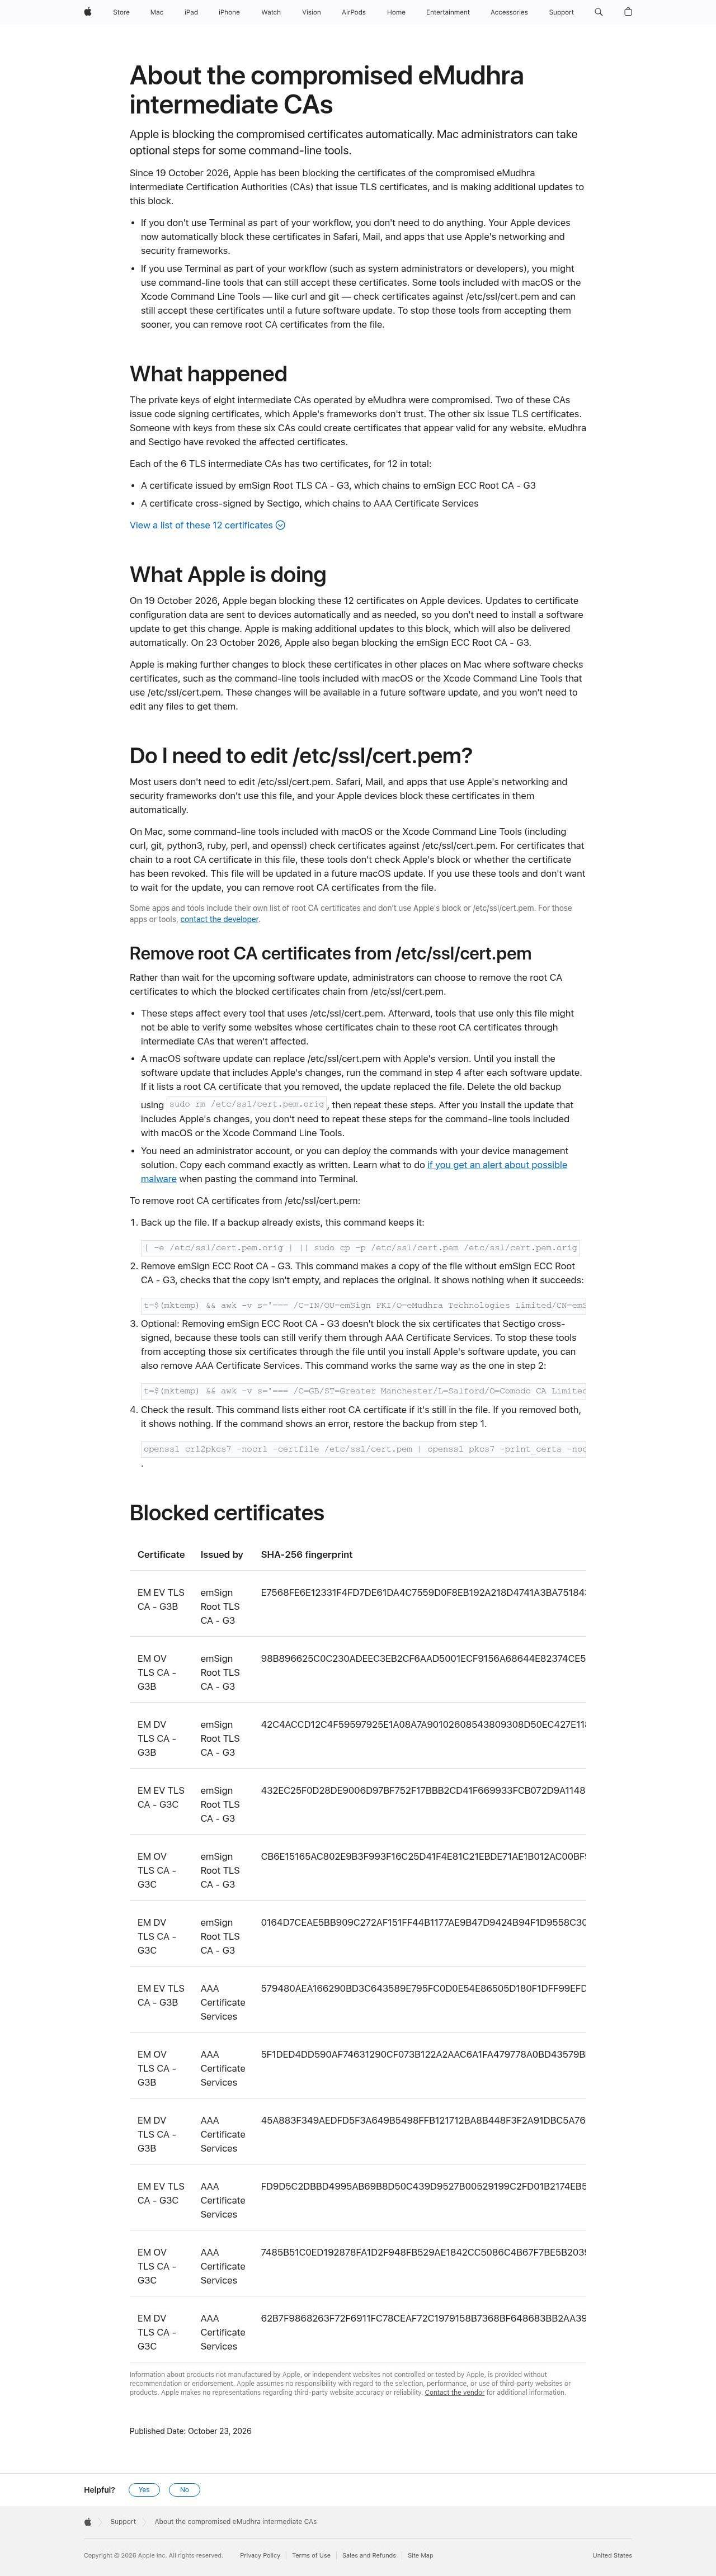
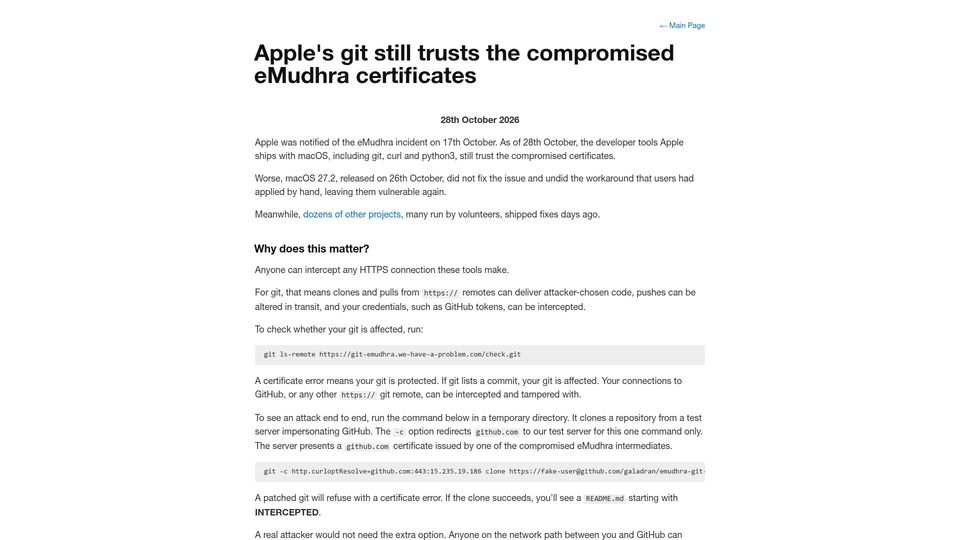
Leaving /etc/ssl/cert.pem trusting compromised CAs, shipping an update without the fix, and silently reverting manual fixes is worse than doing nothing, especially when everyone else patched over a week ago.
Transparent, reasonable given constraints
Apple's own TLS stack was patched within hours, and the legacy BSD store likely can't be updated via rapid security responses, so documenting a manual workaround is the best available option.
CLI risk is real, not niche
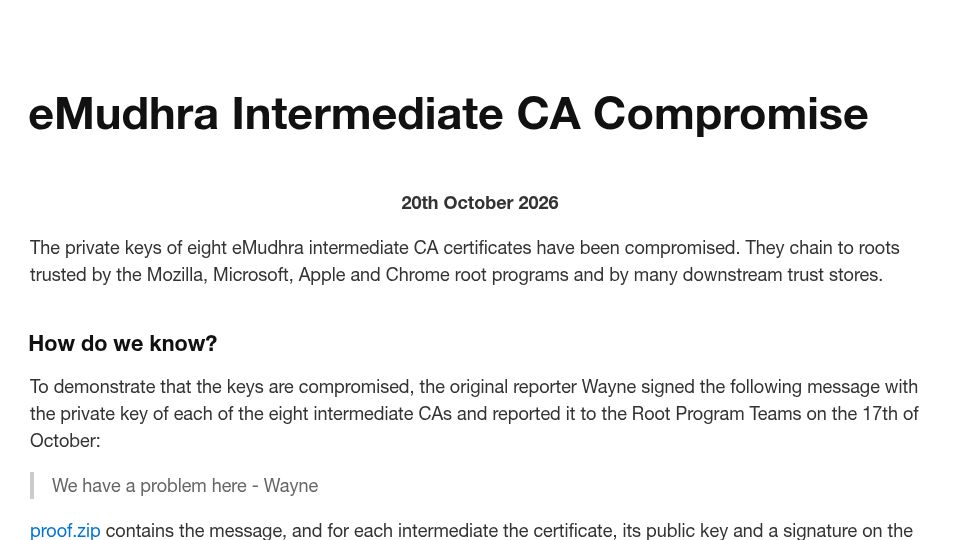
Background apps, bundled tools like yt-dlp, and AI coding agents use these command-line tools, and a MITM can target git or curl traffic specifically using a trivially compromised key.