OpenSSH 10.6(openssh.org)
97 points by torcete | 23 comments
Release notes for OpenSSH 10.6, noting many AI-assisted security bug reports, more frequent releases, and an upcoming deprecation of scp's -R flag.
13 stories tagged openssh, newest first.
97 points by torcete | 23 comments
Release notes for OpenSSH 10.6, noting many AI-assisted security bug reports, more frequent releases, and an upcoming deprecation of scp's -R flag.
4 points by zbruceli | 0 comments
Long-form blog profile of OpenSSH creator Theo de Raadt, covering his NetBSD exit, lost DARPA grant, and security-focused philosophy.
478 points by ingve | 166 comments
Apple man page apple_ssh_and_filevault(7) explaining how macOS 26 Tahoe allows unlocking a FileVault data volume remotely via SSH password authentication.
428 points by throw0101d | 114 comments
OpenSSH documentation page explaining its post-quantum key agreement algorithms, defaults since 9.0 and 10.0, and the warnings for non-PQ key exchange in OpenSSH 10.1.
781 points by robinhoodexe | 290 comments
Qualys security advisory describing CVE-2024-6387 (regreSSHion), a signal handler race condition enabling unauthenticated remote code execution in OpenSSH's sshd on glibc Linux.
368 points by zdw | 251 comments
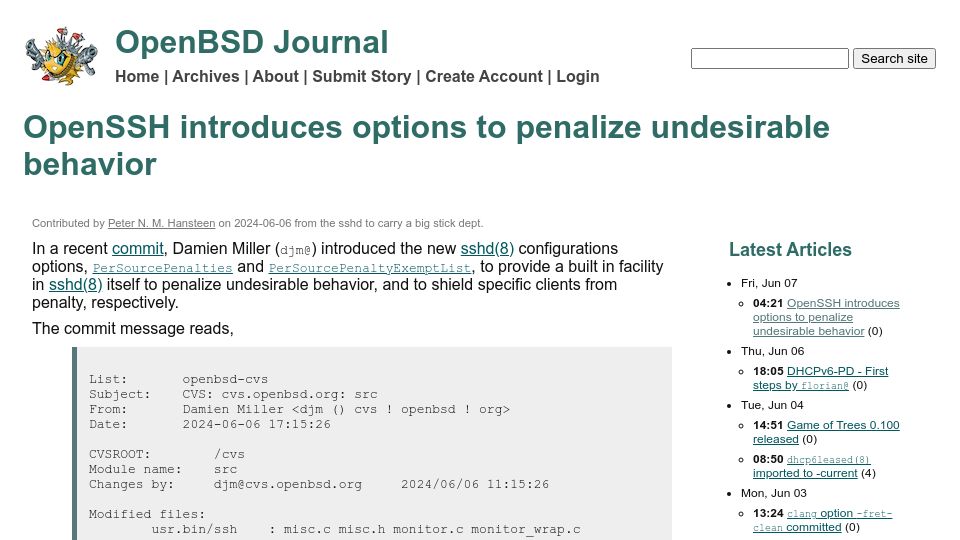
OpenBSD Journal article on Damien Miller's commit adding PerSourcePenalties and PerSourcePenaltyExemptList options to sshd to penalize undesirable client behavior.
381 points by nathell | 212 comments
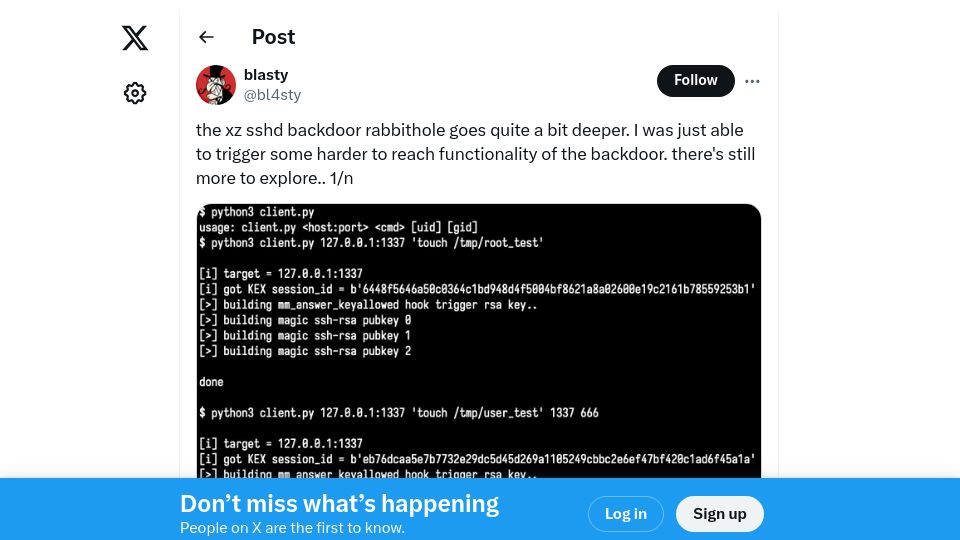
A post on X by security researcher blasty showing he triggered deeper, harder-to-reach functionality of the xz sshd backdoor, with a terminal screenshot of a client script.
967 points by todsacerdoti | 431 comments
Russ Cox's blog post giving a detailed timeline of the social engineering behind the xz/liblzma backdoor attack by "Jia Tan".
816 points by q3k | 425 comments
GitHub repository with notes, a honeypot, and an exploit demo for the xz backdoor (CVE-2024-3094), including Go code and an OpenSSH patch.
439 points by ecliptik | 90 comments
Gynvael Coldwind's blog post explaining the obfuscation techniques used in the bash stages of the xz/liblzma backdoor that affected OpenSSH.
1207 points by junon | 743 comments
Bluesky post by Filippo Valsorda sharing preliminary analysis that the xz backdoor enables gated, unreplayable RCE via a hooked RSA_public_decrypt verifying an Ed448 signature.
4122 points by rkta | 1526 comments
Andres Freund's oss-security mailing list post disclosing a backdoor in upstream xz/liblzma tarballs 5.6.0 and 5.6.1 that compromises SSH servers.
556 points by zdw | 239 comments
OpenBSD Journal post announcing Damien Miller's commit adding keystroke timing obfuscation with chaff keystrokes to OpenSSH's ssh client.