First screen, captured .
Looks similar
Amazon identifies Oct 17 PHP2Shell exploitation prior to public disclosure(aws.amazon.com)
227 points by cubefox | 98 comments
AWS Security Blog post reporting that Amazon's MadPot honeypots saw PHP2Shell exploitation attempts four days before public disclosure, with IOCs and recommended actions.
Related stories
Microsoft technical breakdown of CrowdStrike incident(microsoft.com)
318 points by nar001 | 304 comments
Microsoft Security blog post by David Weston on Windows security best practices for integrating security tools, including a technical analysis of the CrowdStrike outage.
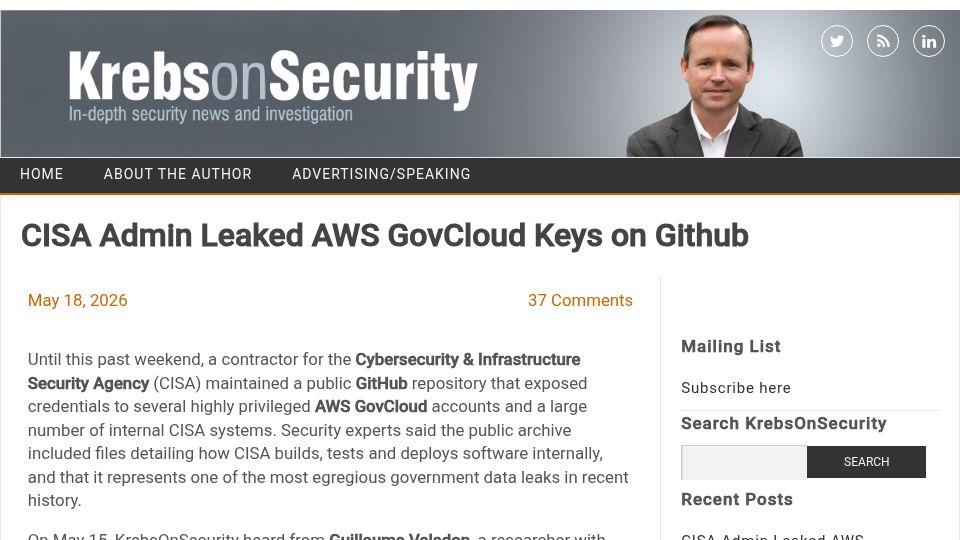
CISA Admin Leaked AWS GovCloud Keys on GitHub(krebsonsecurity.com)
433 points by LelouBil | 171 comments
KrebsOnSecurity article reporting that a CISA contractor kept a public GitHub repository exposing privileged AWS GovCloud credentials and internal CISA system details.
I found a Vulnerability. They found a Lawyer(dixken.de)
831 points by toomuchtodo | 381 comments
Blog post by a diving instructor and platform engineer recounting how reporting a security vulnerability led to a legal response from the affected organization.
I could've accessed 17T Microsoft records(blog.faav.net)
287 points by luispa | 120 comments
A security researcher's blog post describing a Microsoft internal analytics service flaw where unchecked token signatures allowed admin access to query 17.3 trillion records.
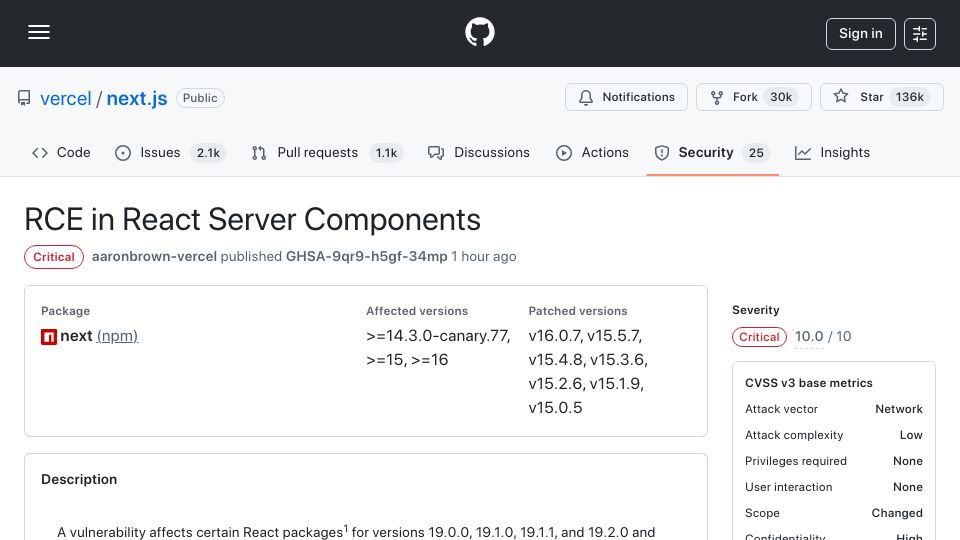
RCE Vulnerability in React and Next.js(github.com)
559 points by rayhaanj | 214 comments
GitHub security advisory GHSA-9qr9-h5gf-34mp for a critical (CVSS 10.0) remote code execution vulnerability in React Server Components affecting Next.js, with patched versions listed.
Nvidia's Risky Business(stratechery.com)
325 points by jonbaer | 157 comments
Stratechery article by Ben Thompson analyzing Nvidia's business risks, opening with a historical anecdote about financier Jay Cooke.