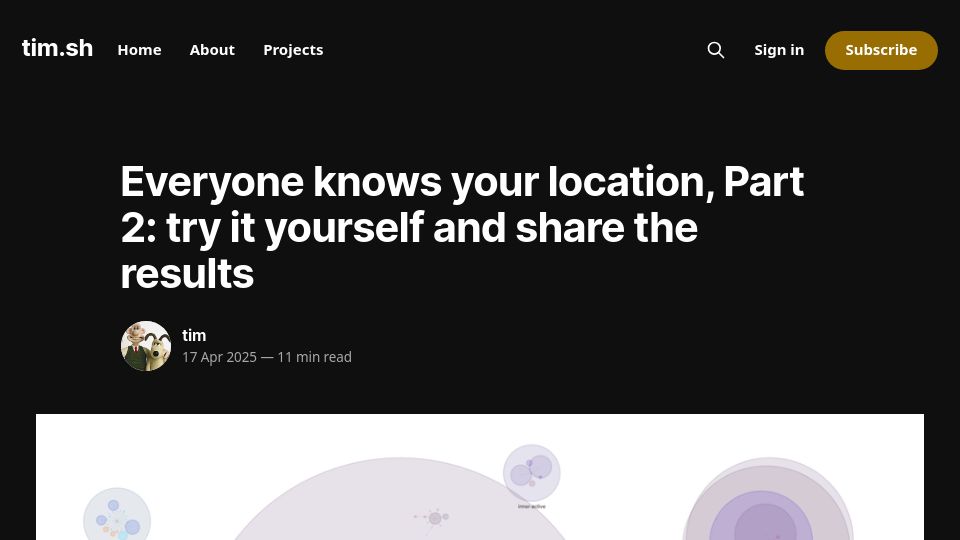

First screen, captured .
Looks similar
Apple allows some iOS apps to track user locations via lists of nearby SSIDs(wingu.se)
722 points by lloyds_barclays | 264 comments
Blog post arguing that Apple's iOS HotspotHelper API, available since iOS 9, lets apps infer user locations from nearby Wi-Fi networks without user authorization.
Related stories
Stealing OAuth tokens of Microsoft accounts via open redirect in Harvest App(eval.blog)
349 points by skilled | 102 comments
A security researcher's write-up on leaking Microsoft account OAuth tokens through an open redirect vulnerability in the Harvest time-tracking app.
Stealing Reasoning Traces from Proprietary LLM APIs(stolen-thoughts.com)
665 points by quantumgarbage | 295 comments
Project page for a research paper on extracting hidden reasoning traces from proprietary LLM APIs, by authors from MATS, ELLIS, Max Planck and Tübingen.
Disrupting the first reported AI-orchestrated cyber espionage campaign(anthropic.com)
341 points by koakuma-chan | 261 comments
Anthropic news post describing how it detected and disrupted a cyber espionage campaign largely orchestrated using its Claude AI model, with a linked full report.
How did Facebook intercept their competitor's encrypted mobile app traffic?(doubleagent.net)
408 points by haxrob | 161 comments
A technical investigation into class action lawsuit claims that Facebook used the Onavo Protect app to intercept encrypted traffic from competitors' mobile apps.
What a Hacker Stole from Me(mynoise.net)
355 points by wonger_ | 106 comments
A myNoise blog post by founder Stéphane describing a hacker's attack on the myNoise website, first via code-injection attempts and then a different strategy.
Privacy doesn't mean anything anymore, anonymity does(servury.com)
390 points by ybceo | 252 comments
A blog post from Servury arguing that privacy has become a marketing term and that true anonymity must be built into system architecture; page showed a Cloudflare check.