First screen, captured .
Looks similar
"Localhost tracking" explained. It could cost Meta €32B(zeropartydata.es)
330 points by donohoe | 167 comments
Substack post explaining Meta's "localhost tracking" technique that bypassed Android sandboxing to identify users' browsing, and the potential €32B regulatory fines.
Io_uring, kTLS and Rust for zero syscall HTTPS server(blog.habets.se)
444 points by guntars | 138 comments
Blog post describing building an HTTPS web server in Rust using io_uring and kernel TLS to avoid system calls on the request path.
Dear Ubuntu(hackaday.com)
43 points by Alupis | 37 comments
Abusing Ahrefs backlink checker(trickster.dev)
45 points by rl1987 | 16 comments
Related stories
AI-Built Torrent Site Looks Inside Downloads to Catch Fakes and Malware(torrentfreak.com)
6 points by HieronymusBosch | 1 comments
TorrentFreak article on TorrentClaw, an AI-built torrent search engine whose TrueSpec feature inspects torrent contents, revealing a malware trick using a genuine VLC player as a decoy.
Shutting down my legal torrent site after 17 years(legittorrents.info)
706 points by en3r0 | 366 comments
Farewell page for Legit Torrents, a legal torrent tracker run from 2005 to 2023, explaining its shutdown after a null route and looking back on its history.
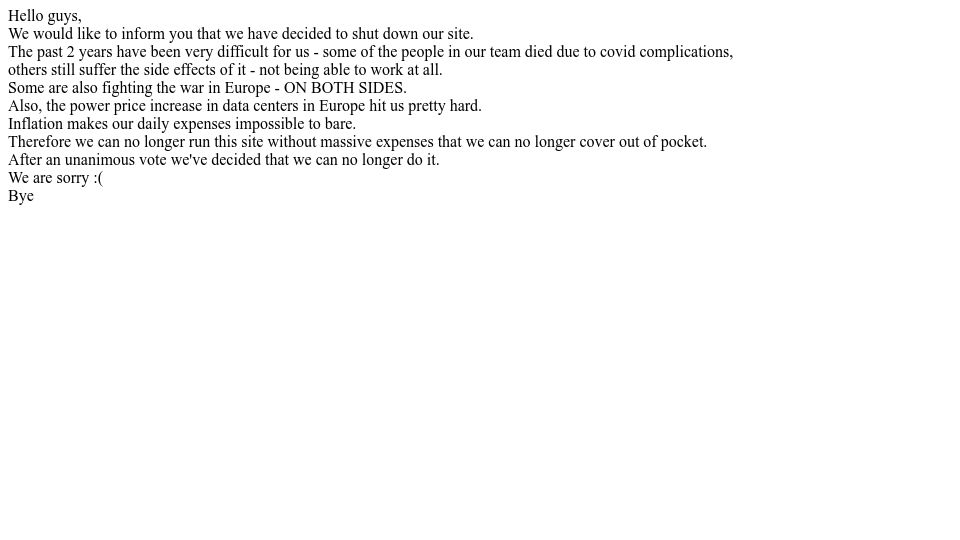
Rarbg Is No More(web.archive.org)
1275 points by 0___0 | 519 comments
Archived RARBG shutdown notice explaining the torrent site is closing due to team deaths from covid, the war in Europe, energy costs, and inflation.
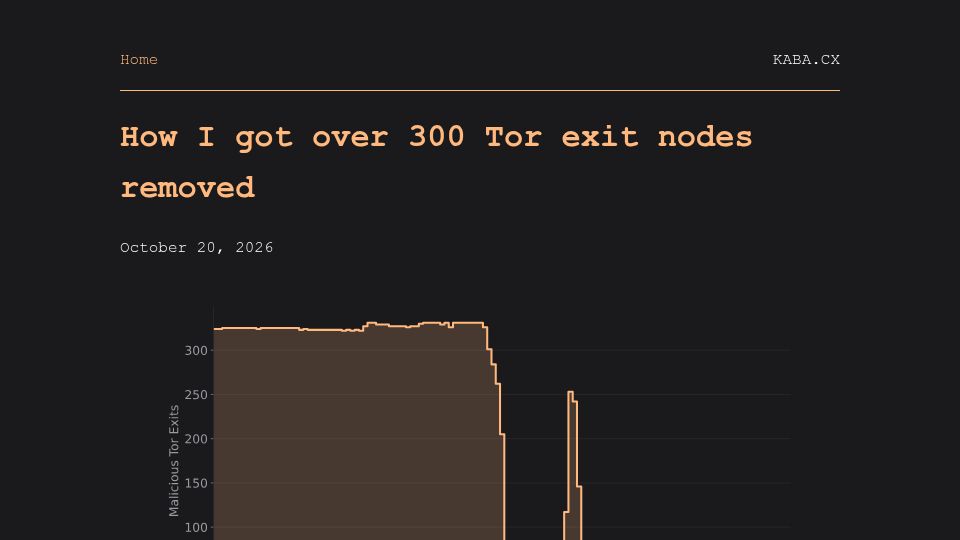
How I got over 300 Tor exit nodes removed(kaba.cx)
346 points by kabakabakaba | 104 comments
Blog post describing how the author identified and got over 300 malicious Tor exit nodes removed, with a chart of malicious exit counts over time.
RCE Vulnerability in QBittorrent(sharpsec.run)
352 points by udev4096 | 173 comments
Security blog post disclosing that qBittorrent's DownloadManager ignored SSL certificate errors for 14 years, enabling remote code execution, fixed in version 5.0.1.
I'm being cyberattacked by Tesla, Inc(dreamstation.systems)
389 points by robinpie | 109 comments
Personal blog post describing persistent attack traffic in nginx logs from IPs with Host/Referer headers pointing to pool-ntp.tesla.com.