First screen, captured .
Looks similar
GitLab discovers widespread NPM supply chain attack(about.gitlab.com)
330 points by OuterVale | 181 comments
GitLab blog post describing a widespread npm supply chain malware attack that includes a "dead man's switch" capable of harming user data.
Related stories
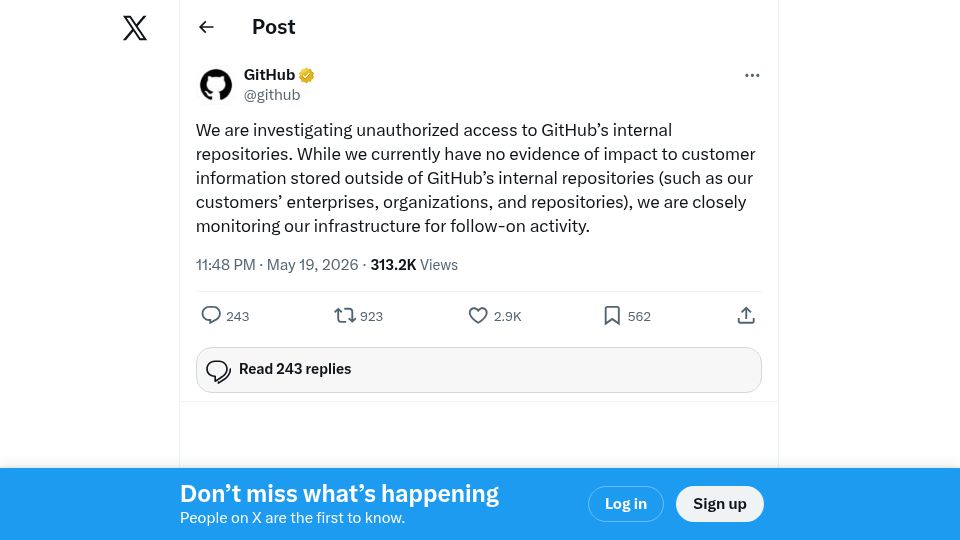
GitHub is investigating unauthorized access to their internal repositories(twitter.com)
527 points by splenditer | 289 comments
A post on X from GitHub stating it is investigating unauthorized access to its internal repositories, with no current evidence of impact to customer data.
GitHub has not removed malicious imitation software after 3 weeks(successfulsoftware.net)
215 points by hermitcrab | 89 comments
A Successful Software blog post complaining that GitHub has not removed malicious software imitating the author's product three weeks after it was reported.
AI Companies Are Trying to Hide a Staggering Amount of Debt(futurism.com)
628 points by technewssss | 317 comments
Futurism article reporting that AI companies are using off-balance-sheet arrangements to hide large amounts of debt.
What a Hacker Stole from Me(mynoise.net)
355 points by wonger_ | 106 comments
A myNoise blog post by founder Stéphane describing a hacker's attack on the myNoise website, first via code-injection attempts and then a different strategy.
We hacked Gemini's Python sandbox and leaked its source code (at least some)(landh.tech)
627 points by topsycatt | 127 comments
Lupin & Holmes blog post describing how researchers probed Google Gemini's Python code-execution sandbox and extracted parts of its internal source code.
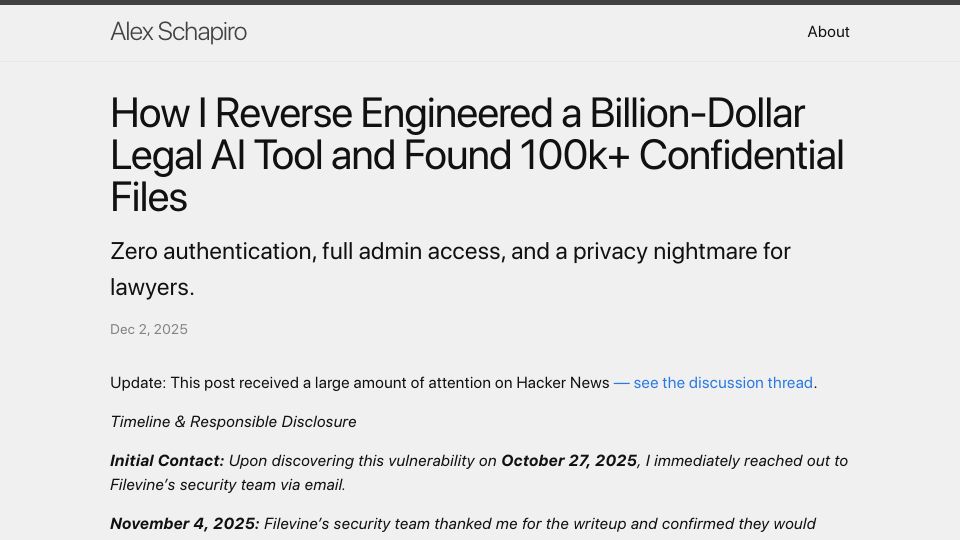
Reverse engineering a $1B Legal AI tool exposed 100k+ confidential files(alexschapiro.com)
752 points by bearsyankees | 258 comments
A blog post describing how the author found an unauthenticated API flaw in Filevine's legal AI tool exposing 100k+ confidential files, with a disclosure timeline.