First screen, captured .
Looks similar
How we exploited CodeRabbit: From simple PR to RCE and write access on 1M repos(research.kudelskisecurity.com)
657 points by spiridow | 219 comments
Kudelski Security research post describing how a pull request to CodeRabbit led to remote code execution and write access to about one million repositories.
Related stories
Claude Code can debug low-level cryptography(words.filippo.io)
446 points by Bogdanp | 199 comments
Filippo Valsorda's blog post on using Claude Code to debug his new Go implementation of the ML-DSA post-quantum signature algorithm.
Io_uring, kTLS and Rust for zero syscall HTTPS server(blog.habets.se)
444 points by guntars | 138 comments
Blog post describing building an HTTPS web server in Rust using io_uring and kernel TLS to avoid system calls on the request path.
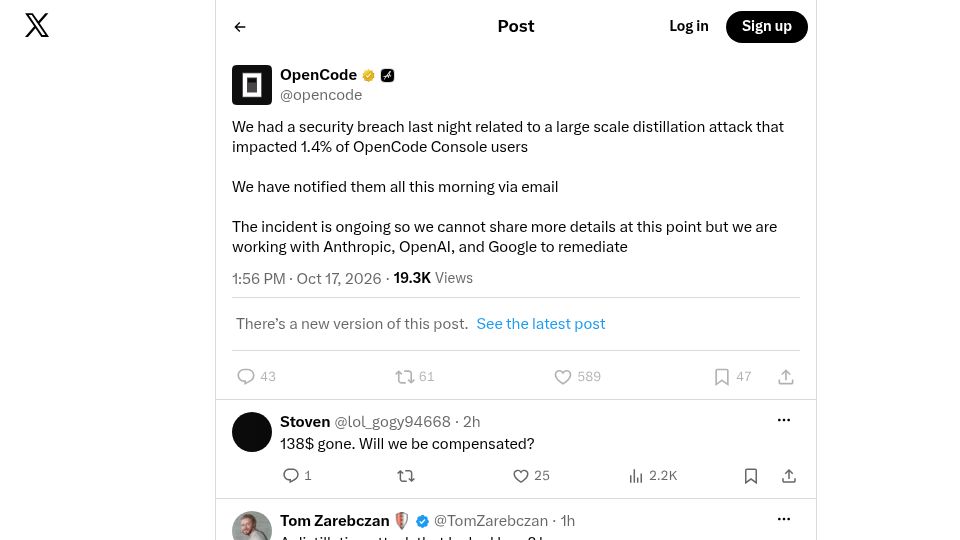
OpenCode Hacked: User credentials leaked(twitter.com)
794 points by pranshuchittora | 145 comments
OpenCode's post on X announcing a security breach tied to a large-scale distillation attack that affected 1.4% of OpenCode Console users.
Infosec 101 for Activists(infosecforactivists.org)
440 points by greenie_beans | 174 comments
Infosec 101 for Activists is a guide by Drew Bjorn, Mark Sherman, and Blake Skinner on digital security practices for US activists attending protests.
Cyber Security: A pre-war reality check(berthub.eu)
446 points by edent | 199 comments
Bert Hubert's lightly edited transcript of his talk at the ACCSS/NCSC/Surf 'Cyber Security and Society' seminar on cybersecurity preparedness ahead of potential war.
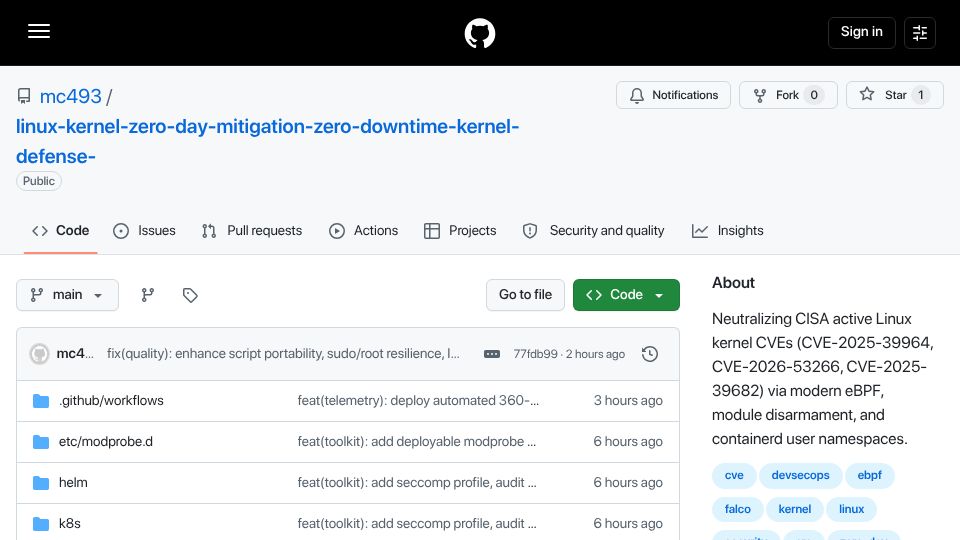
Zero-downtime Linux kernel zero-day mitigation via eBPF and SECCOMP(github.com)
5 points by mc493 | 0 comments
GitHub repository with a toolkit for mitigating actively exploited Linux kernel CVEs without reboots using eBPF, module disarmament, seccomp profiles, and user namespaces.