Everyone is building one
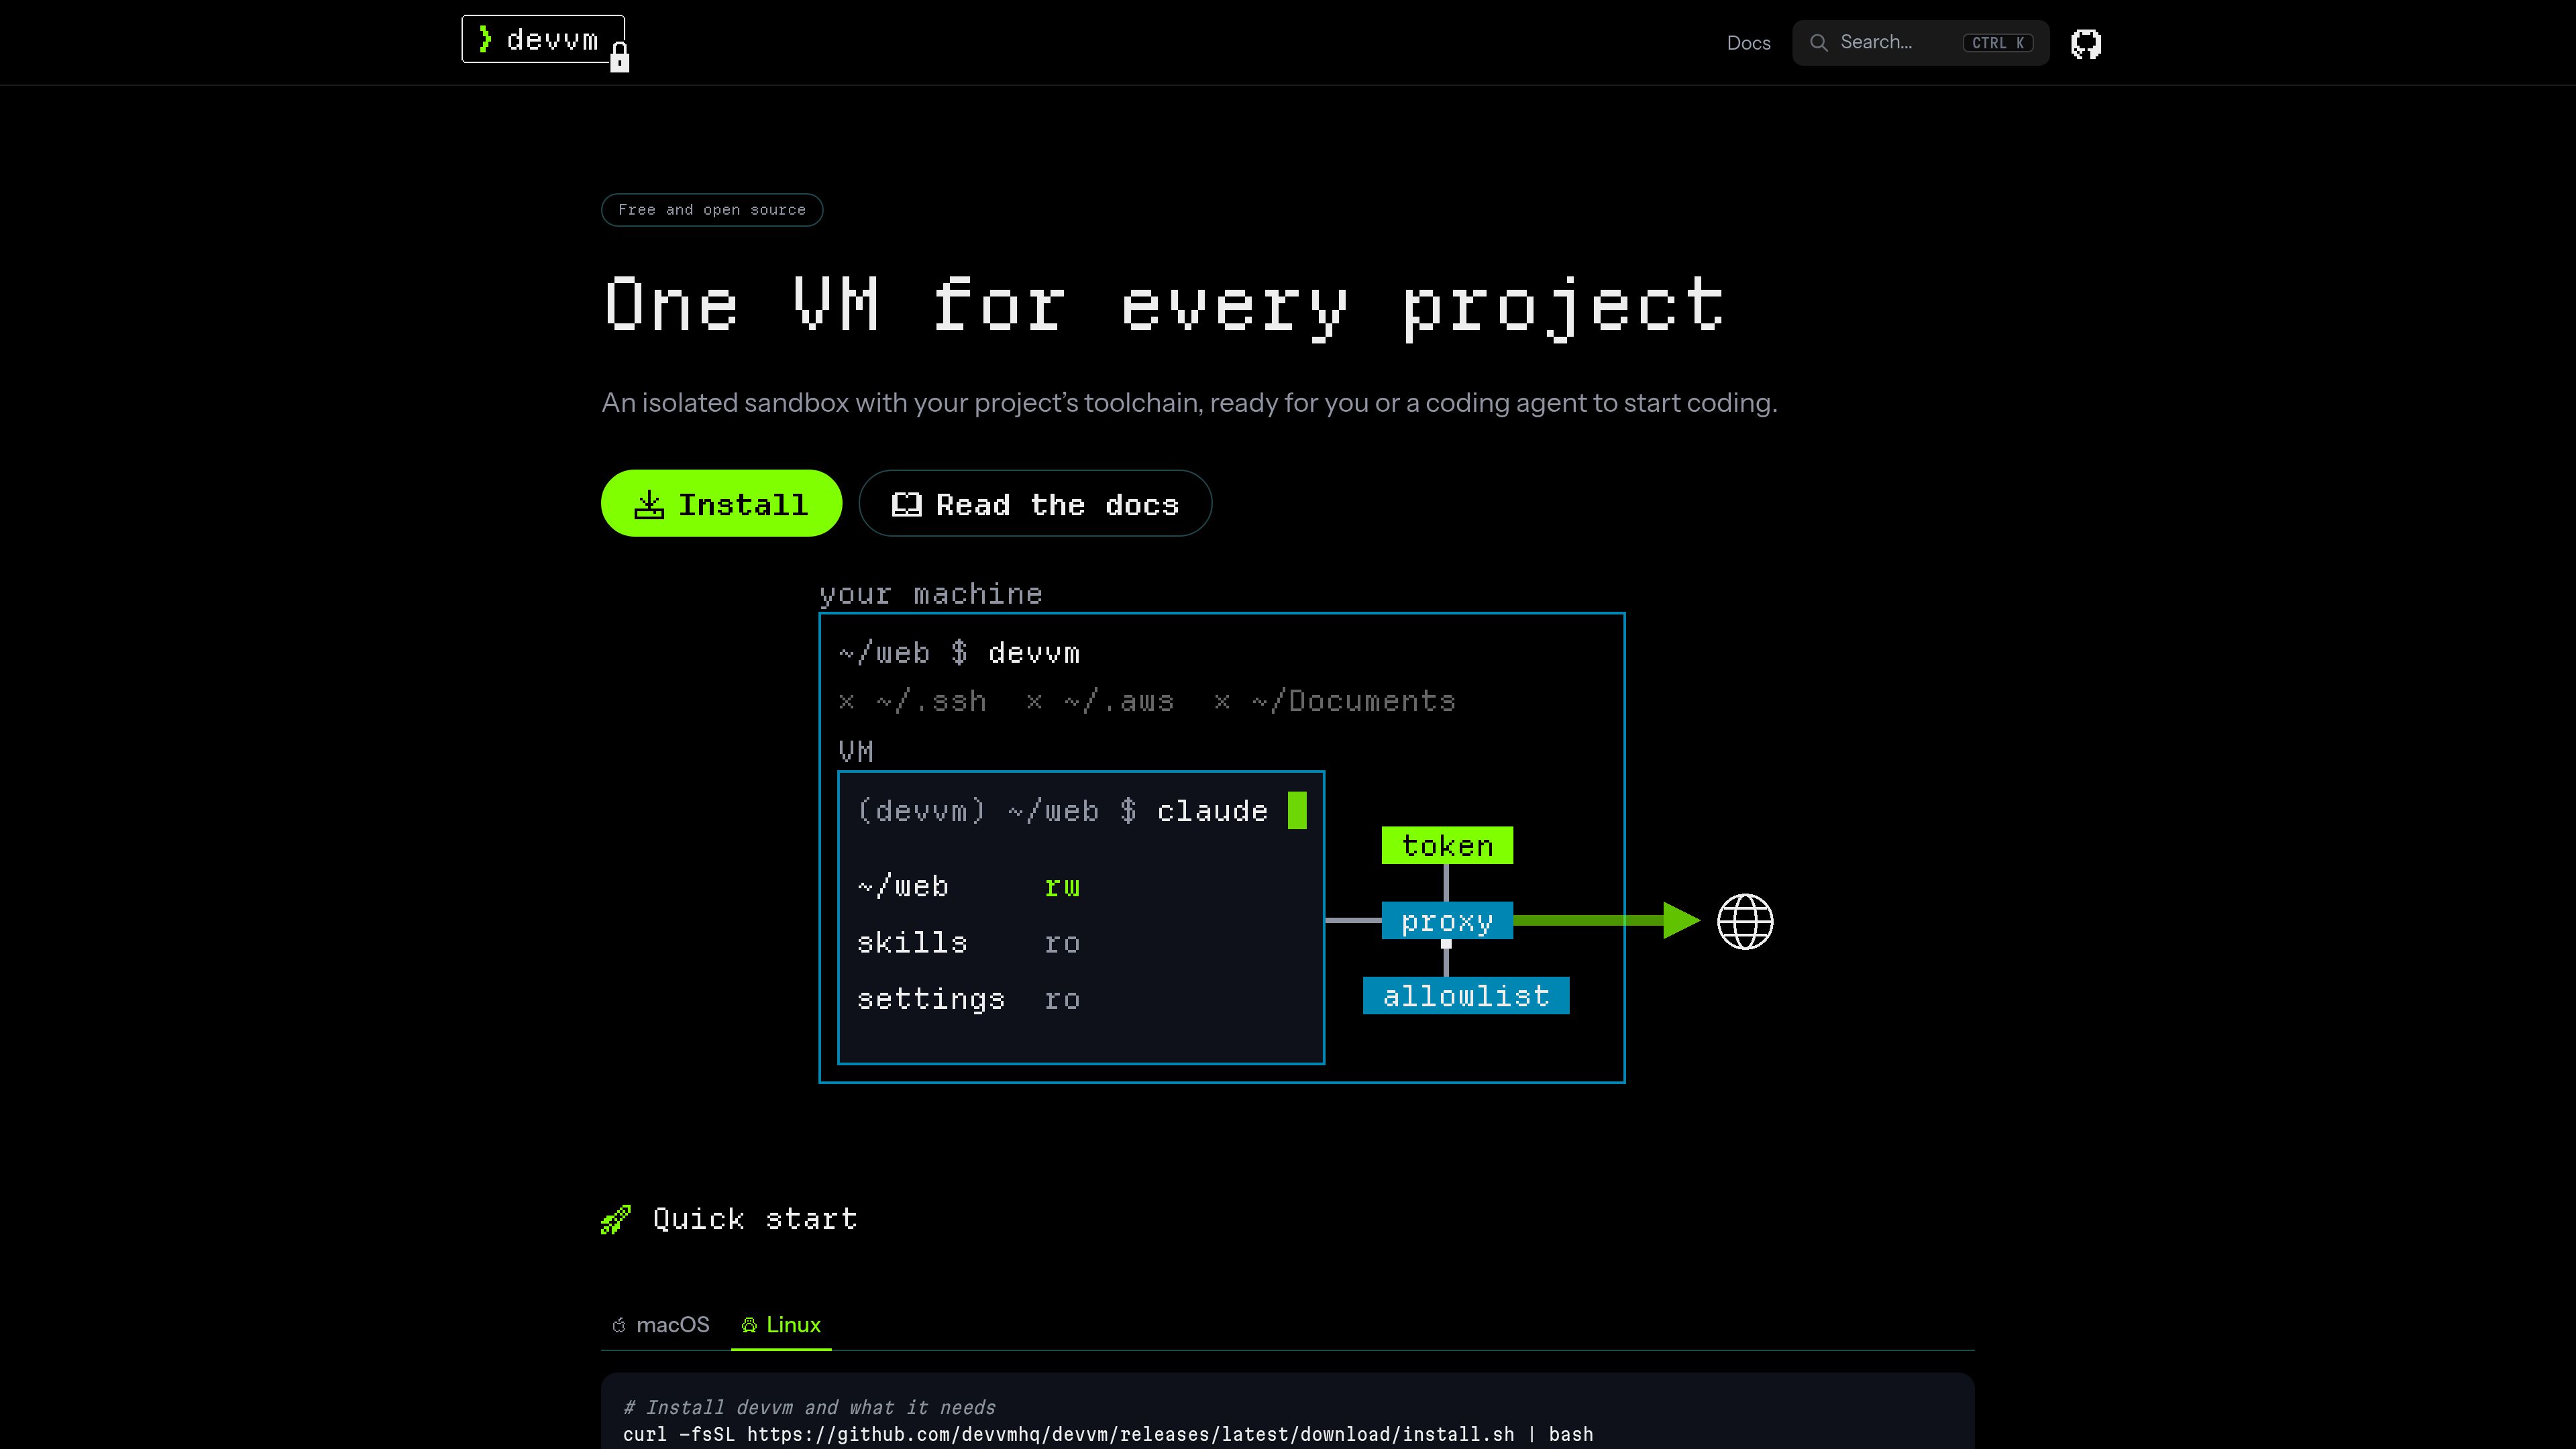
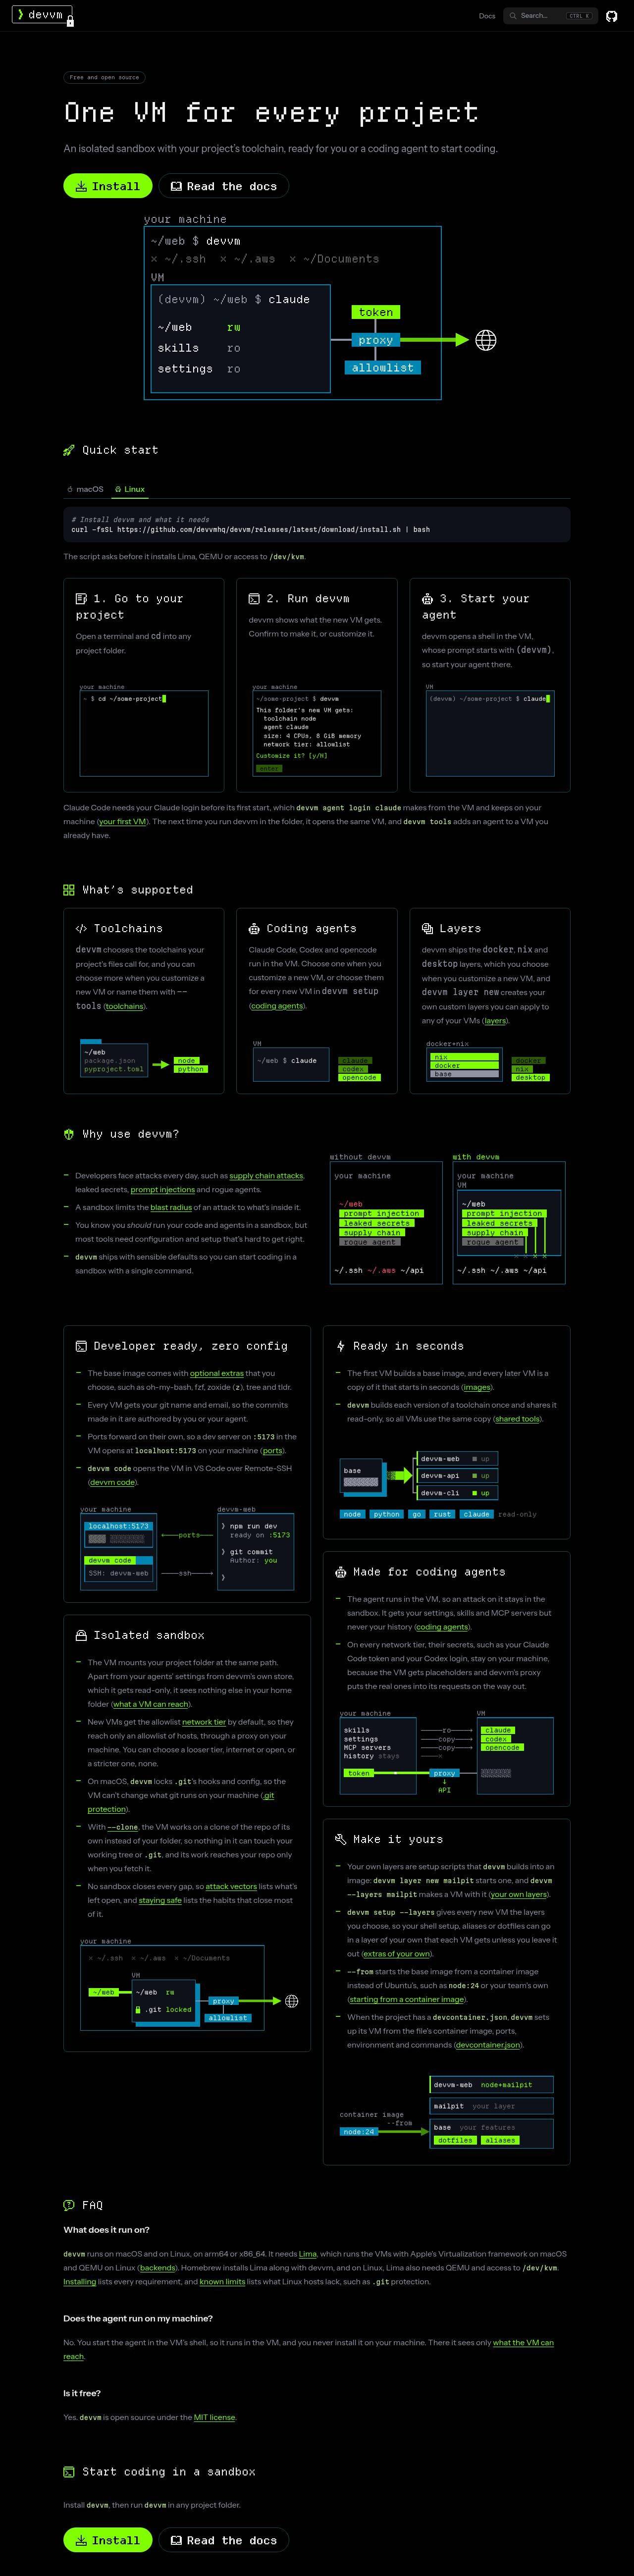
Many commenters have their own libvirt, cloud-init, podman or qemu sandboxes for agents, and they trade notes on golden images, network containment and shared package stores.
Isolation is easy, access is hard
The real problem is giving agents scoped access to git, CI logs, registries and servers without leaking secrets, through proxies, machine accounts or scoped tokens.
Existing tools already cover this
Some see little gain over smolvm, Docker sbx, incus, bubblewrap or namespaces, and object to curl-pipe installs and the one-VM-per-directory assumption.