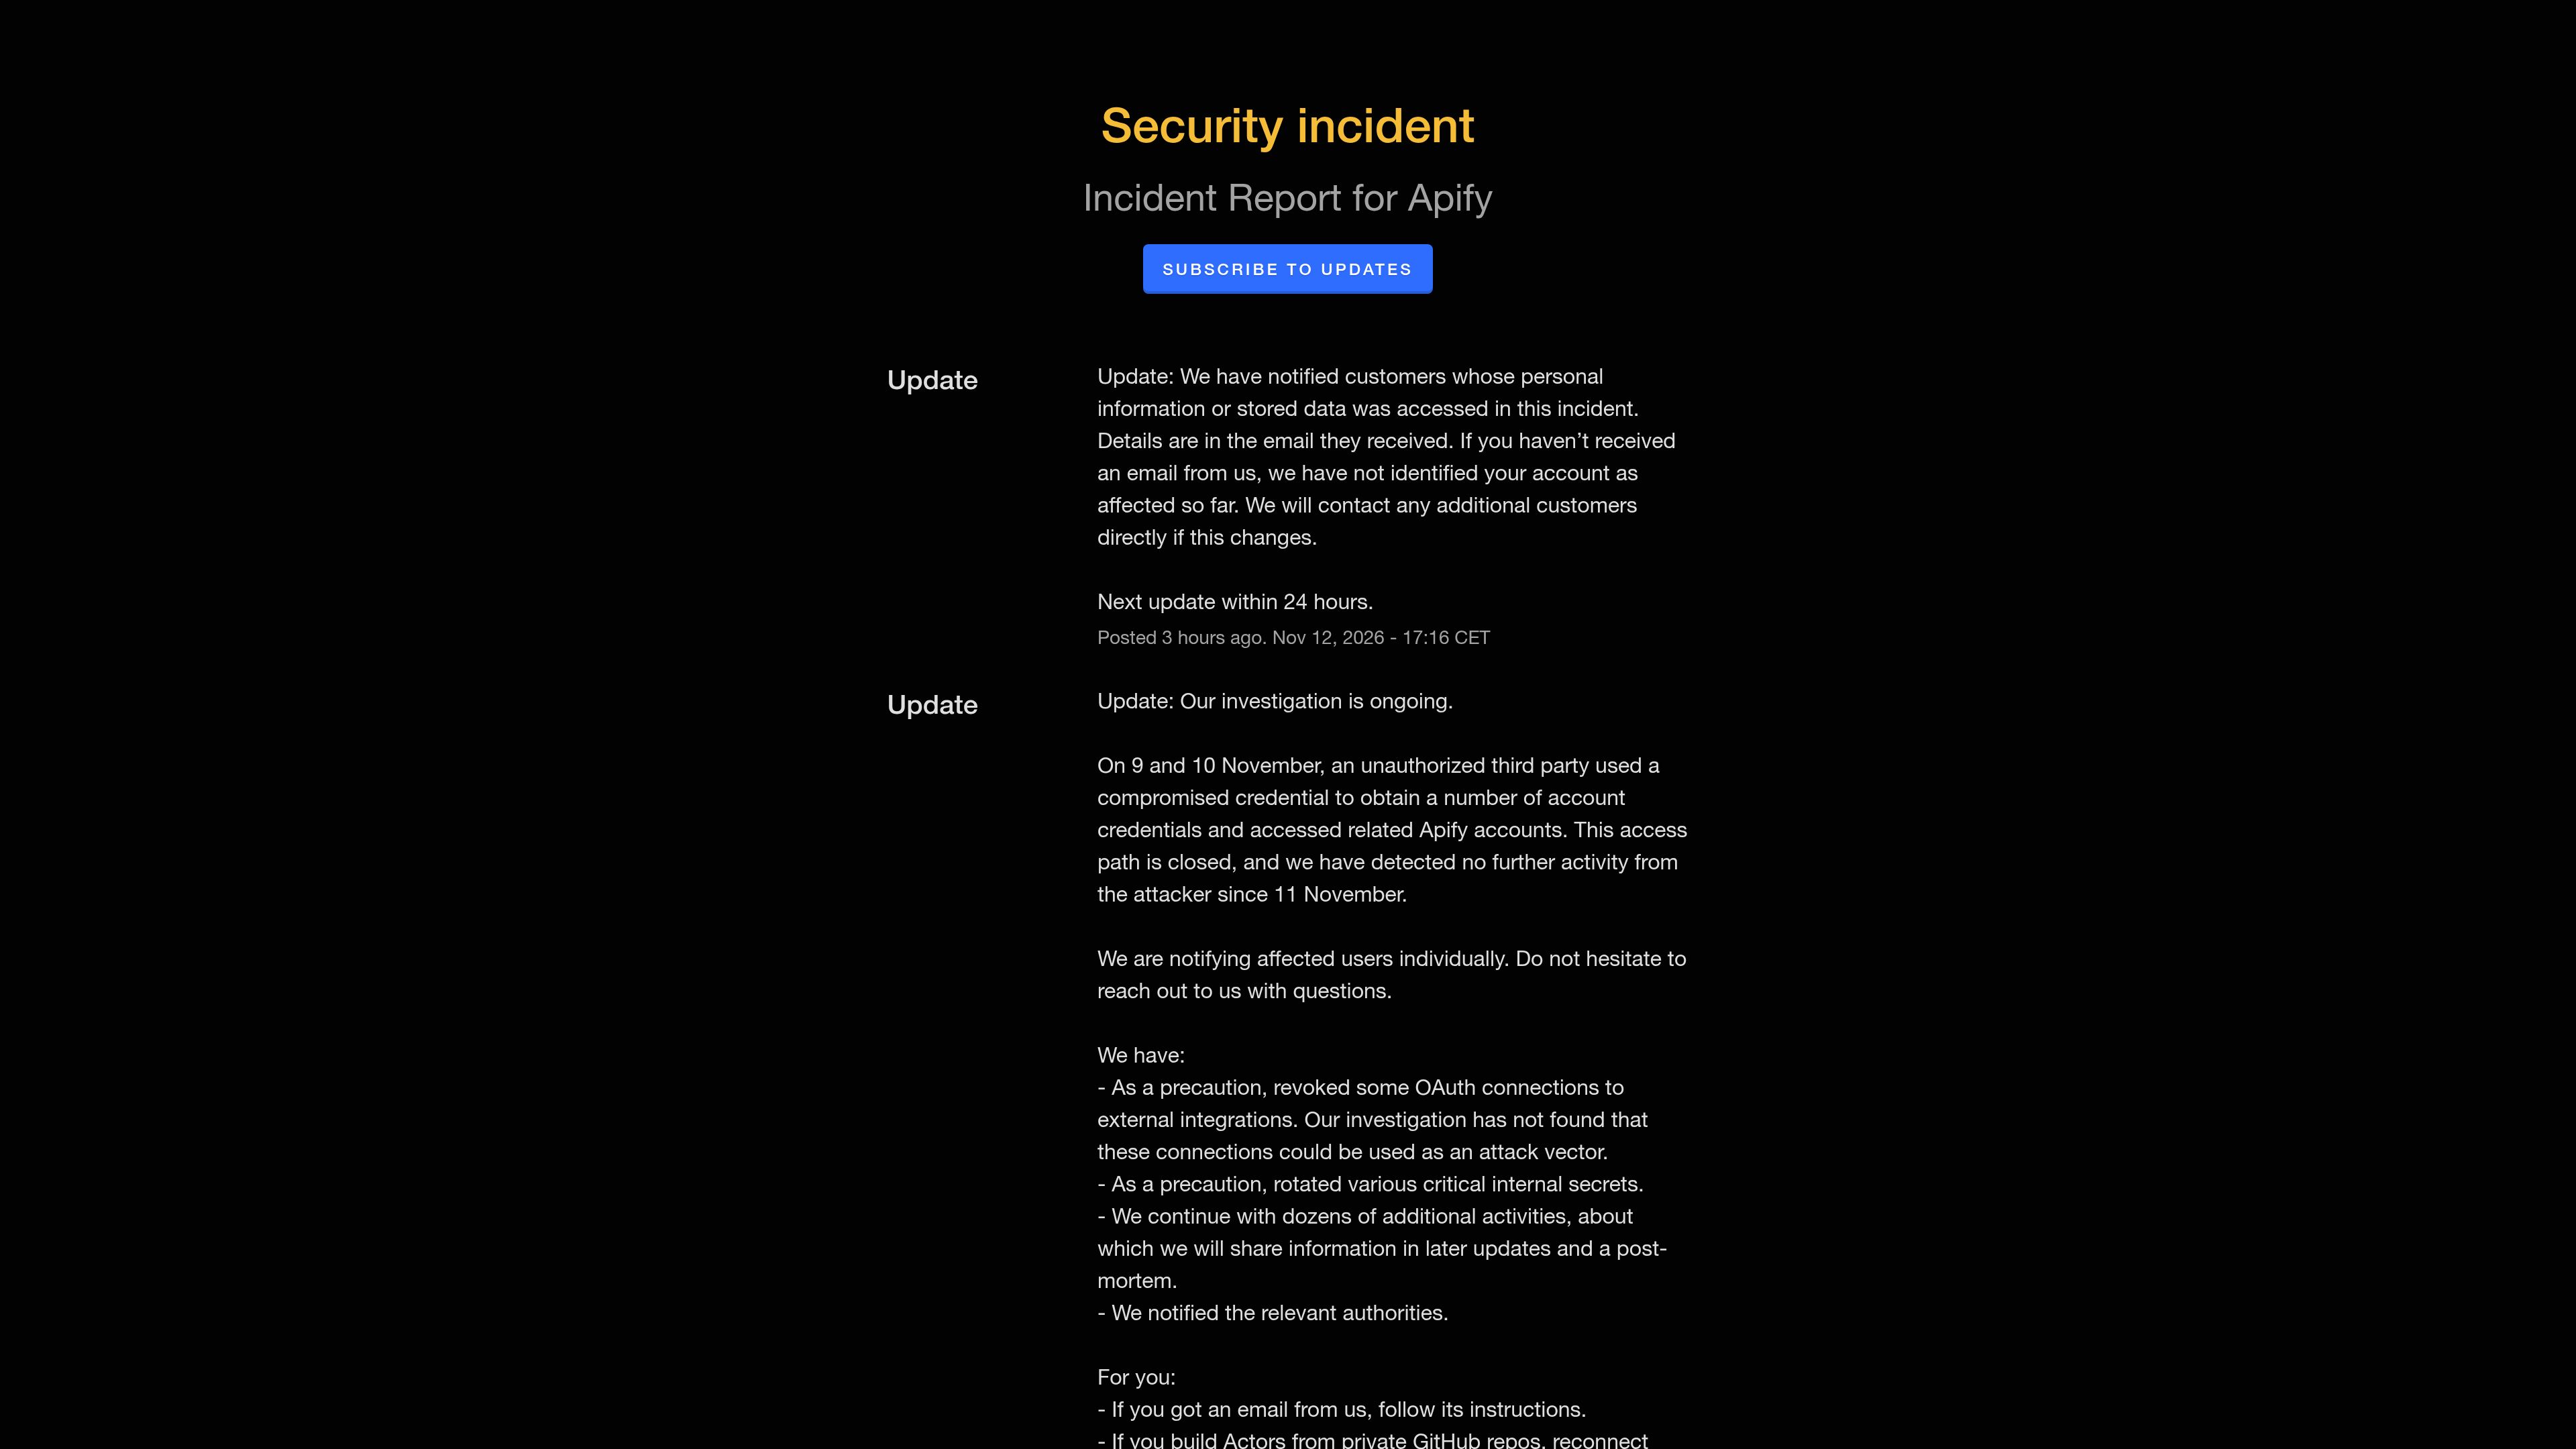
Apify Security Incident(status.apify.com)
8 points by choult | 0 comments
Apify status page incident report on a November 2026 breach where an attacker used a compromised credential to access internal systems and customer accounts.
First screen, captured . Open the video.
Captured . Click for the whole screenshot.
8 points by choult | 0 comments
Apify status page incident report on a November 2026 breach where an attacker used a compromised credential to access internal systems and customer accounts.
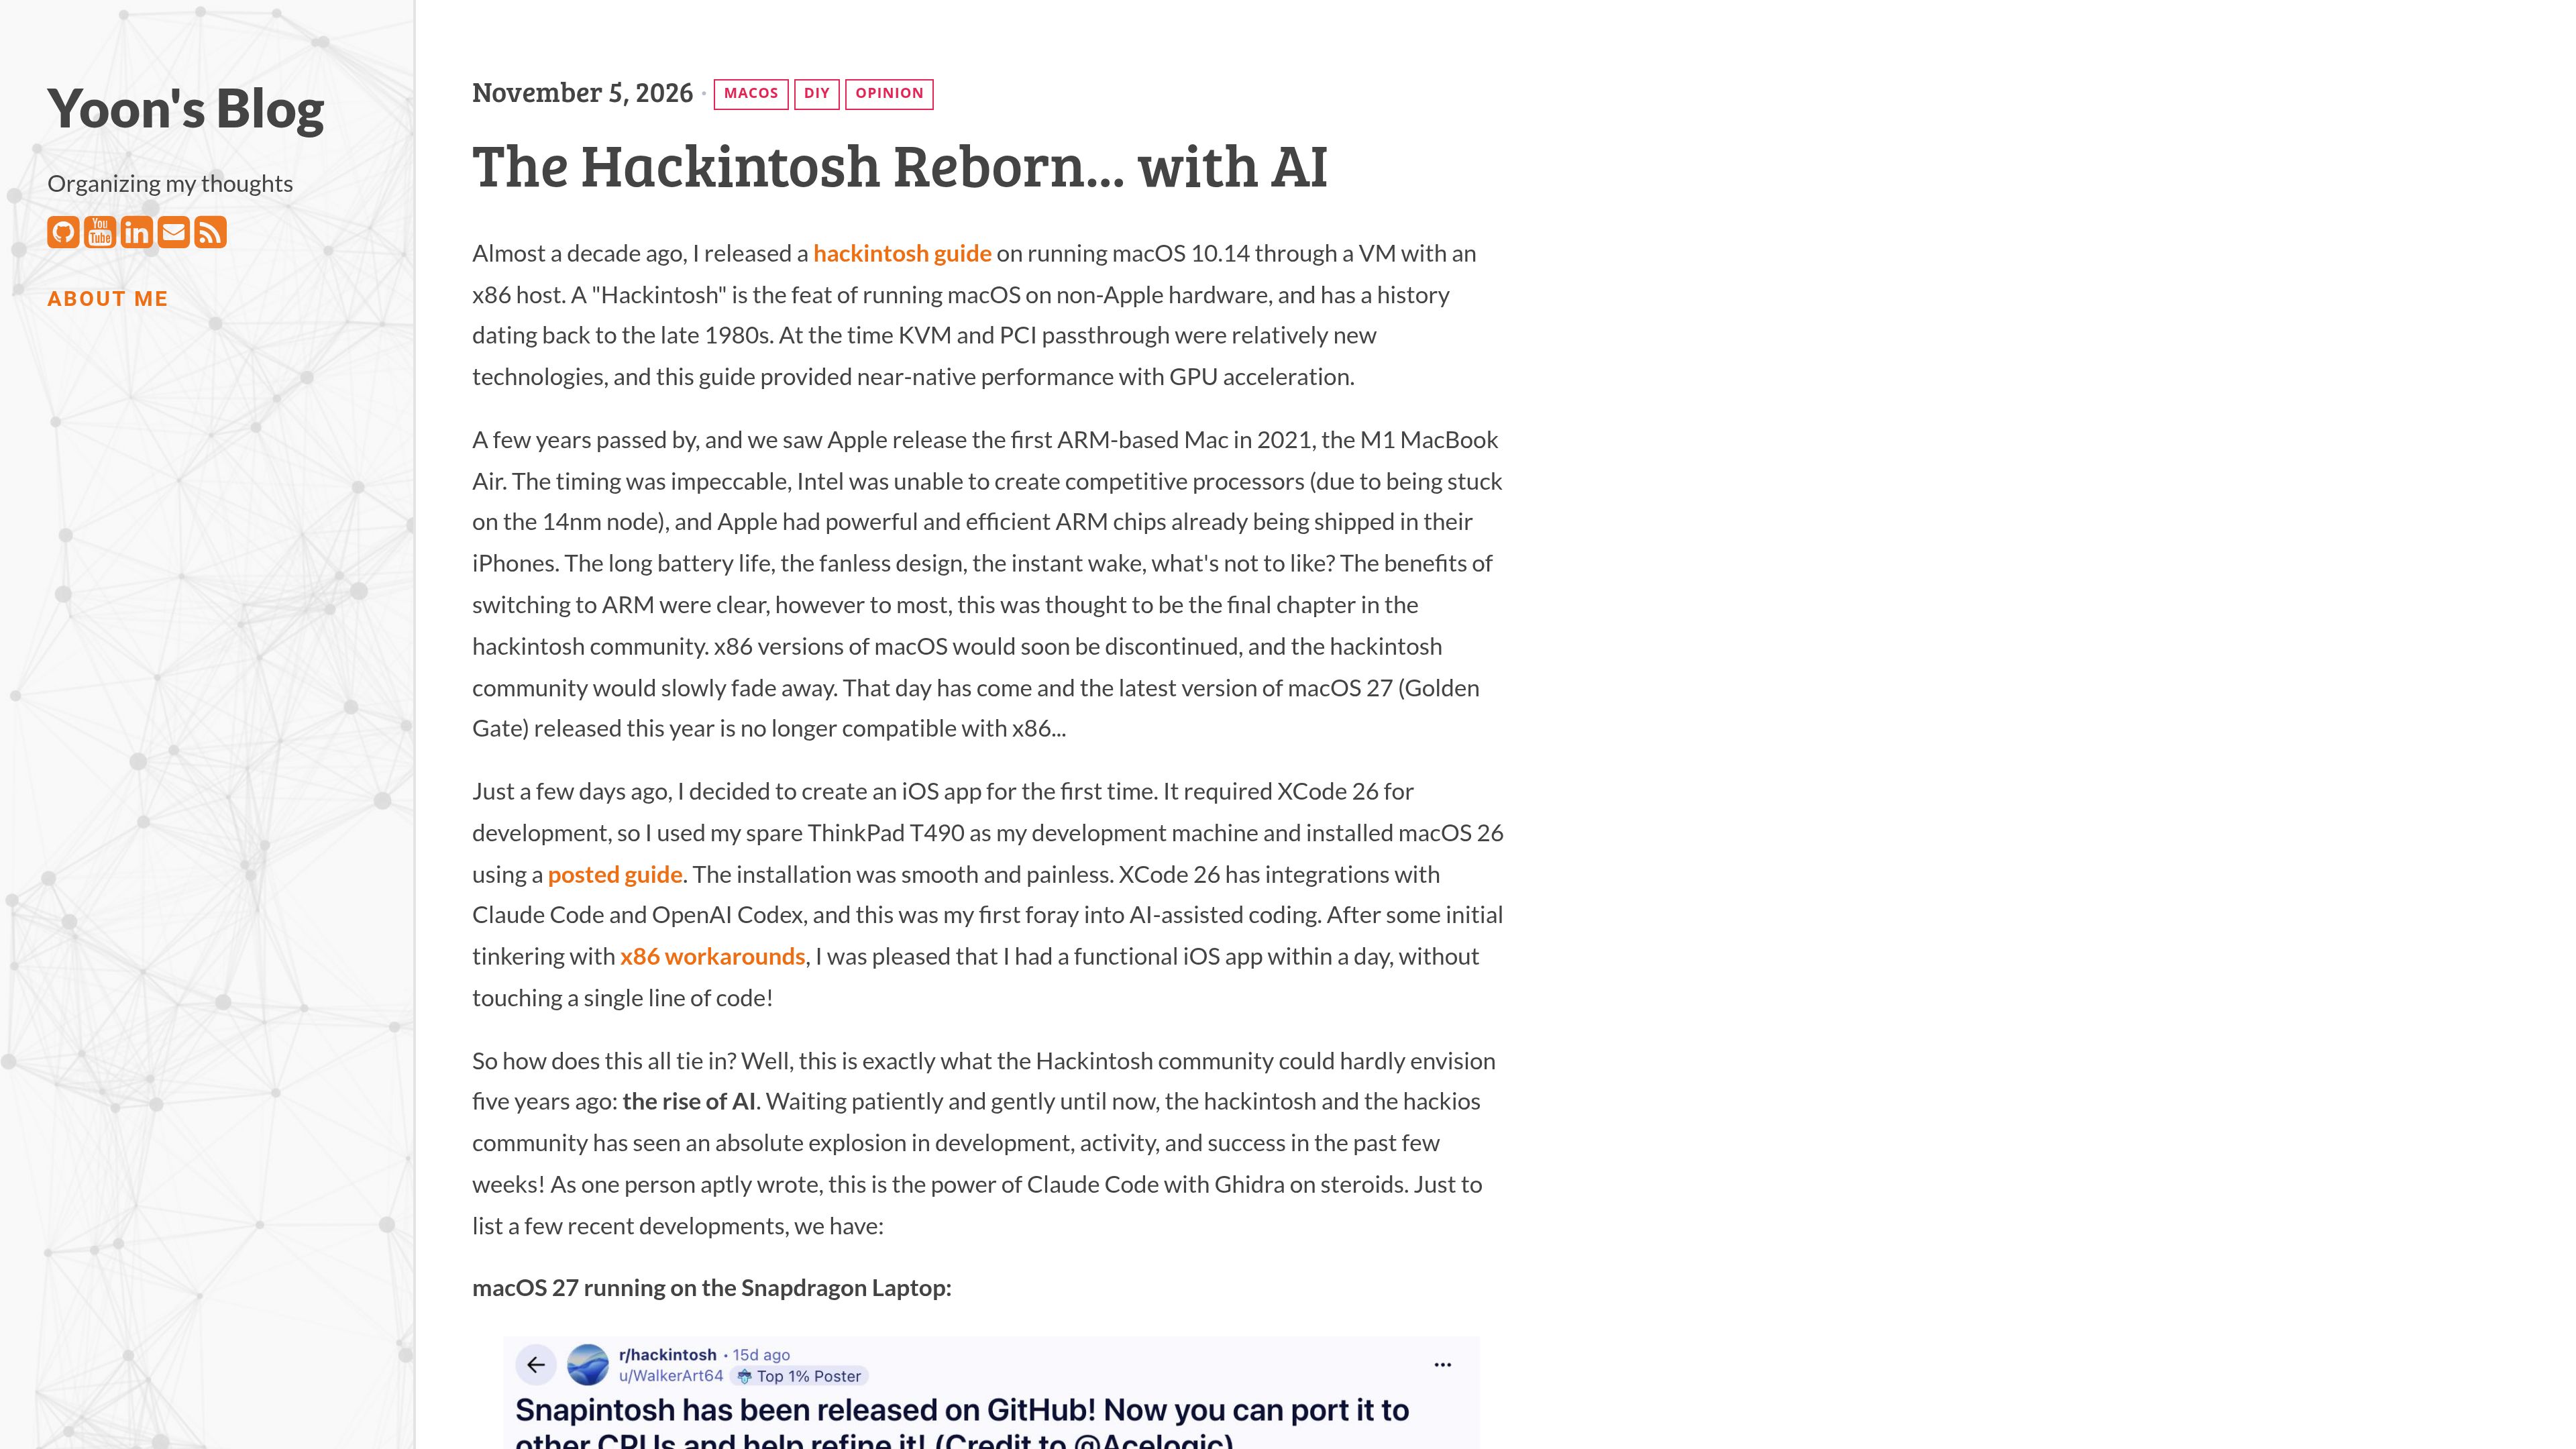
385 points by rubatuga | 223 comments
Blog post arguing AI coding tools like Claude Code are reviving the Hackintosh community, citing macOS ports to Snapdragon, ARM SBCs, and Nvidia GPU support.
90 points by cynicalpeace | 10 comments
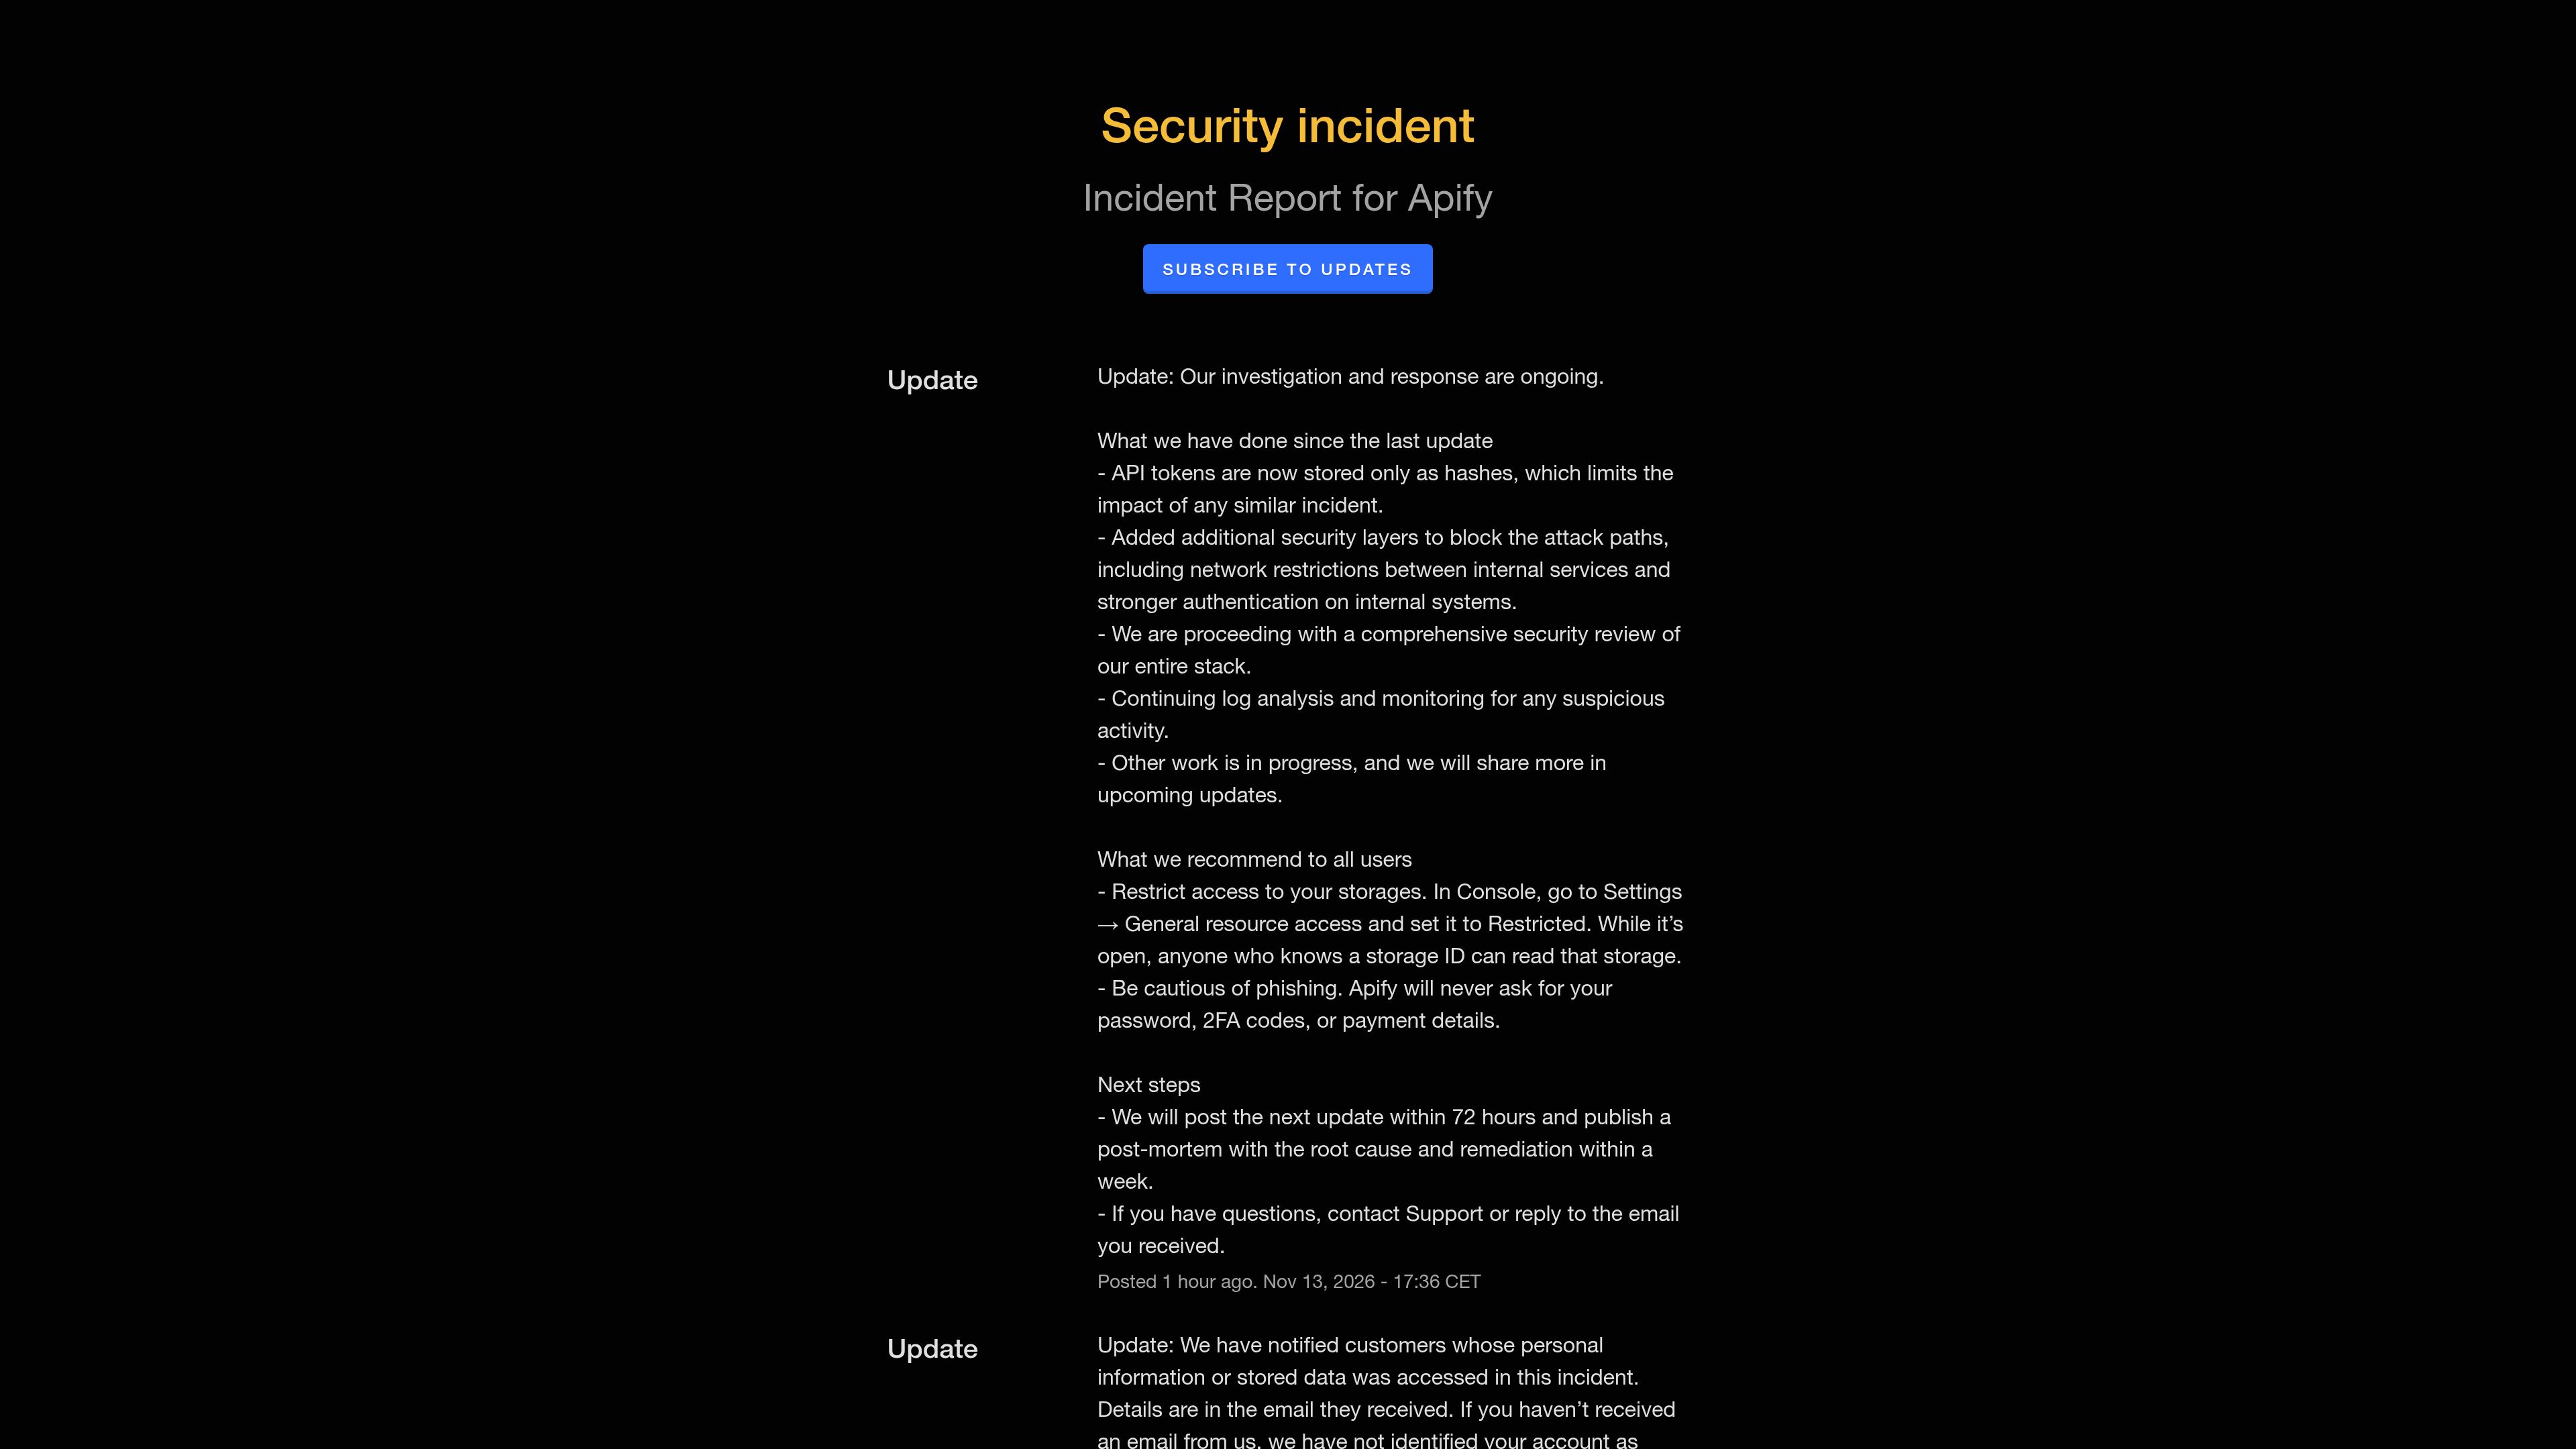
Apify status page incident report describing a November 2026 breach where an attacker used a compromised credential to access internal systems and customer accounts.
32 points by theorchid | 39 comments
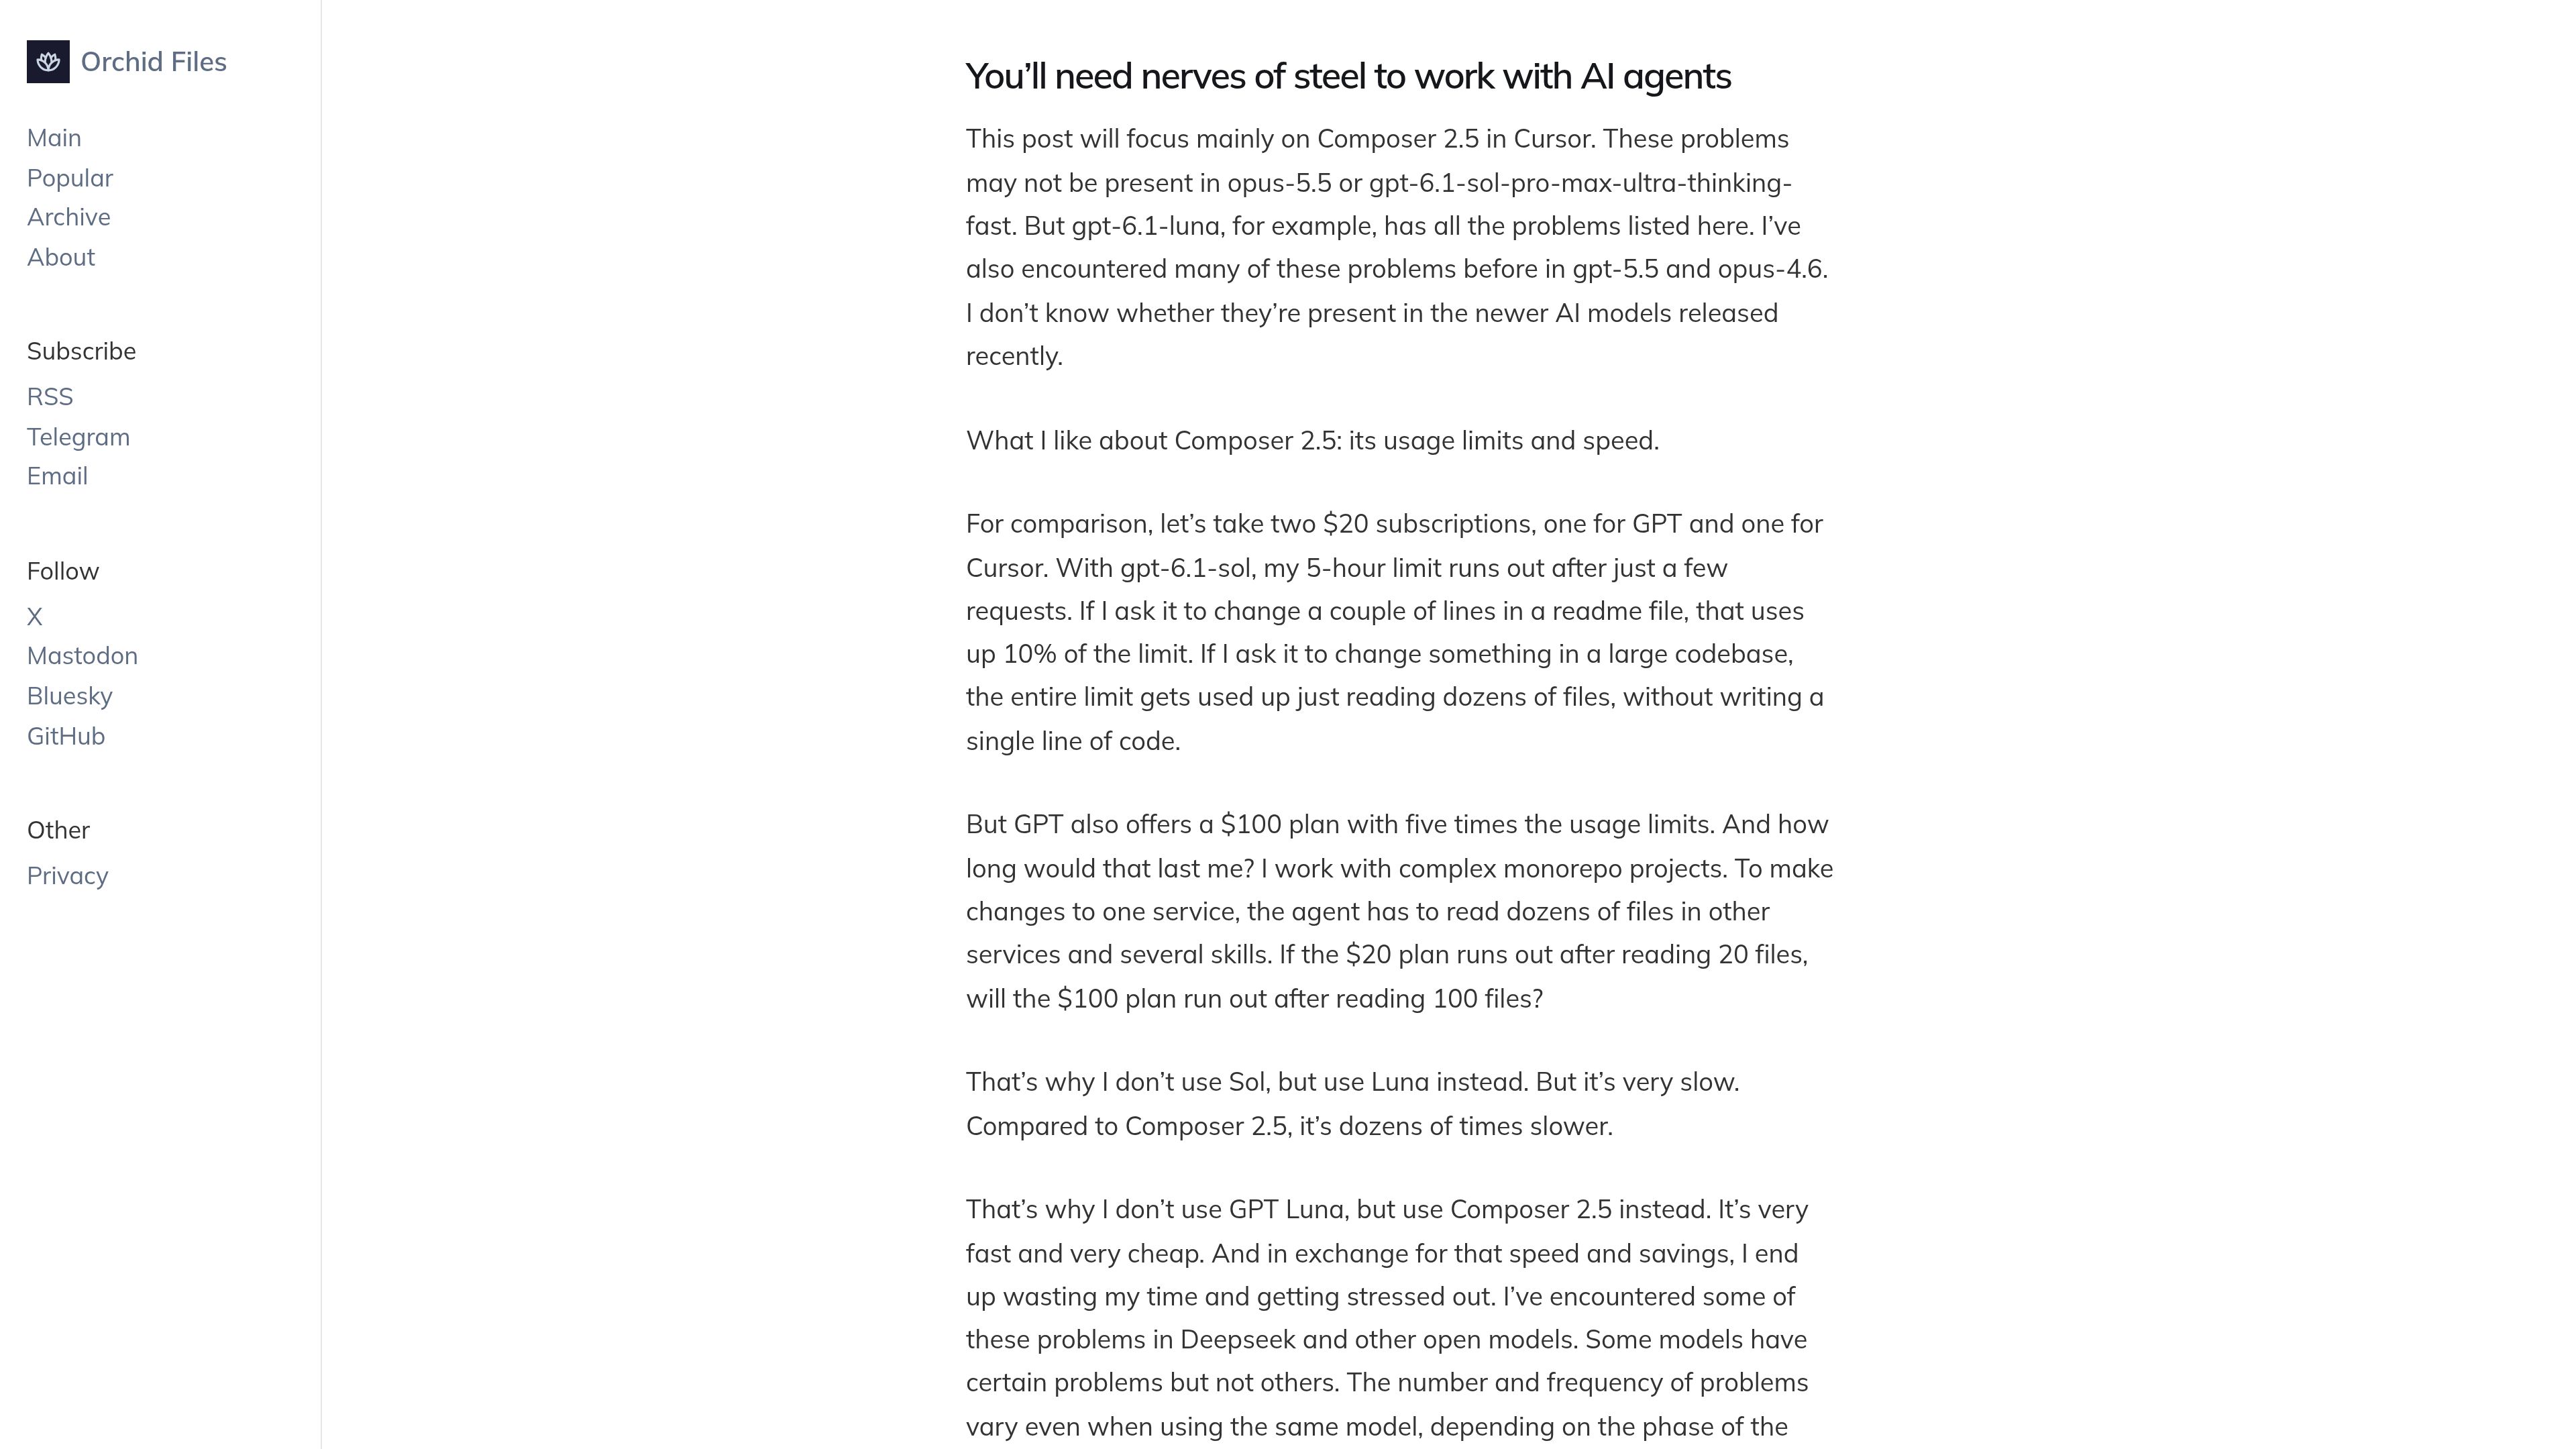
A blog post listing frustrating problems the author encountered using Cursor's Composer 2.5 AI coding agent, such as unwanted deletions, broken tests, and ignored style rules.
162 points by sidcool | 131 comments
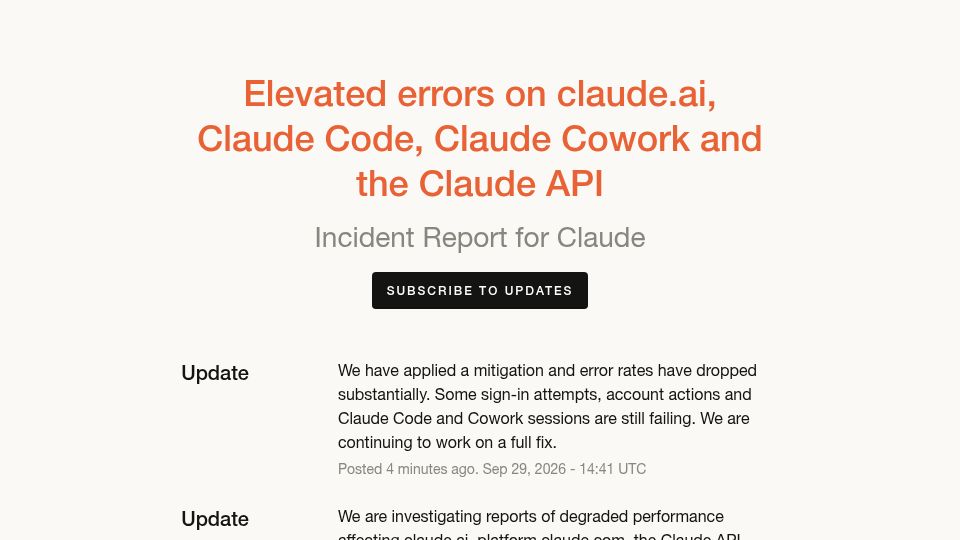
Anthropic status page incident report on elevated errors affecting claude.ai, Claude Code, Claude Cowork and the Claude API, with mitigation updates.
450 points by j12y | 172 comments
Semgrep security research post reporting that PyPI package lightning versions 2.6.2 and 2.6.3 were compromised with Shai-Hulud themed credential-stealing malware.
31 points by soltanov | 9 comments
GitHub repository listing uncensored AI models and models fine-tuned for offensive cybersecurity tasks, with a capability comparison chart.
827 points by takira | 366 comments
PromptArmor threat intelligence report showing Claude Cowork is vulnerable to file exfiltration via indirect prompt injection due to code execution isolation flaws.
456 points by fuck_flock | 147 comments
Nexanet threat intel blog post reporting that Flock Safety hardcoded a password 53 times across its surveillance infrastructure software.
394 points by zdw | 317 comments
CSO Online news analysis reporting that foreign hackers breached the NNSA's Kansas City nuclear weapons plant by exploiting Microsoft SharePoint vulnerabilities.
252 points by sbulaev | 118 comments
An arXiv paper showing AI models can embed encrypted neural network backdoors that provably hide arbitrary capabilities from elicitation-based safety evaluations.