How we rooted Copilot(research.eye.security)
341 points by uponasmile | 136 comments
Eye Security research blog post describing how the team gained root access inside Microsoft Copilot's code execution sandbox.
First screen, captured .
341 points by uponasmile | 136 comments
Eye Security research blog post describing how the team gained root access inside Microsoft Copilot's code execution sandbox.
349 points by skilled | 102 comments
A security researcher's write-up on leaking Microsoft account OAuth tokens through an open redirect vulnerability in the Harvest time-tracking app.
287 points by luispa | 120 comments
A security researcher's blog post describing a Microsoft internal analytics service flaw where unchecked token signatures allowed admin access to query 17.3 trillion records.
669 points by cbg0 | 734 comments
AP News article reporting that the European Union found Microsoft breached antitrust rules by bundling Teams with its Office software.
412 points by miles | 271 comments
CSO Online news article on a Microsoft Authenticator design flaw that overwrites existing MFA accounts when new ones are added, locking users out.
444 points by georgehill | 397 comments
Wired article reporting that Microsoft will make its AI Recall screen-recording feature opt-in and add privacy protections after security criticism.
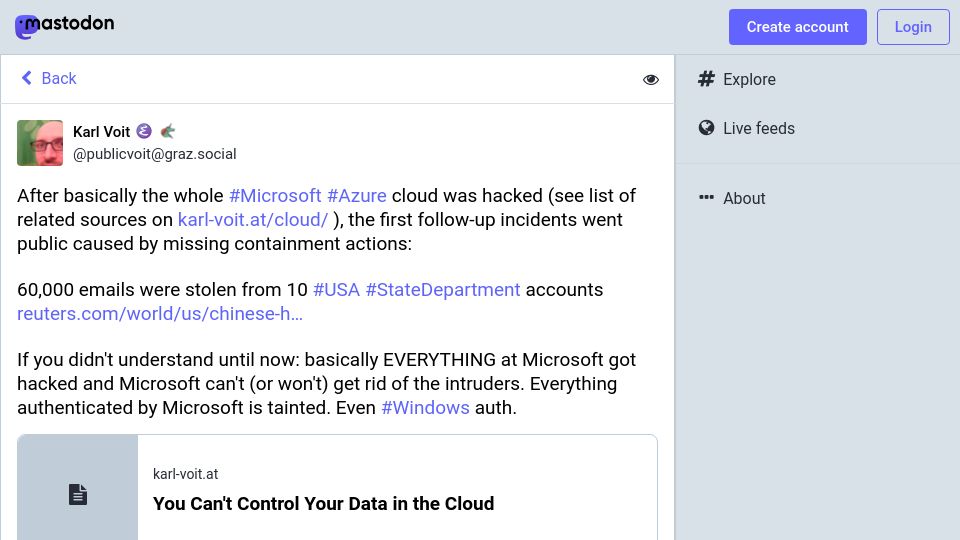
653 points by ColinWright | 277 comments
A Mastodon post by Karl Voit arguing that the Microsoft Azure cloud hack, including 60,000 stolen US State Department emails, means everything Microsoft authenticates is tainted.