First screen, captured .
Looks similar
Related stories
I found a Vulnerability. They found a Lawyer(dixken.de)
831 points by toomuchtodo | 381 comments
Blog post by a diving instructor and platform engineer recounting how reporting a security vulnerability led to a legal response from the affected organization.
There isn't an easy exploit for this PHP vulnerability(eliastaylor.com)
566 points by zkldi | 437 comments
Blog post arguing a newly disclosed PHP vulnerability is hard to exploit and that thousands of LLM-generated GitHub PoC exploits don't work against vanilla PHP.
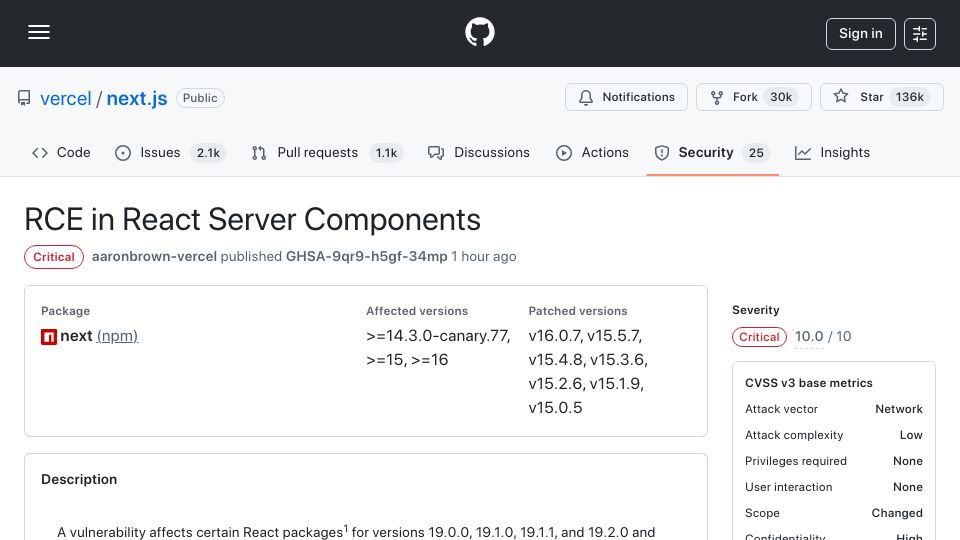
RCE Vulnerability in React and Next.js(github.com)
559 points by rayhaanj | 214 comments
GitHub security advisory GHSA-9qr9-h5gf-34mp for a critical (CVSS 10.0) remote code execution vulnerability in React Server Components affecting Next.js, with patched versions listed.
TODOs aren't for doing(sophiebits.com)
380 points by todsacerdoti | 218 comments
A blog post by Sophie Alpert arguing that TODO comments are valuable as documentation of known issues even if never acted on, and shouldn't be auto-deleted or tracked.
A Vulnerability in Libsodium(00f.net)
323 points by raggi | 47 comments
Blog post by Frank Denis, libsodium's author, describing a vulnerability found in the libsodium cryptographic library.
Open Source is one person(opensourcesecurity.io)
325 points by LawnGnome | 132 comments
Blog post by Josh Bressers on Open Source Security arguing that many open source projects are maintained by a single person.