Leaving Neovim for Zed(stevedylan.dev)
289 points by mxstbr | 252 comments
First screen, captured .
289 points by mxstbr | 252 comments
85 points by skaplich | 114 comments
289 points by speckx | 156 comments
323 points by jandeboevrie | 130 comments
A TIL blog post explaining how to recognize base64-encoded JSON, certificates, and private keys by their characteristic leading characters.
416 points by gasull | 200 comments
A personal blog essay arguing that end-to-end encrypting private data and communications has become an ethical duty, using a glass-walls analogy.
355 points by wonger_ | 106 comments
A myNoise blog post by founder Stéphane describing a hacker's attack on the myNoise website, first via code-injection attempts and then a different strategy.
637 points by __rito__ | 261 comments
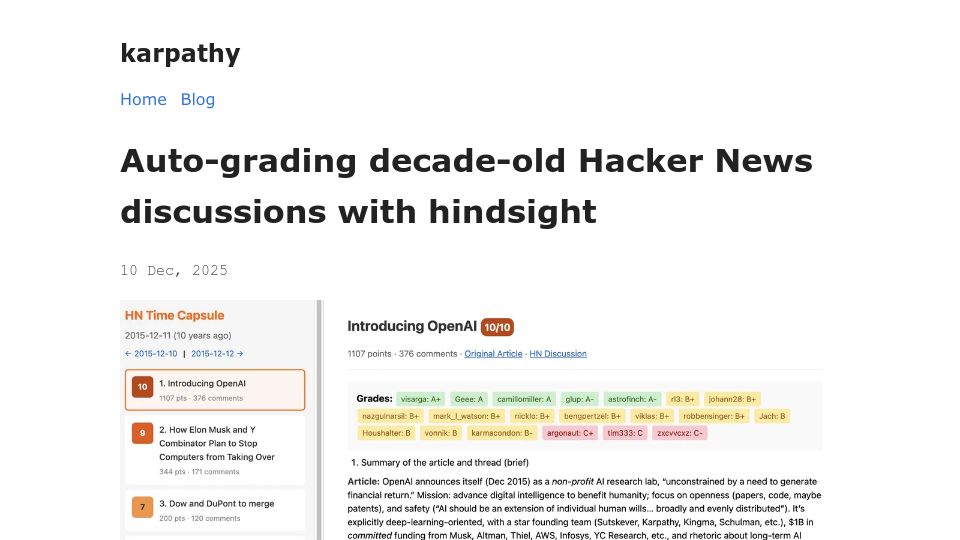
Andrej Karpathy blog post about using LLMs to grade decade-old Hacker News discussions and commenters' predictions with hindsight, presented as an "HN Time Capsule" site.
433 points by LelouBil | 171 comments
KrebsOnSecurity article reporting that a CISA contractor kept a public GitHub repository exposing privileged AWS GovCloud credentials and internal CISA system details.
344 points by vinhnx | 95 comments
Astral blog post by William Woodruff describing the techniques Astral uses to secure its open source tools and their build, test, and release processes against supply chain attacks.