Firewall rules as stopgap mitigation
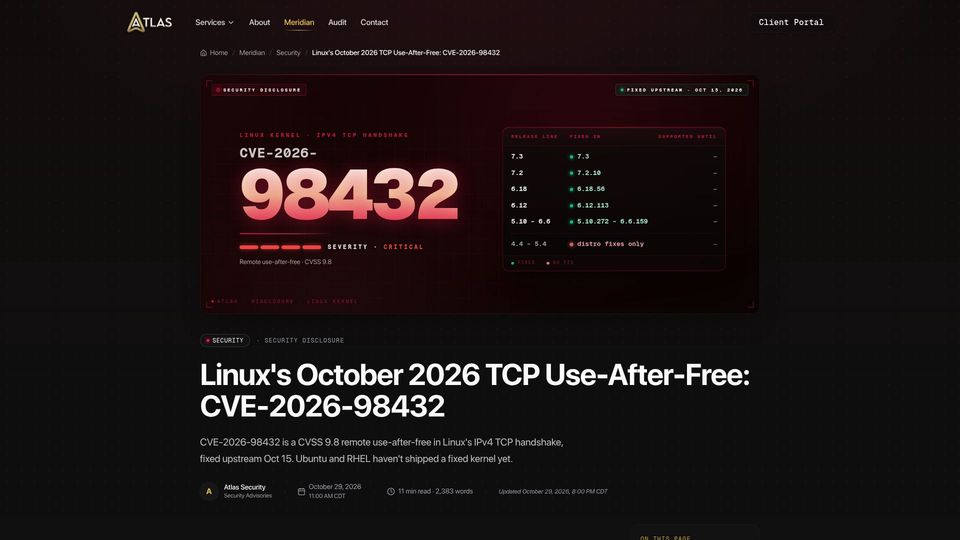
Several commenters say dropping IPv4 TCP packets with IP options in raw PREROUTING blunts the bug, though Red Hat says this only reduces exposure and eBPF, namespaces and containers can bypass netfilter.
Ubuntu's delay breaks trust
Many see the slow response as a reason to move servers to Debian or other distros, and users relying on automatic updates feel let down.
Risk is overblown
Some argue the bug is a narrow race that is hard to exploit and no in-the-wild attacks have been seen. Others counter with working PoCs against their own servers and the case for attack chaining.