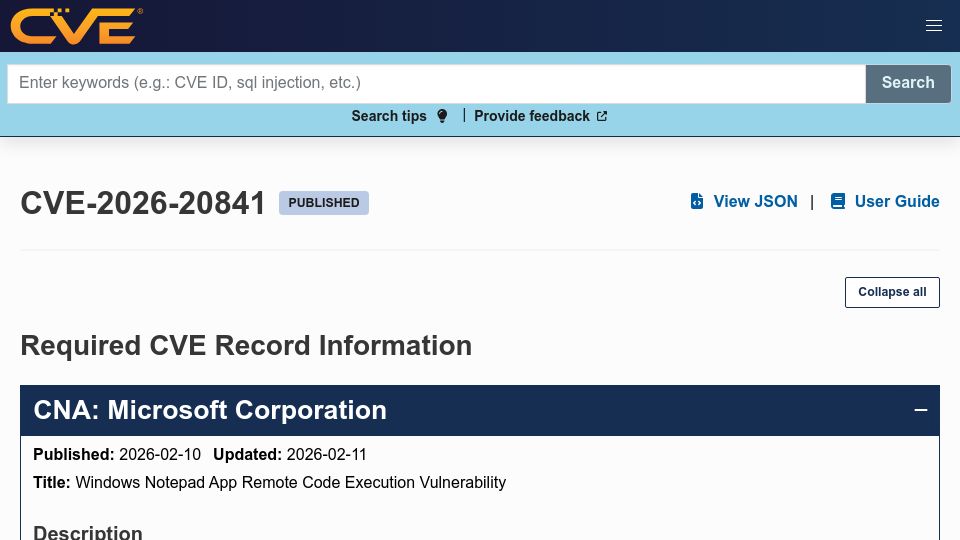
Windows Notepad App Remote Code Execution Vulnerability(cve.org)
737 points by riffraff | 450 comments
CVE record CVE-2026-20841 published by Microsoft describing a remote code execution vulnerability in the Windows Notepad app.
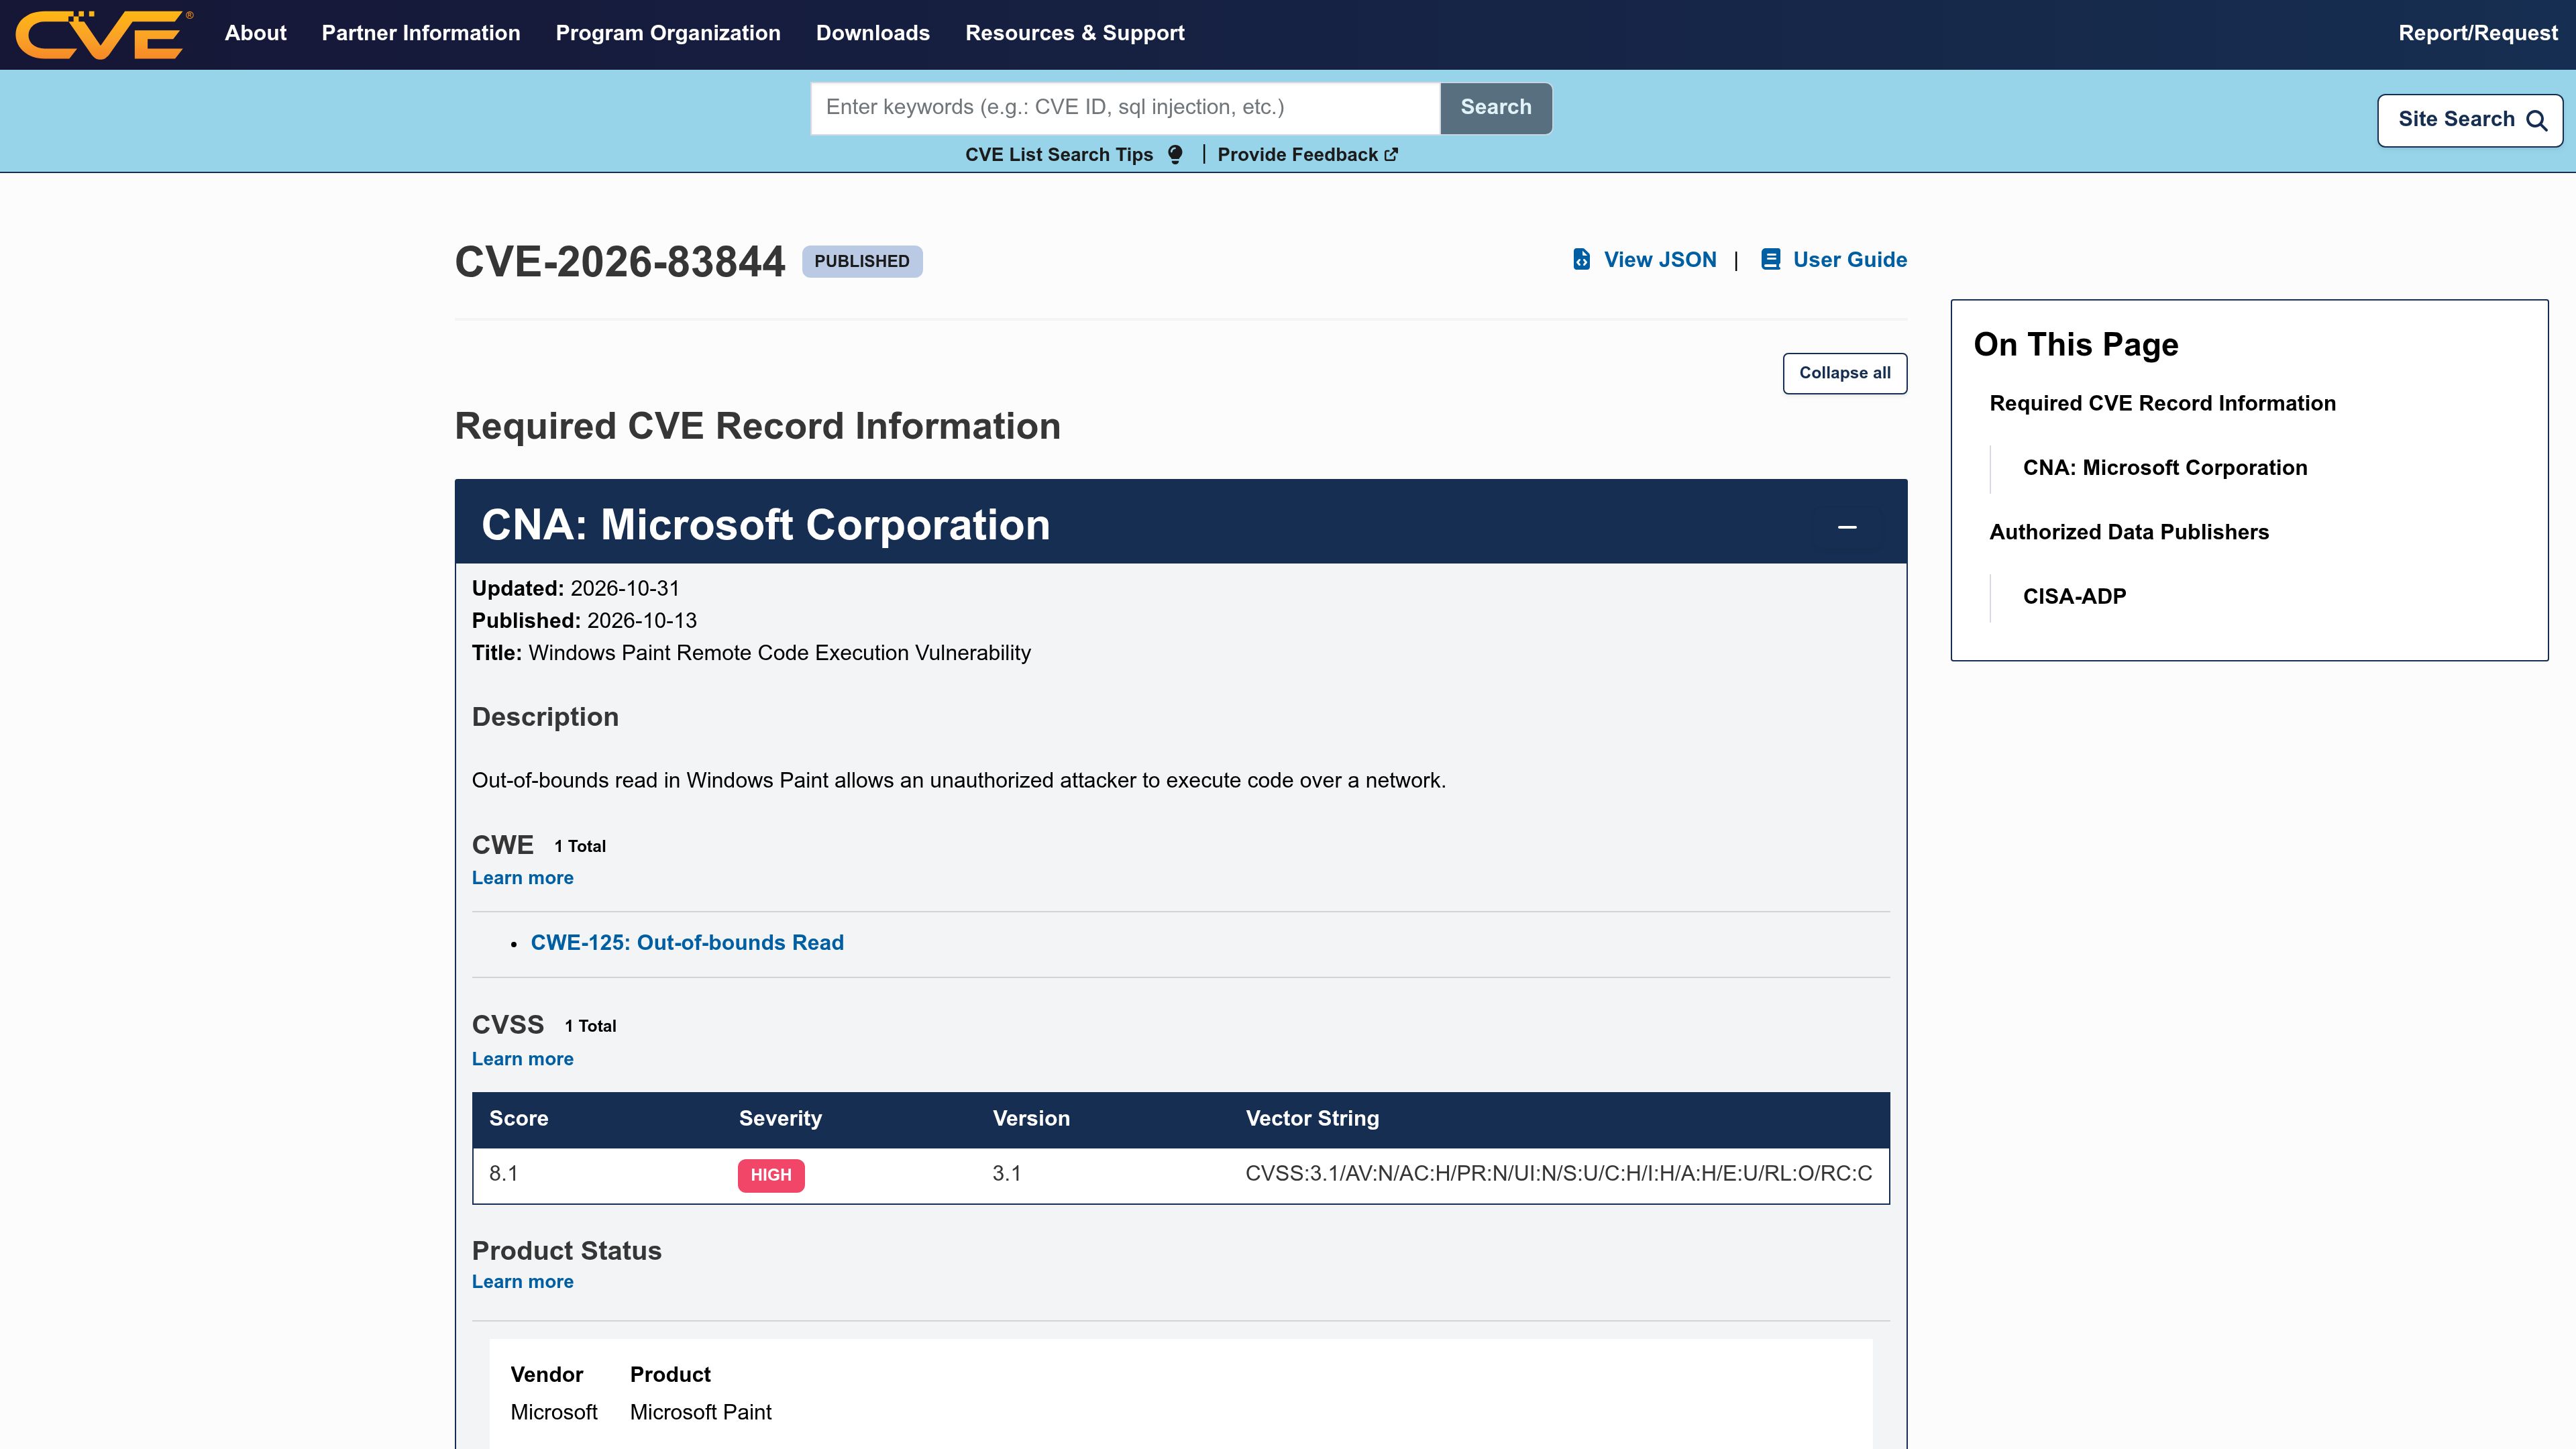
First screen, captured . Open the video.
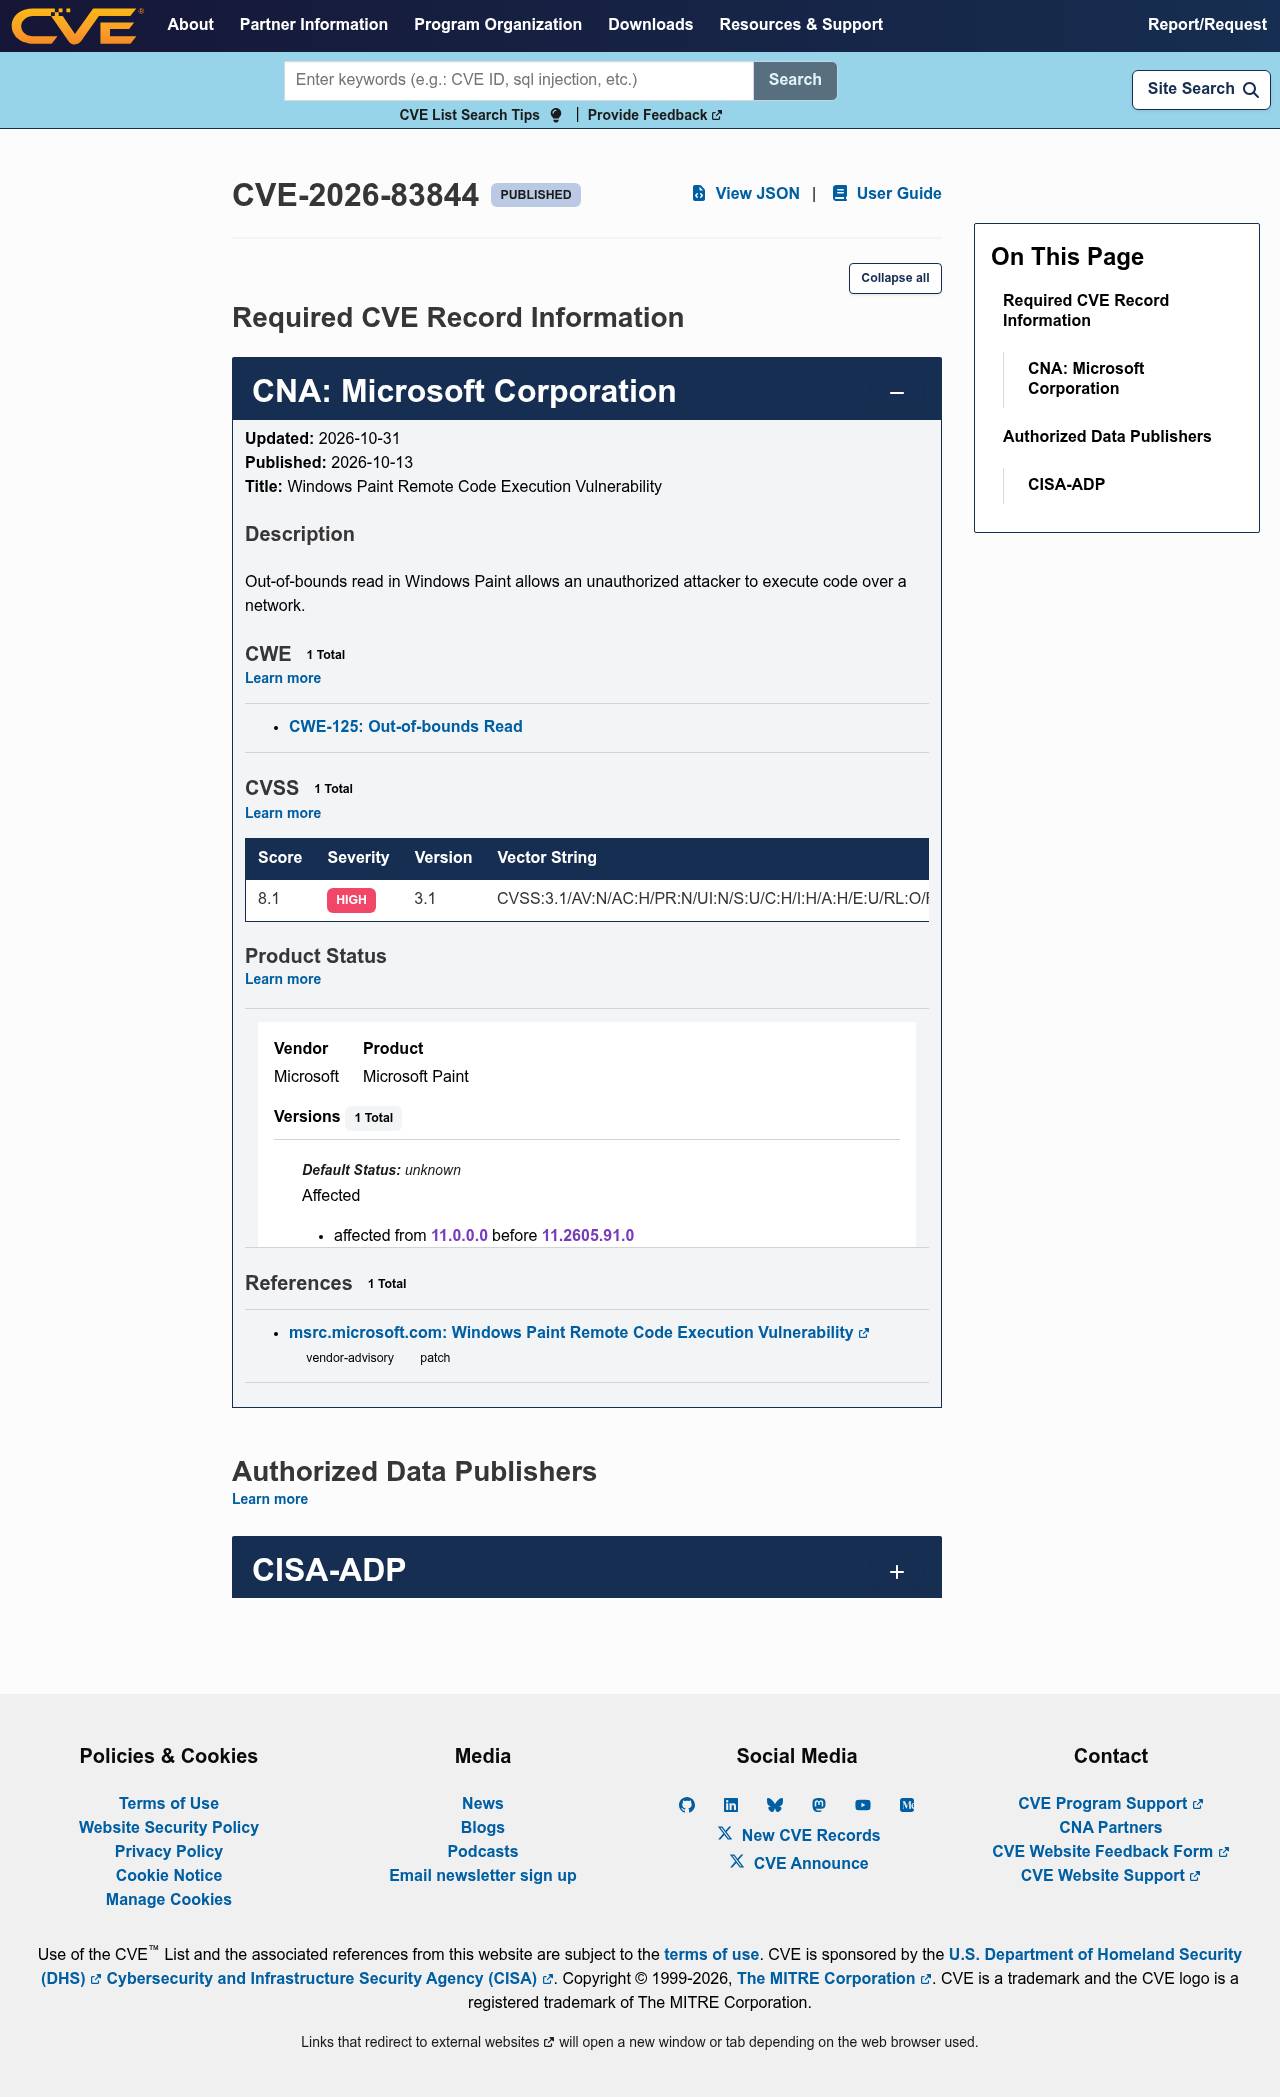
Captured . Click for the whole screenshot.
737 points by riffraff | 450 comments
CVE record CVE-2026-20841 published by Microsoft describing a remote code execution vulnerability in the Windows Notepad app.
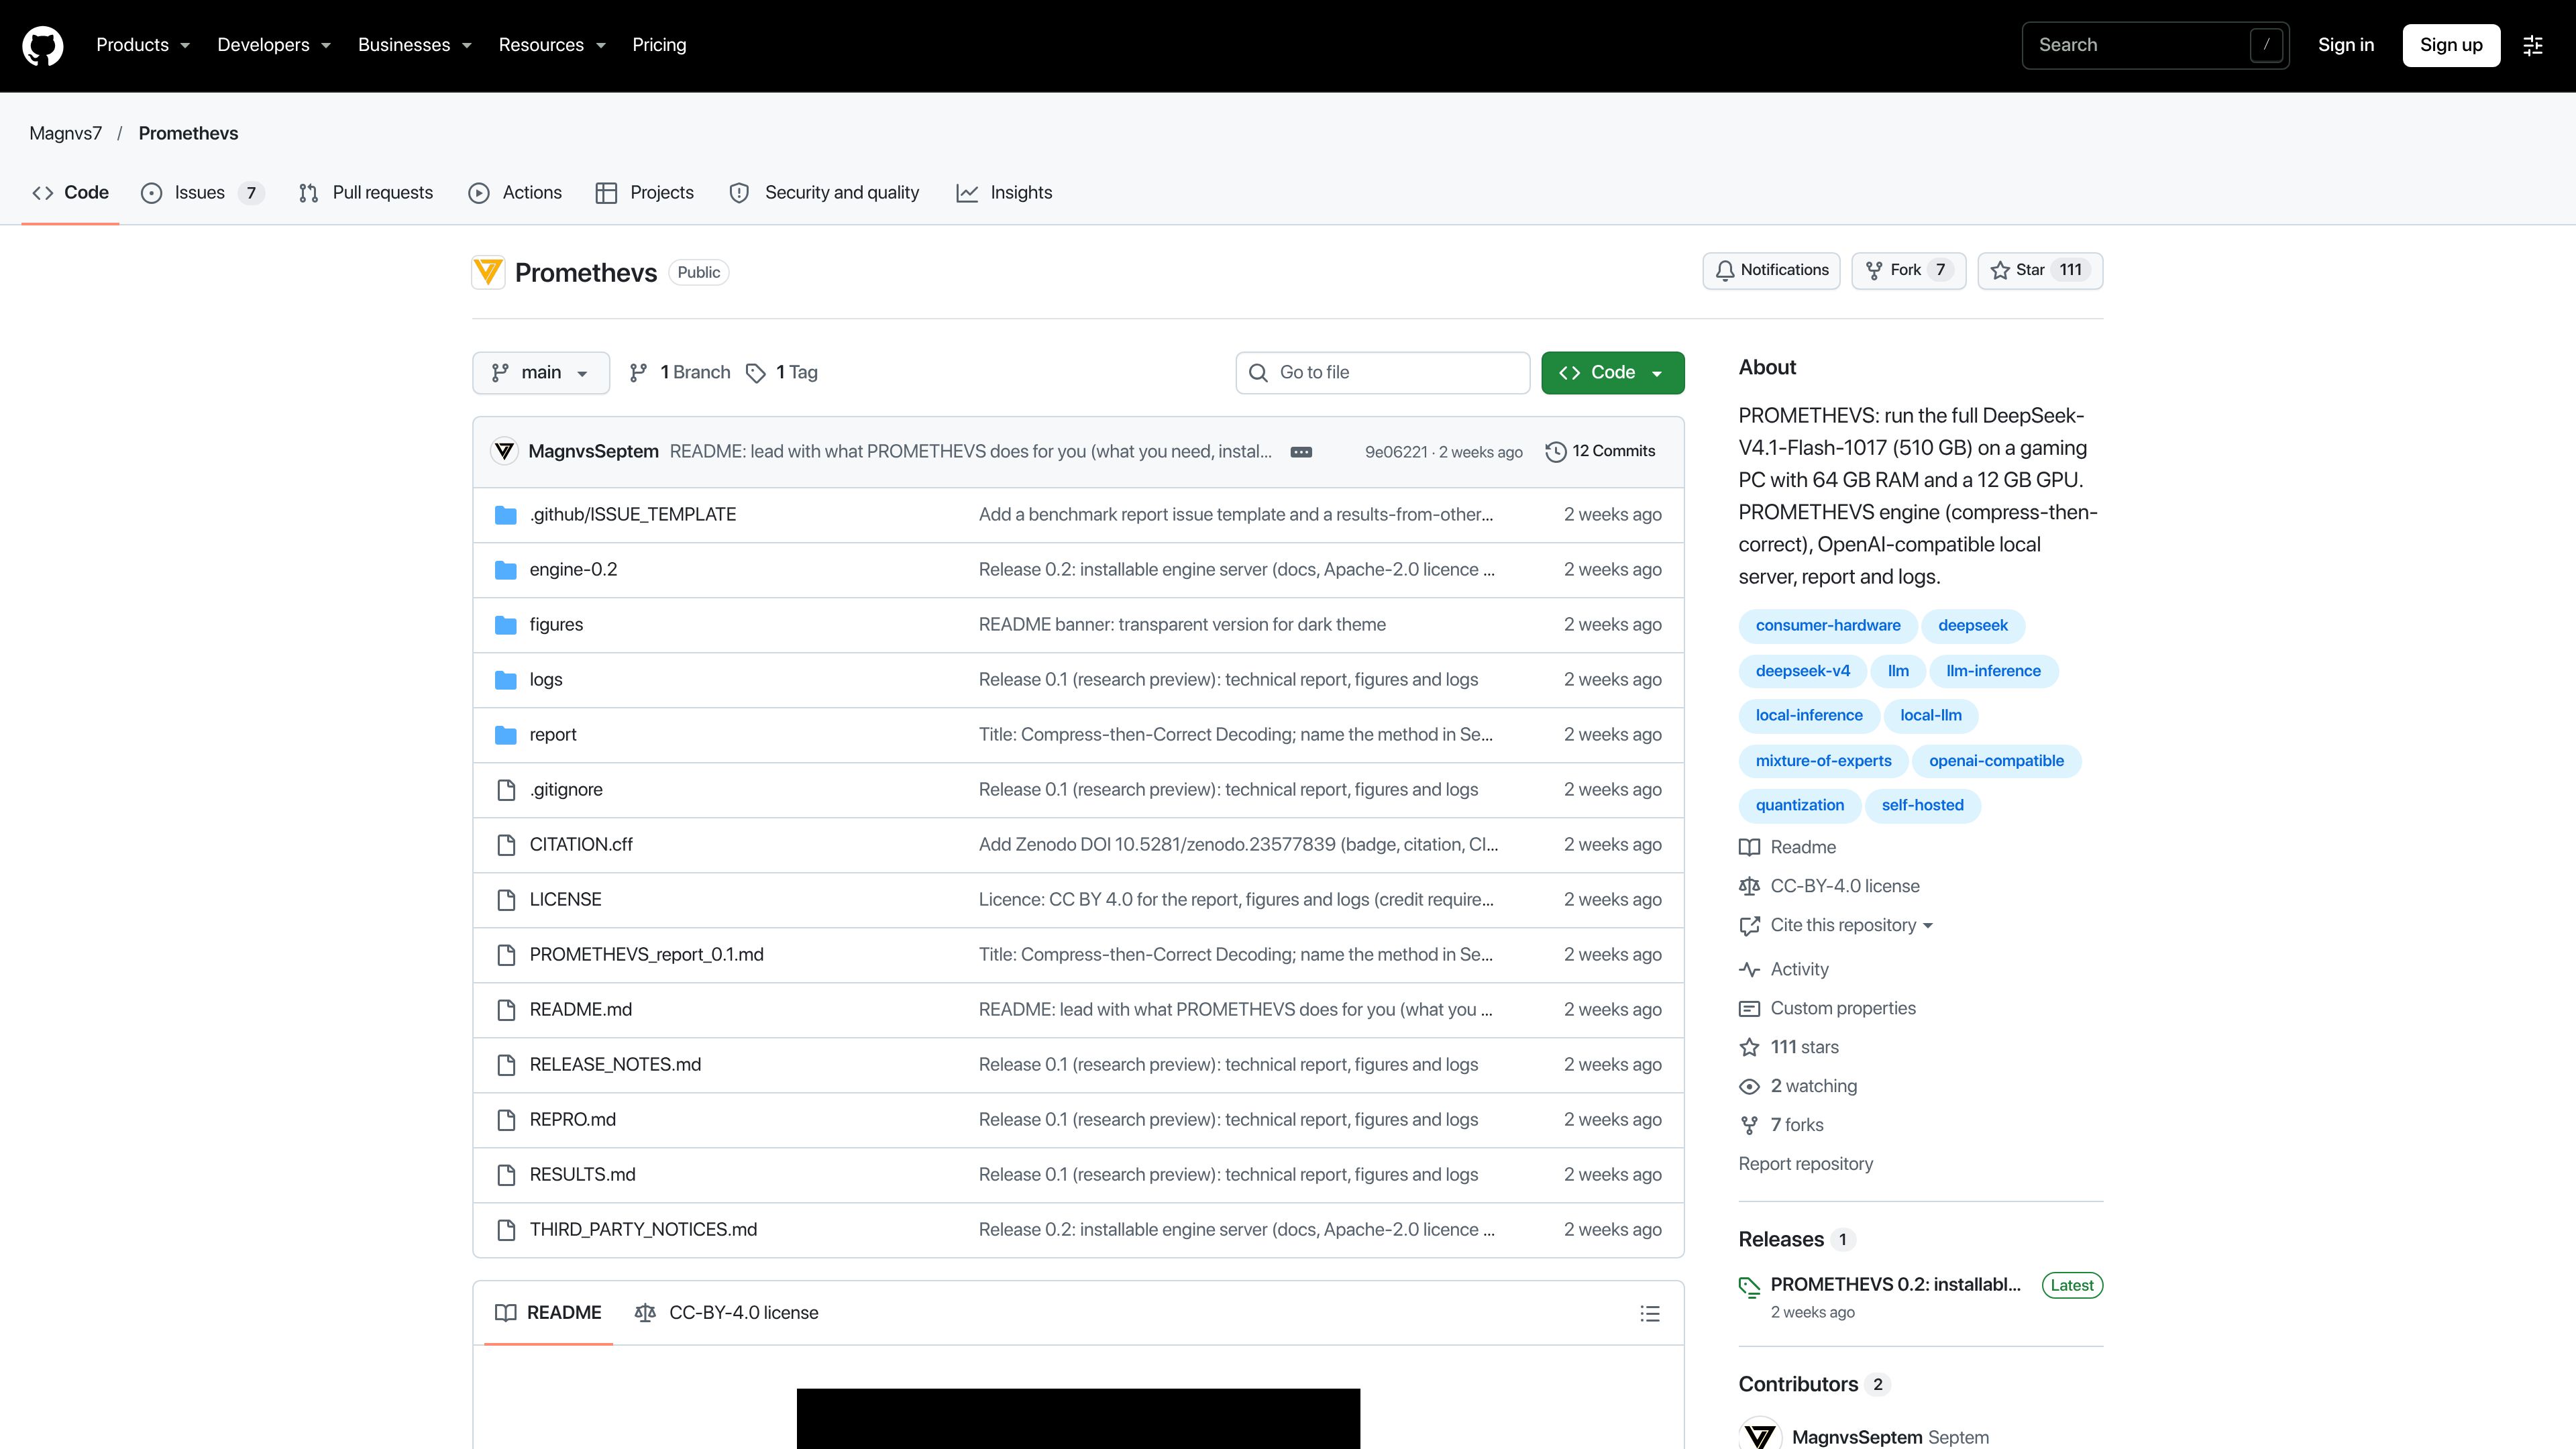
4 points by ar-nelson | 0 comments
GitHub repository for PROMETHEVS, an engine that runs the full 510 GB DeepSeek-V4.1-Flash model on a PC with 64 GB RAM and a 12 GB GPU using compress-then-correct decoding.
4 points by EGreg | 0 comments
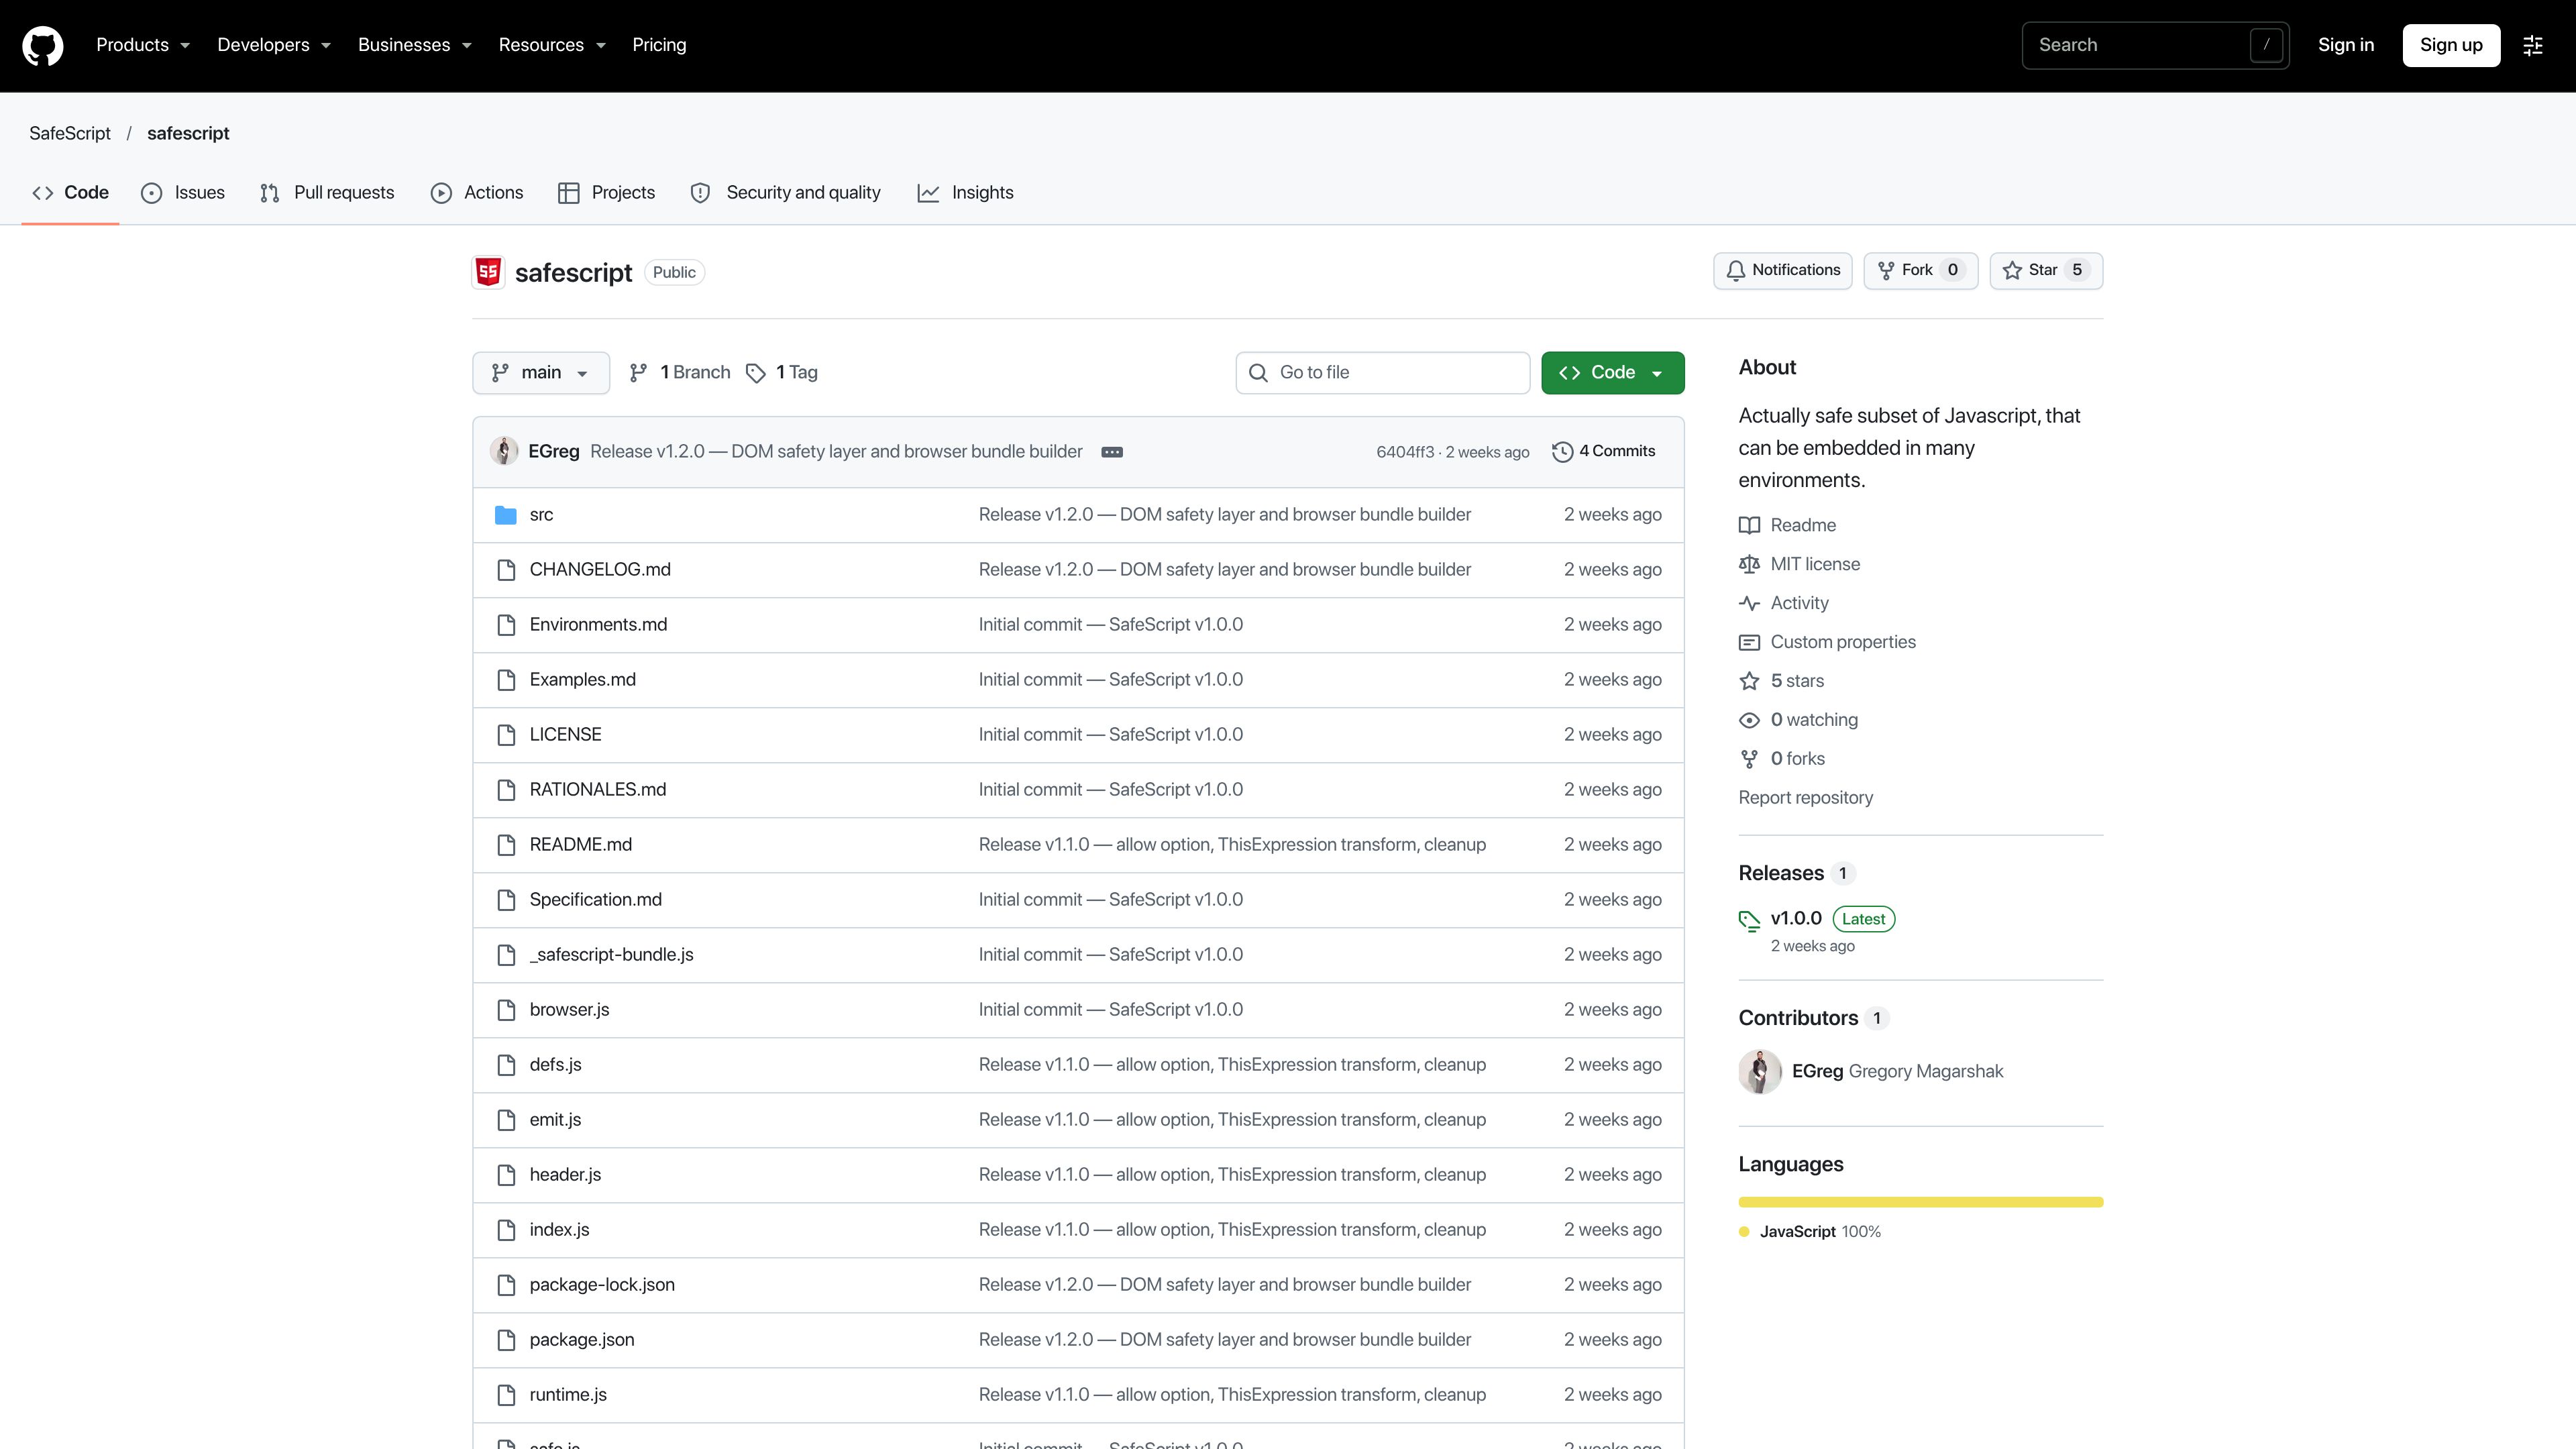
GitHub repository for SafeScript, a safe subset of JavaScript that compiles to JS and PHP for sandboxed execution of untrusted code.
145 points by CoderLuii | 131 comments
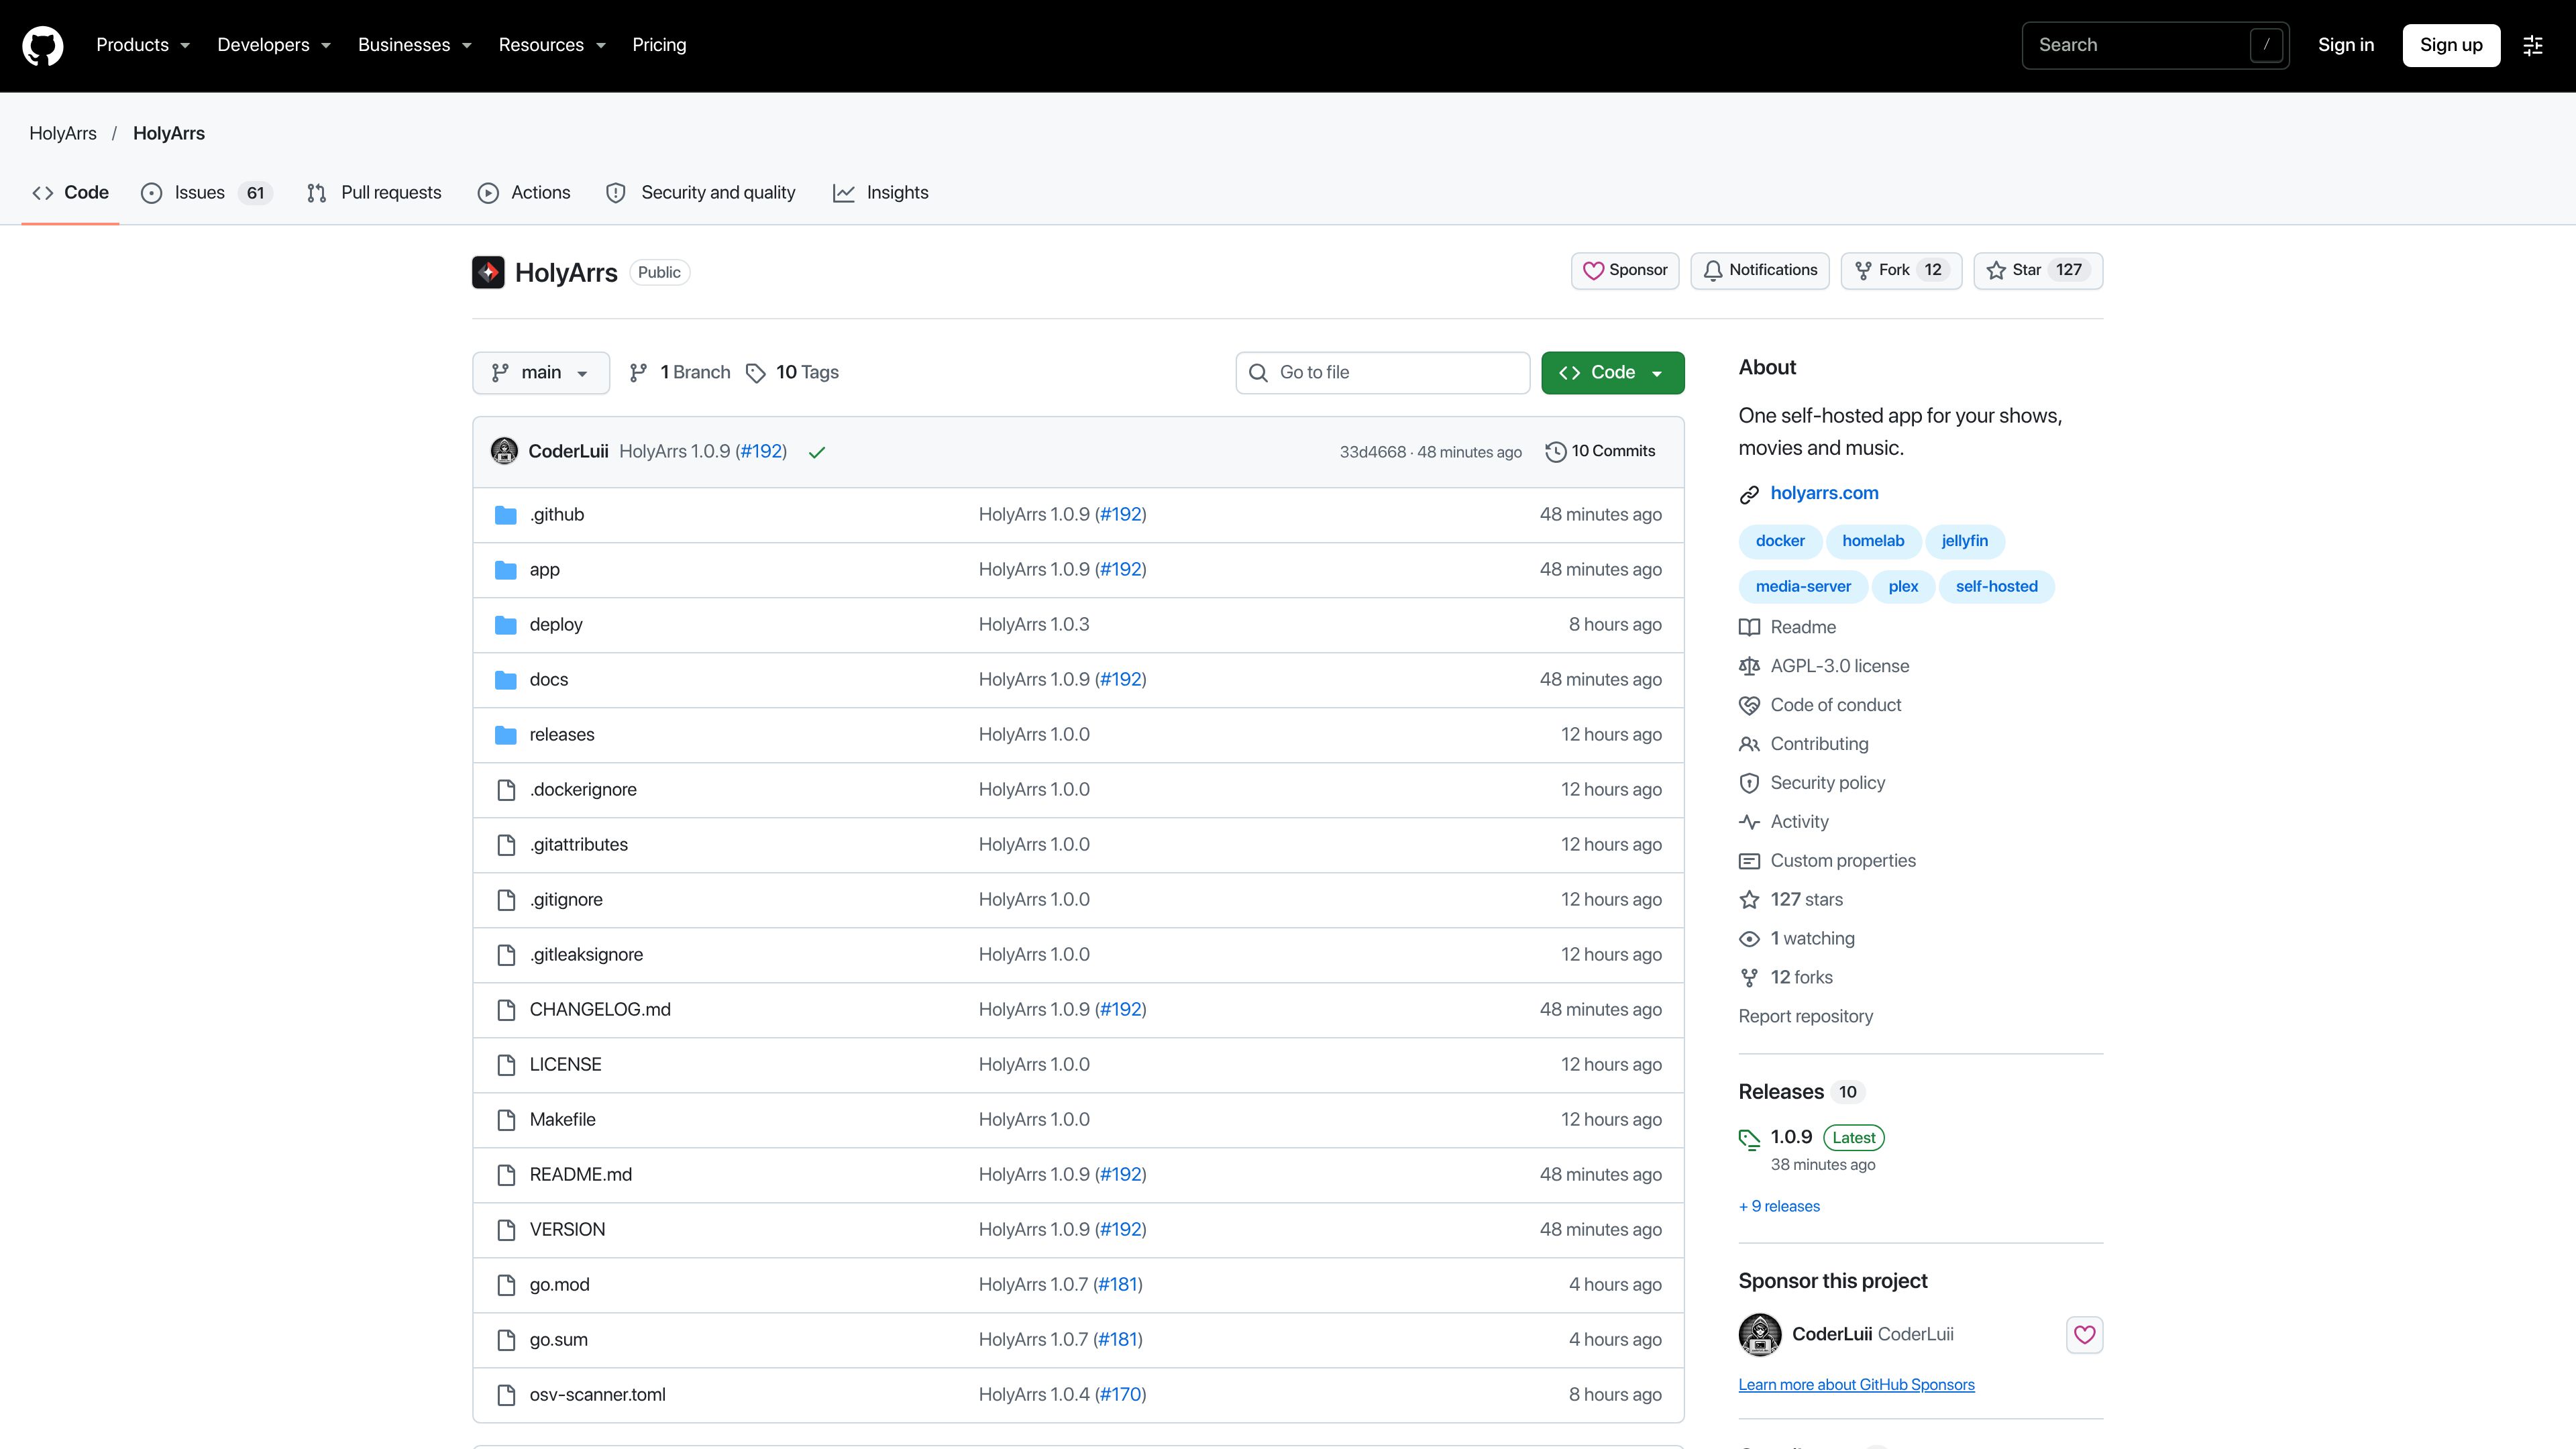
GitHub repository for HolyArrs, an AGPL-licensed self-hosted Go app that manages and streams your shows, movies, music and downloads in one place.
15 points by christ_dev | 2 comments
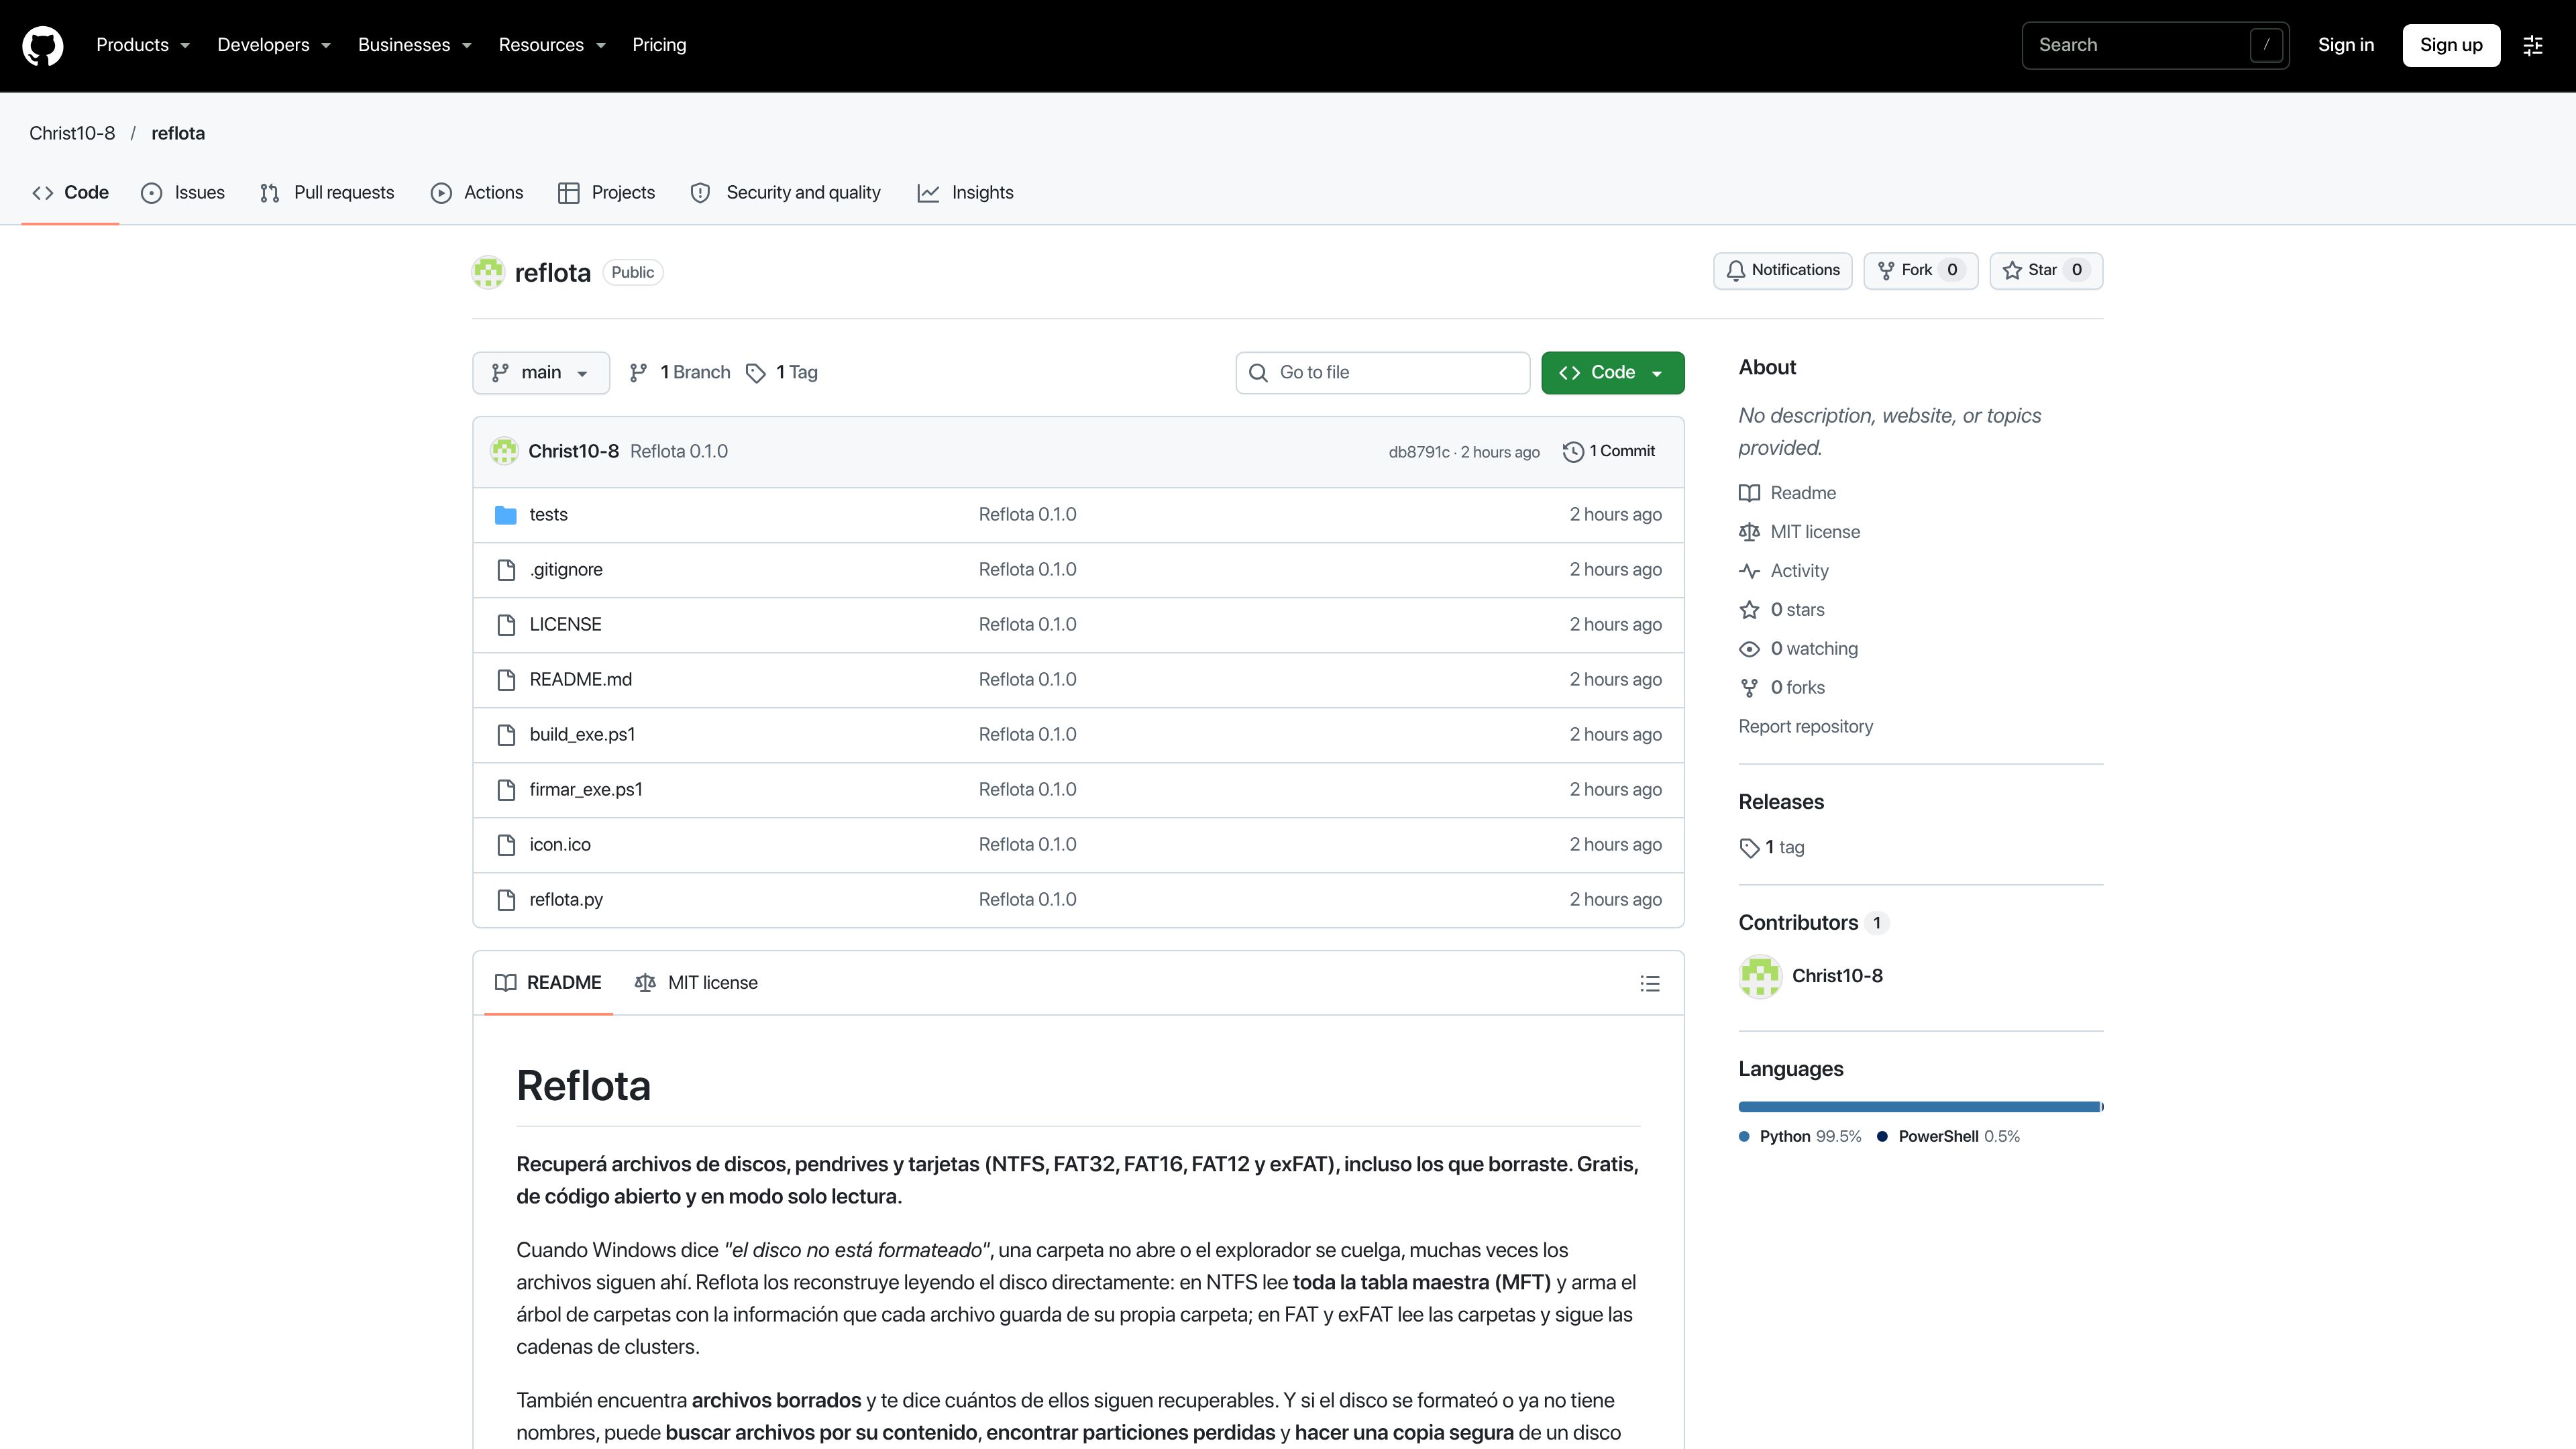
GitHub repository for Reflota, an open-source, read-only Windows tool for recovering deleted and lost files from NTFS, FAT and exFAT disks, with phased disk imaging.
113 points by colejohnson66 | 94 comments
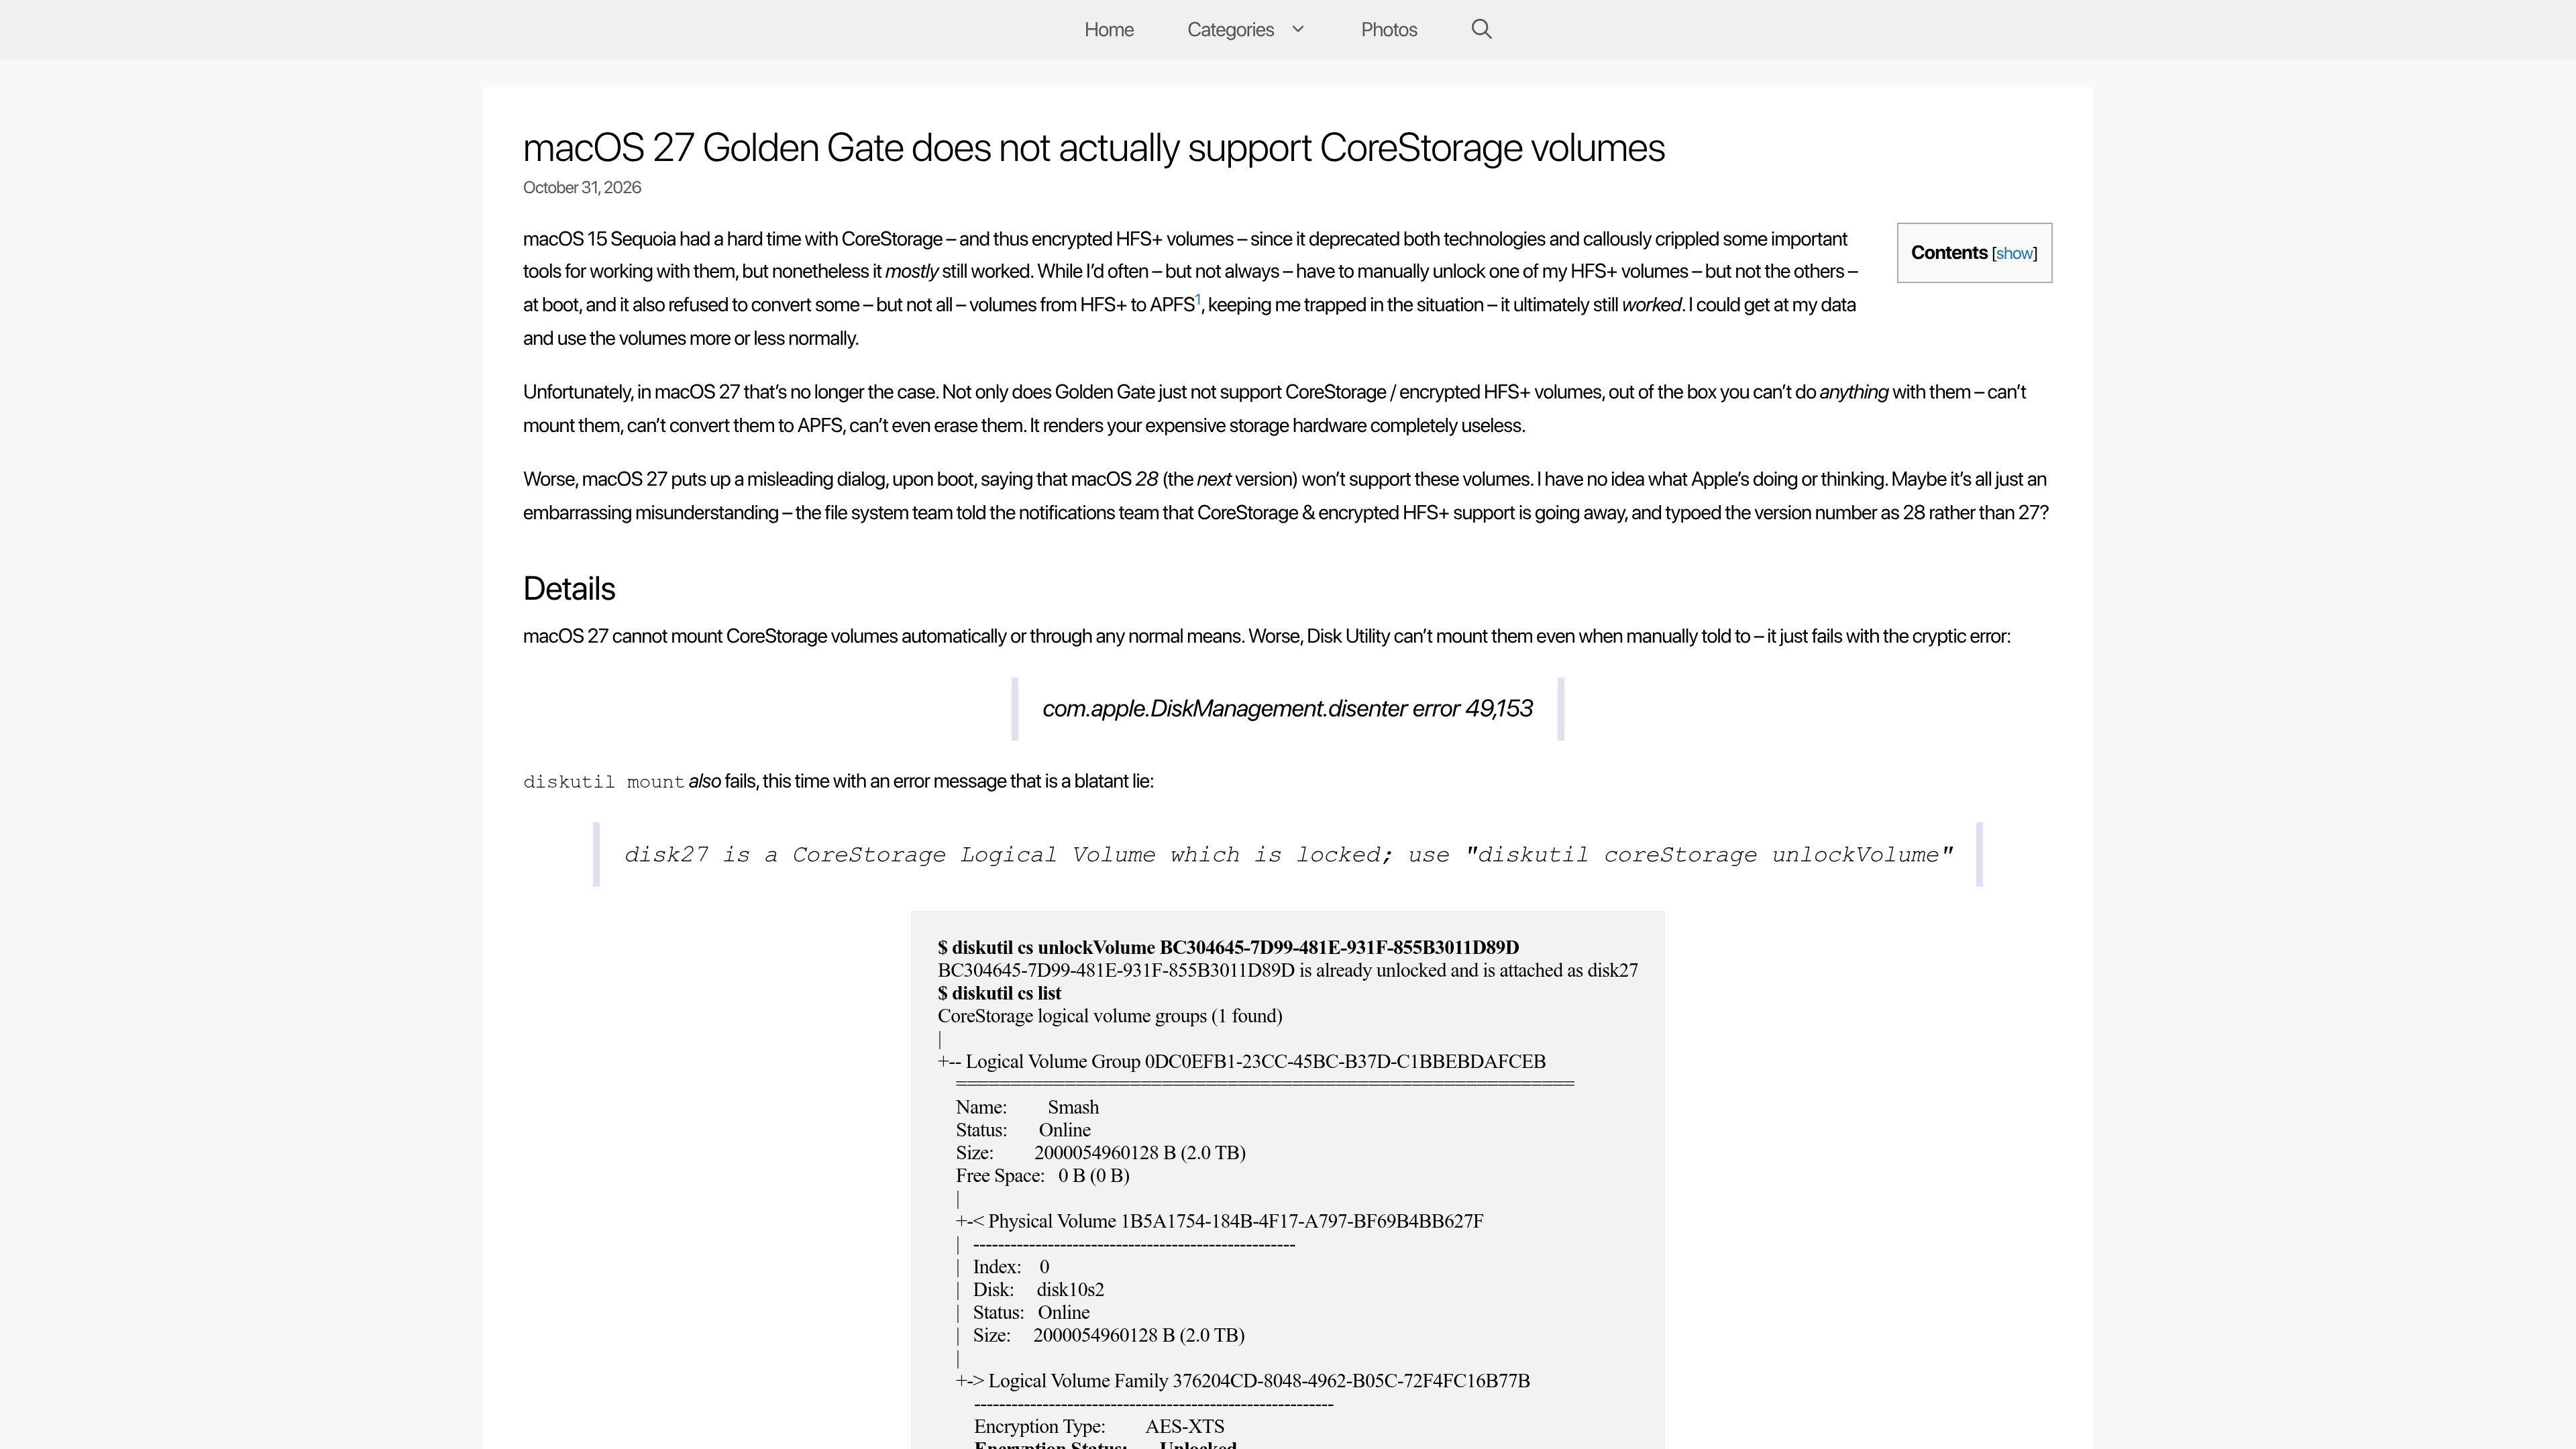
Blog post describing how macOS 27 Golden Gate fails to mount, convert, or erase CoreStorage encrypted HFS+ volumes, with debugging details and a workaround.
737 points by riffraff | 450 comments
CVE record CVE-2026-20841 published by Microsoft describing a remote code execution vulnerability in the Windows Notepad app.
829 points by ComputerGuru | 411 comments
Blog post reverse engineering how Microsoft Paint and Photos embed a server-issued GUID as an invisible pixel watermark in locally generated AI images.
424 points by bo0tzz | 89 comments
Wiz Research blog post detailing CVE-2026-3854, a critical flaw in GitHub's internal git infrastructure enabling remote code execution on GitHub.com and GitHub Enterprise Server.
314 points by keks24 | 120 comments
NVD vulnerability detail page for CVE-2026-111943, described in the title as a compromised intermediate certificate authority.
493 points by kykeonaut | 232 comments
NVD entry for CVE-2026-33579, a privilege escalation vulnerability in OpenClaw; the captured screenshot shows a Reddit network-policy block page instead.
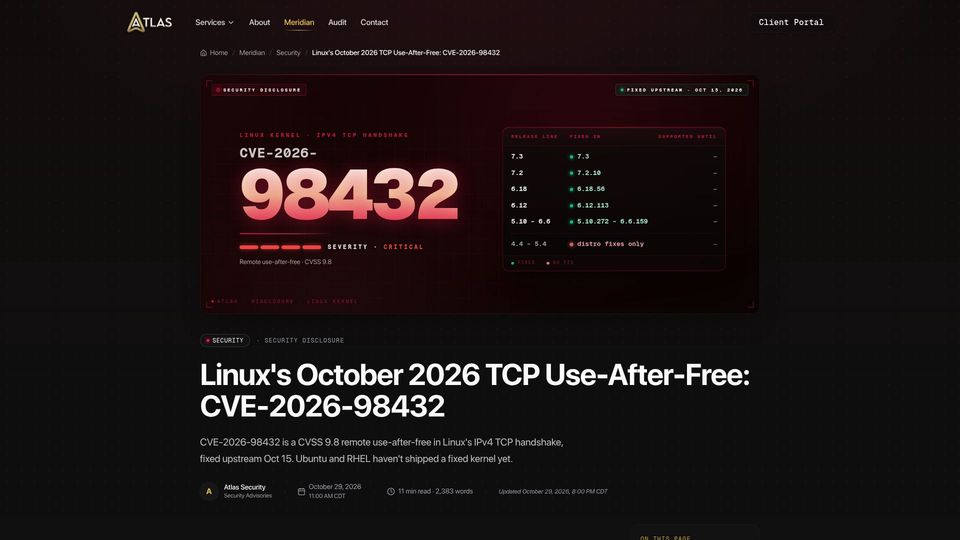
688 points by oger | 323 comments
Atlas Security advisory on CVE-2026-98432, a CVSS 9.8 remote use-after-free in Linux's IPv4 TCP handshake, covering affected versions, distro status, checks, and mitigations.