Secretive makes the enclave usable
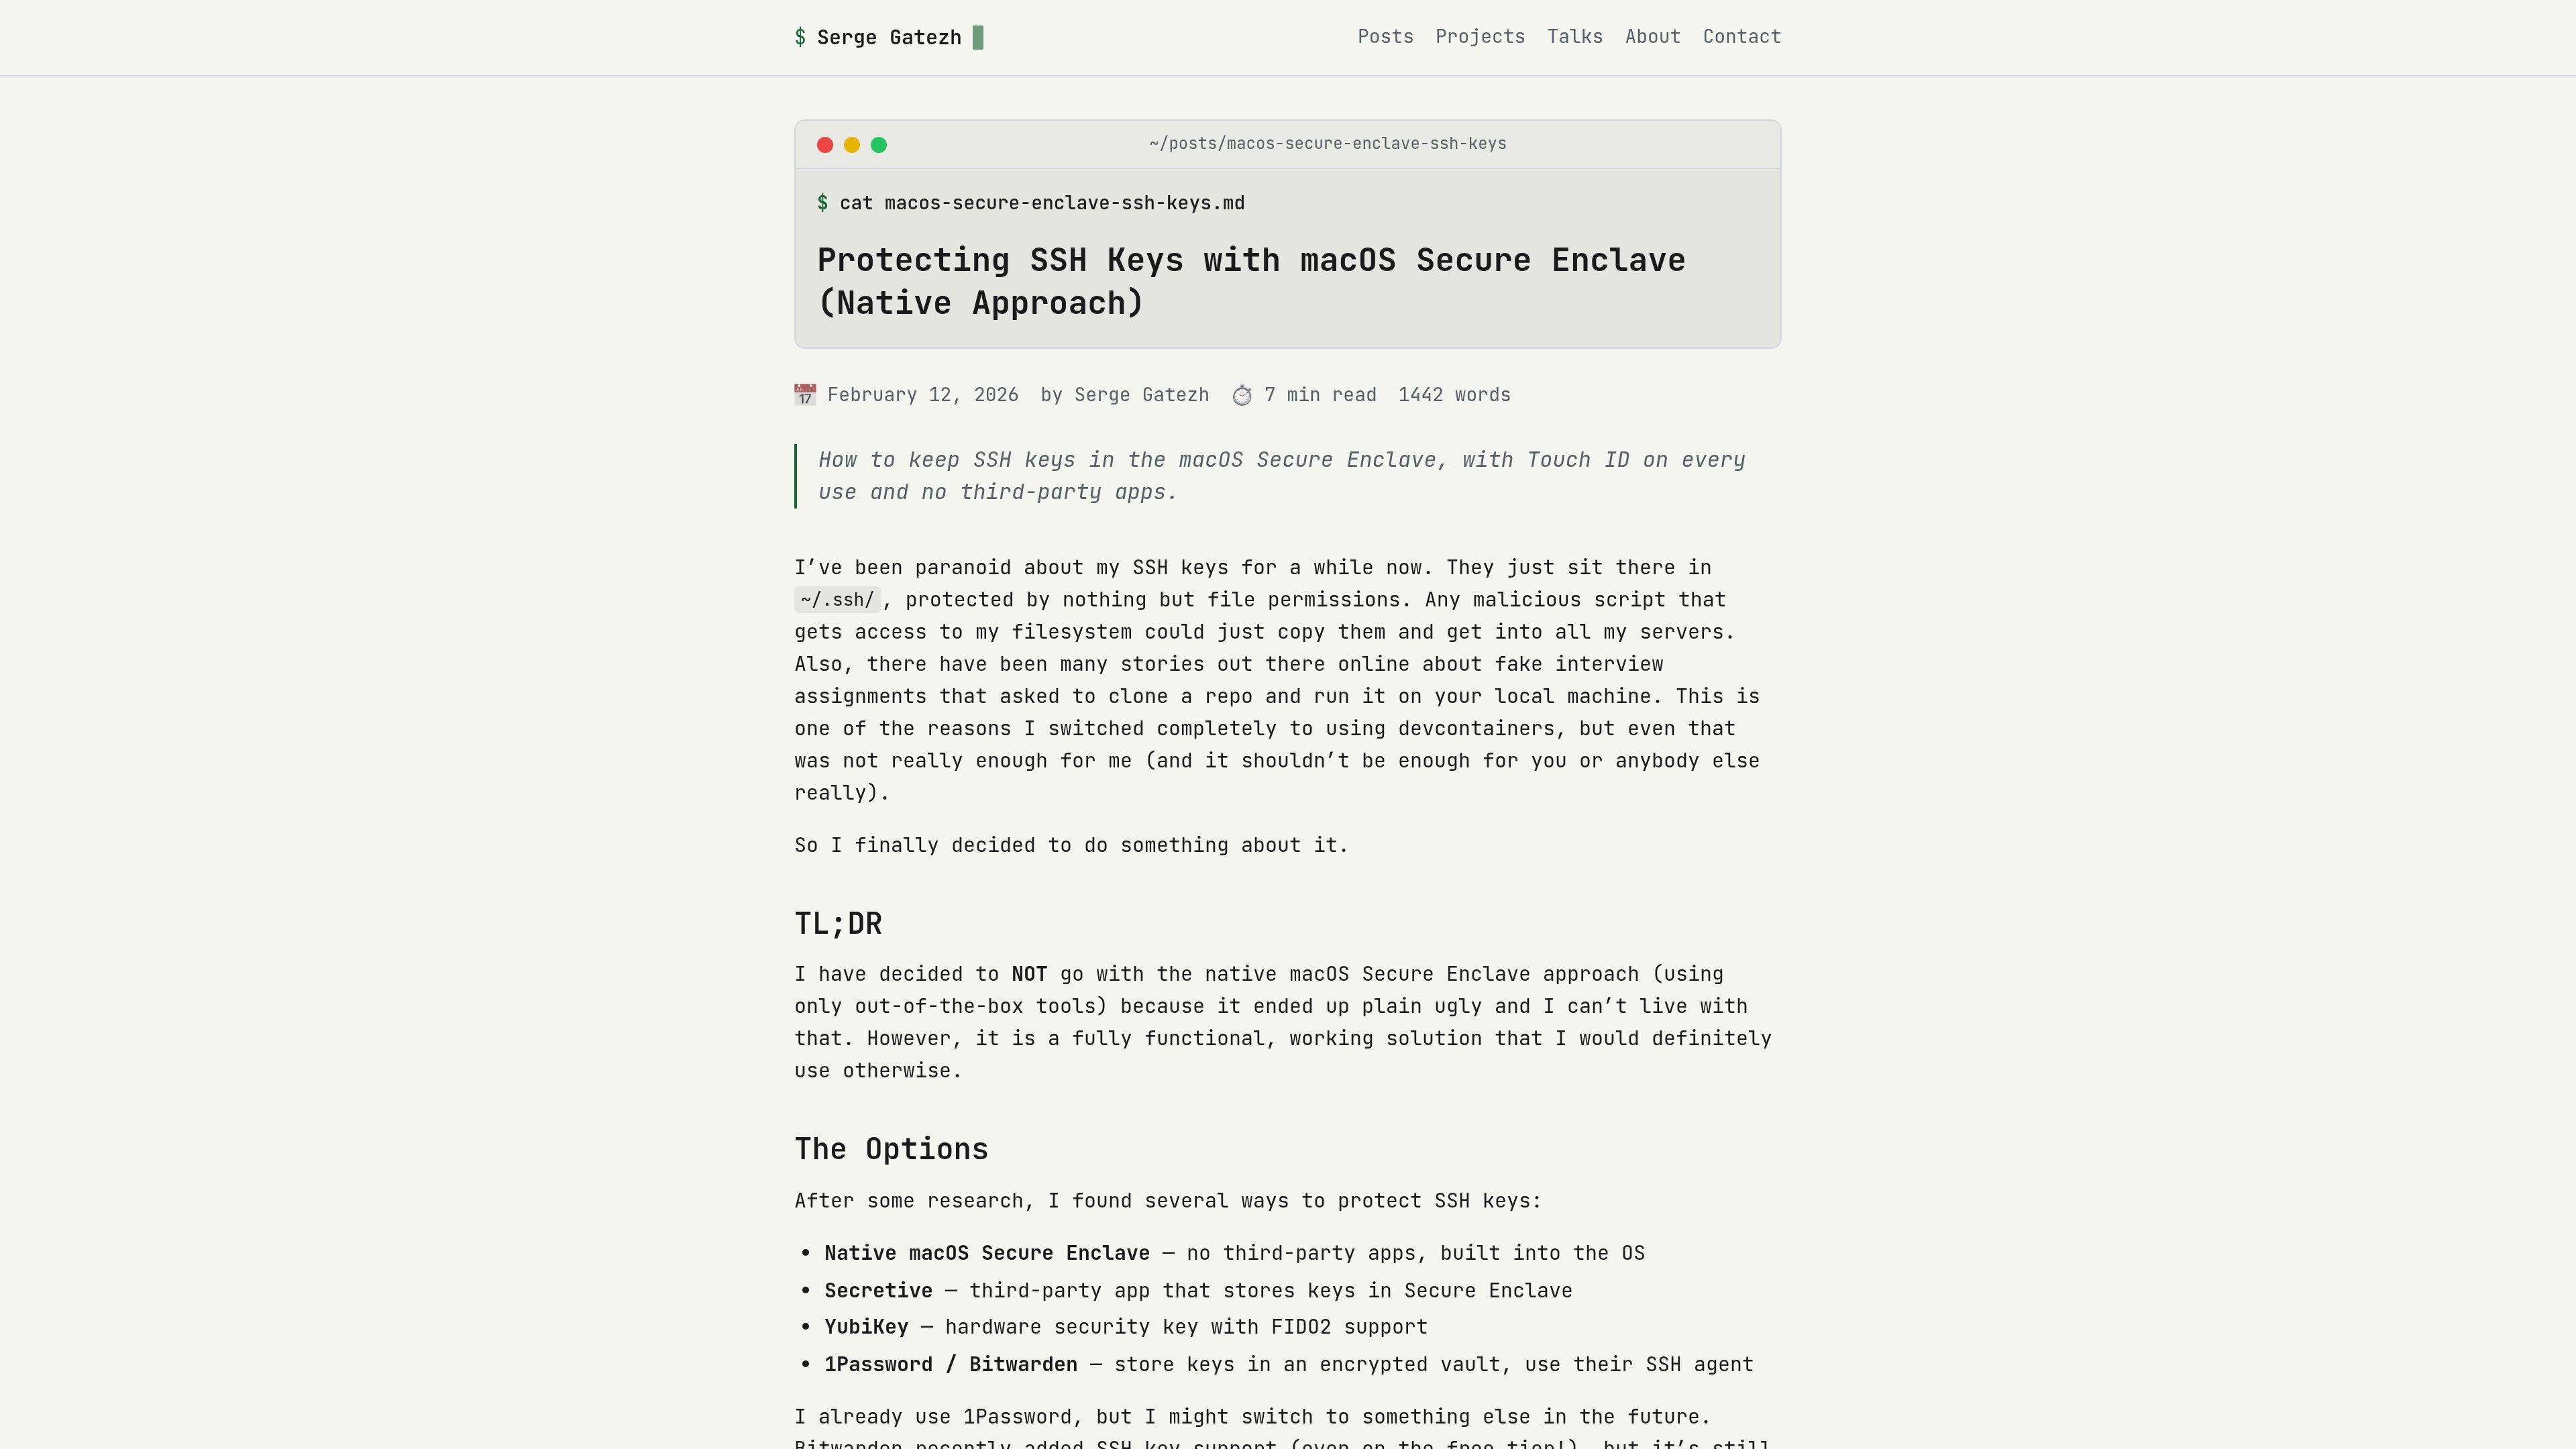
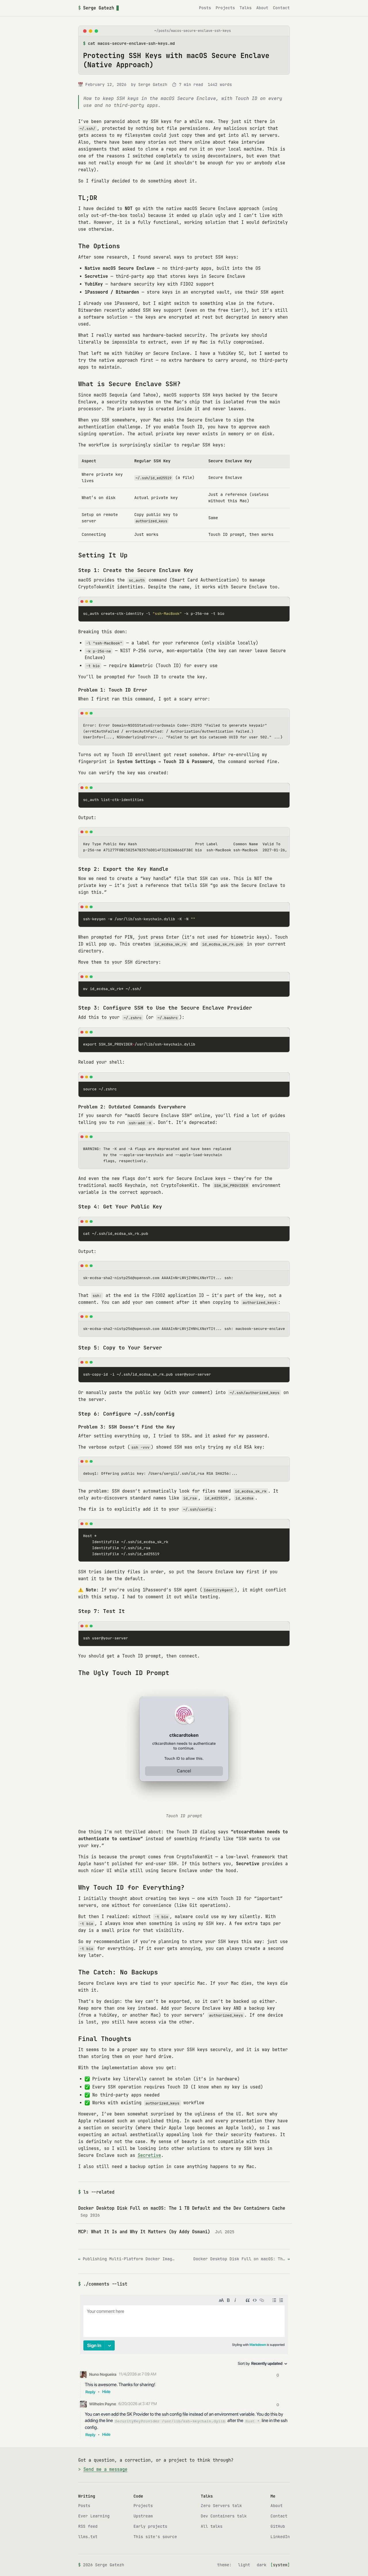
Many commenters, including the author, use Secretive for Secure Enclave SSH keys with Touch ID, often forwarding the agent into VMs or containers, or using it for remote sudo.
Platform keystores are fragile
Keychain bugs, undocumented APIs and non-exportable keys mean you can lose access, so keep backup keys and expect breakage, as the WireGuard config-deletion story shows.
Portable hardware keys or passphrases instead
Some prefer vendor-independent YubiKeys or TKeys, or argue a passphrase-protected key plus agent is enough. Others say presence-gated signing is what actually stops malware and AI agents.