First screen, captured .
Looks similar
SHA1-Hulud the Second Comming – Postman, Zapier, PostHog All Compromised via NPM(aikido.dev)
317 points by birdculture | 98 comments
Aikido Security blog post reporting a second Shai Hulud npm supply-chain attack compromising packages from Zapier, ENS, AsyncAPI, PostHog, and Postman.
Related stories
GitHub RCE Vulnerability: CVE-2026-3854 Breakdown(wiz.io)
424 points by bo0tzz | 89 comments
Wiz Research blog post detailing CVE-2026-3854, a critical flaw in GitHub's internal git infrastructure enabling remote code execution on GitHub.com and GitHub Enterprise Server.
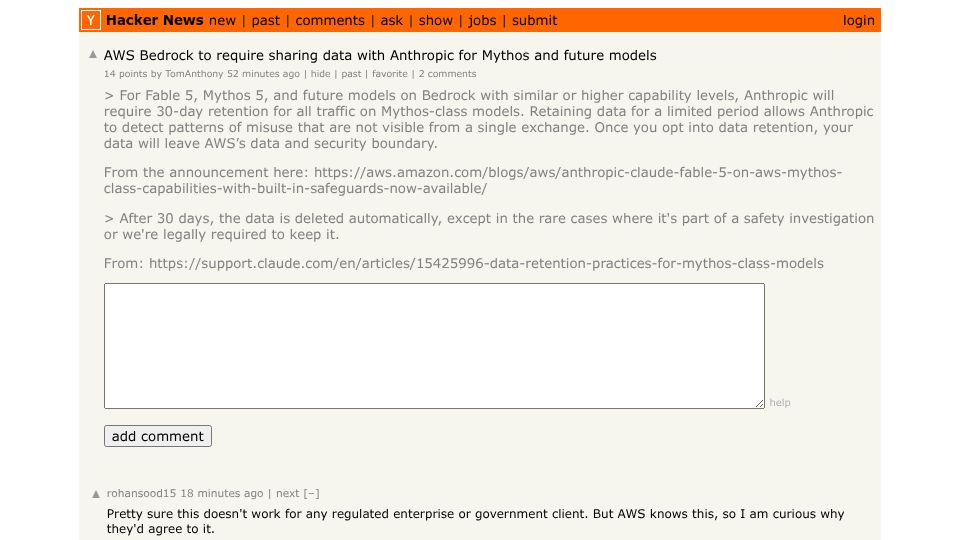
AWS Bedrock to require sharing data with Anthropic for Mythos and future models
369 points by TomAnthony | 216 comments
Hacker News discussion of Anthropic requiring 30-day data retention for Mythos-class Claude models on AWS Bedrock, moving data outside AWS's security boundary.
QwQ-32B: Embracing the Power of Reinforcement Learning(qwenlm.github.io)
445 points by nwjsmith | 147 comments
Qwen Team blog post announcing QwQ-32B, a 32B-parameter reasoning model trained with scaled reinforcement learning.
Windows Notepad App Remote Code Execution Vulnerability(cve.org)
737 points by riffraff | 450 comments
CVE record CVE-2026-20841 published by Microsoft describing a remote code execution vulnerability in the Windows Notepad app.
Io_uring, kTLS and Rust for zero syscall HTTPS server(blog.habets.se)
444 points by guntars | 138 comments
Blog post describing building an HTTPS web server in Rust using io_uring and kernel TLS to avoid system calls on the request path.
OpenClaw privilege escalation vulnerability(nvd.nist.gov)
493 points by kykeonaut | 232 comments
NVD entry for CVE-2026-33579, a privilege escalation vulnerability in OpenClaw; the captured screenshot shows a Reddit network-policy block page instead.