First screen, captured .
Looks similar
OpenSSH Ships on Every Mac, Linux Server and Windows. Its Creator Trusts No One(zbruceli.org)
4 points by zbruceli | 0 comments
Long-form blog profile of OpenSSH creator Theo de Raadt, covering his NetBSD exit, lost DARPA grant, and security-focused philosophy.
One parser, two bugs, many routers: Exploiting Broadcom WiFi across eCos, Linux(quentinkaiser.be)
87 points by zoobab | 22 comments
Blog post by Quentin Kaiser describing two bugs in a Broadcom WiFi parser and how they are exploited on routers running eCos and Linux.
Related stories
Several vulnerabilities have been discovered in the Linux kernel(lwn.net)
529 points by luispa | 380 comments
LWN.net repost of Debian Security Advisory DSA-6528-1, a Linux kernel security update fixing numerous CVEs, dated September 29, 2026.
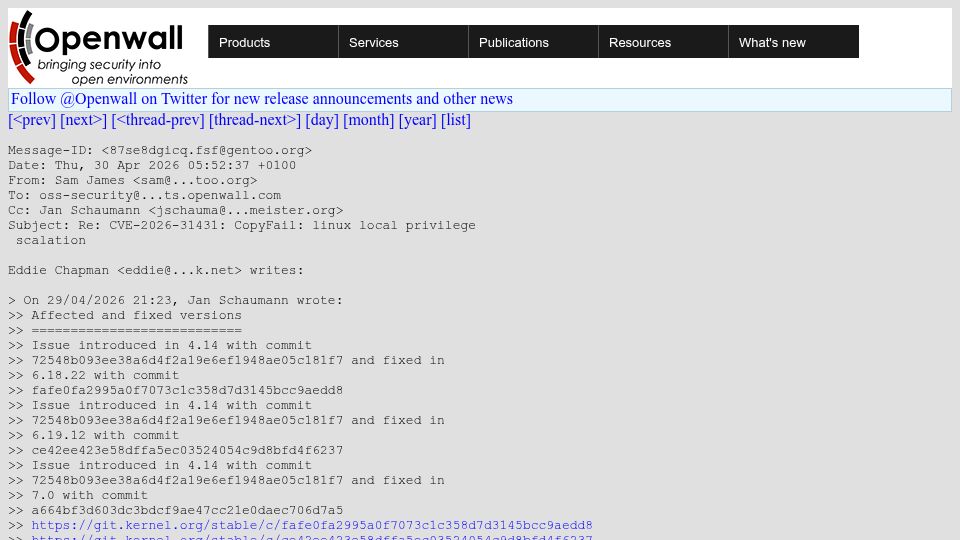
For Linux kernel vulnerabilities, there is no heads-up to distributions(openwall.com)
565 points by ori_b | 477 comments
An oss-security mailing list reply from Gentoo's Sam James on CVE-2026-31431 (CopyFail), a Linux local privilege escalation, and the lack of advance notice to distributions.
New Linux udisks flaw lets attackers get root on major Linux distros(bleepingcomputer.com)
336 points by smig0 | 227 comments
BleepingComputer news article about a udisks vulnerability that lets attackers gain root privileges on major Linux distributions.
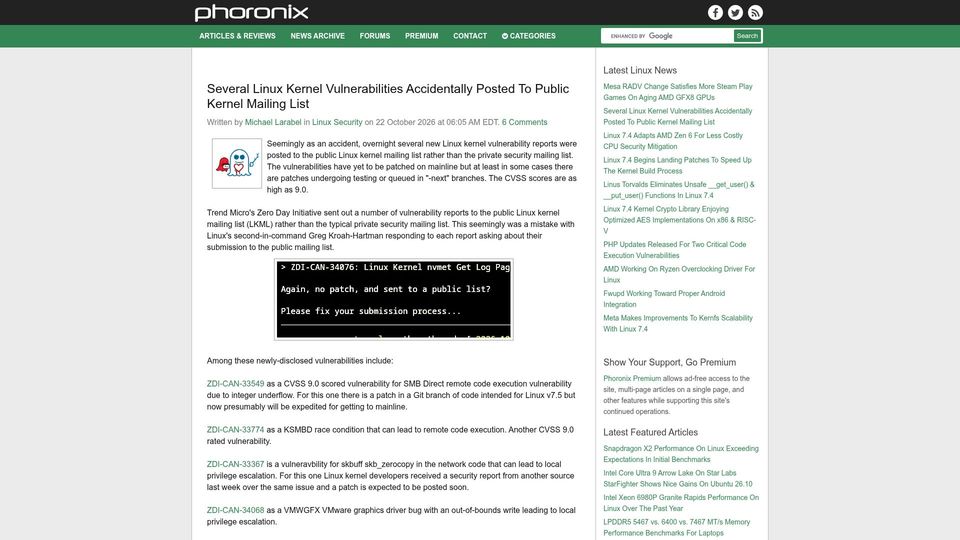
Several Linux kernel vulnerabilities accidentally posted to public mailing list(phoronix.com)
223 points by mrkn1 | 89 comments
Phoronix news article reporting that Trend Micro's Zero Day Initiative accidentally posted several unpatched Linux kernel vulnerability reports to the public LKML.
The Linux Kernel Module Programming Guide(sysprog21.github.io)
350 points by wrycoder | 35 comments
Online edition of The Linux Kernel Module Programming Guide, a free book on writing Linux kernel modules, with GitHub and PDF links.
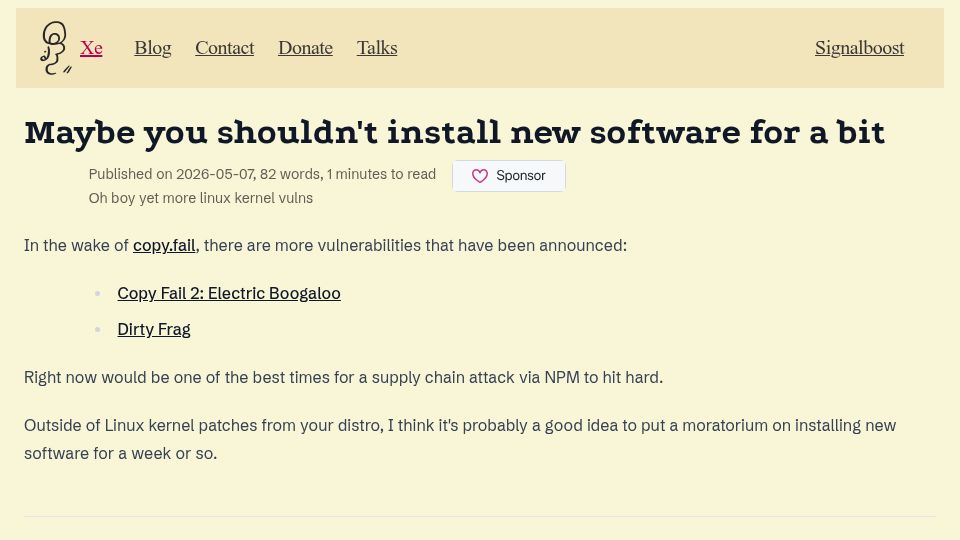
Maybe you shouldn't install new software for a bit(xeiaso.net)
813 points by psxuaw | 427 comments
Short blog post by Xe Iaso noting new Linux kernel vulnerabilities and advising a week-long pause on installing new software due to supply chain attack risk.