First screen, captured .
Looks similar

DuckDB NPM packages 1.3.3 and 1.29.2 compromised with malware(github.com)
367 points by tosh | 263 comments
GitHub security advisory reporting that DuckDB npm packages (duckdb 1.3.3, node-api, node-bindings, duckdb-wasm 1.29.2) were published with malware, listing patched versions.
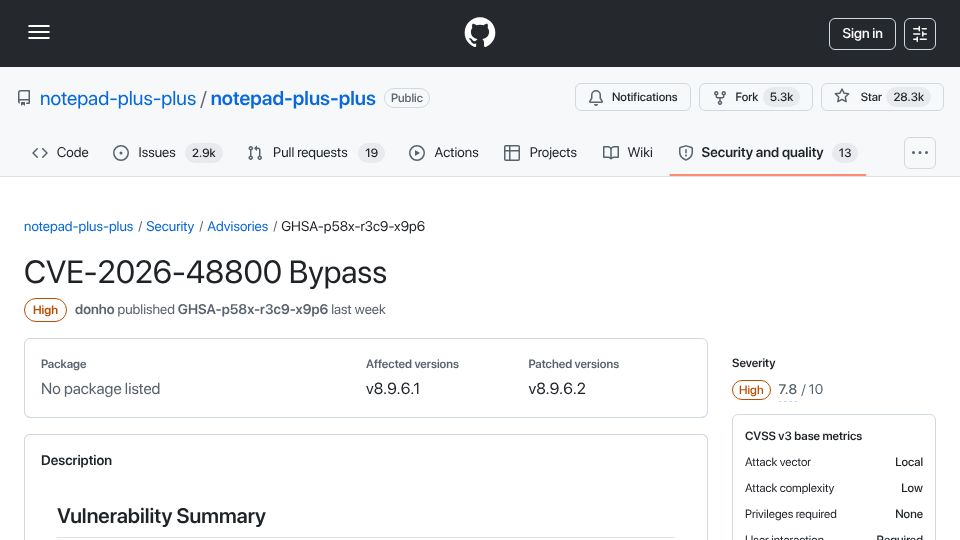
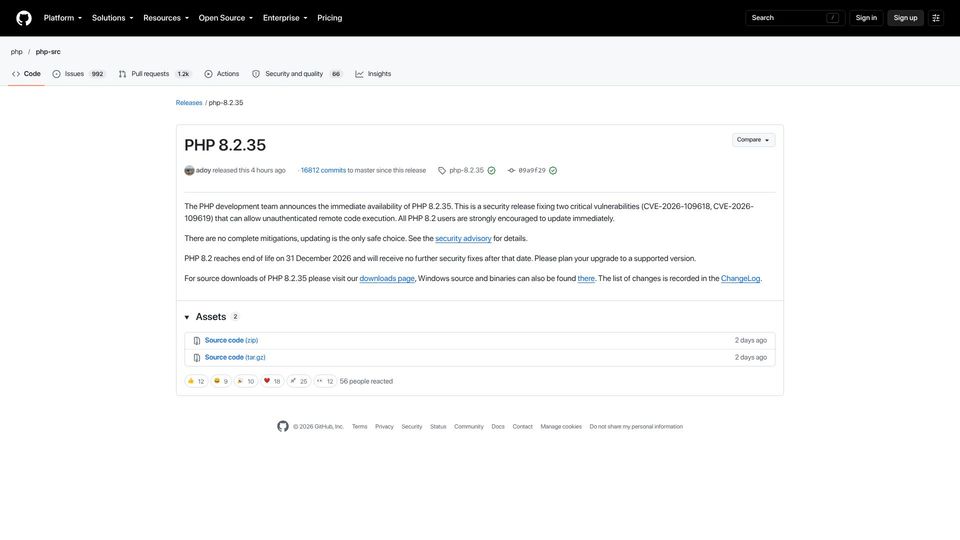
PHP 8.2.35(github.com)
1036 points by tuyuri | 562 comments
GitHub release page for PHP 8.2.35, a security release fixing two critical unauthenticated remote code execution vulnerabilities; PHP 8.2 reaches end of life December 2026.
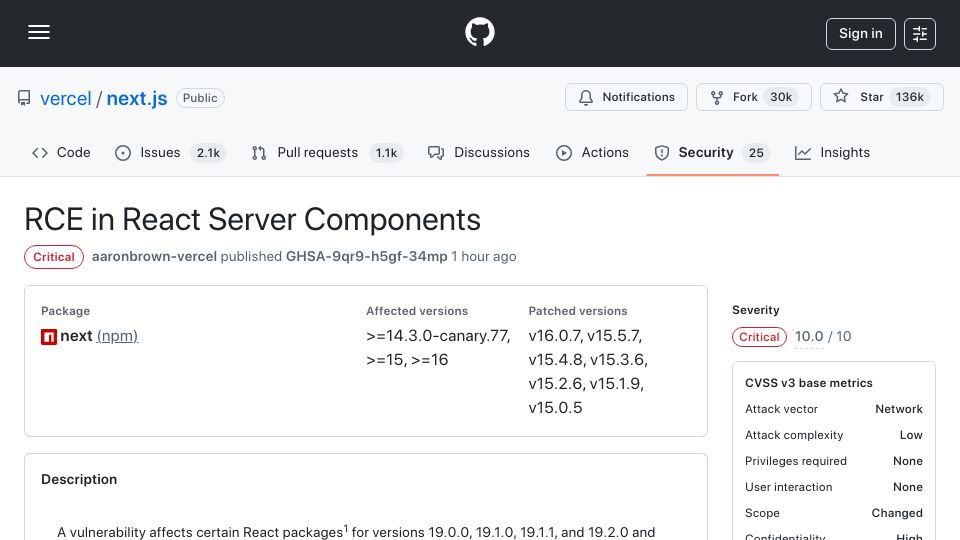
RCE Vulnerability in React and Next.js(github.com)
559 points by rayhaanj | 214 comments
GitHub security advisory GHSA-9qr9-h5gf-34mp for a critical (CVSS 10.0) remote code execution vulnerability in React Server Components affecting Next.js, with patched versions listed.
Related stories
RCE Vulnerability in React and Next.js(github.com)
559 points by rayhaanj | 214 comments
GitHub security advisory GHSA-9qr9-h5gf-34mp for a critical (CVSS 10.0) remote code execution vulnerability in React Server Components affecting Next.js, with patched versions listed.
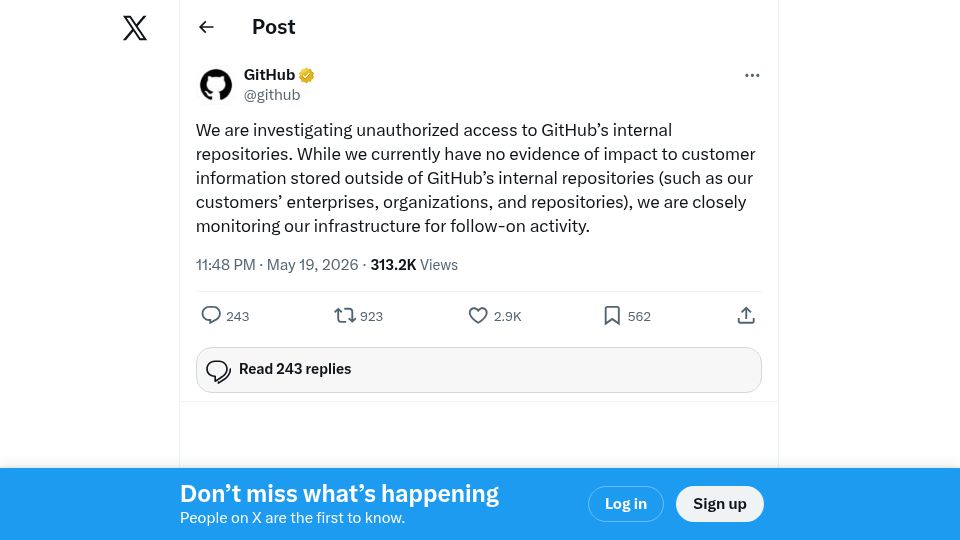
GitHub is investigating unauthorized access to their internal repositories(twitter.com)
527 points by splenditer | 289 comments
A post on X from GitHub stating it is investigating unauthorized access to its internal repositories, with no current evidence of impact to customer data.
CISA Admin Leaked AWS GovCloud Keys on GitHub(krebsonsecurity.com)
433 points by LelouBil | 171 comments
KrebsOnSecurity article reporting that a CISA contractor kept a public GitHub repository exposing privileged AWS GovCloud credentials and internal CISA system details.
Io_uring, kTLS and Rust for zero syscall HTTPS server(blog.habets.se)
444 points by guntars | 138 comments
Blog post describing building an HTTPS web server in Rust using io_uring and kernel TLS to avoid system calls on the request path.
Today's PHP security release, and how we're strengthening security(thephp.foundation)
761 points by ejohnso49 | 394 comments
PHP Foundation blog post on a PHP security release fixing two critical RCE vulnerabilities, how they were found, the disclosure leak, and how PHP security work is being strengthened.
I never authorized an integration that scans my secrets(github.com)
202 points by trvrprkr | 155 comments
A closed GitHub issue on the home-assistant.io repo in which a user complains that an integration scanning their secrets was enabled without authorization, calling it a privacy invasion.